

PenBox
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
exploitationfuzzinginformation-gathering+8
534
x3omdax/penboxPenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 irsl/cve-2022-3168-adb-unexpected-reverse-forwards
Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations
 leochen-coremind/spd_flasher
CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 youssefnoser/opd2415-6.6.118-cve-2026-64560-ksu
Per-boot KernelSU late-load via CVE-2026-64560 — OnePlus Pad 3 (OPD2415, SM8750, kernel 6.6.118-android15-8, 4K, locked bootloader): payload port,…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
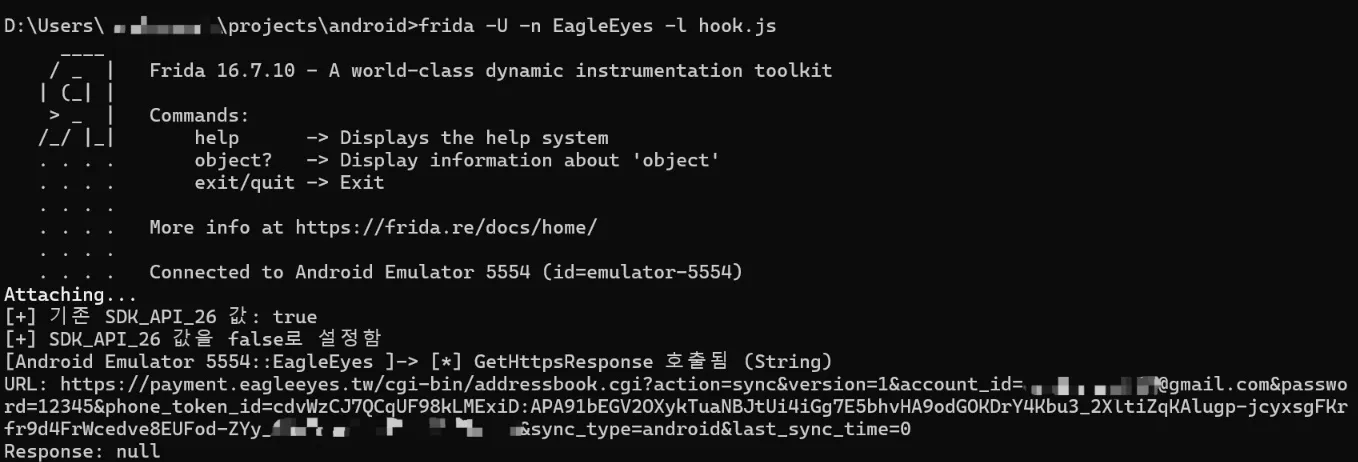 shinycolumn/cve-2025-46408
Improper Hostname Verification in EagleEyes Lite Android Application