
mtk_bp
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
binary-analysisembedded-systems-securityfirmware-analysis+4
80
nccgroup/mtk_bpTools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 xyzasian/janus-cve-2017-13156
Java-based exploit tool for CVE-2017-13156 that bypasses Android APK signature verification by appending a DEX file to an existing APK, enabling code…
 xcodeon1/ssh-killv2
SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 starling021/cve-2019-11932-supportapp
Exploit helper for CVE-2019-11932 (WhatsApp GIF RCE) that calculates system() function and ROP gadget addresses for different devices to enable…
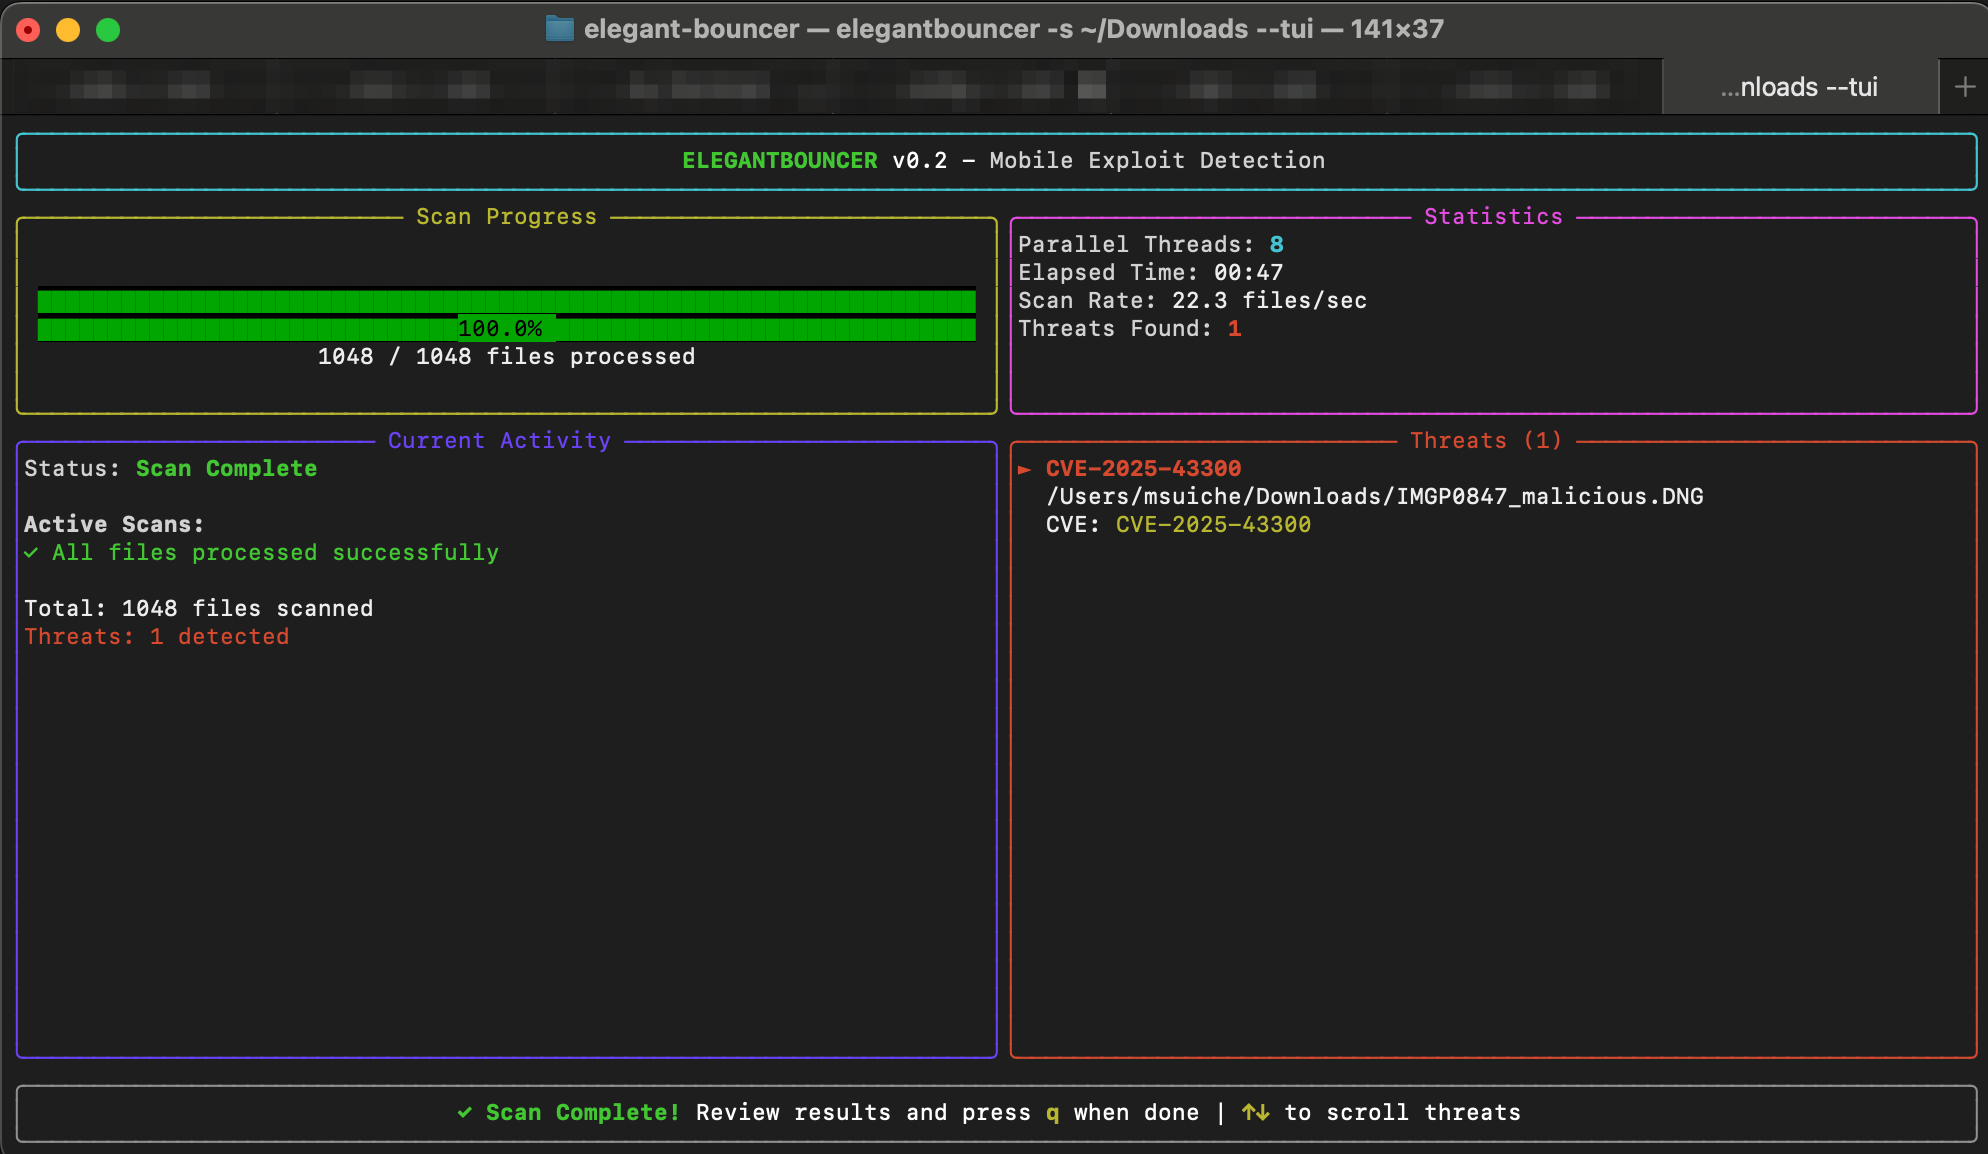 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 infiniteloopers/cve-2019-11932
Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…
 neternels/android_kernel_xiaomi_sunny
CAFest nethunter kernel based on LA.UM.9.1.r1-11900-SMXXX0.0 with latest upstream-f2fs-stable-linux-4.14.y merged, bb and perf focused. | Force push…
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…
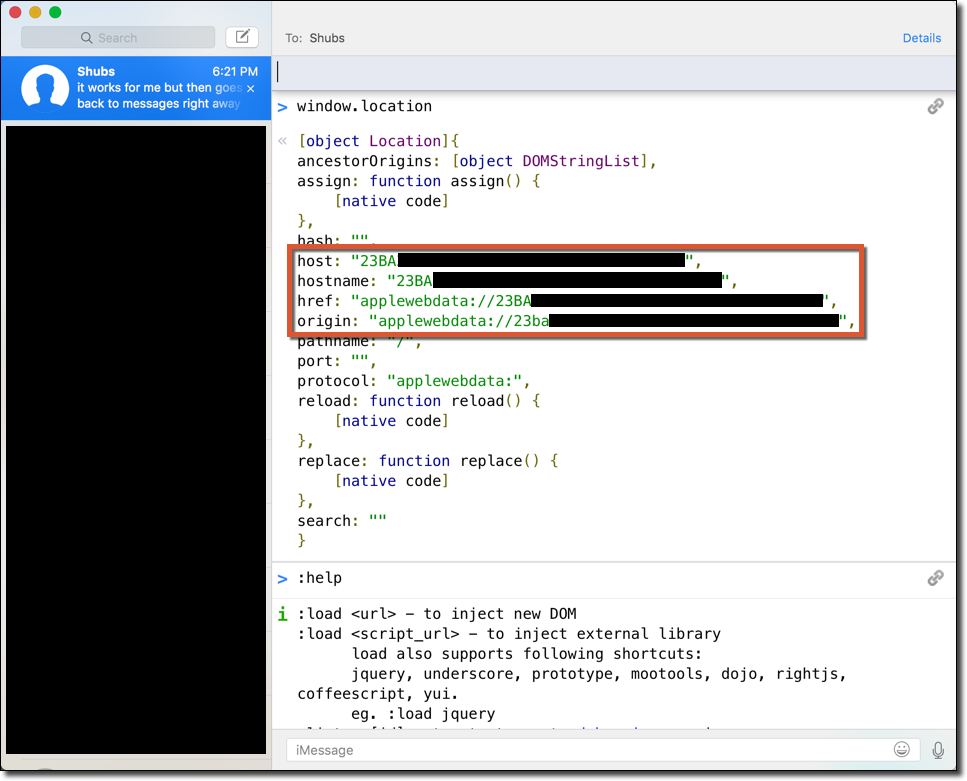 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 felix-pb/kfd
kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety