
Sandb0x-Xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…


A list of awesome penetration testing tools and resources.

A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.

Secure, Unified, Powerful and Extensible Rust Android Analyzer

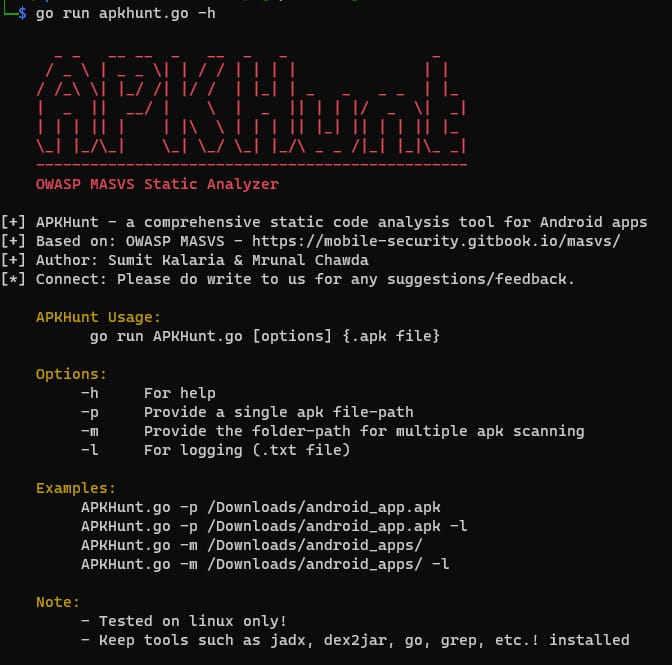
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…

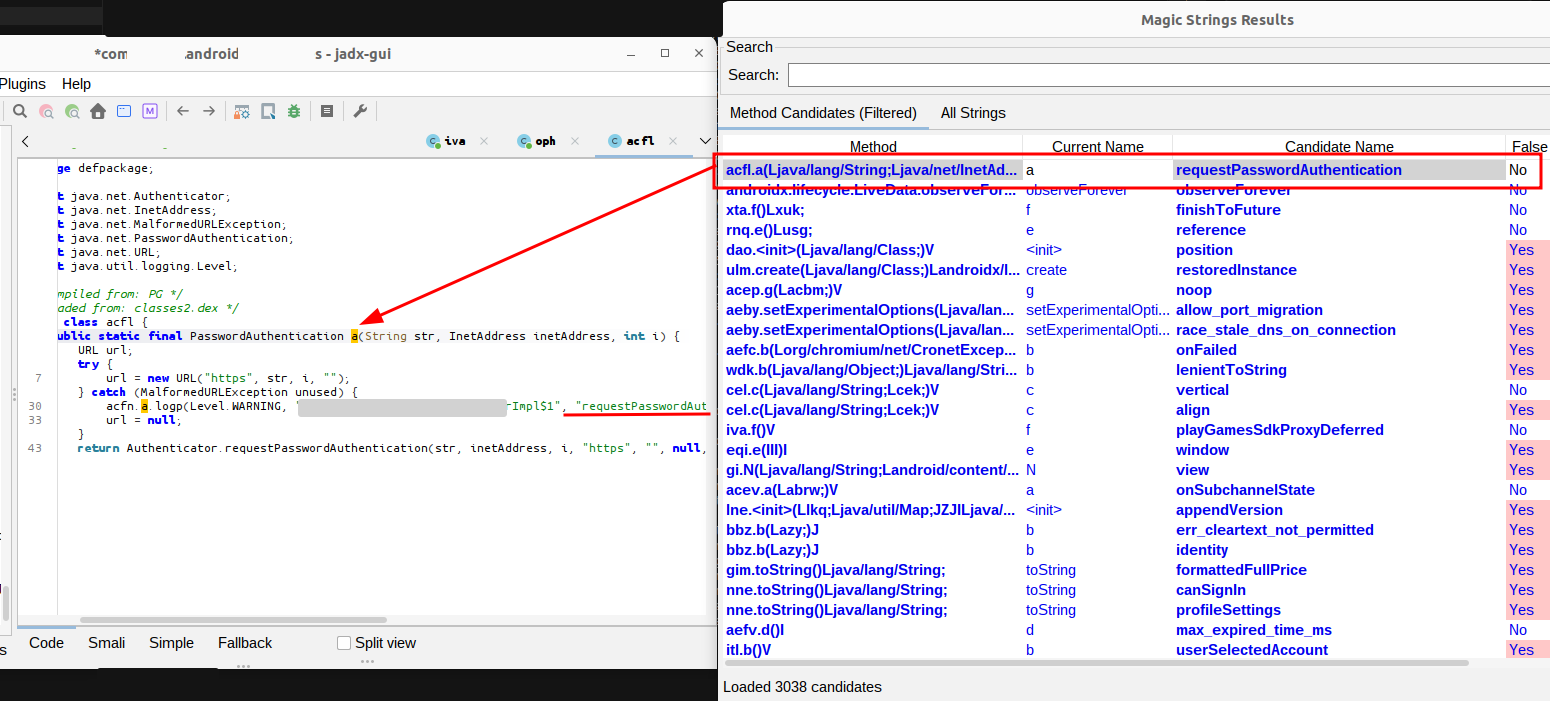
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

Exploit for CVE-2019-11932, a remote code execution vulnerability in WhatsApp via malicious GIF files. Includes proof-of-concept code and technical…

Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…

SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…

Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…

Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.

The source files and tools needed to build the OWASP Cornucopia decks in various languages

A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…

Proof-of-concept exploit for CVE-2020-0458, a vulnerability in Android 10's media framework enabling remote code execution via crafted media files.

Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…

Python utility for parsing Xamarin AssemblyStore blob files

AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…