
CVE-2019-6447
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
android-securityexploitationinformation-gathering+2
osuni-99/cve-2019-6447The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
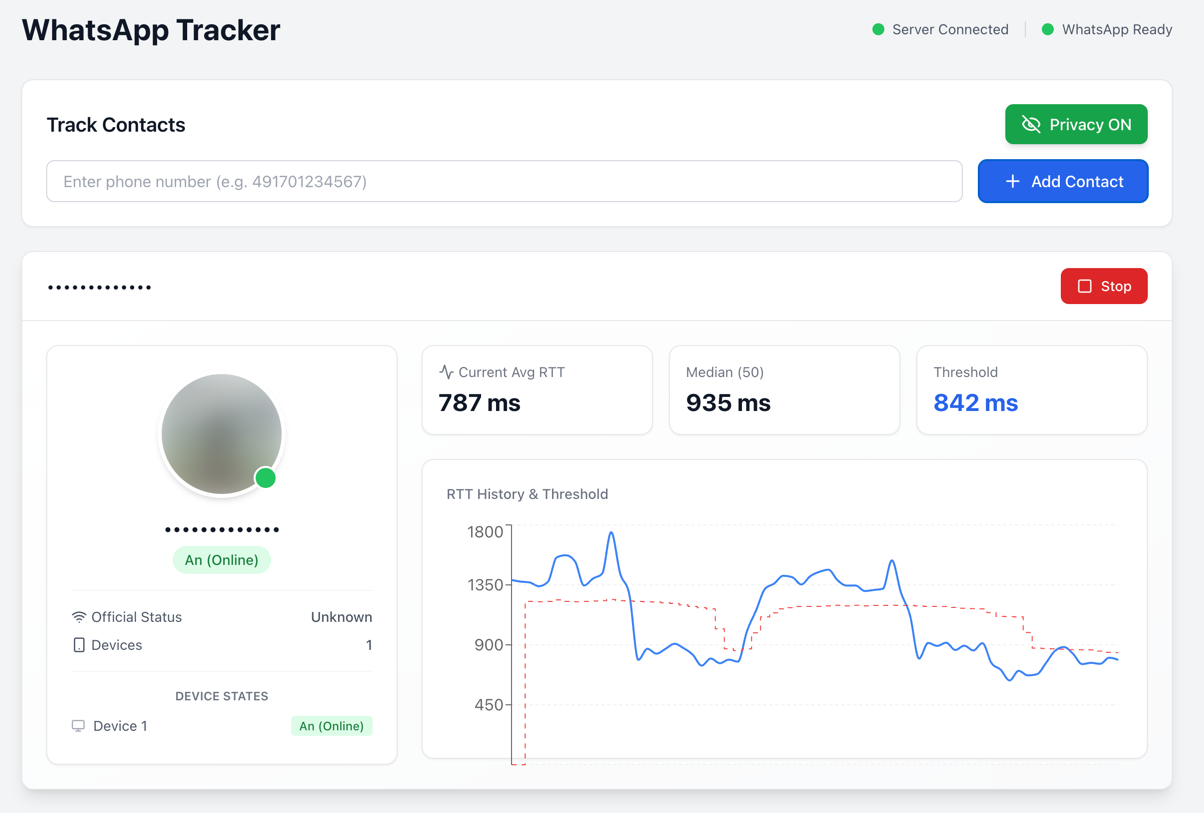 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
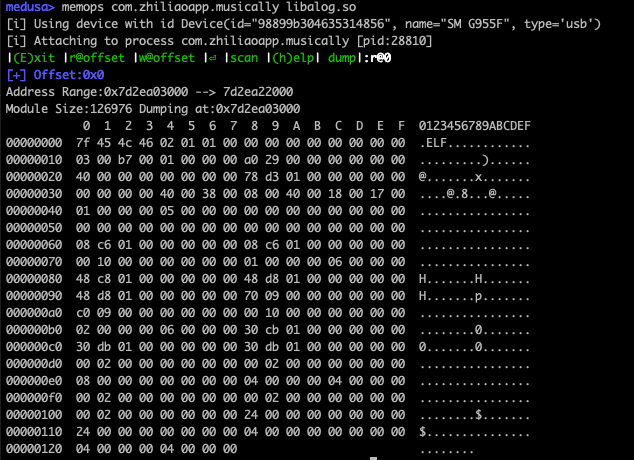 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
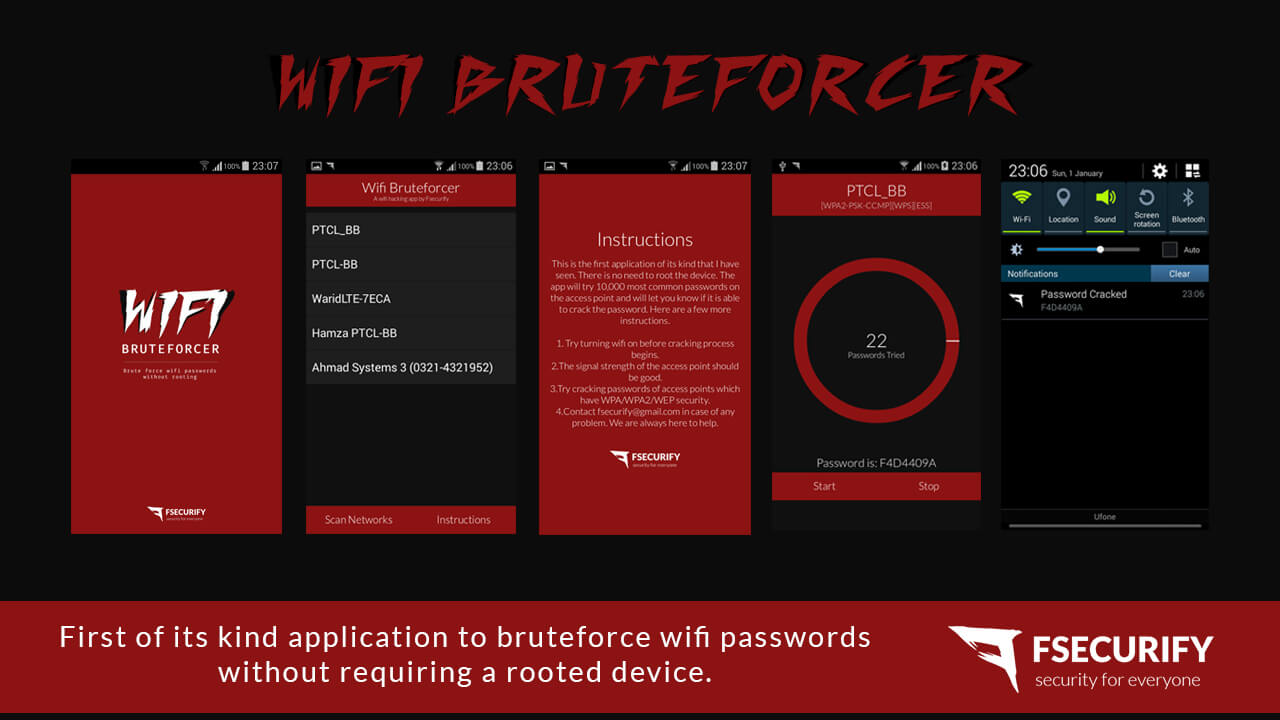 faizann24/wifi-bruteforcer-fsecurify
Android application to brute force WiFi passwords without requiring a rooted device.
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
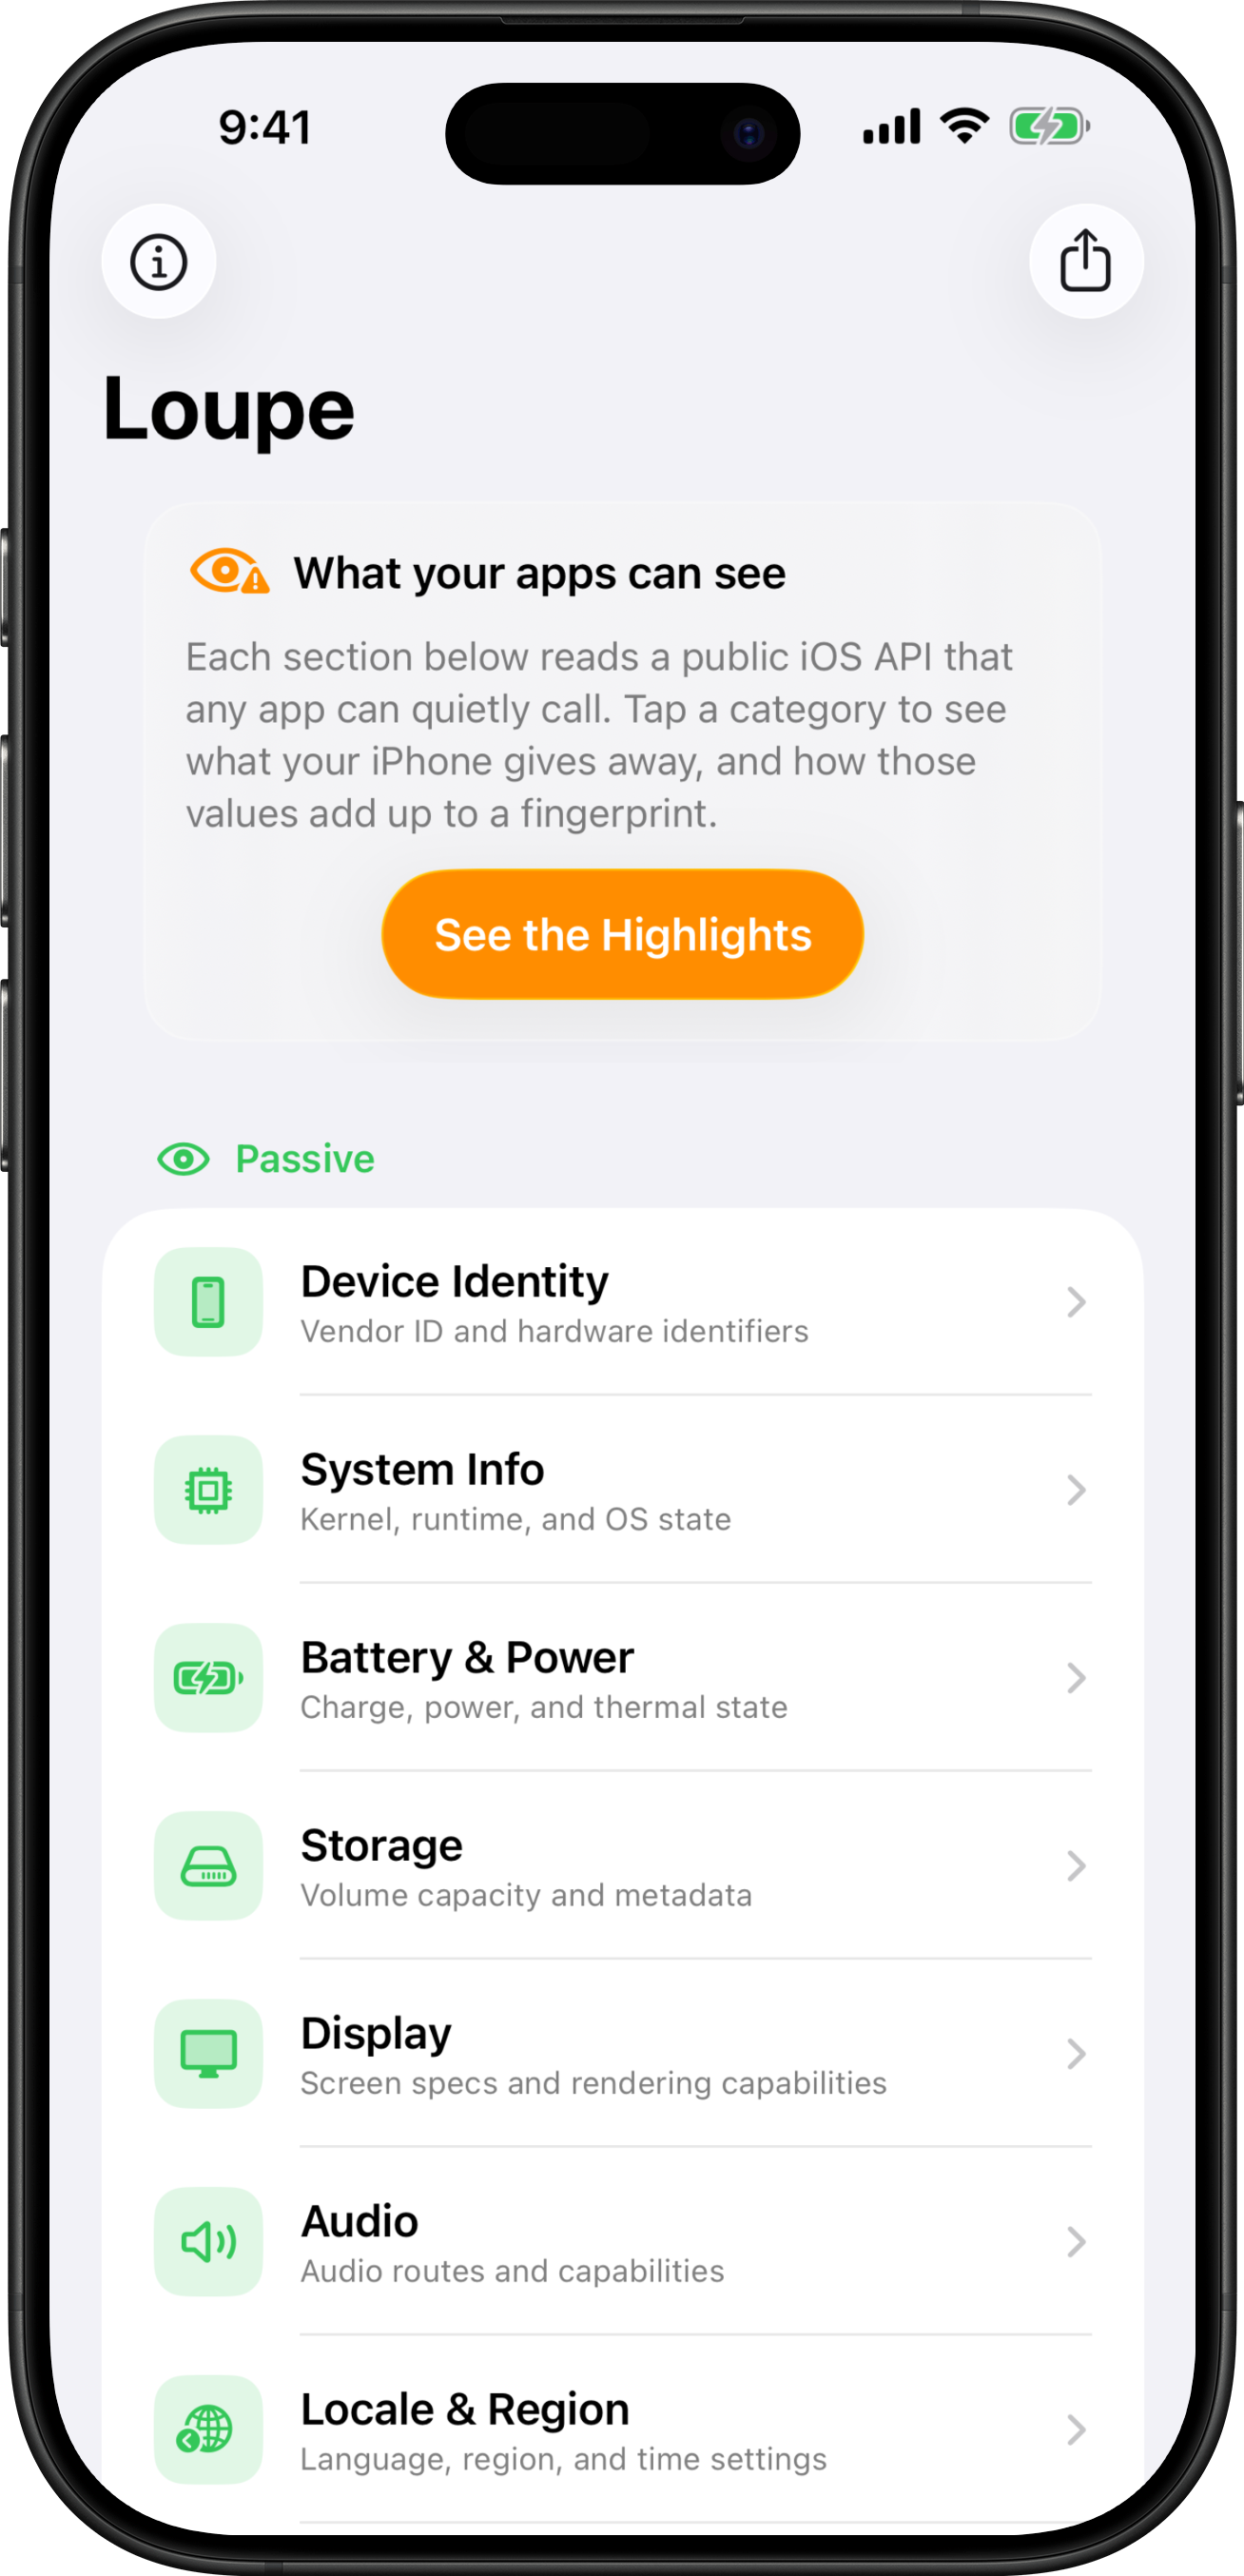 mysk-research/loupe
A privacy-focused iOS app that raises awareness about what native apps can see
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…