cve-2026-43499-firetv-sheldonp-writeup

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Gain root privilege by exploiting CVE-2014-3153 vulnerability

Privilege escalation in Andy emulator

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…

Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…

Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…

Android client for Prey: reliable device tracking and security tool

Research tool for enumerating WhatsApp user accounts via phone number probing, demonstrating large-scale enumeration vulnerabilities and their…

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

Proof of concept for CVE-2022-1364 against Alibaba's UC Browser

Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…

Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.

Details of CVE-2020-14292

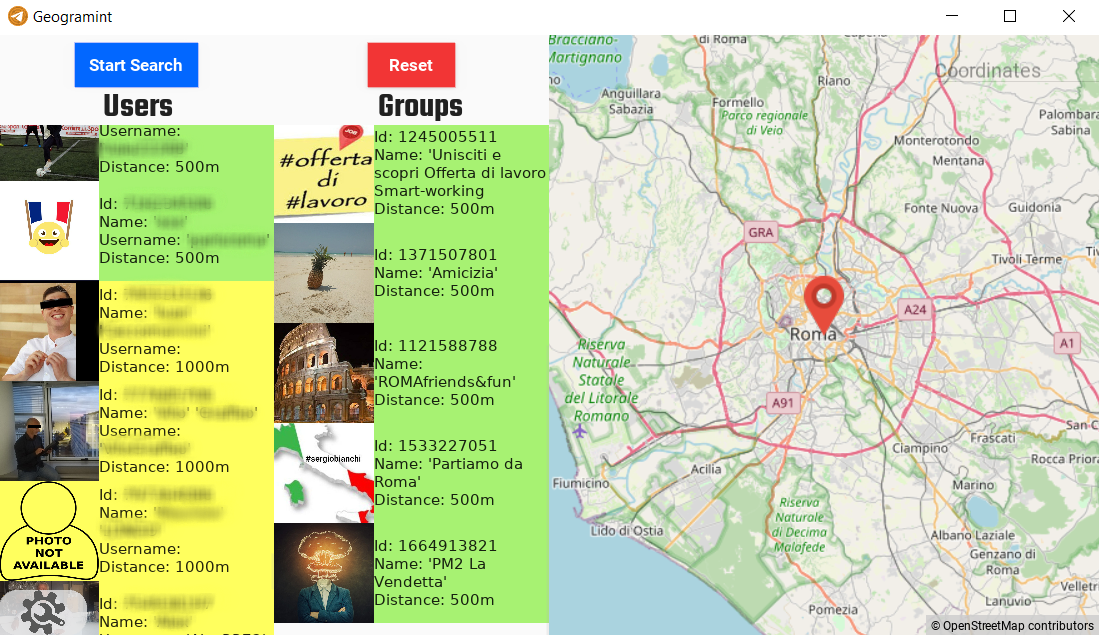
An OSINT Geolocalization tool for Telegram that find nearby users and groups 📡🌍🔍

Collection of scripts for reversing Qualcomm Hexagon baseband / modem firmware

DoS against Belkin smart plugs via crafted firmware injection

Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…

Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations