

androguard
 androguard/androguard
Reverse engineering and pentesting for Android applications
android-securitydynamic-analysis-sandboxingmalware-analysis+6
6.2k9 days ago
androguard/androguardReverse engineering and pentesting for Android applications
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
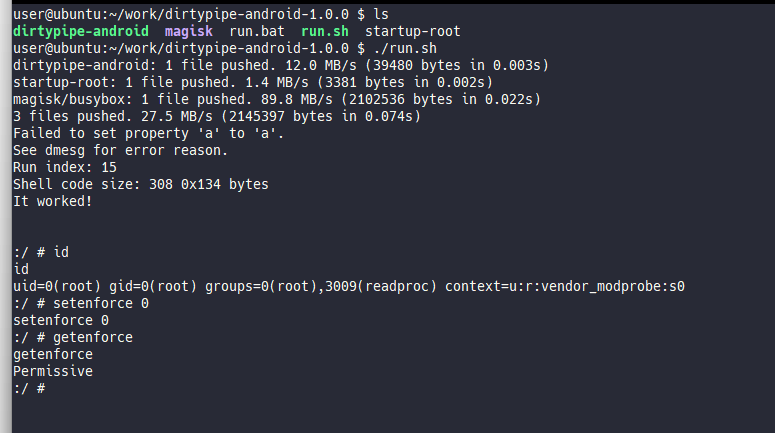 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 northbit/metaphor
Metaphor - Stagefright with ASLR bypass
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 pixel-props/build.prop
Bash script to build your own system.prop
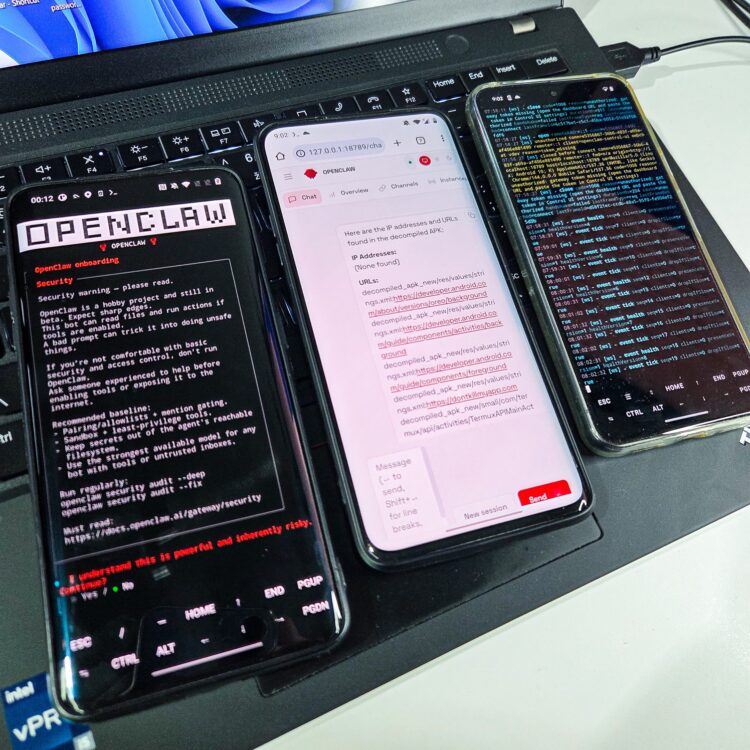 androidmalware/openclaw_termux
How to Install OpenClaw on an Android Phone and Control It via WhatsApp

 darknavysecurity/poc
Curated proof-of-concept exploits for real-world CVEs affecting iOS, macOS, Chrome Renderer, and Steam clients, with version-specific targets and…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
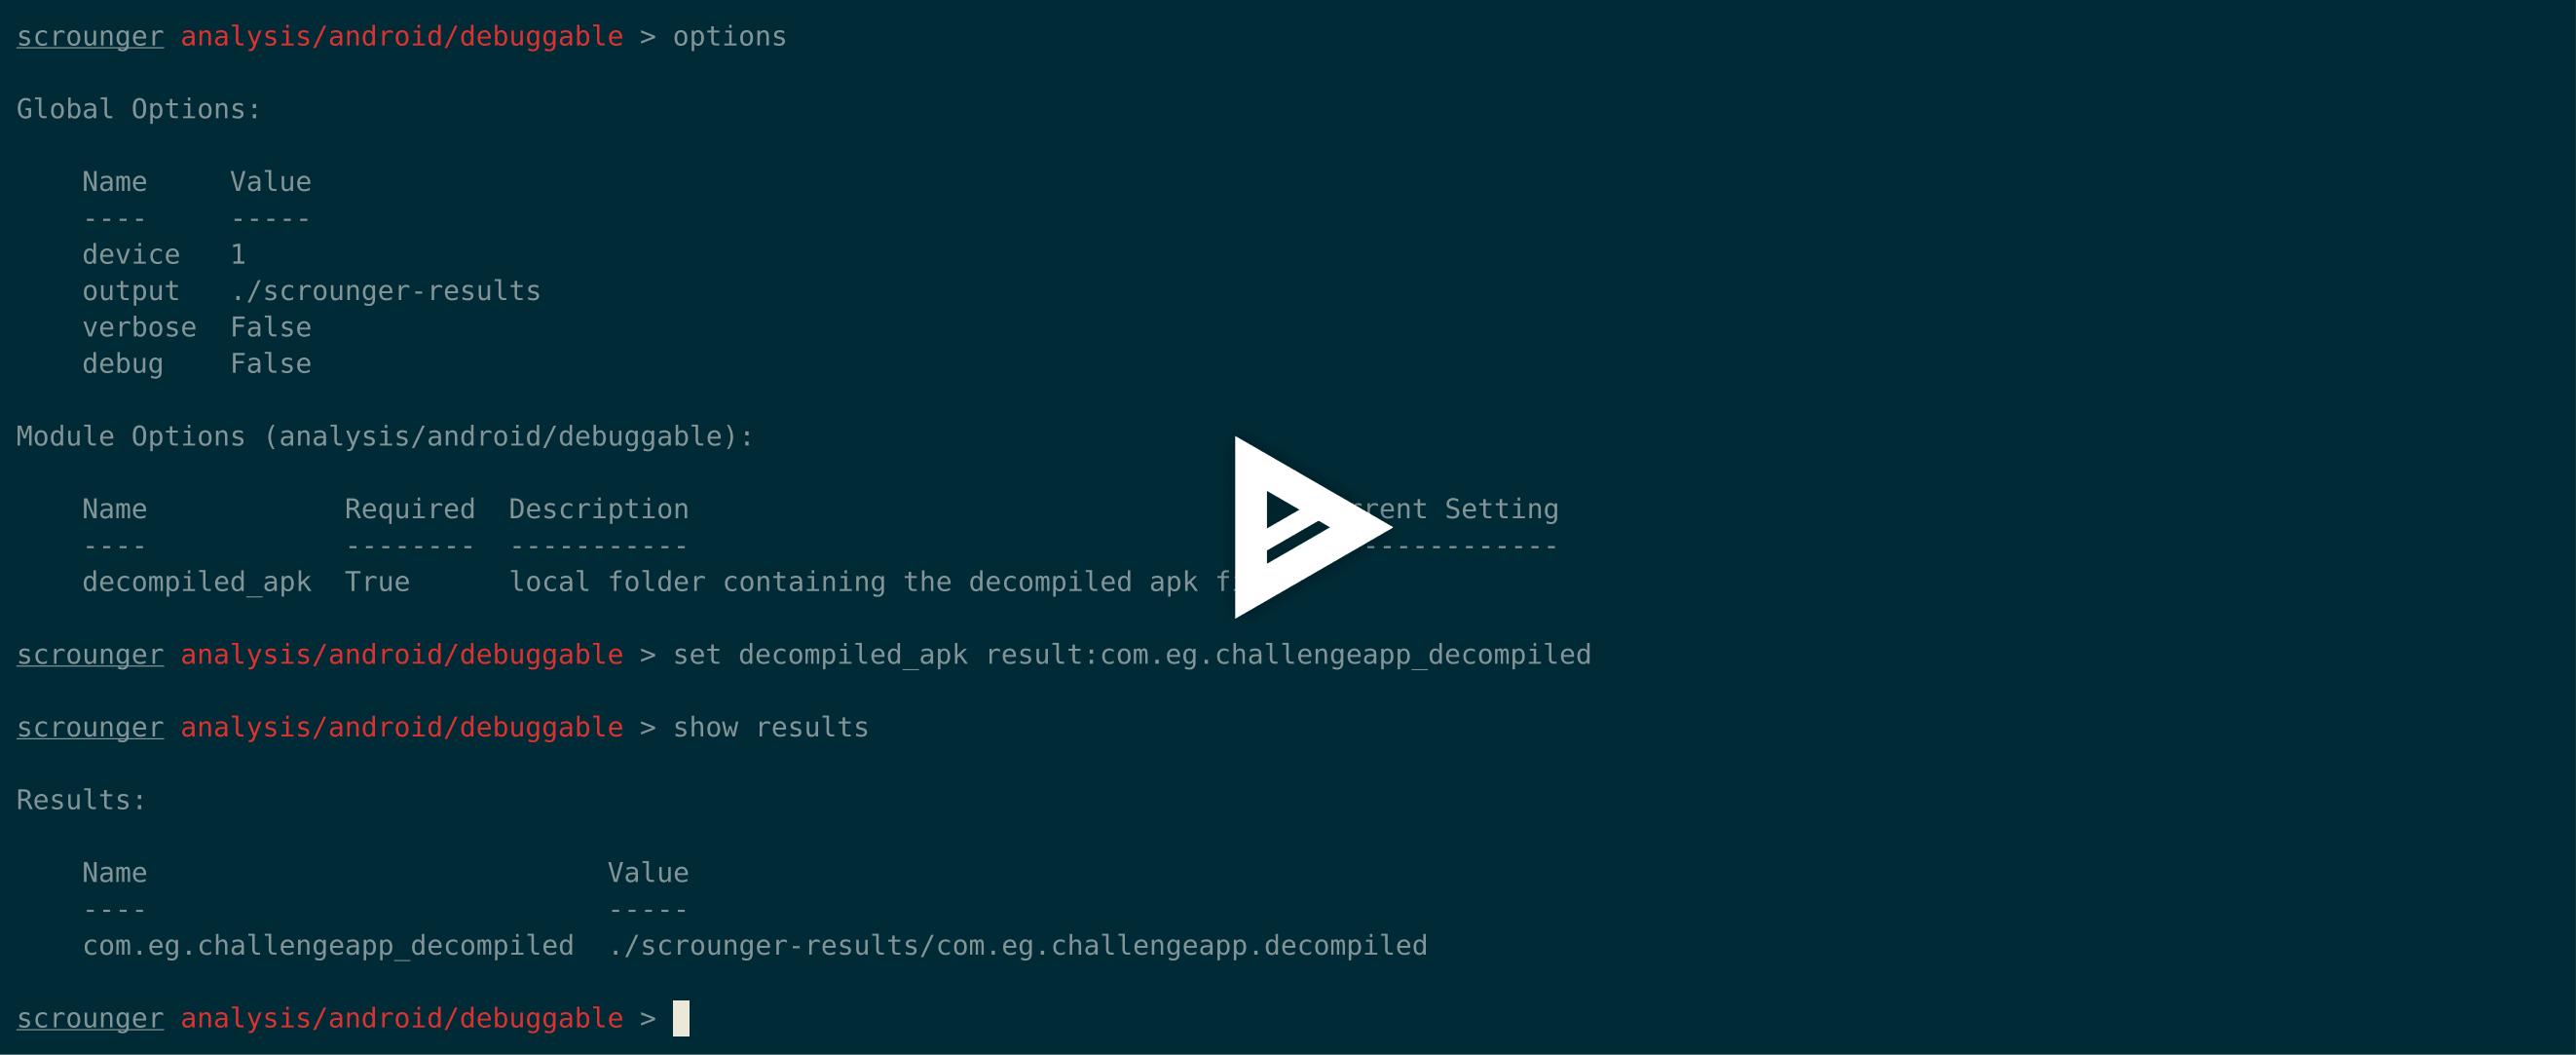 nettitude/scrounger
Mobile application testing toolkit
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker