CVE-2013-4710-WebView-RCE-Vulnerability

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…

Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…

OkHttp sample app vulnerable to CVE-2016-2402

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.

Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…

Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…

The above investigation of the ES file browser security weakness allows us to see the issue in its entirety

Android AOSP 10 framework base repository containing the fix for CVE-2023-21097, a vulnerability in the Android framework that could lead to local…

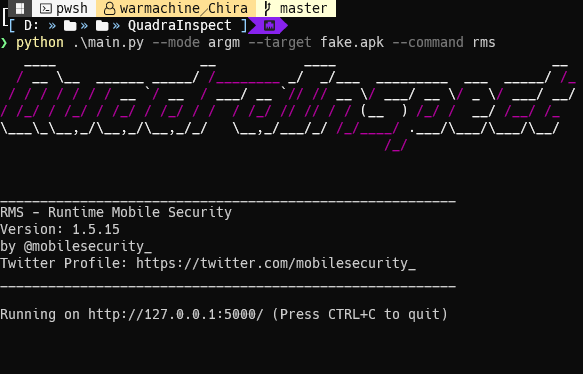
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…

Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.

Yet another static code analyzer for malicious Android applications

Exploit for Apple CoreGraphics heap overflow (CVE-2014-4377) enabling arbitrary code execution on iOS 7.1.x via crafted PDF used as HTML image.

This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…

A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…

A tool that allows you to search for vulnerable android devices across the world and exploit them.