
desc_race_A15
 markie-dev/desc_race_a15
CVE-2021-30955 iOS 15.1.1 POC for 6GB RAM devices (A14-A15)
binary-exploitationexploitationios-security+2
484 years ago
markie-dev/desc_race_a15CVE-2021-30955 iOS 15.1.1 POC for 6GB RAM devices (A14-A15)
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
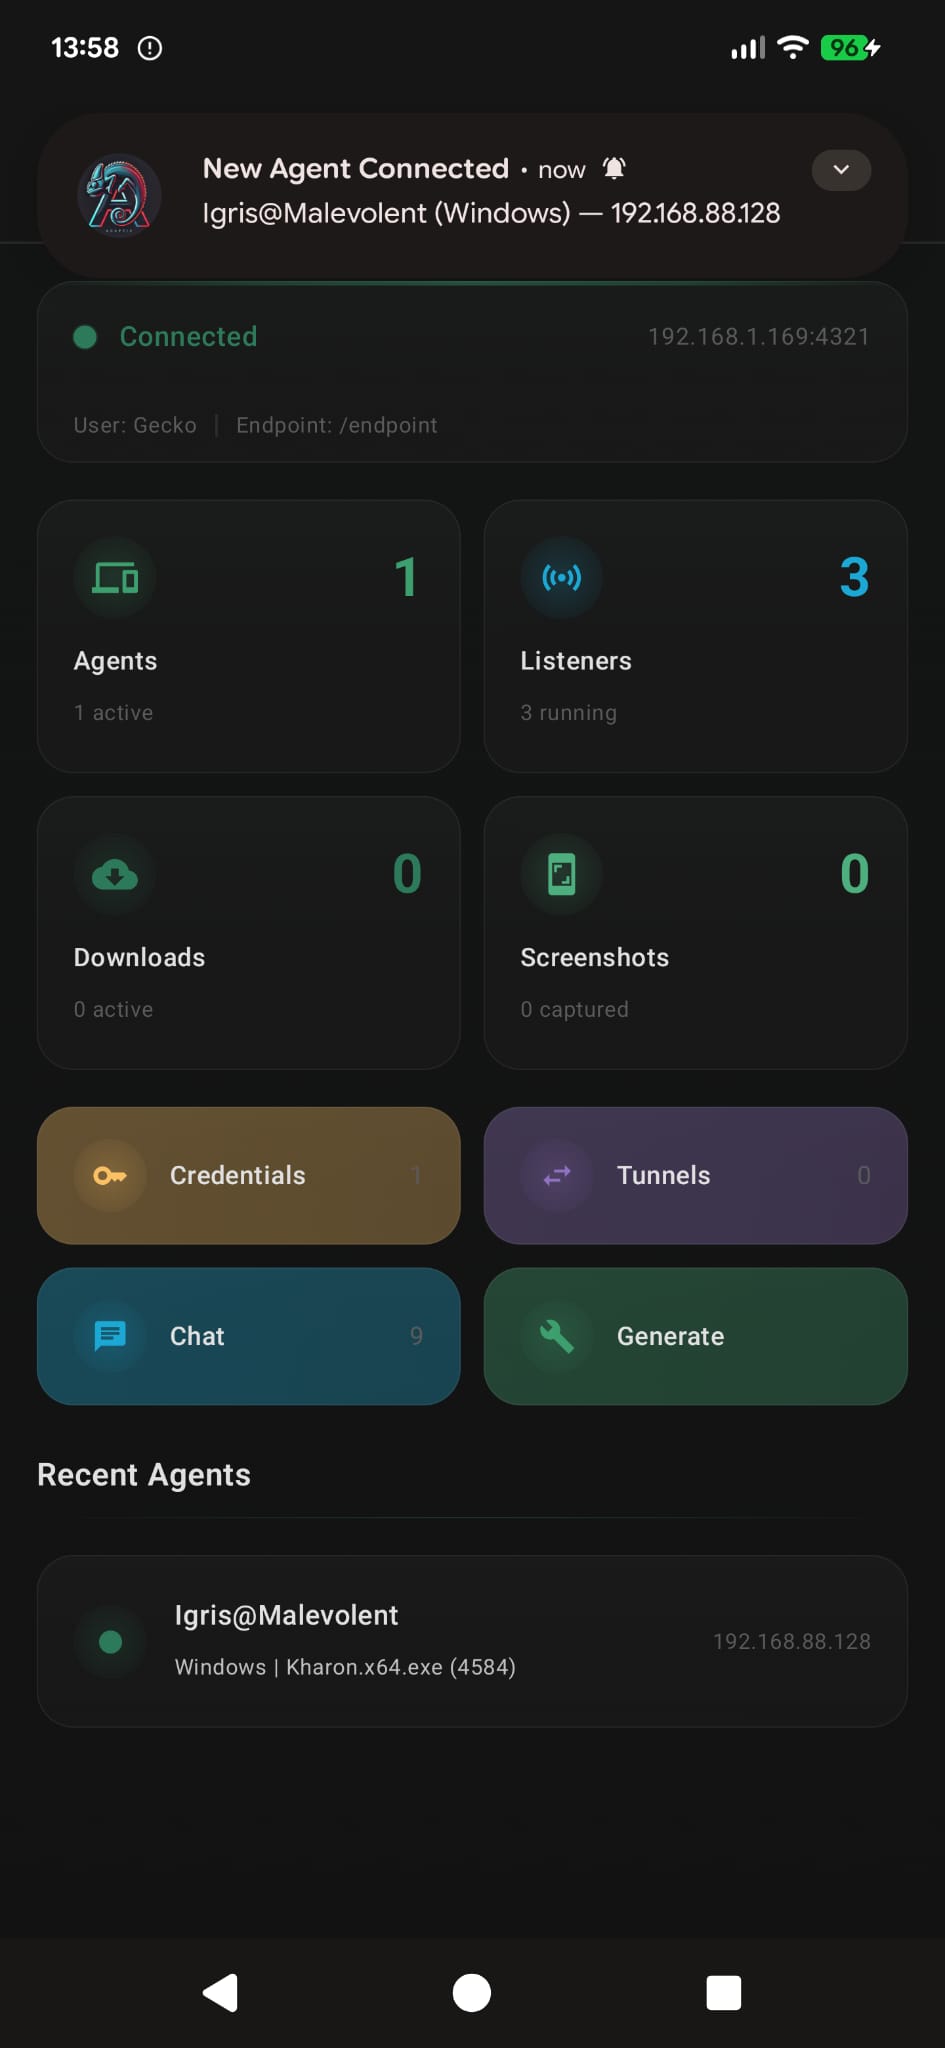 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 laginimaineb/cve-2014-4322
C exploit for Android kernel vulnerability CVE-2014-4322, enabling privilege escalation on affected devices through a crafted application.
 ankitrawatgit/iqoo-z9_5g-vivo-t3_5g-root-ghostlock
An iQOO Z9 5G and vivo T3 5G jailbreak/root CVE-2026-43499 Android application and payloads. Both devices use the MediaTek Dimensity 7200 (MT6886)…
 thegammasqueeze/bootloader_unlock_anbernic_t820
Bootloader unlock using CVE-2022-38694 for Anbernic Unisoc T820 devices
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 aemmitt-ns/skeleton
Zero-click remote code execution exploit for CVE-2021-0326 targeting Android devices, including the Peloton Bike, with a proof-of-concept requiring…
 p1gl3t/cve-2015-1474_poc
Proof-of-concept exploit for CVE-2015-1474, demonstrating a rogue parcel crash in Android SurfaceFlinger via deserialization, enabling privilege…
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 hiikezoe/diaggetroot
Exploit for CVE-2012-4220 providing root privilege escalation on Android devices via a kernel vulnerability.
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
 xingchenrs/cybermeowfians
The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?
 leochen-coremind/spd_flasher
CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices
 hiikezoe/libfb_mem_exploit
CVE-2013-2596 memory corruption exploit for Android devices, targeting a kernel vulnerability to achieve privilege escalation.
 diabl0w/cve-2022-22057_sm-f926u
Qualcomm kgsl driver exploit (CVE-2022-22057) for Samsung Galaxy devices achieving arbitrary kernel memory read/write, SELinux bypass, and temporary…
 fi01/libmsm_cameraconfig_exploit
C exploit for CVE-2013-2595 targeting a kernel memory corruption in Qualcomm MSM camera driver on Android devices, enabling local privilege…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled