frameworks_base_AOSP-4.2.2_r1_CVE-2023-21272

Android framework base repository for AOSP 4.2.2_r1, modified to address CVE-2023-21272, a vulnerability in the Android framework.

Android framework base repository for AOSP 4.2.2_r1, modified to address CVE-2023-21272, a vulnerability in the Android framework.

Android PackageInstaller source code with patch for CVE-2020-0418, a local privilege escalation vulnerability. Provides patched AOSP10 code for…

Android PackageInstaller source code for AOSP 10 r33, patched for CVE-2021-0302, for vulnerability analysis and security research.

iOS app to check device compatibility with CVE-2021-30937 vulnerability, displaying alerts and popups during the process.

Android KeyChain package with patch for CVE-2021-0963, addressing a security vulnerability in AOSP 10.

Android Settings package with a patch for CVE-2020-0201, addressing a security vulnerability in the Settings application.

Targeted reference for CVE-2023-21125, an Android BlueDroid Bluetooth vulnerability, with code and documentation focused on the affected component.

CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13

This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…

Provides AOSP Android Settings source for Android 10 r33, tagged with CVE-2022-20360 for vulnerability reproduction and patch analysis.

Android AOSP 10 framework base repository containing the fix for CVE-2023-21097, a vulnerability in the Android framework that could lead to local…

Analyzes and patches Android framework vulnerability CVE-2021-20138 in AOSP 10, providing security fixes for mobile platforms.

ES File Explorer Open Port Vulnerability - CVE-2019-6447

AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…

Android app to scan for bash Vulnerability - CVE-2014-6271 also known as Shellshock

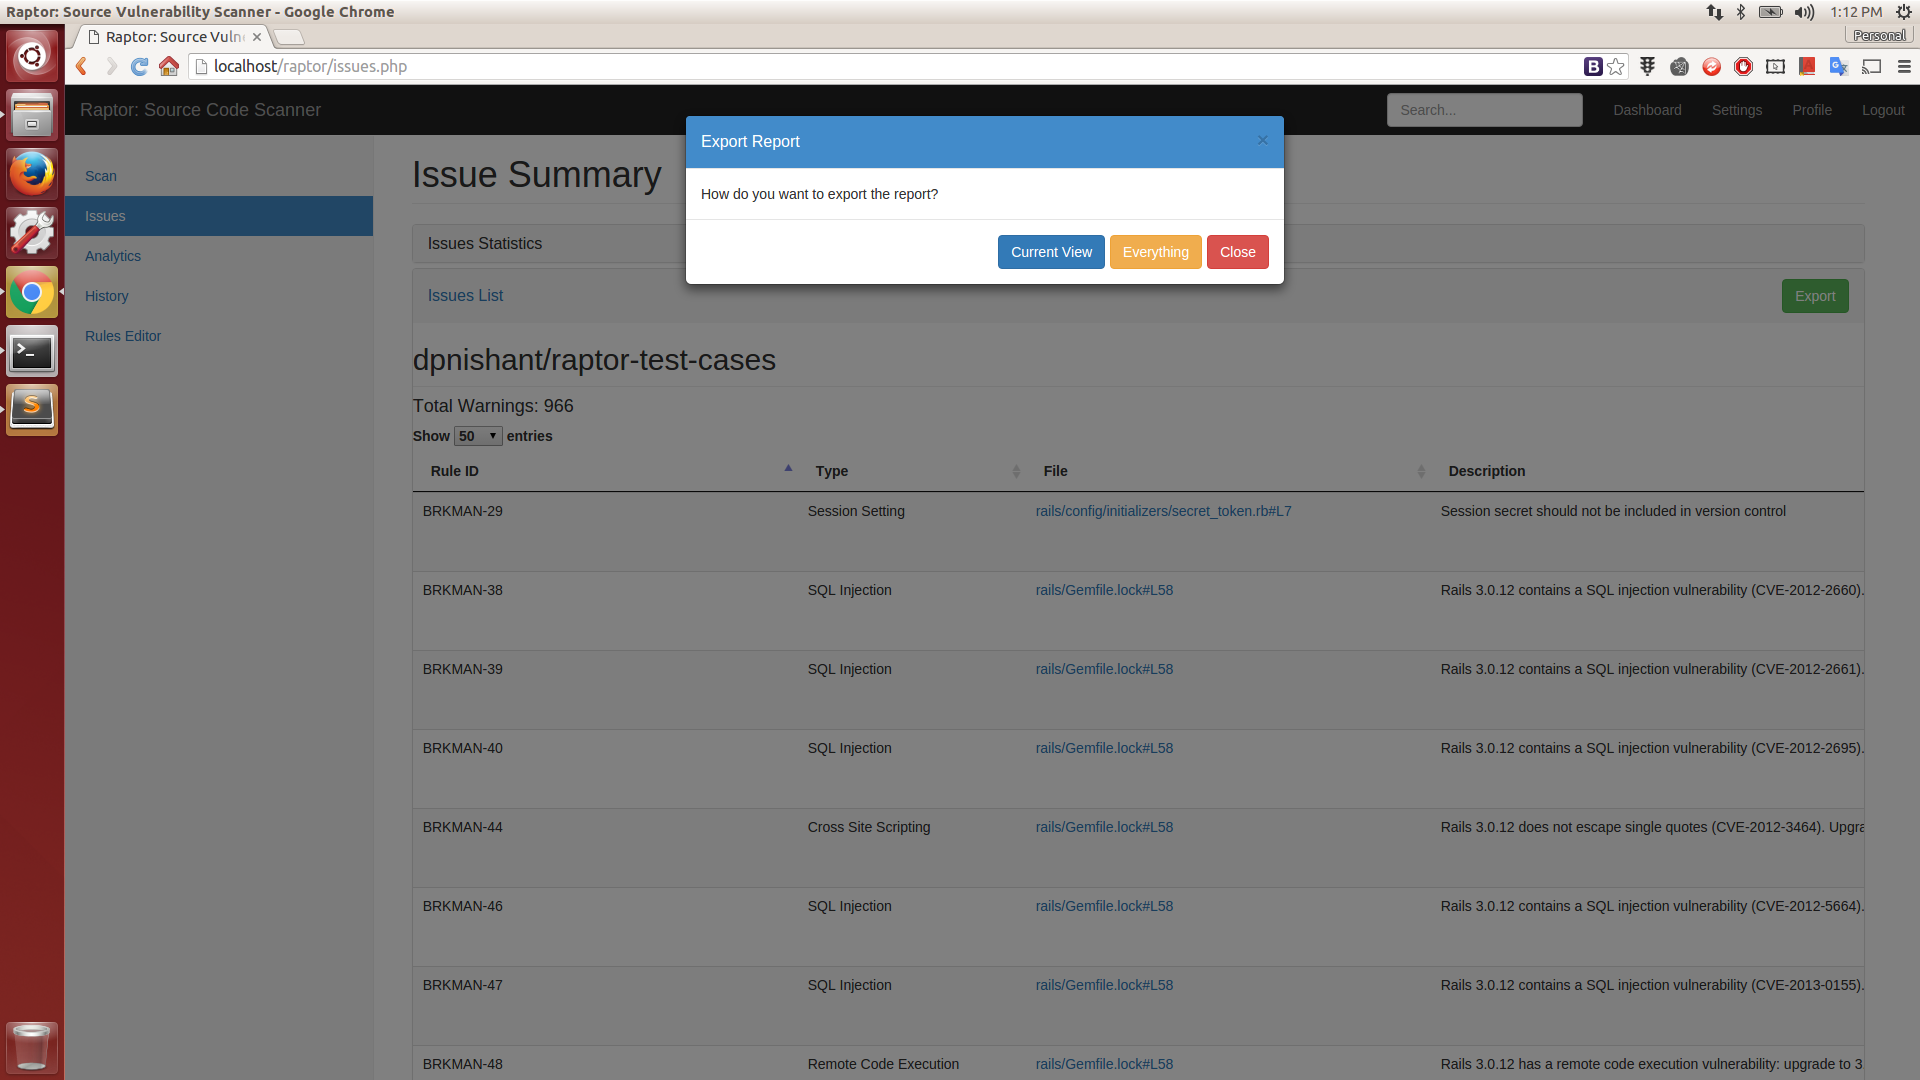
Web-based Source Code Vulnerability Scanner

CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android

Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.