
ipatool
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
information-gatheringios-securitymobile-app-pentesting+2
11.5k
majd/ipatoolCommand-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
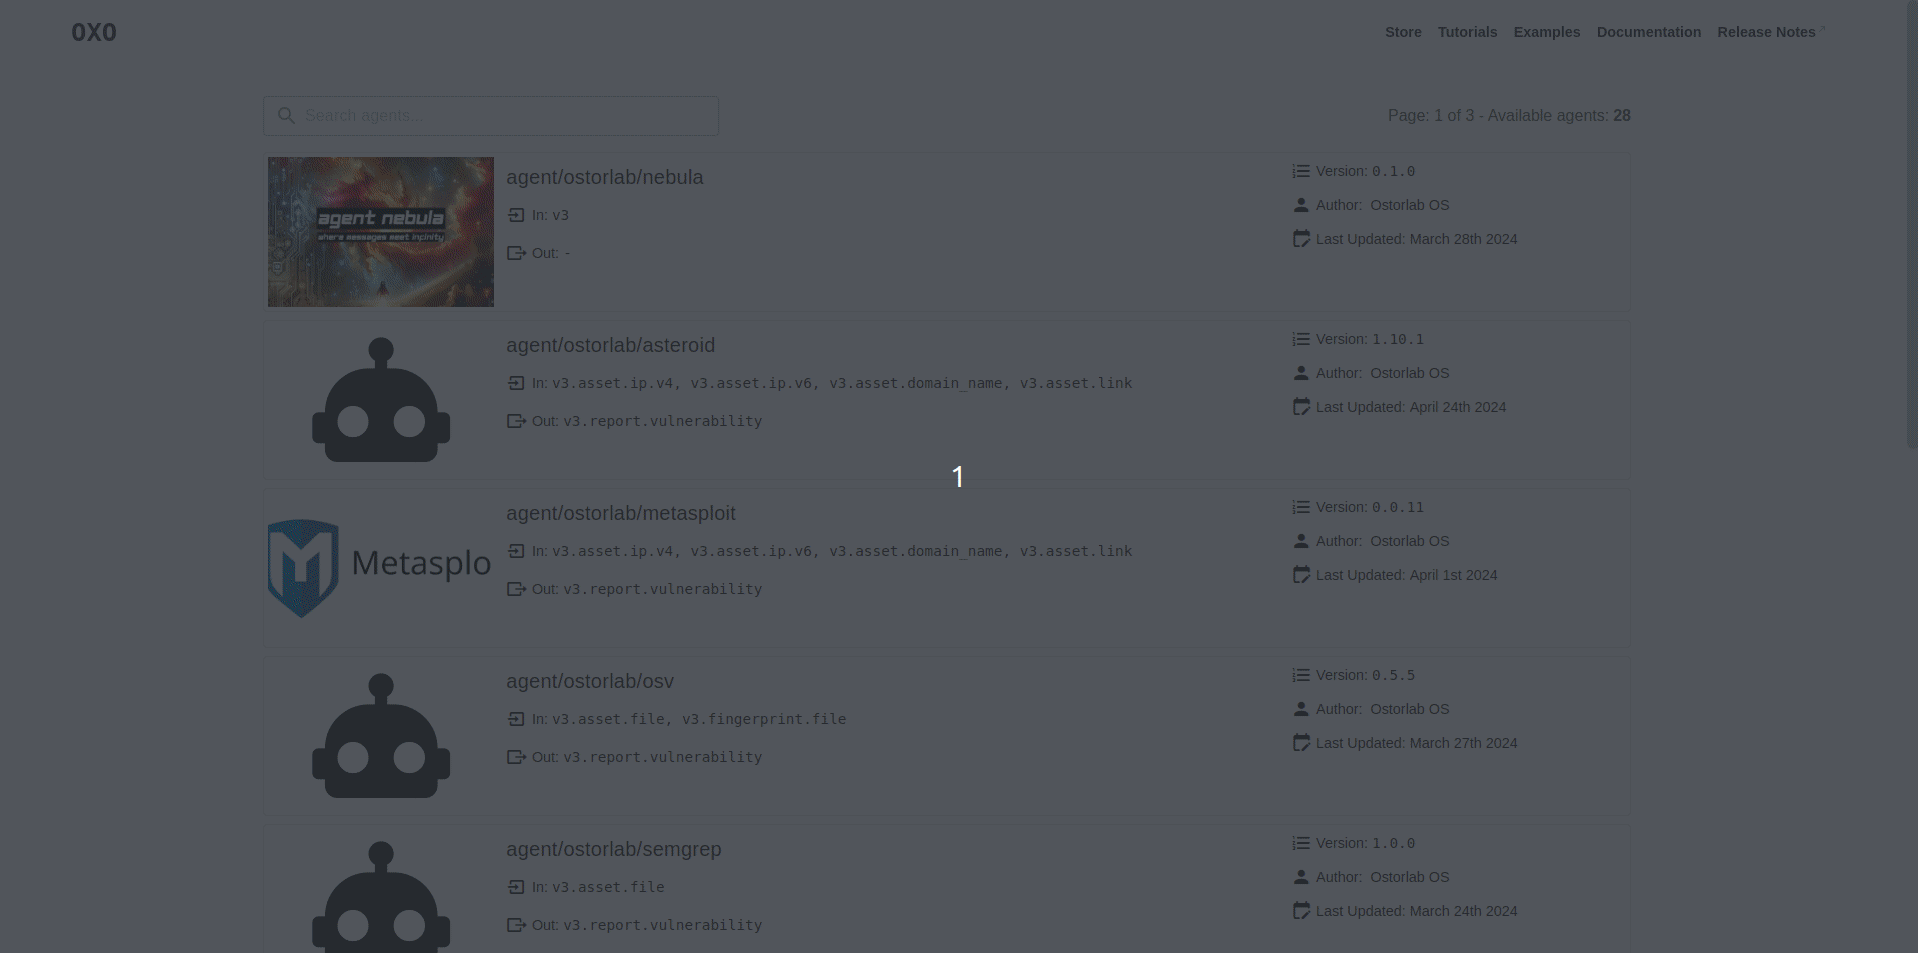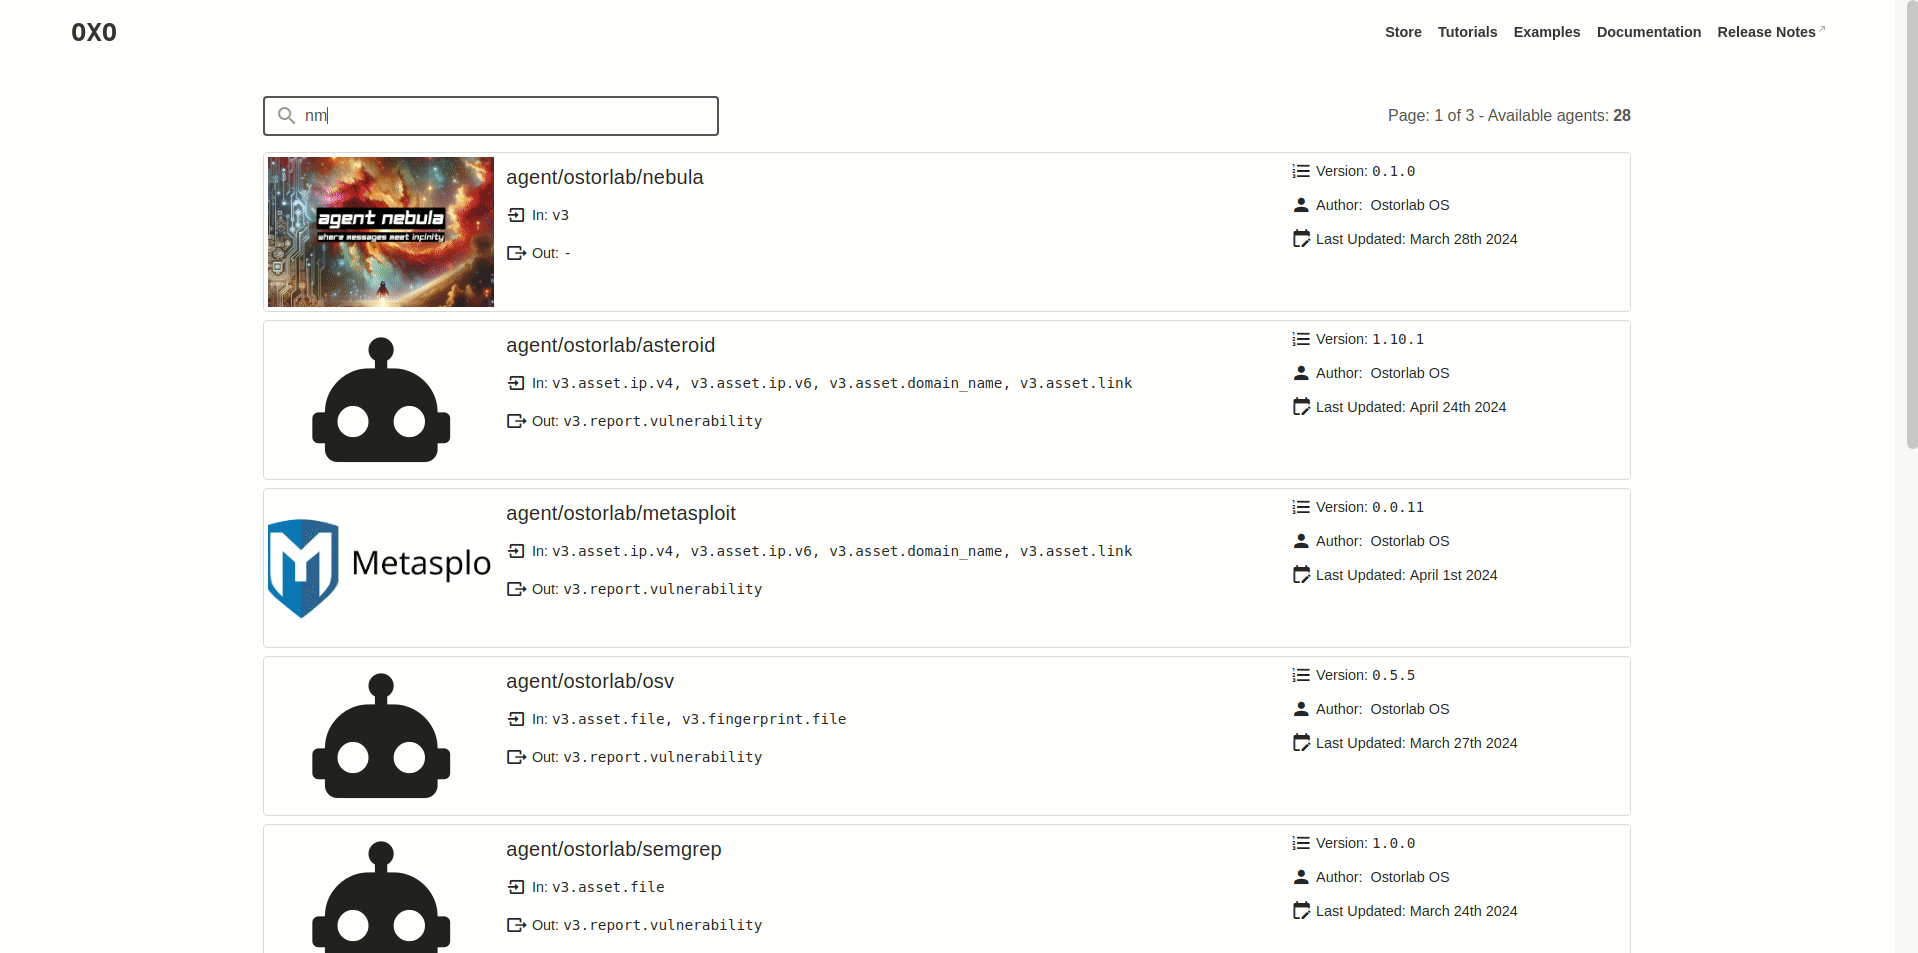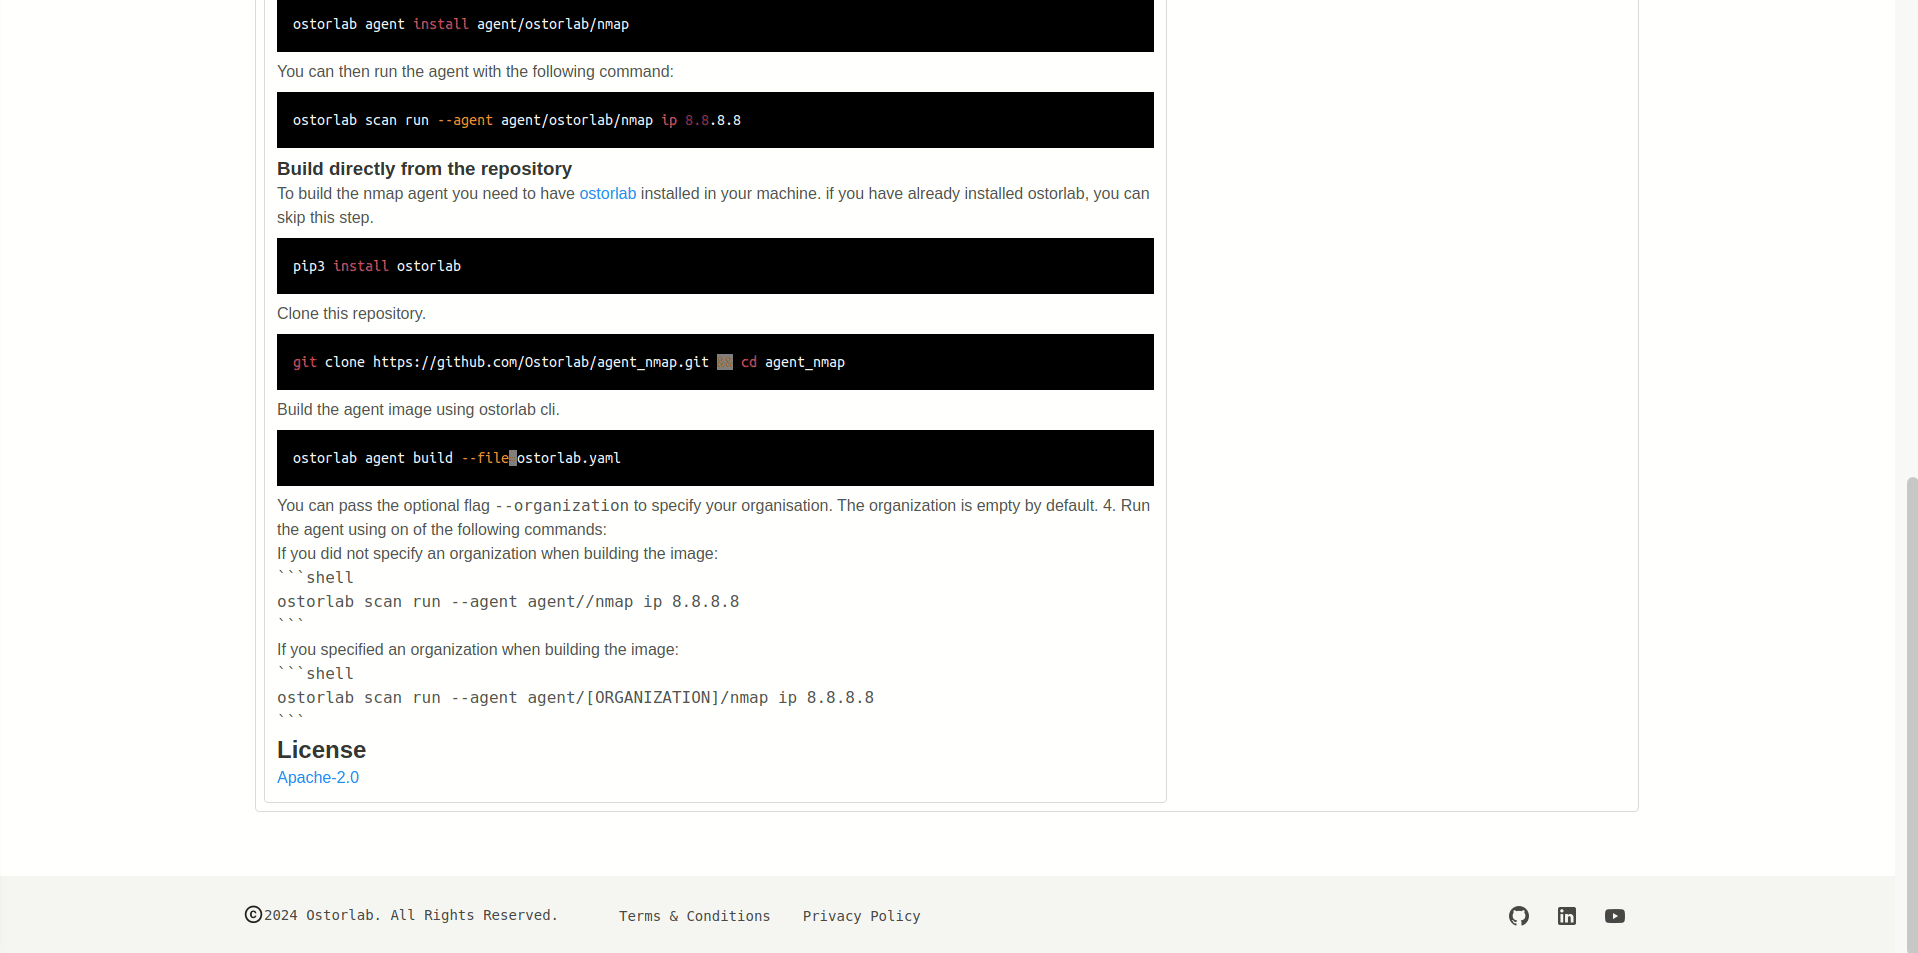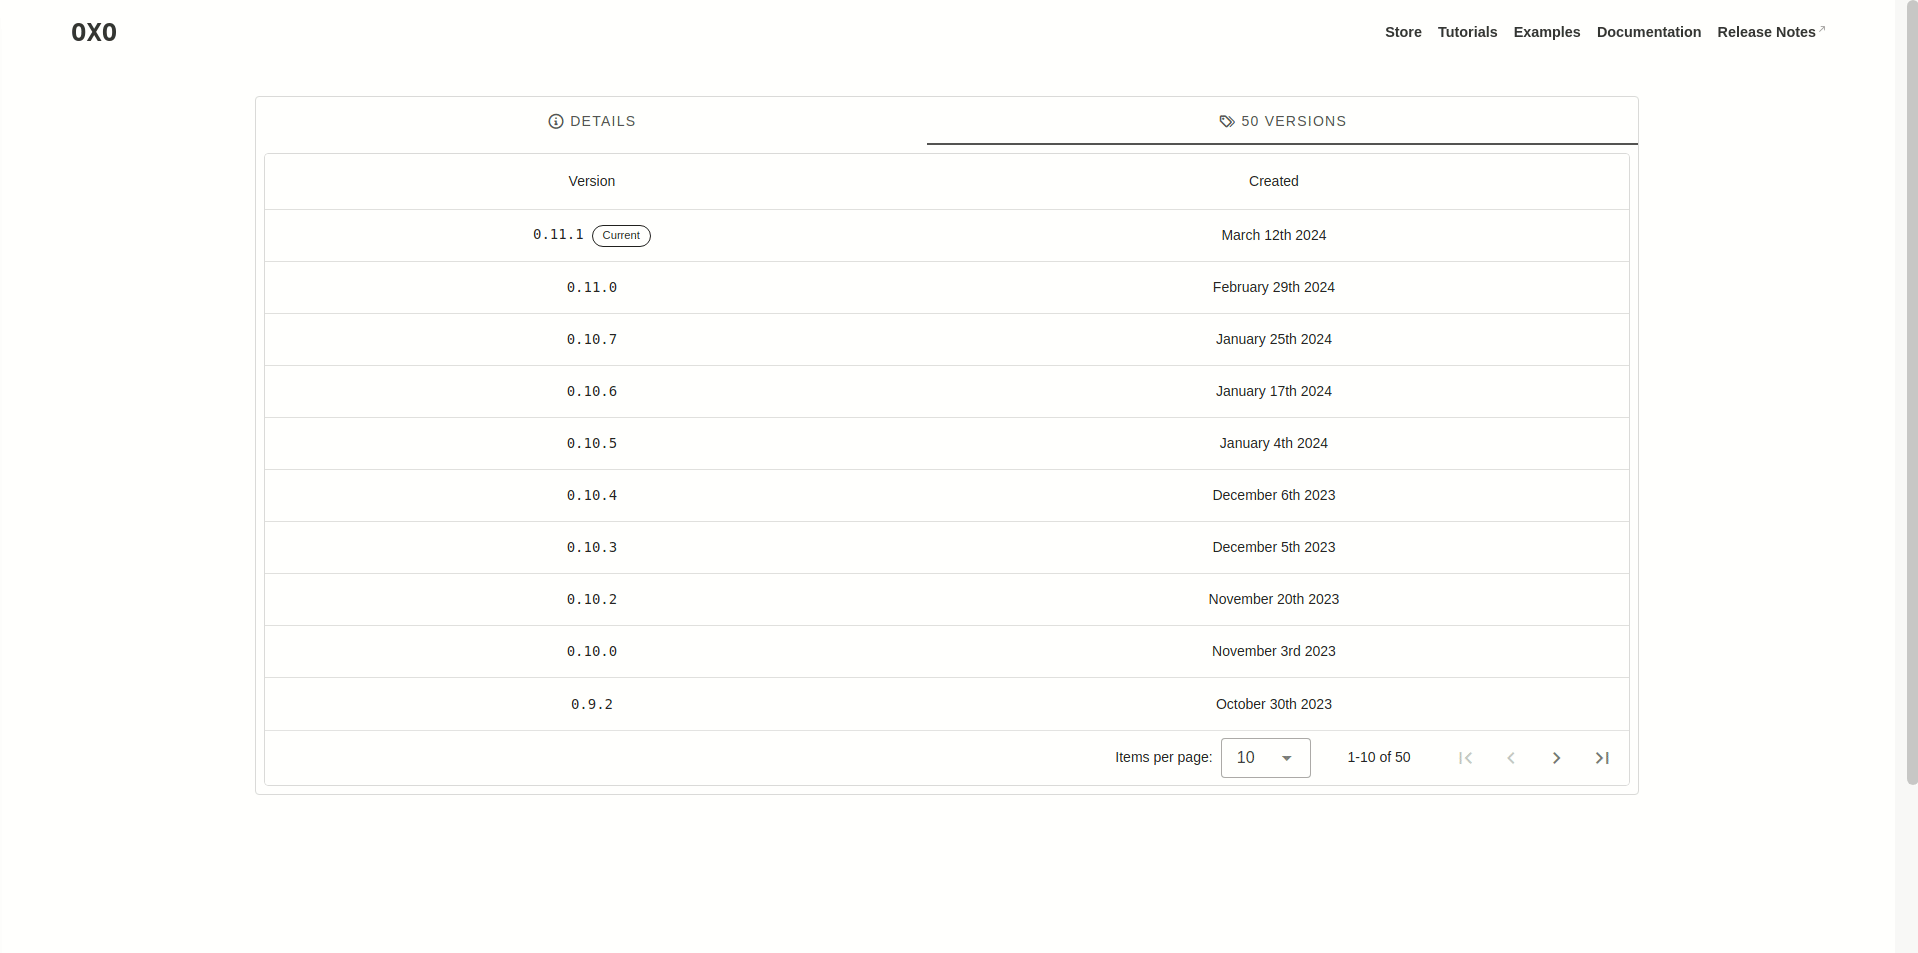 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 justrach/kuri
Browser automation, web crawling, and iOS + Android device control for AI agents. Zig-native, token-efficient CDP snapshots, HAR recording, native…
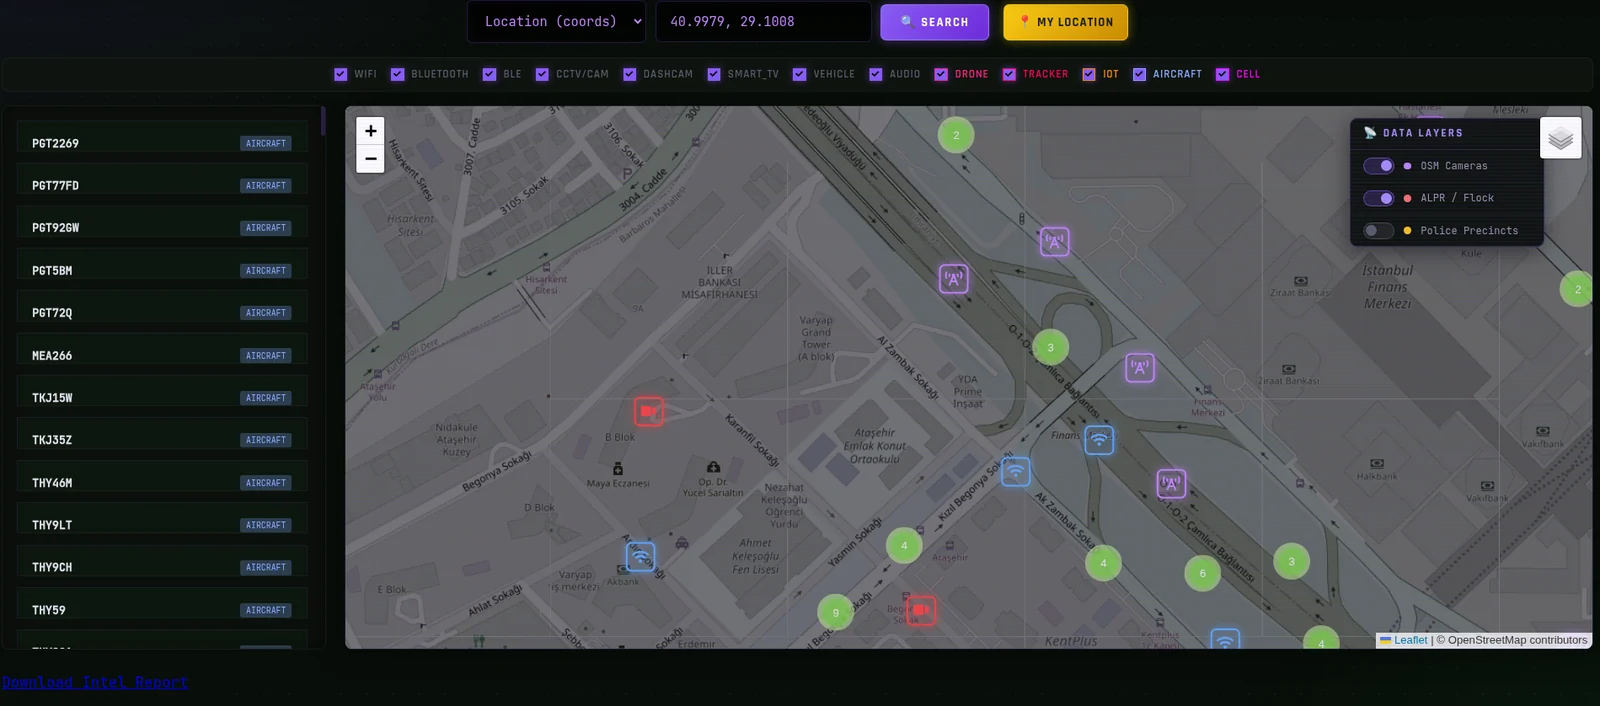 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
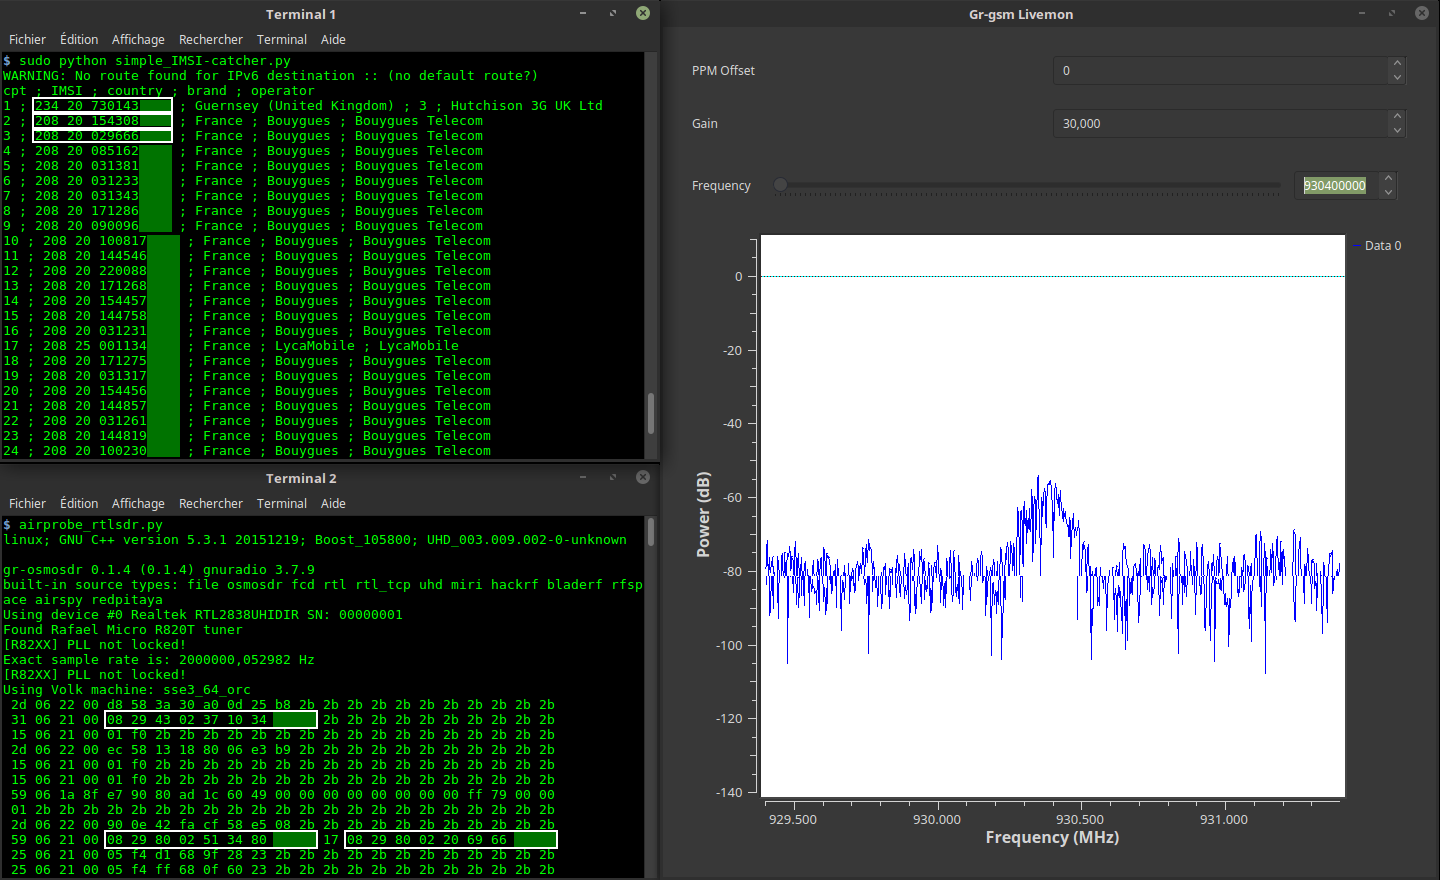 oros42/imsi-catcher
This program show you IMSI numbers of cellphones around you.
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 ajayantoisdev/wasonar
WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…
 kinghacker0/whatsapp-osint
WhatsApp OSINT tool for retrieving profile photos, verifying Business accounts, checking user status, analyzing linked devices, and reviewing privacy…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
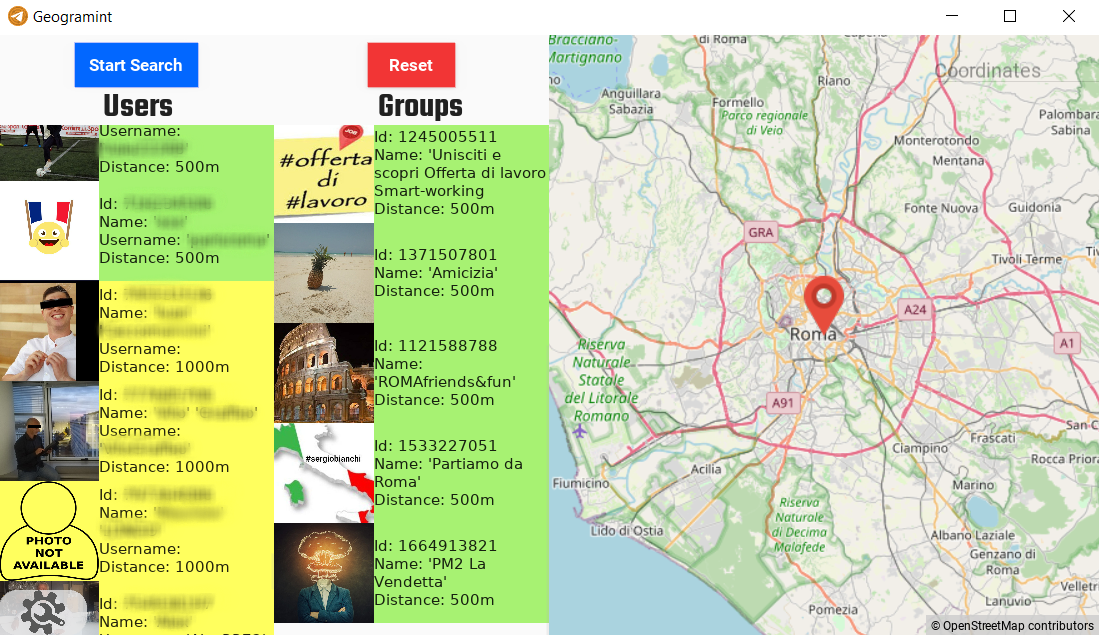 alb-310/geogramint
An OSINT Geolocalization tool for Telegram that find nearby users and groups 📡🌍🔍
 sc1341/instagramosint
An Instagram Open Source Intelligence Tool - Archive
 biscuitehh/cve-2023-40429-ez-device-name
CVE-2023-40429: An app may be able to access sensitive user data.
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.
 biscuitehh/cve-2022-46718-leaky-location
CVE-2022-46718: an app may be able to read sensitive location information.