
mas-website
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
android-securitycurated-resourceseducation+4
13
owasp/mas-websiteThe OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
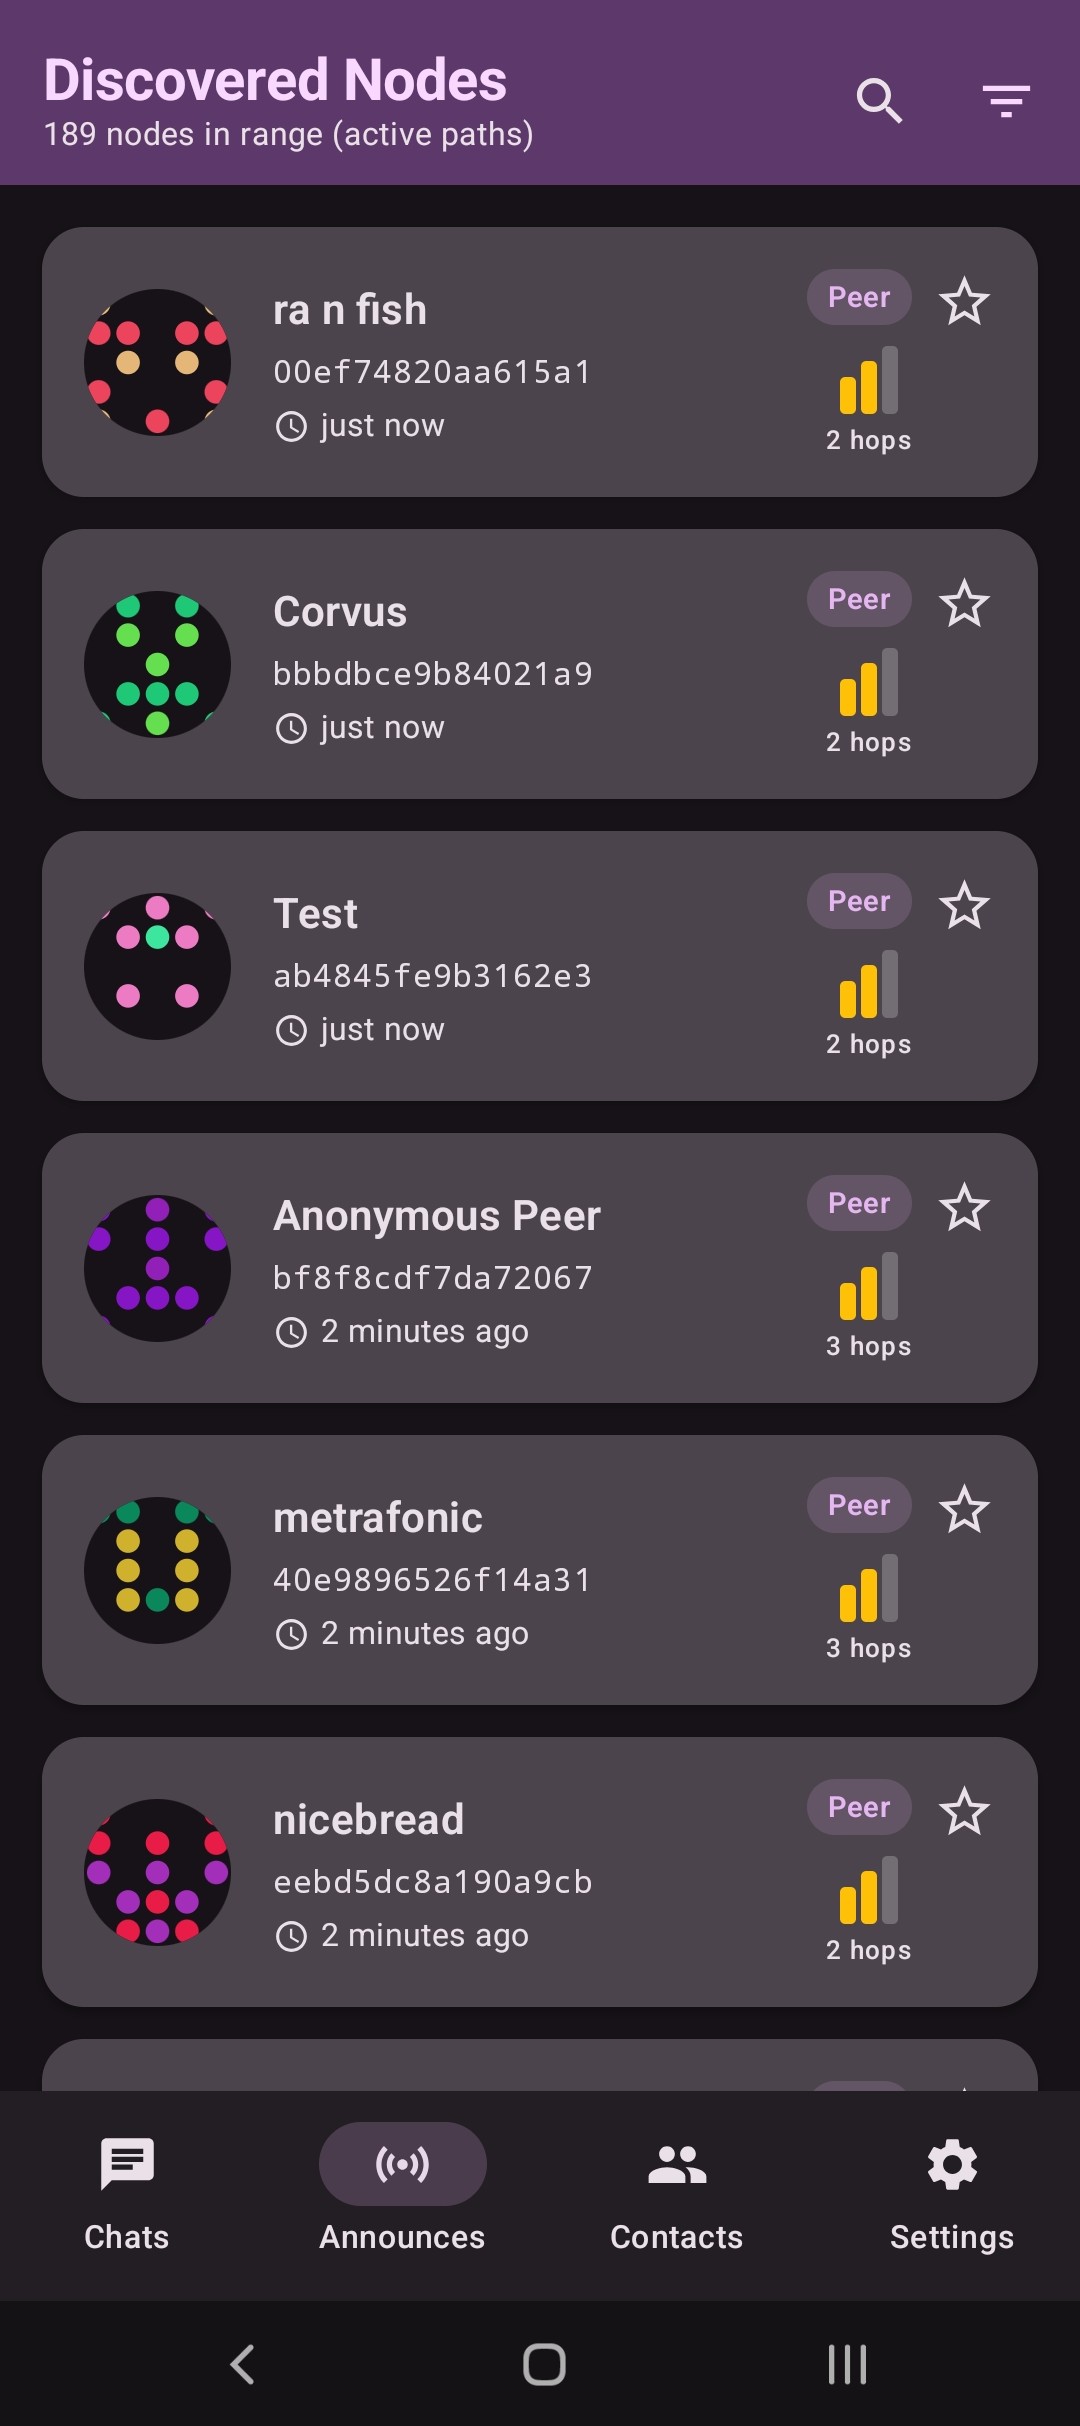 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through the Remote Debugging…
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.