

LIEF
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k
lief-project/liefCross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 androguard/androguard
Reverse engineering and pentesting for Android applications
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
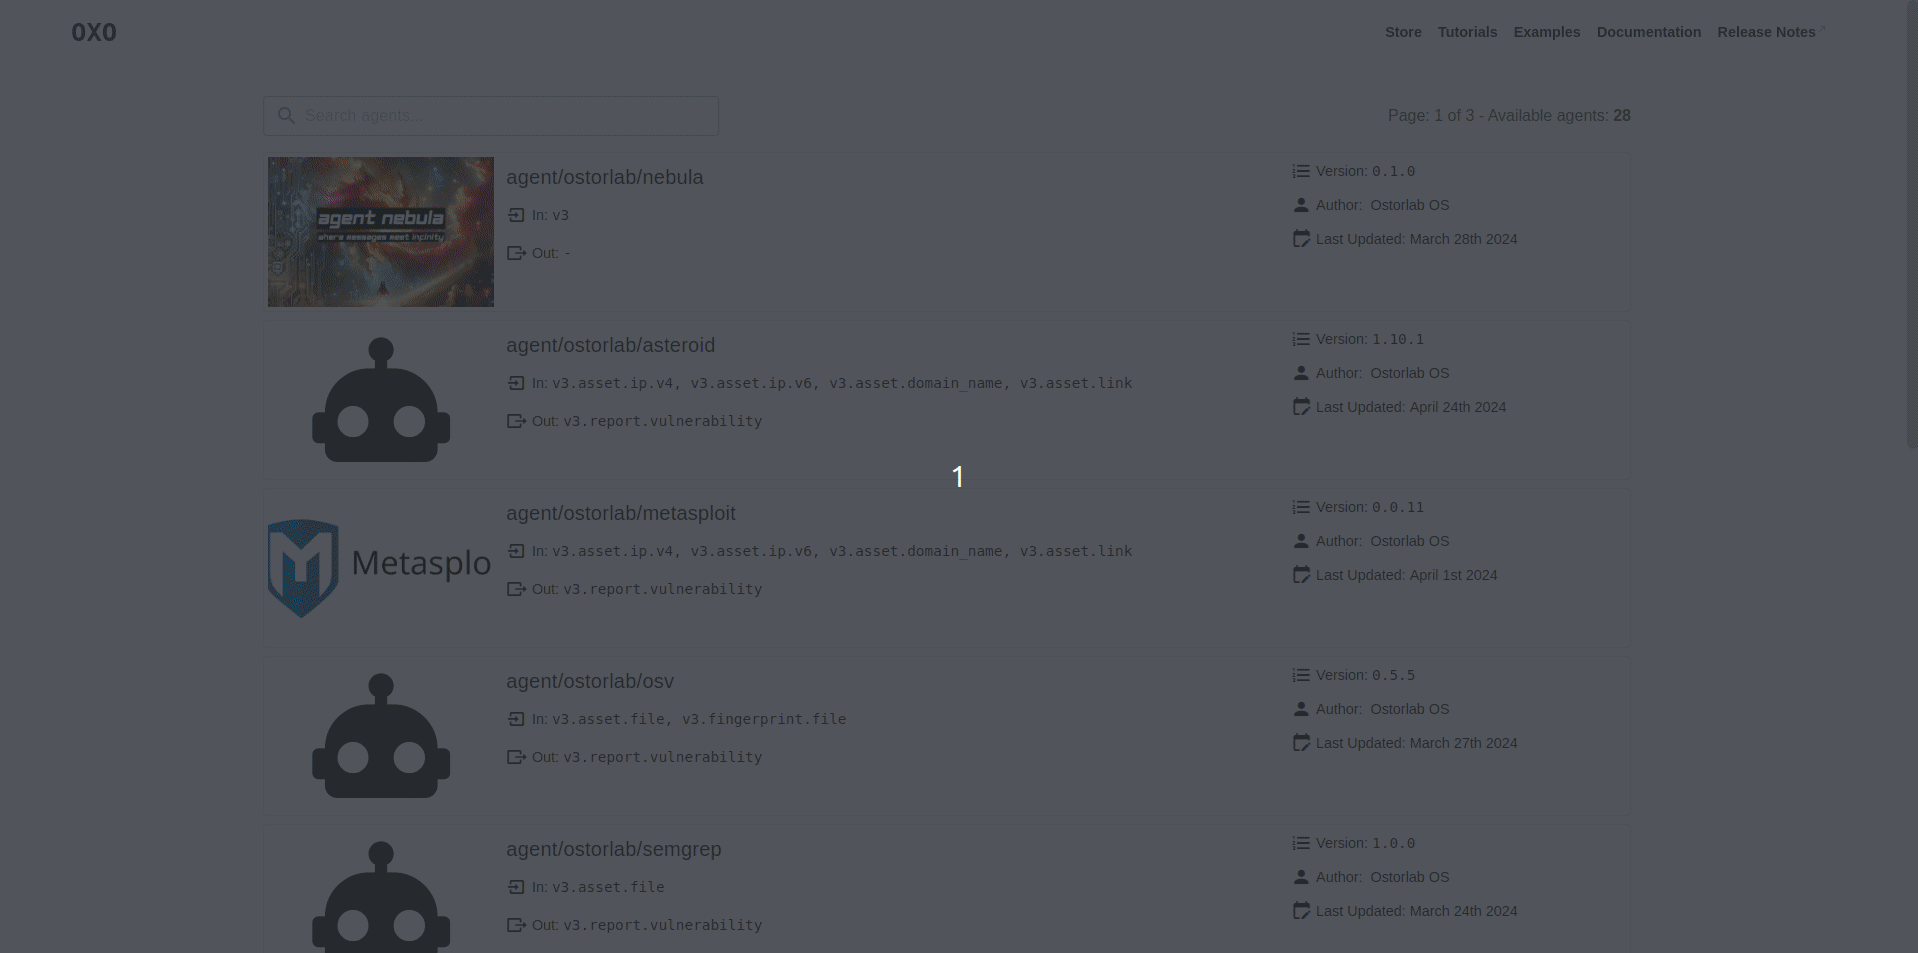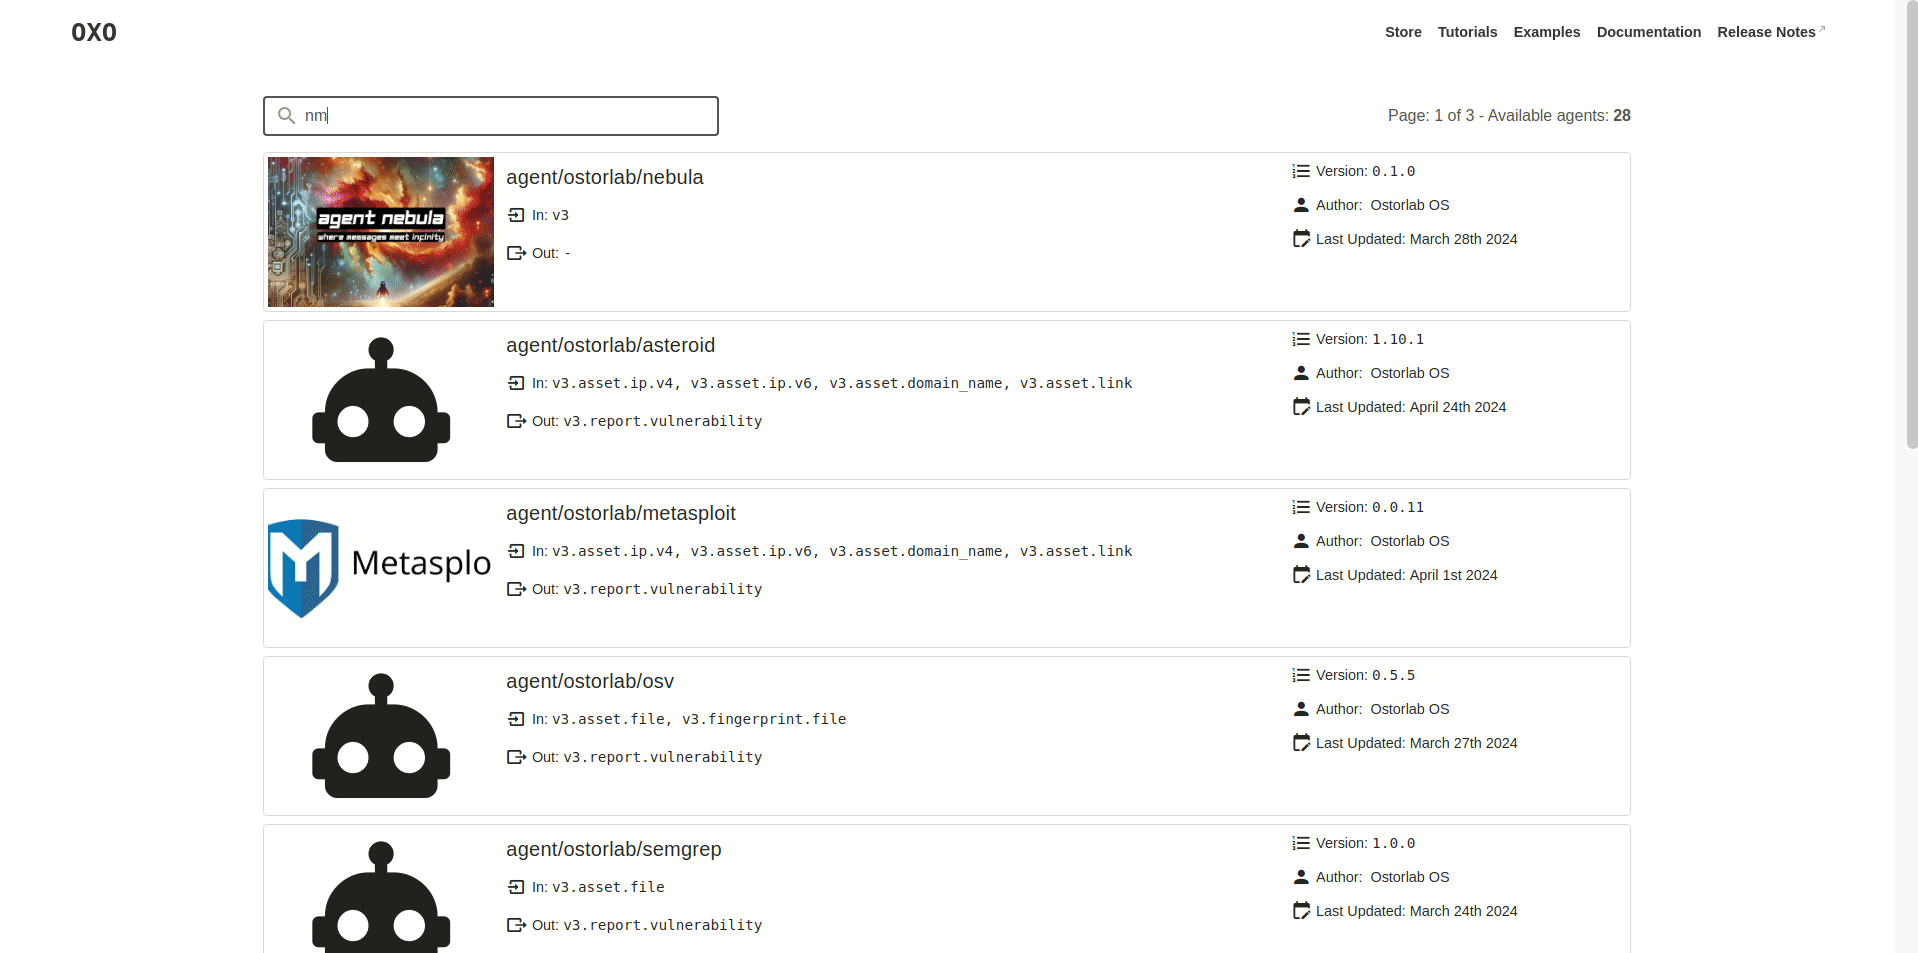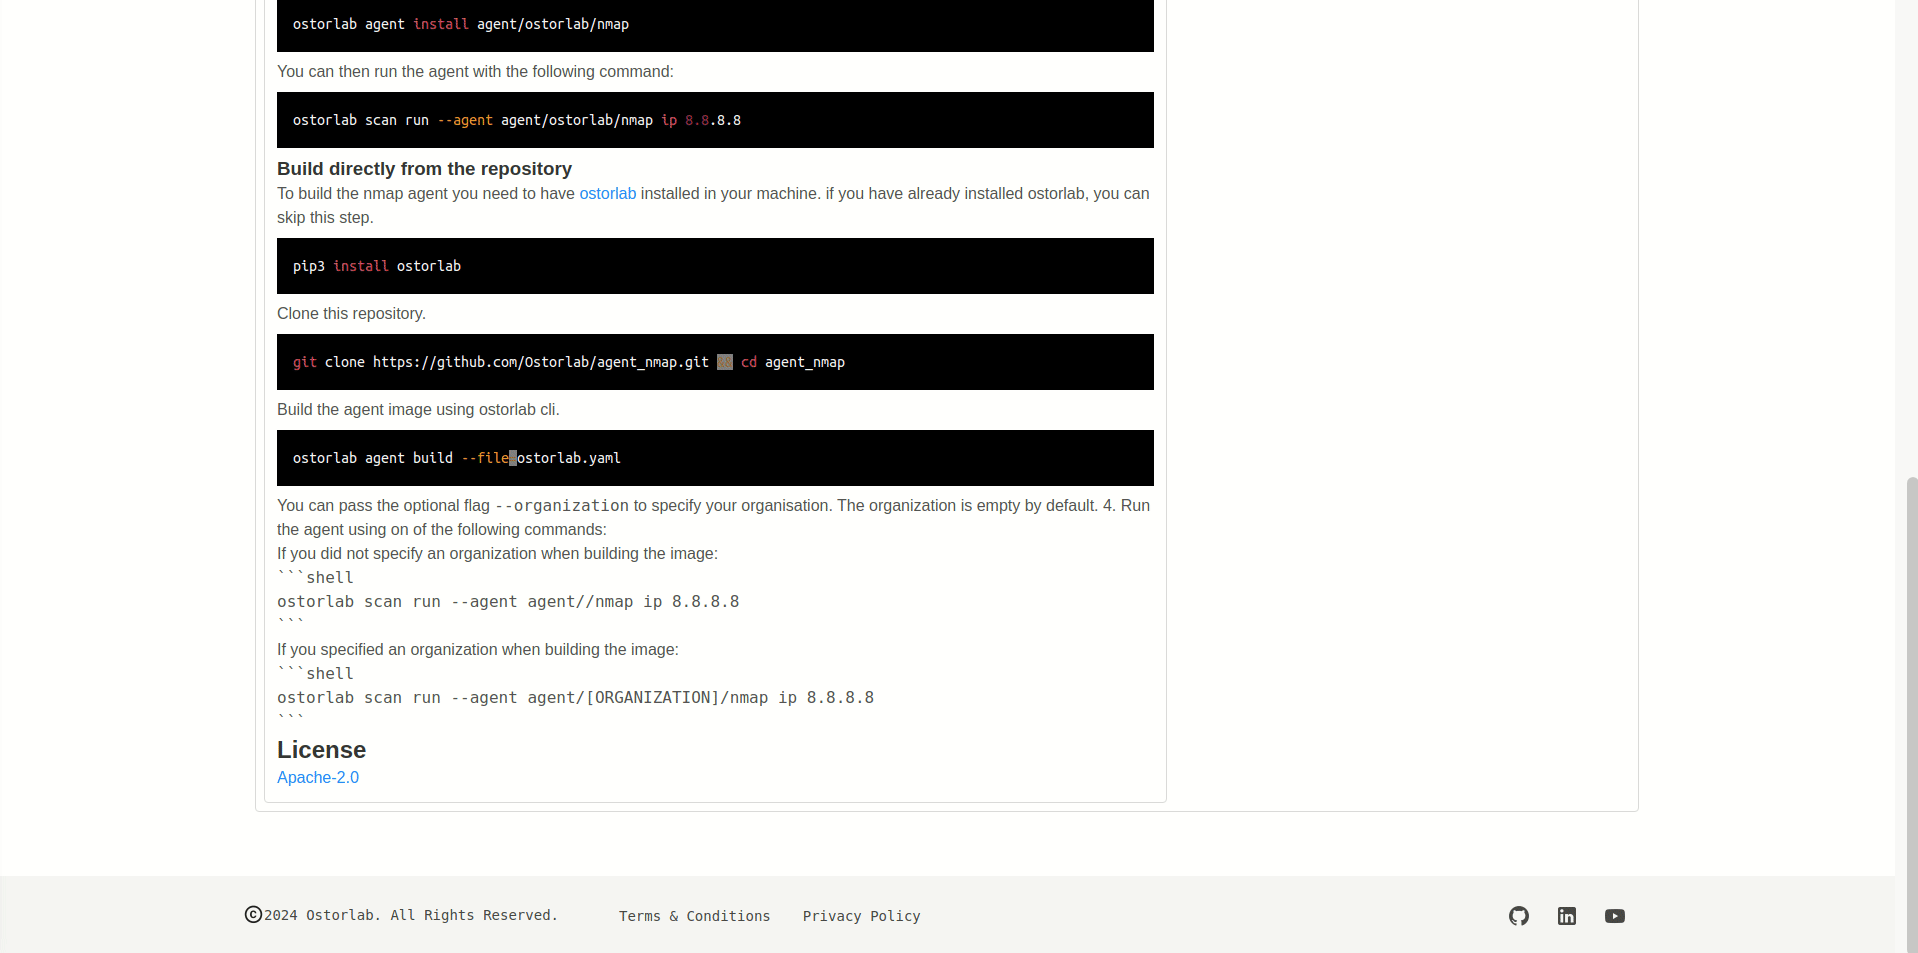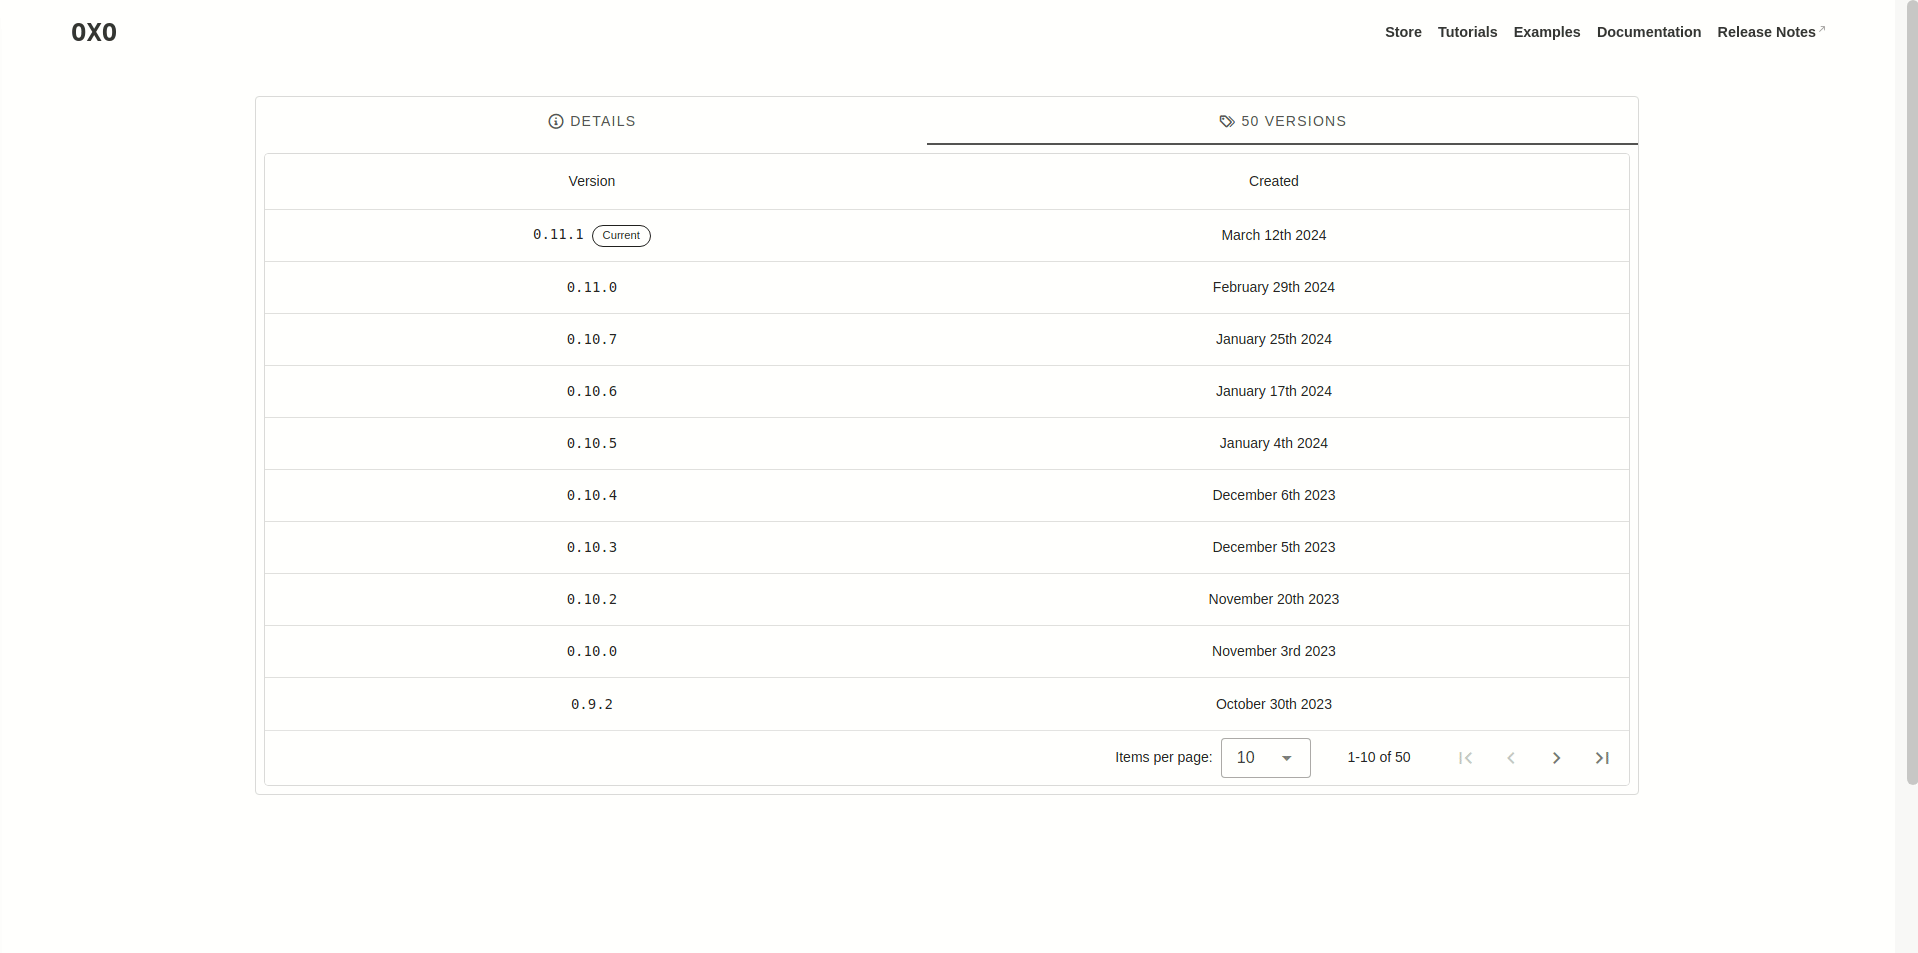 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 frida/frida
Main repo for hosting release binaries
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
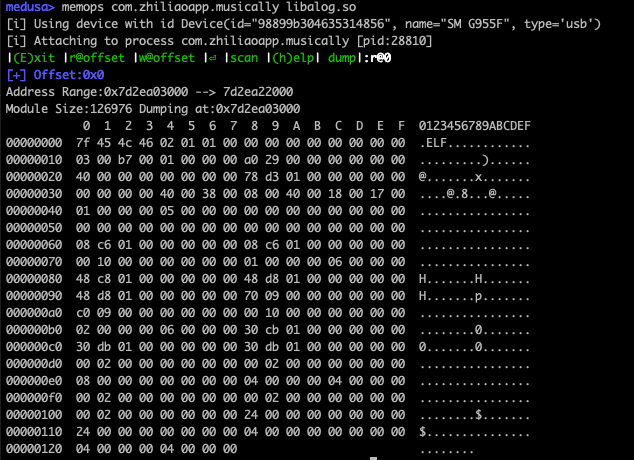 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
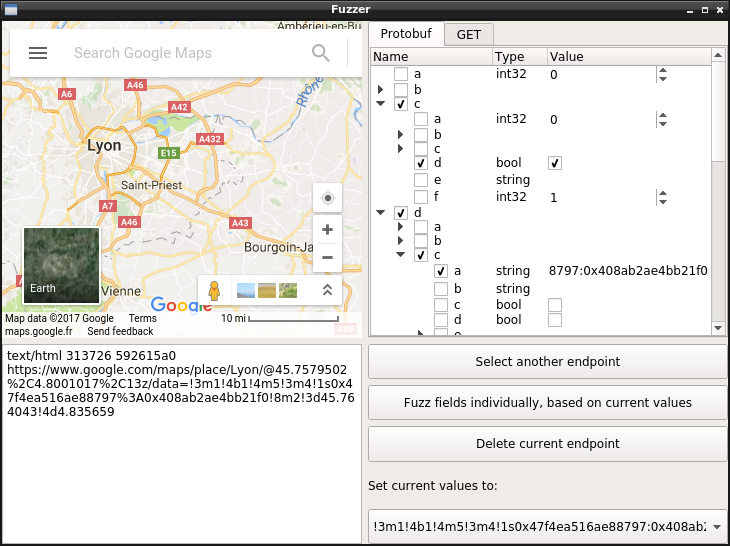 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.