


 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 cellebrite-labs/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
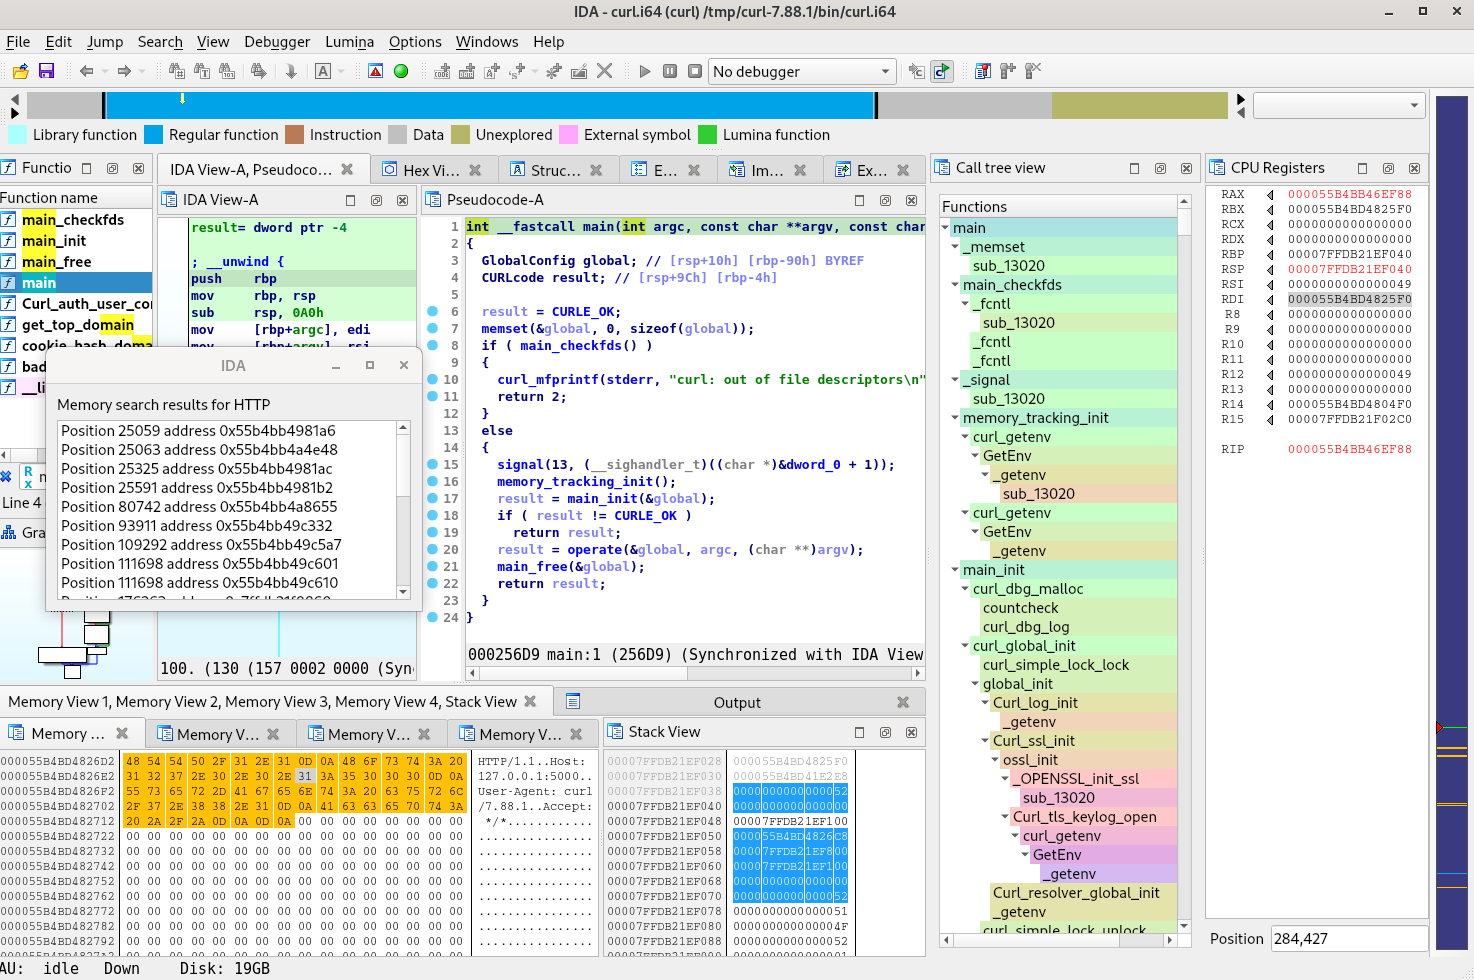 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
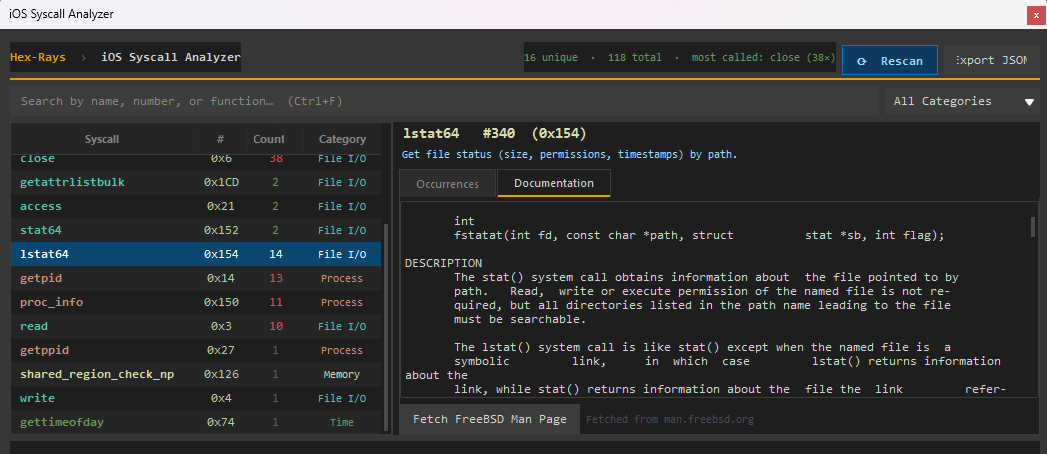 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
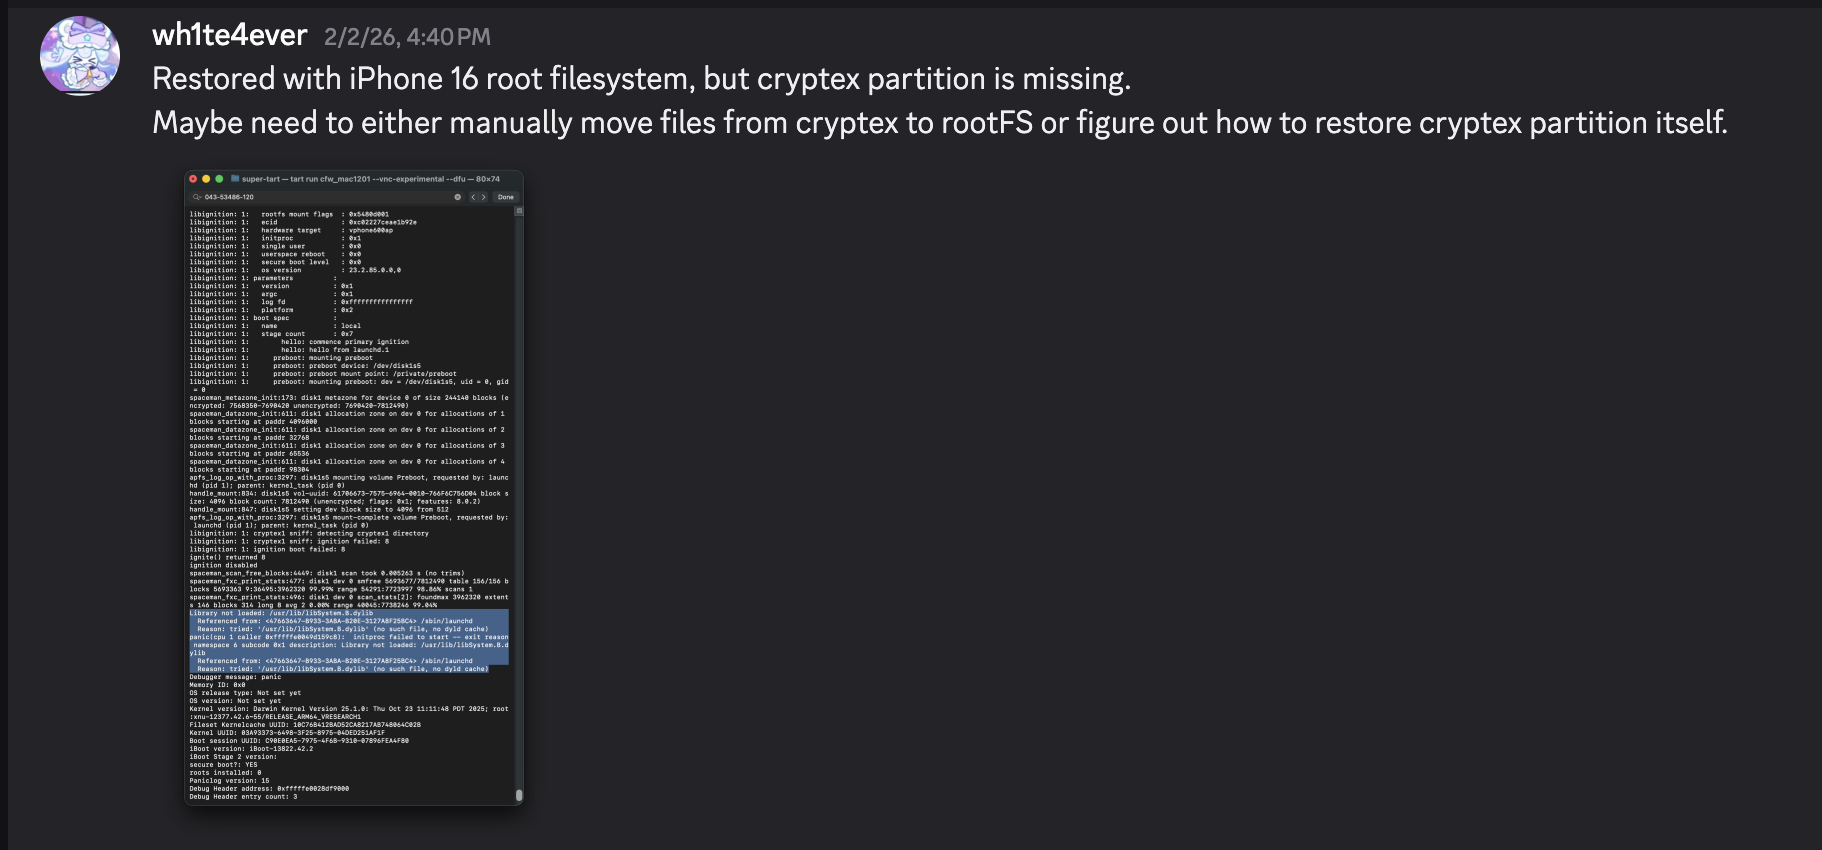 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
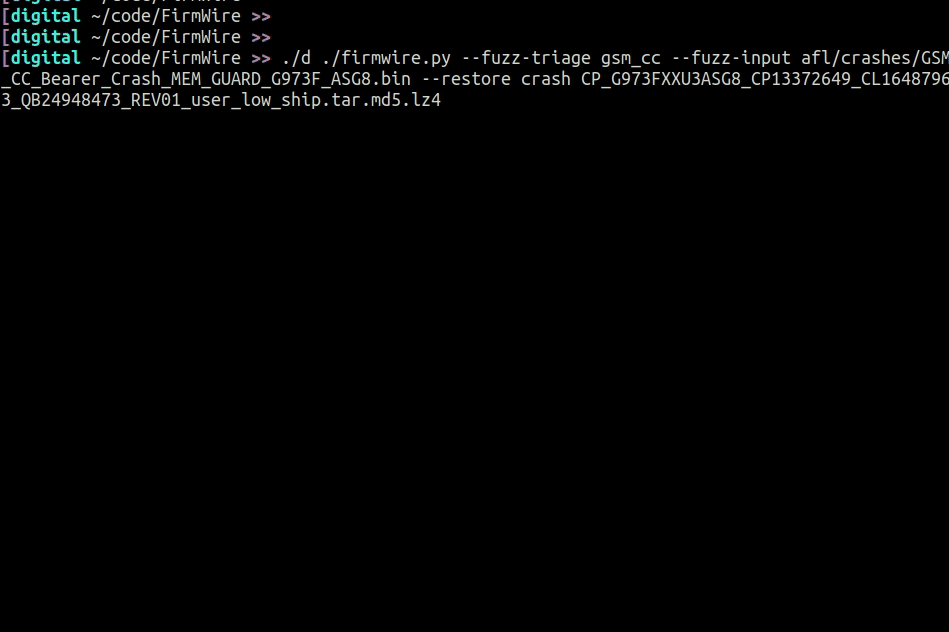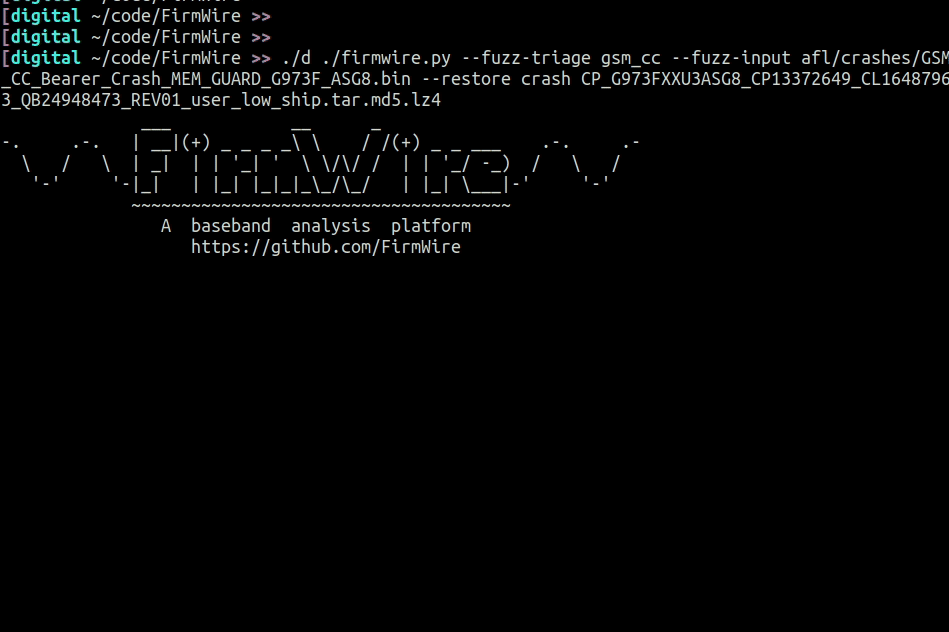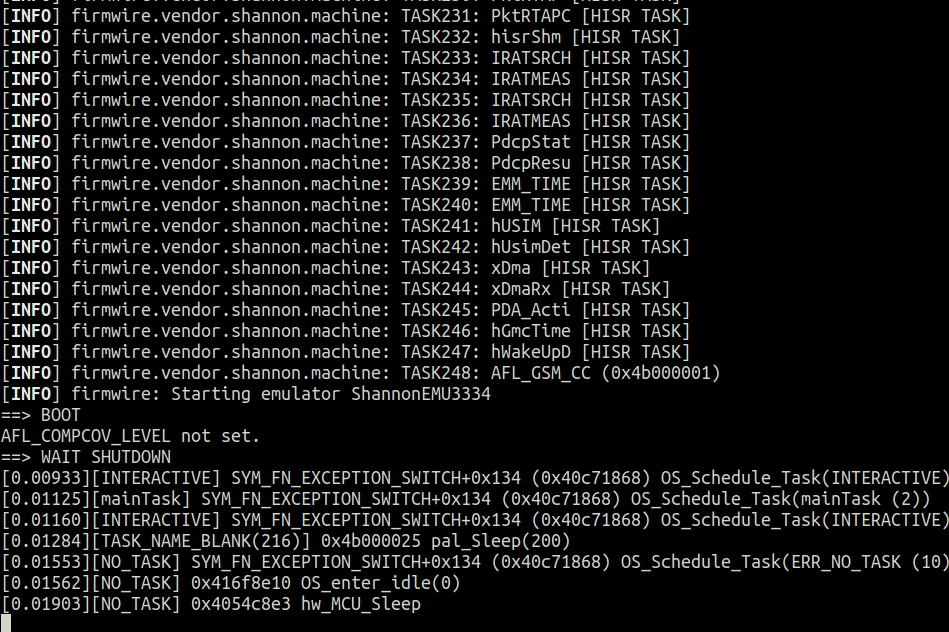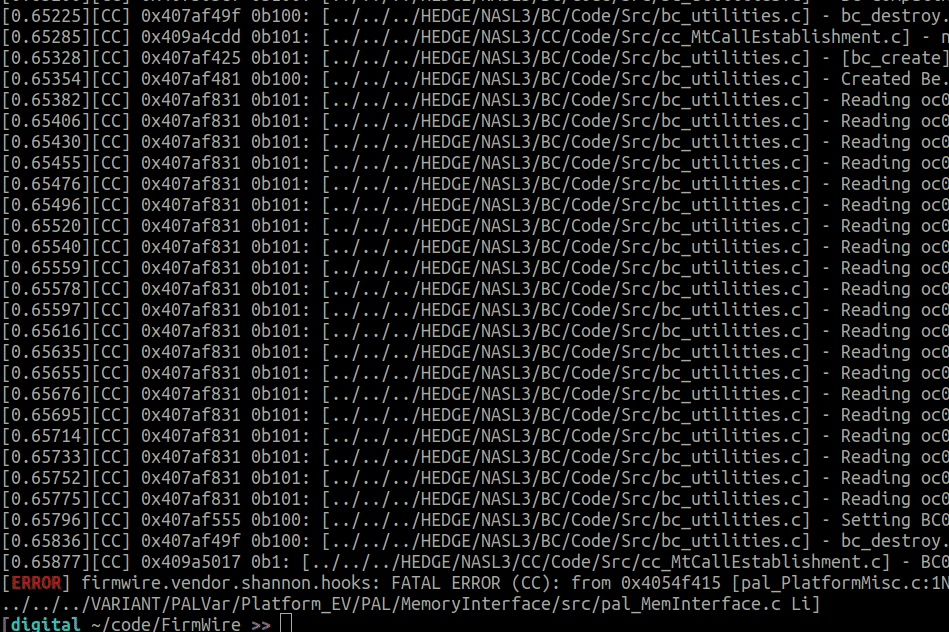 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
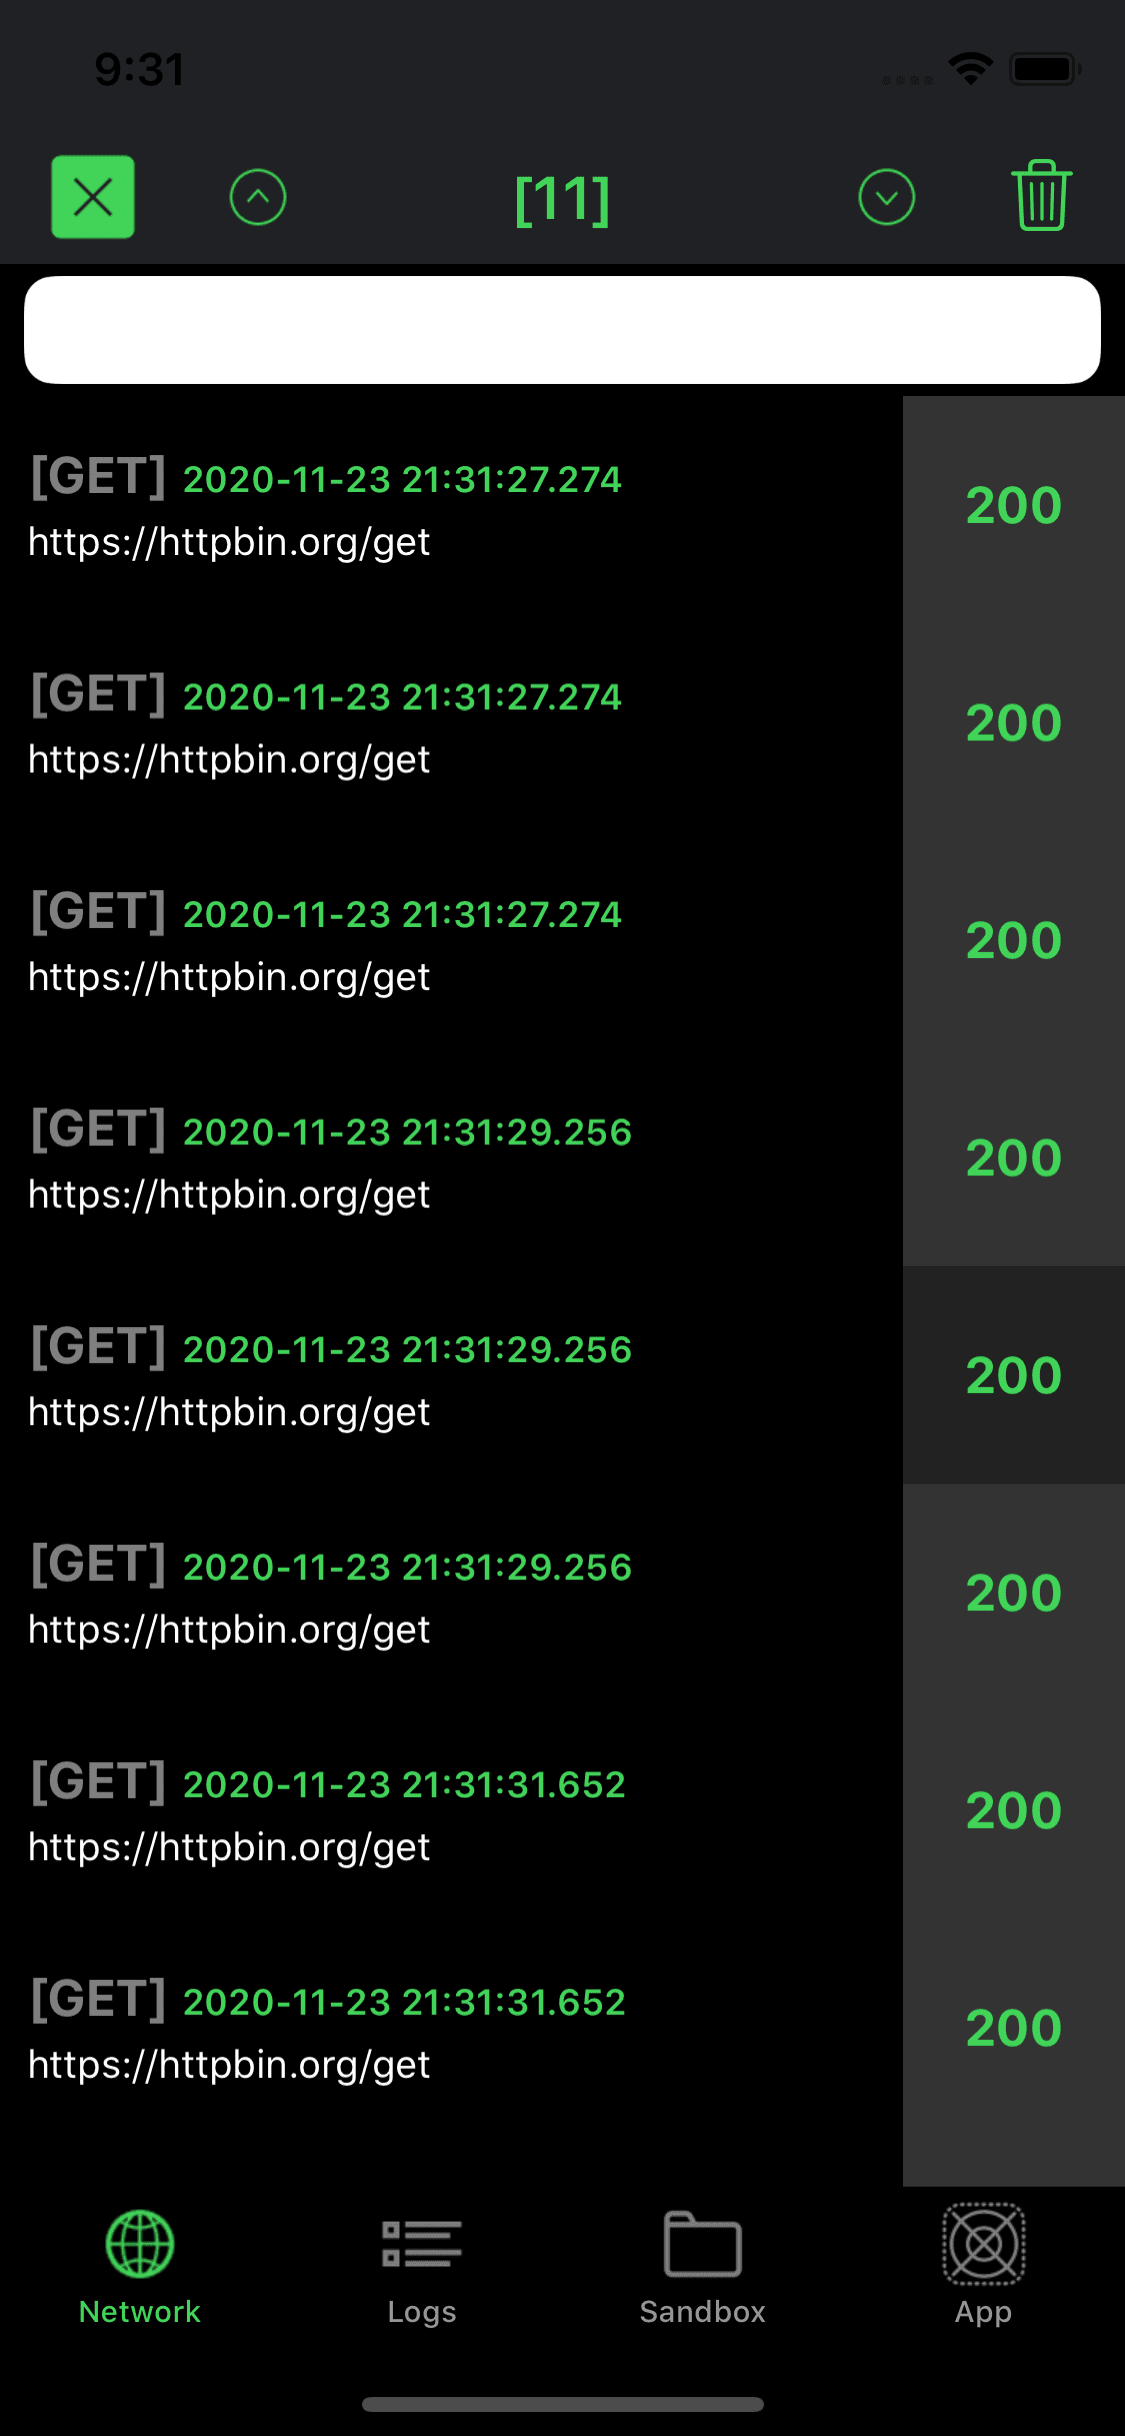 cocoadebug/cocoadebug
iOS Debugging Tool 🚀
 k3vinlusec/whatsapp-double-free-vulnerability_cve-2019-11932
Step-by-step exploit analysis of WhatsApp's CVE-2019-11932 double-free vulnerability using GEF-GDB debugger for dynamic debugging and arbitrary code…
 synacktiv/shannon-dbg
Debugger for the Shannon Baseband
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 bazad/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 q1f3/triple_fetch
This is an exploit for CVE-2017-7047, Works on 10.3.2 and below.
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 frida/aurora
Proof-of-concept web app built on top of Frida