ioscpy
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
information-gatheringios-securitymobile-security+3
lautarovculic/ioscpyNow you can mirror and control your jailbroken iPhone over USB
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
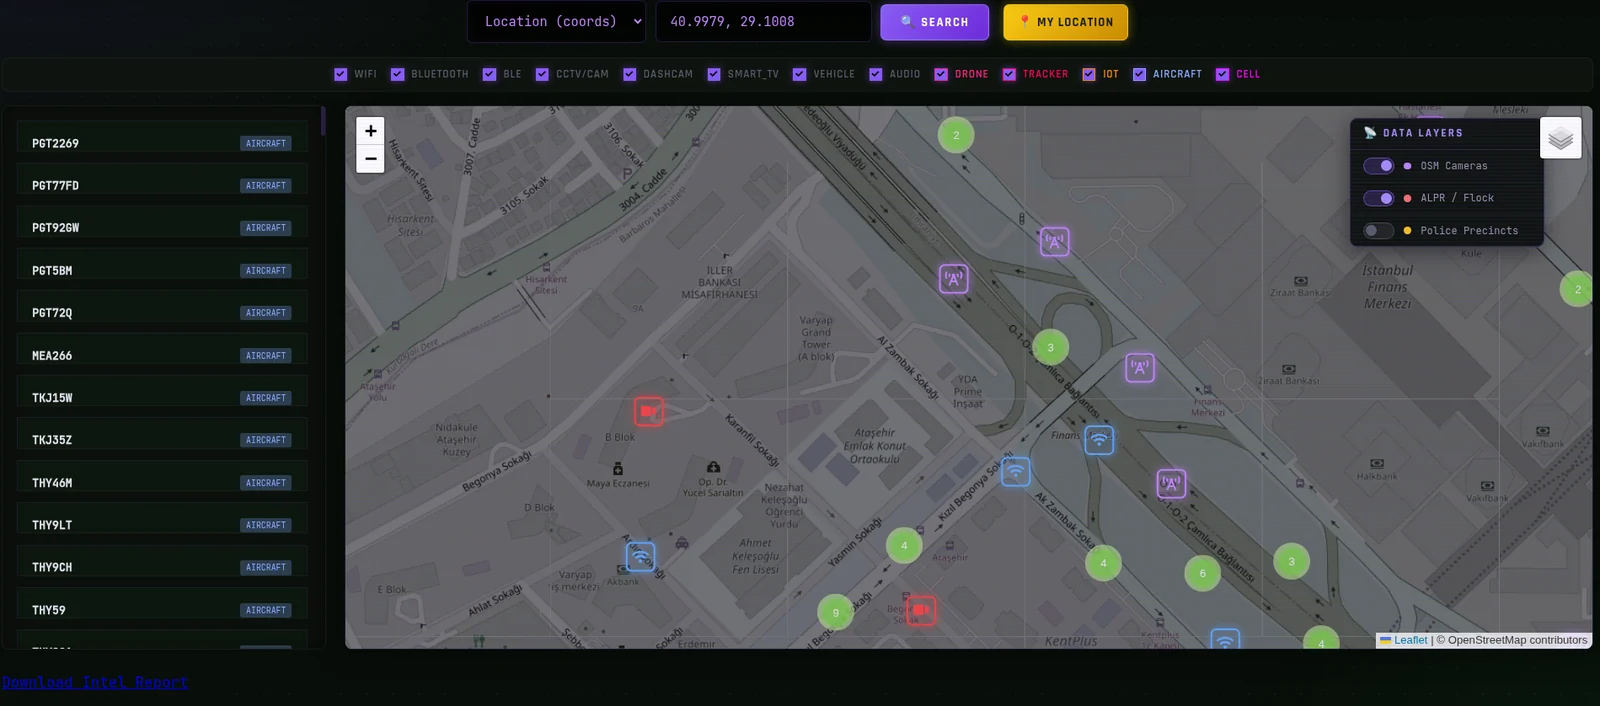 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 justrach/kuri
Browser automation, web crawling, and iOS + Android device control for AI agents. Zig-native, token-efficient CDP snapshots, HAR recording, native…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
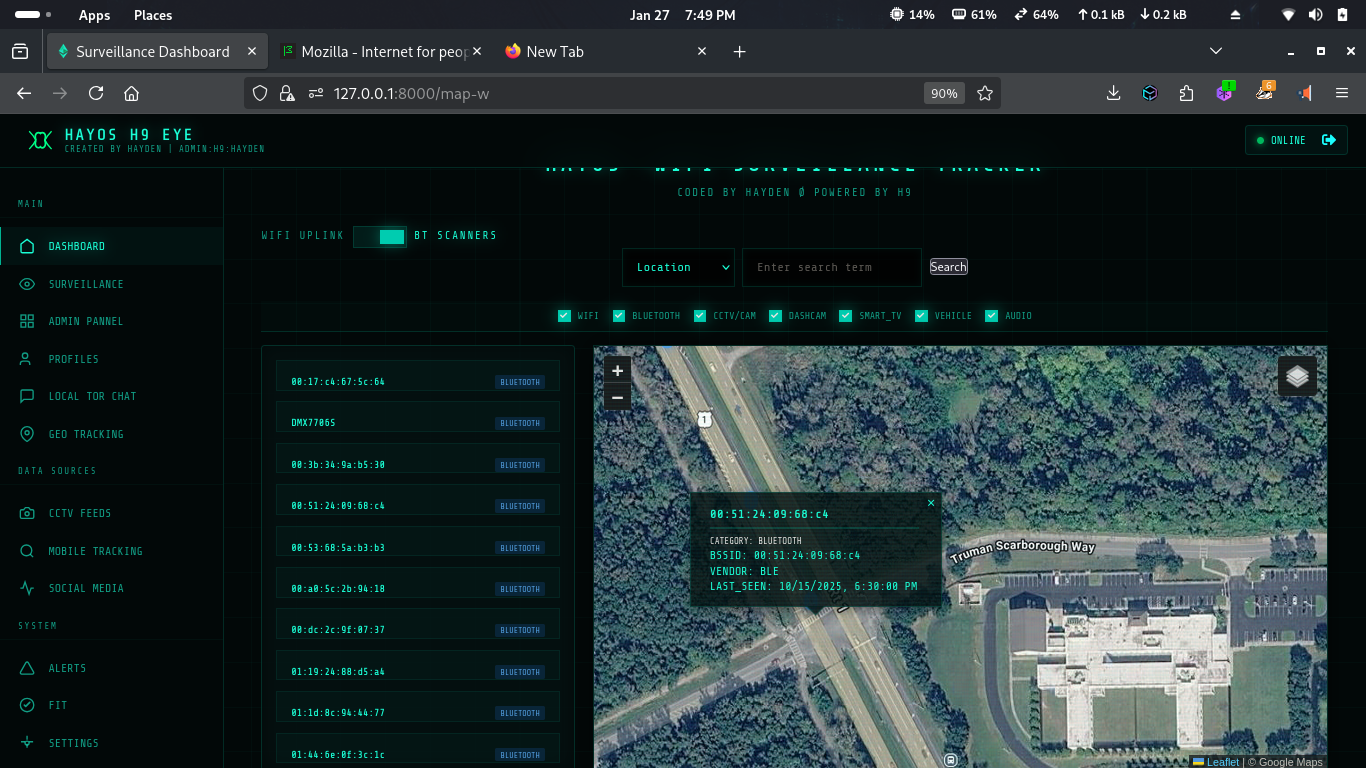 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
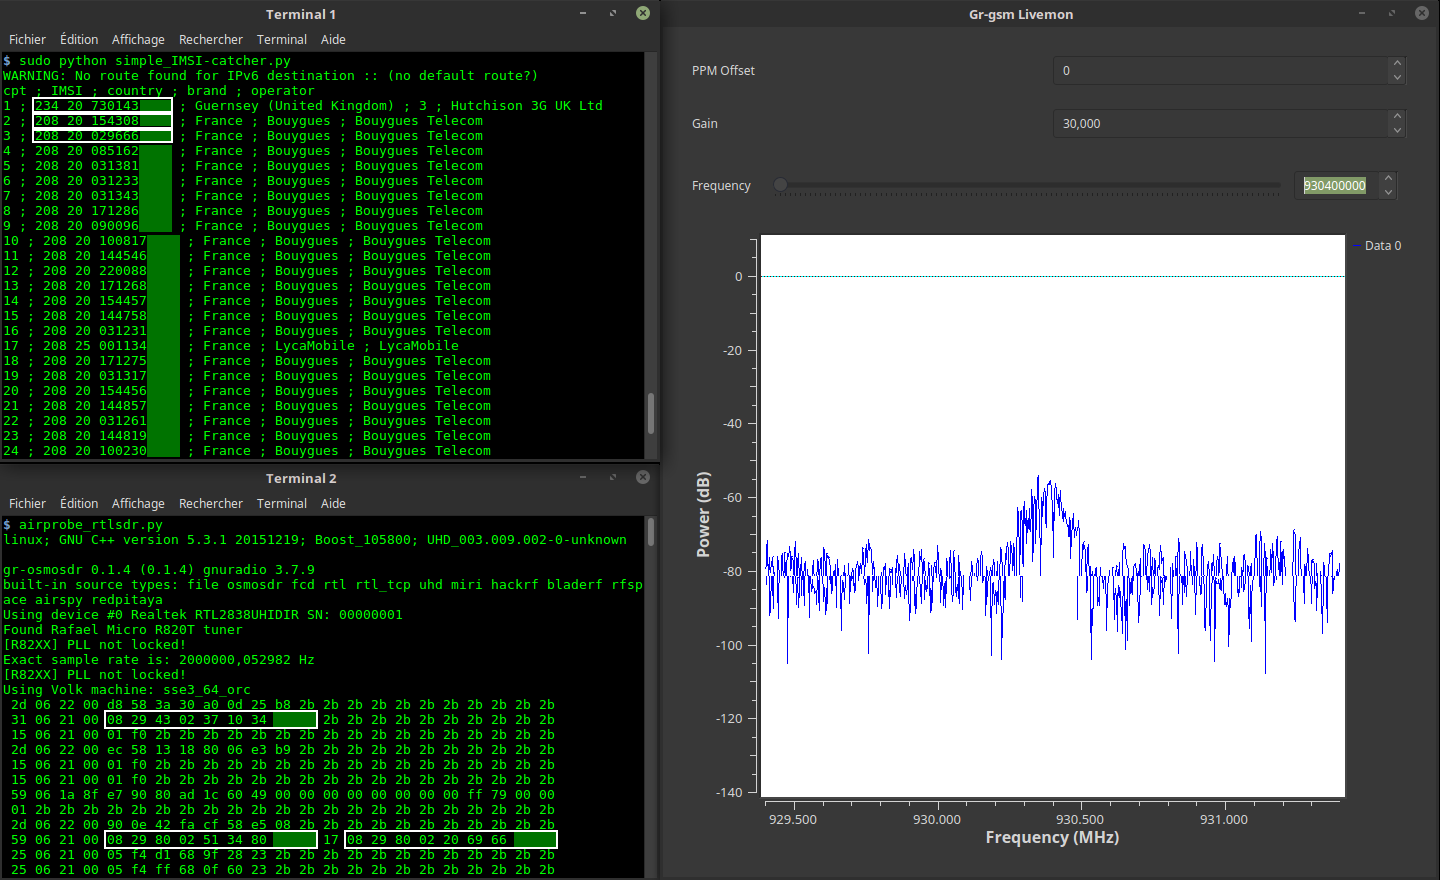 oros42/imsi-catcher
This program show you IMSI numbers of cellphones around you.
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
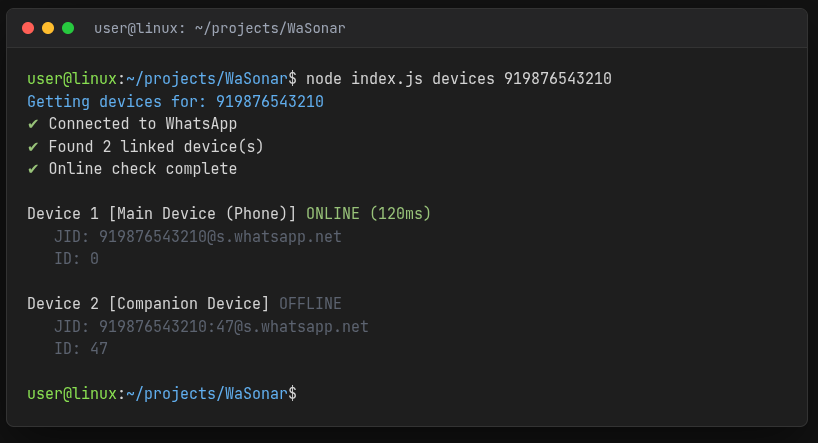 ajayantoisdev/wasonar
WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…
 kinghacker0/whatsapp-osint
WhatsApp OSINT tool for retrieving profile photos, verifying Business accounts, checking user status, analyzing linked devices, and reviewing privacy…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 ifpdz/cve-2025-24104
Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…