

frida-ios-dump
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
4.0k
alonemonkey/frida-ios-dumpExtracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
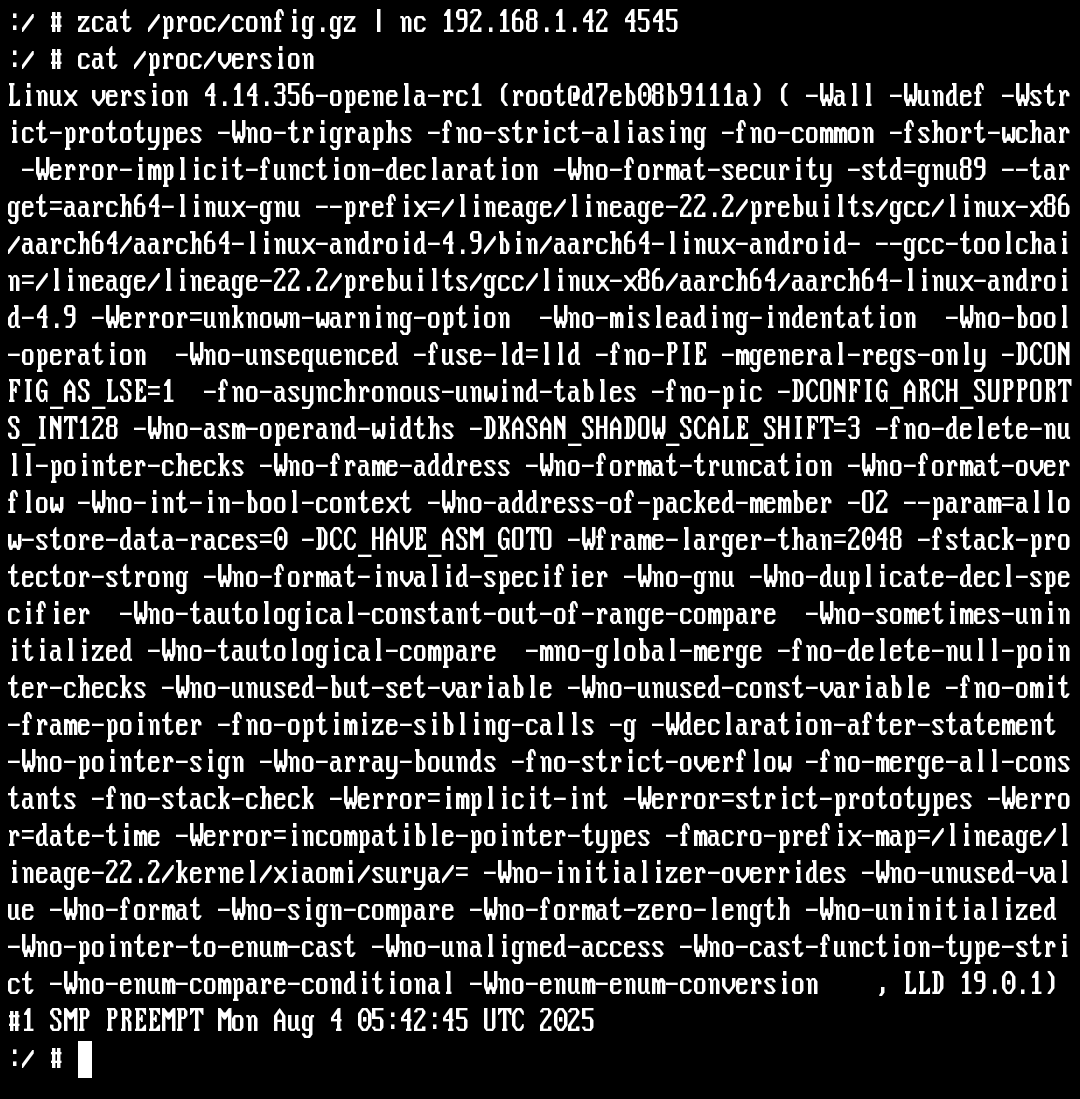
 akabulous/so_you_want_to_build_a_nethunter_kernel
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 humoud/hooketh
A set of scripts that ease working with frida