Charles-Proxy-Mobile-Guide

Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…

Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…

Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

Cross-platform TOTP/HOTP authenticator specification with end-to-end encrypted vault sync, local-first storage, device management, and threshold…

Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…

Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…

Anti-ALPR-surveillance PWA. The camera archive lives on the device.

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Android Chromium fork with built-in ad blocking, anti-fingerprinting mitigations, DNS-over-HTTPS, and hardened privacy and security defaults.

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…

A native APK and DEX decompiler written in Rust

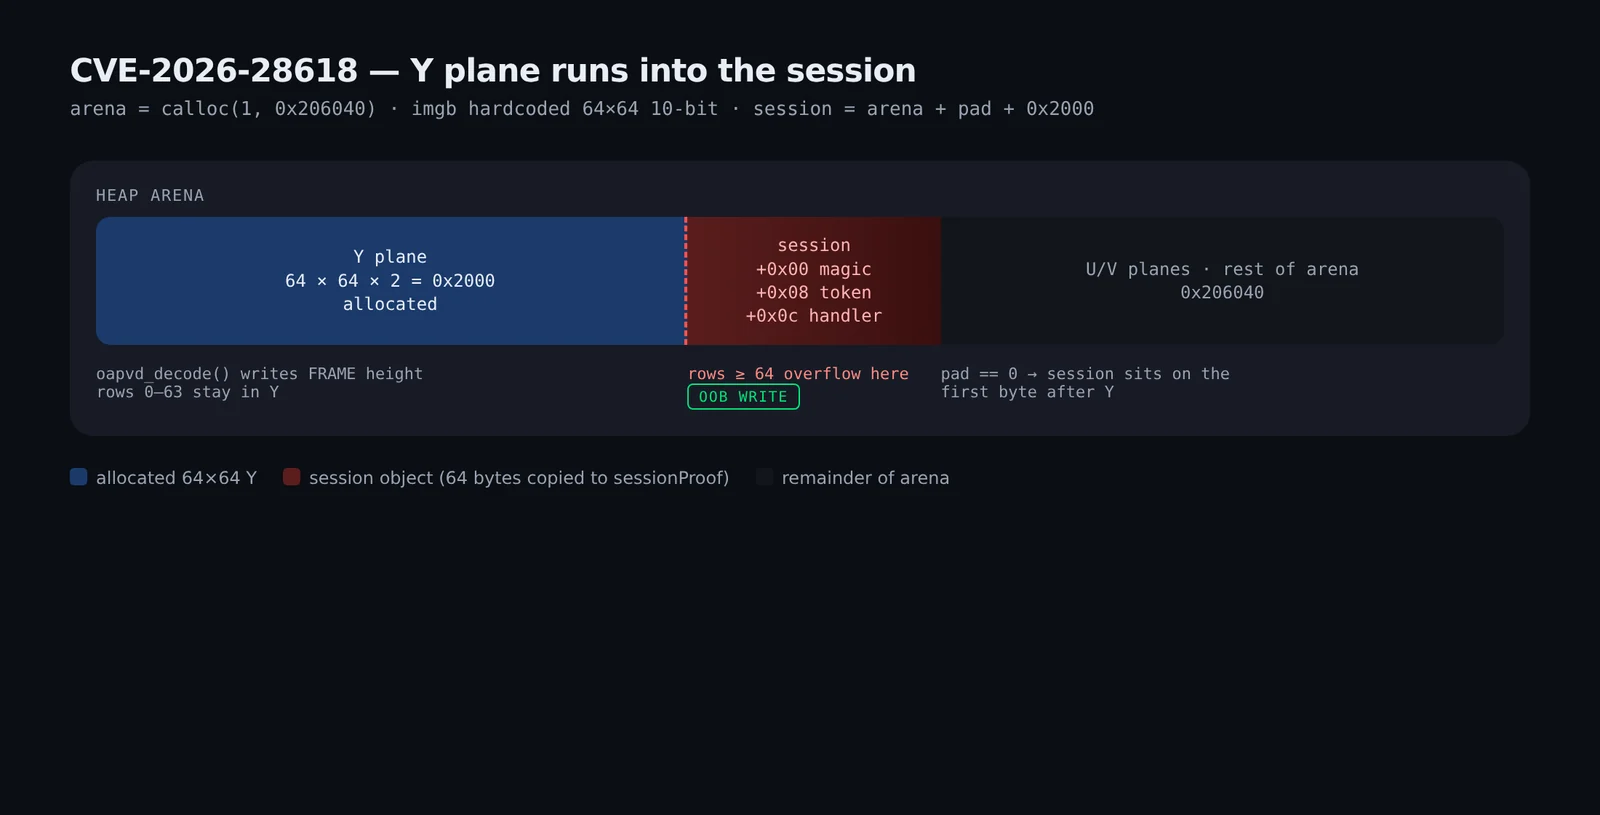
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch

GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.

Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…