
cve-2026-28576
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
android-securitydata-exfiltrationexploitation+6
aayushbankar/cve-2026-28576PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 kal1gh0st/whatsapphack-rce
Exploit for CVE-2019-11932, a remote code execution vulnerability in WhatsApp via malicious GIF files. Includes proof-of-concept code and technical…
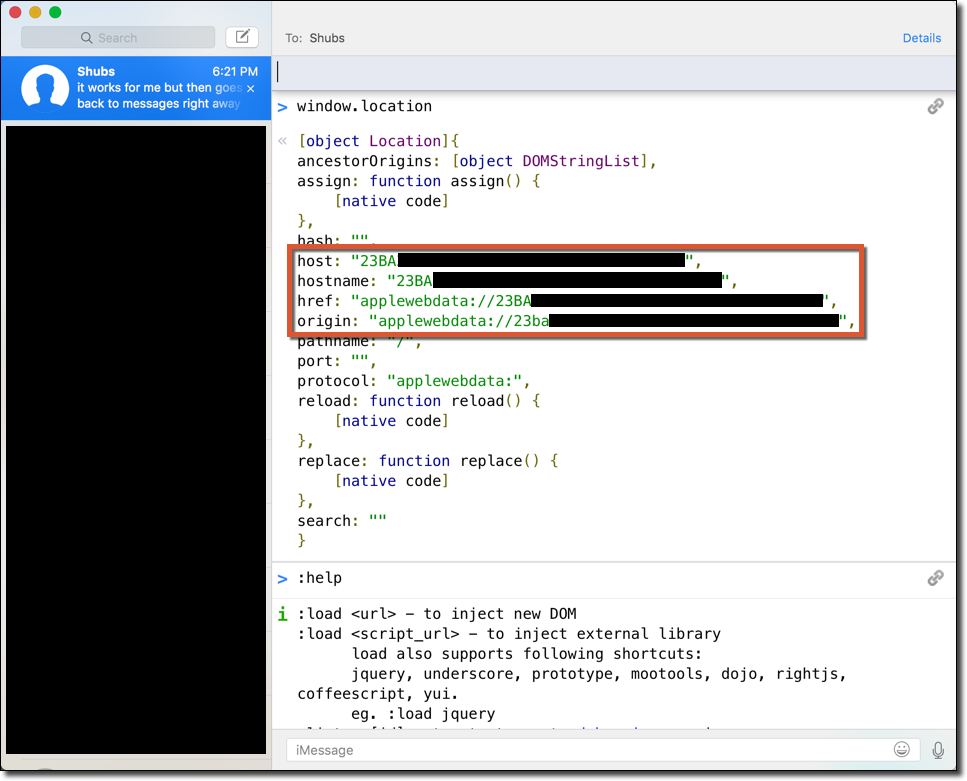 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
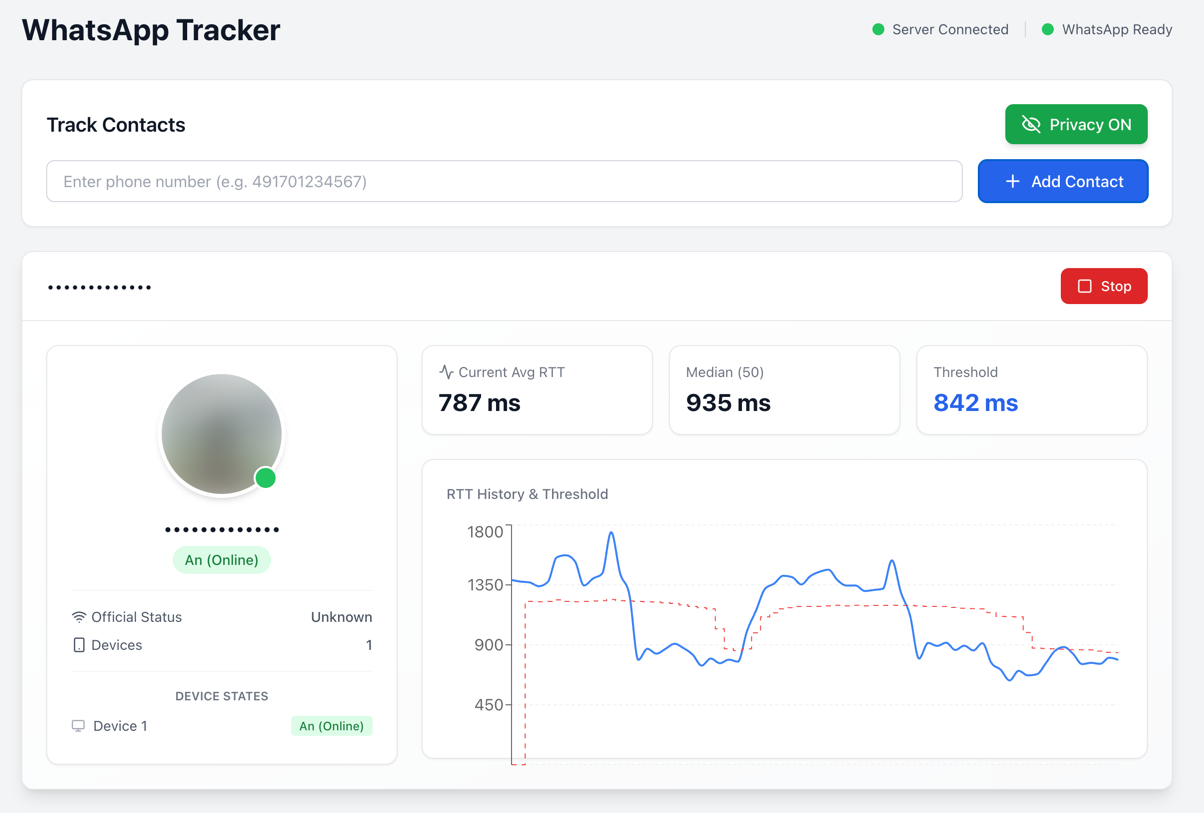 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 ajayantoisdev/wasonar
WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows