awesome-game-security

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…

The patching of Android kernel and Android system

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…

UNIX-like reverse engineering framework and command-line toolset

A collection of awesome penetration testing resources and tools

No-root network monitor, firewall and PCAP dumper for Android

Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…

JA4+ is a suite of network fingerprinting standards

Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

A curated list of awesome Android Reverse Engineering training, resources, and tools.

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

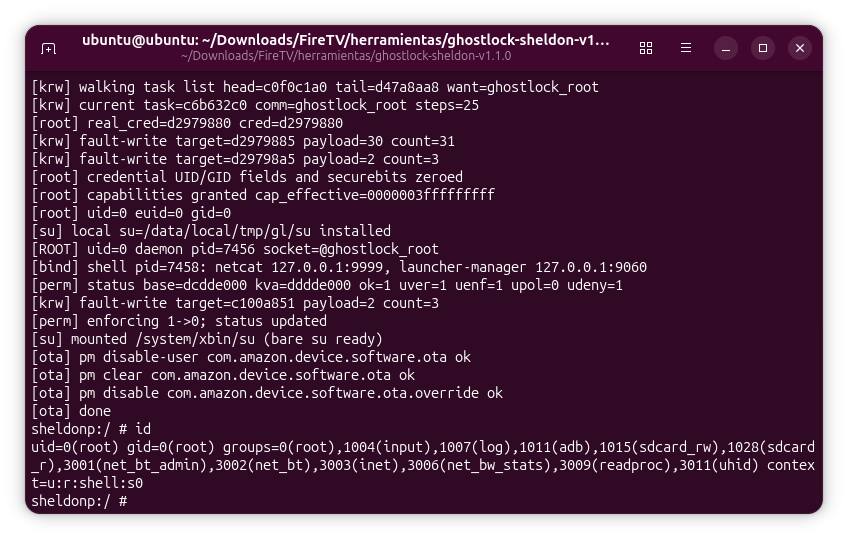
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Mobile Hacker's Weapons / A collection of cool tools used by Mobile hackers. Happy hacking , Happy bug-hunting

Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…