

Magisk
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
android-securitymobile-securityprivilege-escalation
topjohnwu/magiskAndroid customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
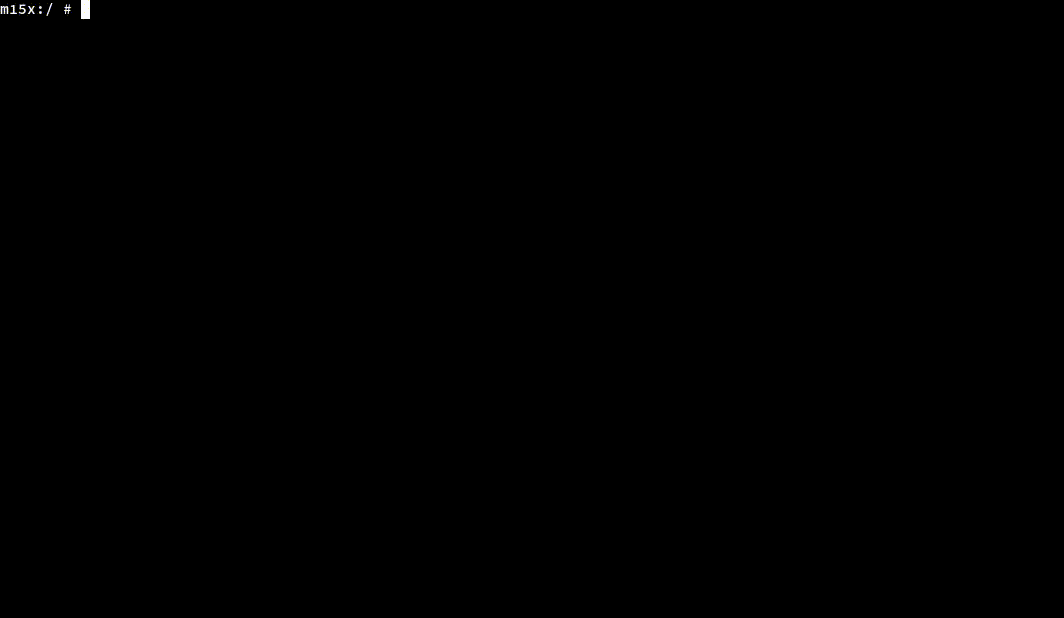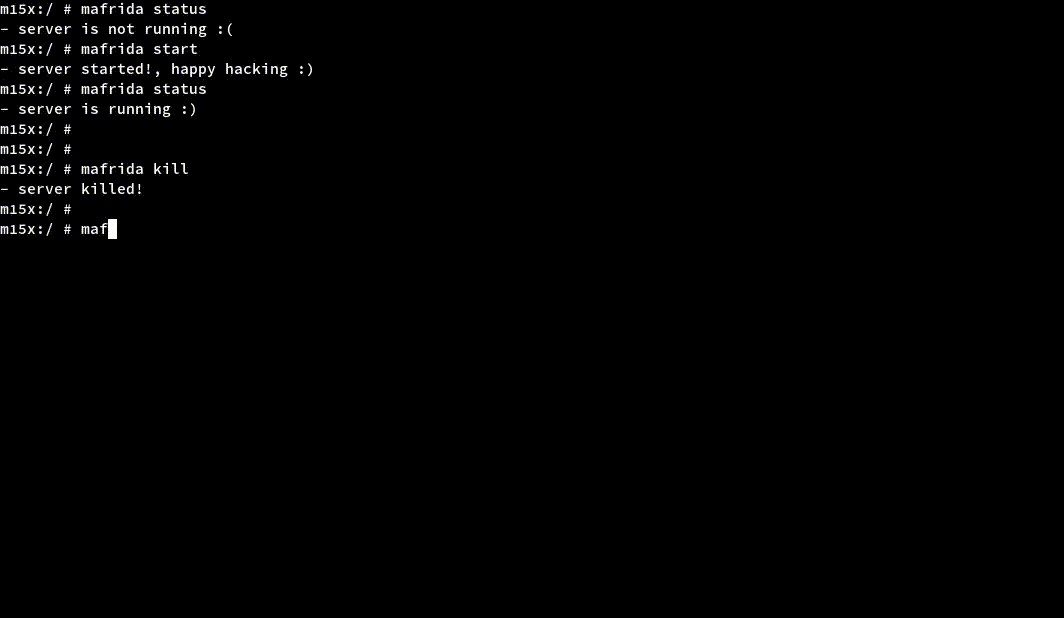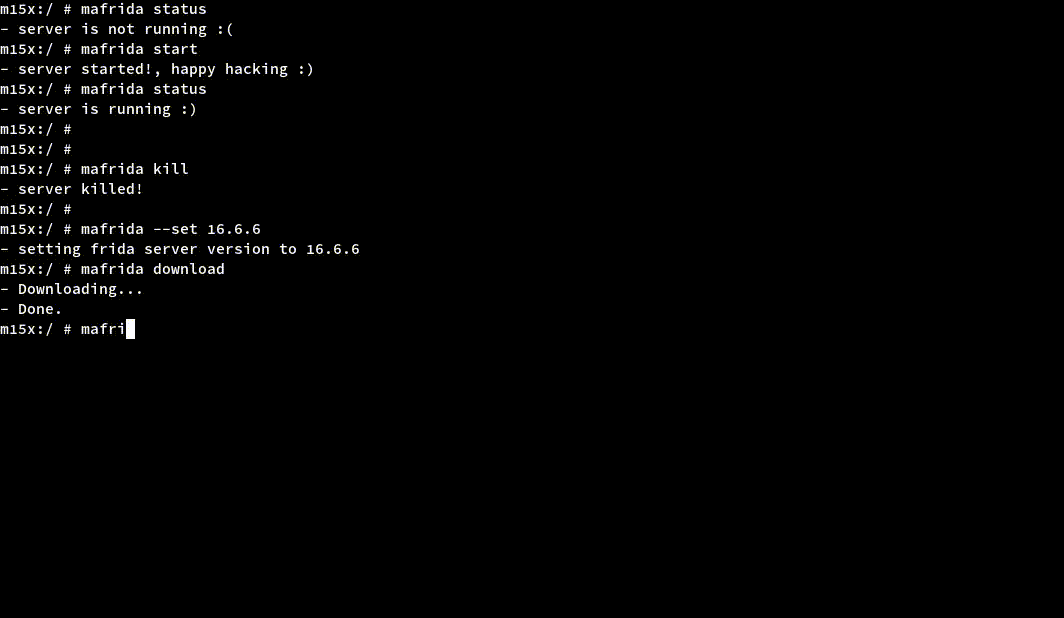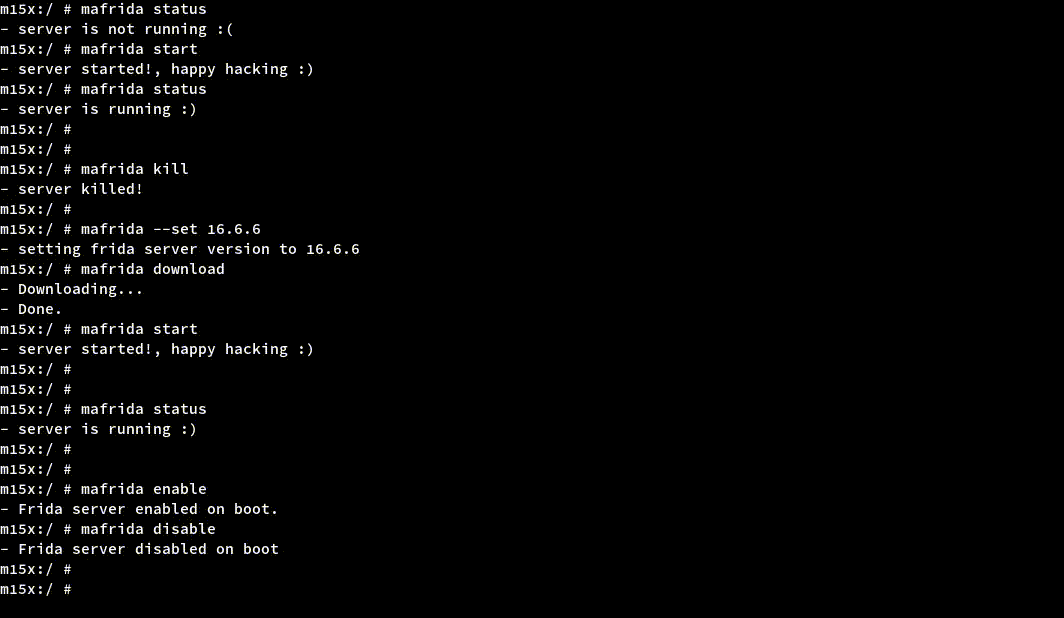 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration