
iDescriptor
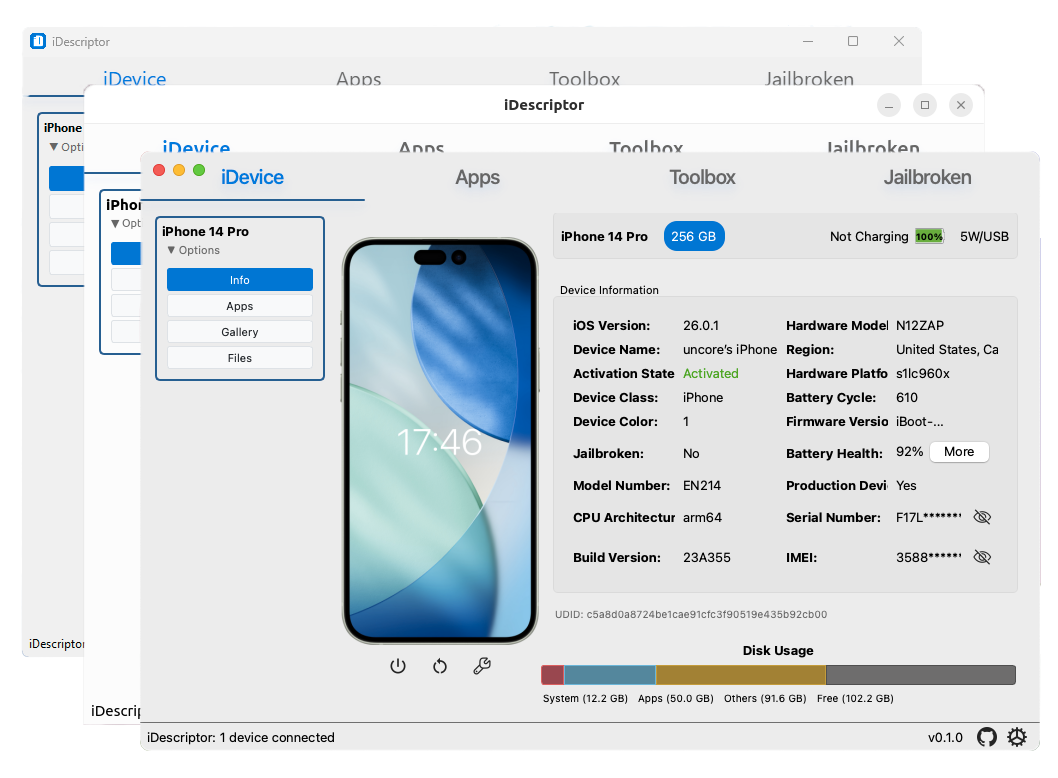
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.6k
idescriptor/idescriptorprivacy-first, open-source and free idevice management tool written in Rust and Qt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 ddz/whatsapp-media-decrypt
Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 levilutz/cve-2021-30860
Scan for evidence of CVE-2021-30860 (FORCEDENTRY) exploit
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
 nowsecure/android-forensics
Open source Android Forensics app and framework