
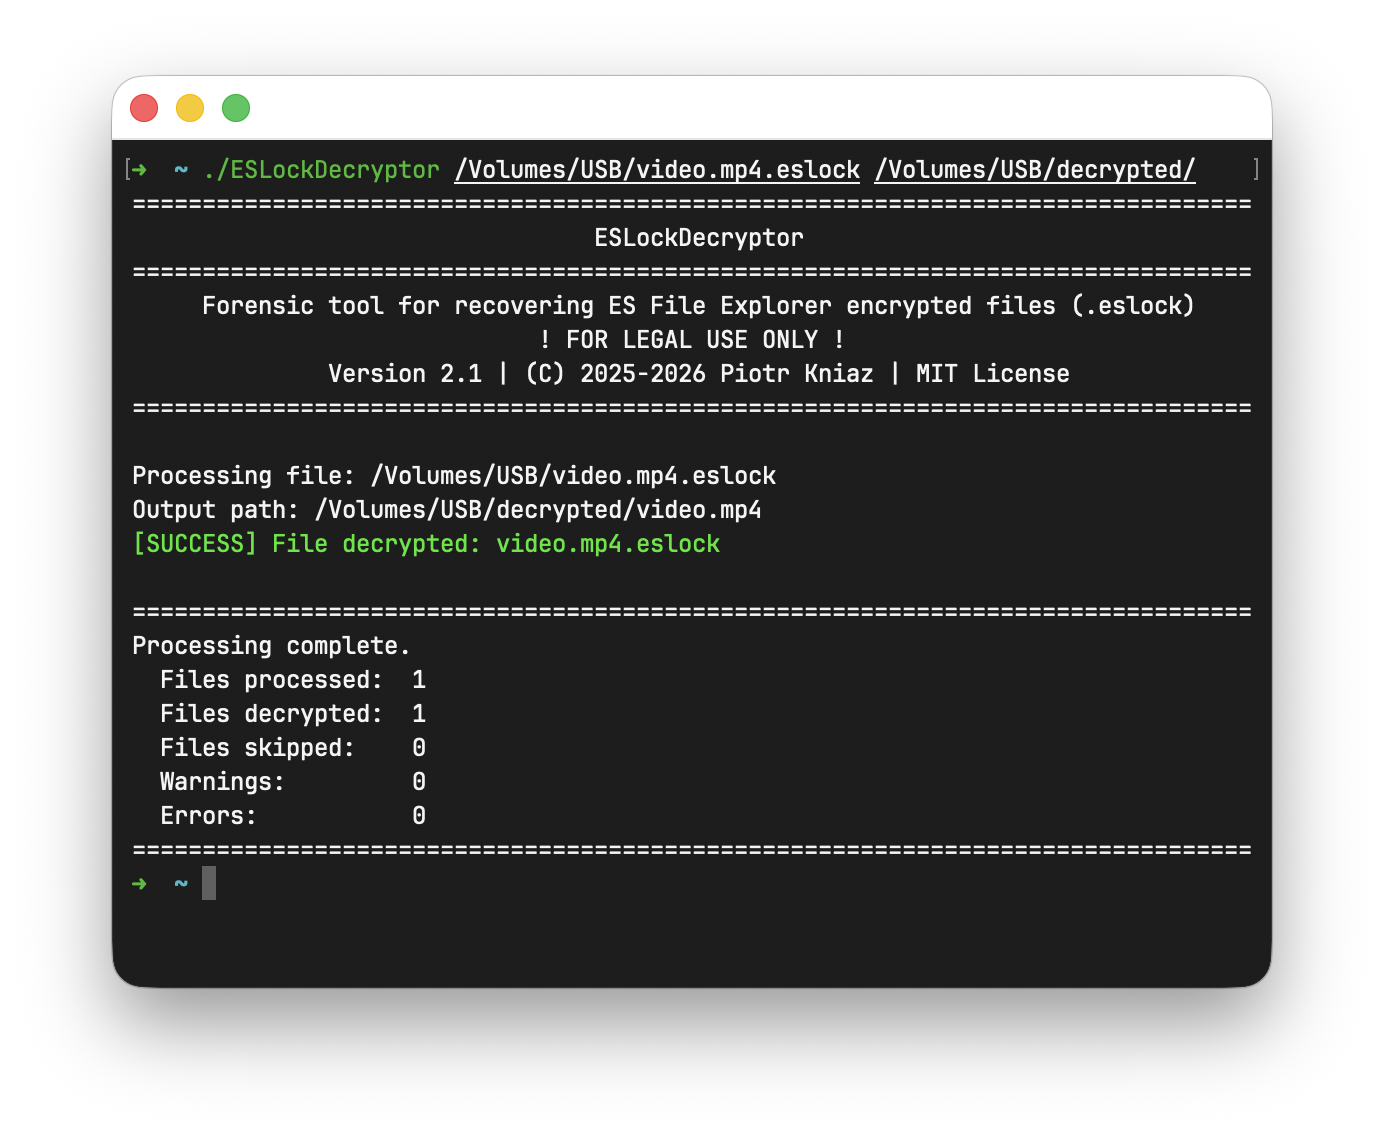
ESLockDecryptor
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
android-securitydata-recoverydigital-forensics+3
16
piotr-kniaz/eslockdecryptorUtility for recovering ES File Explorer encrypted files (.eslock)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
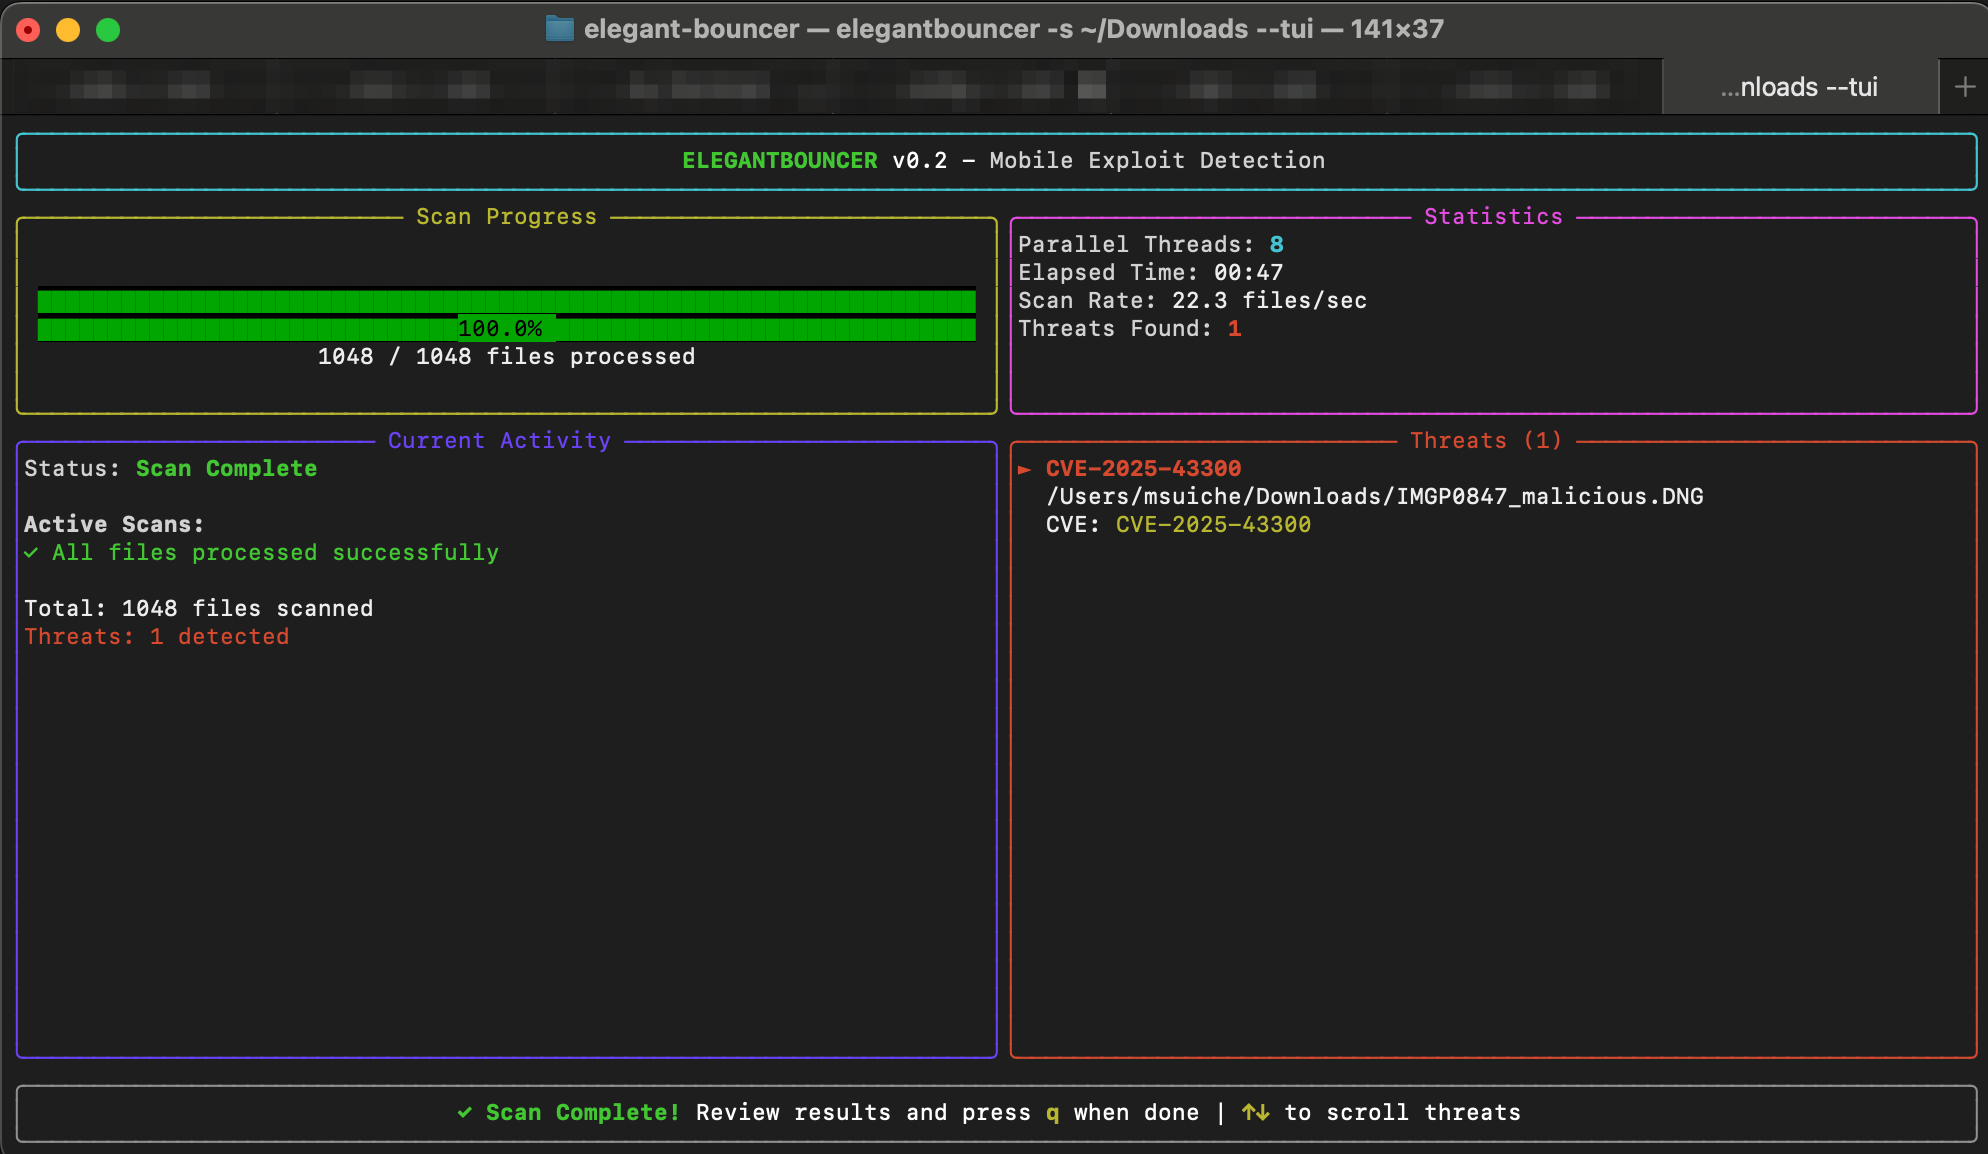 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
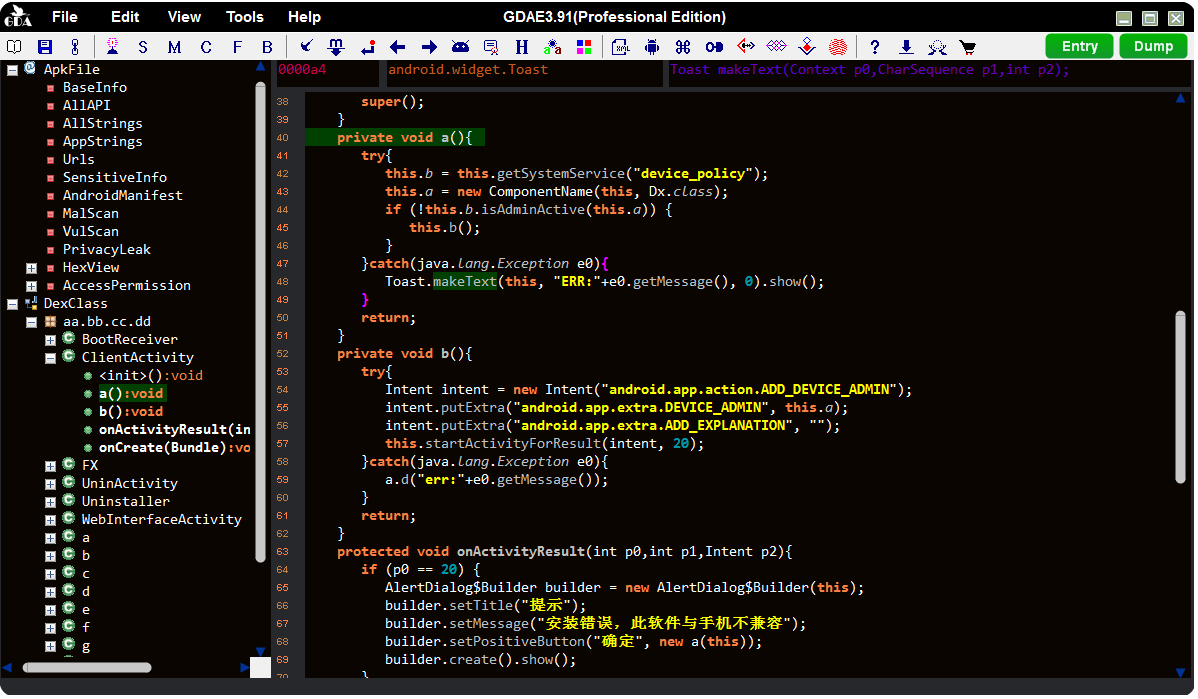 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 telegrip/telegrip
GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 cristianzsh/forensictools
Collection of forensic tools
