
DFIRArtifactMuseum
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
curated-resourcesdigital-forensicseducation+2
667
andrewrathbun/dfirartifactmuseumThe goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 levilutz/cve-2021-30860
Scan for evidence of CVE-2021-30860 (FORCEDENTRY) exploit
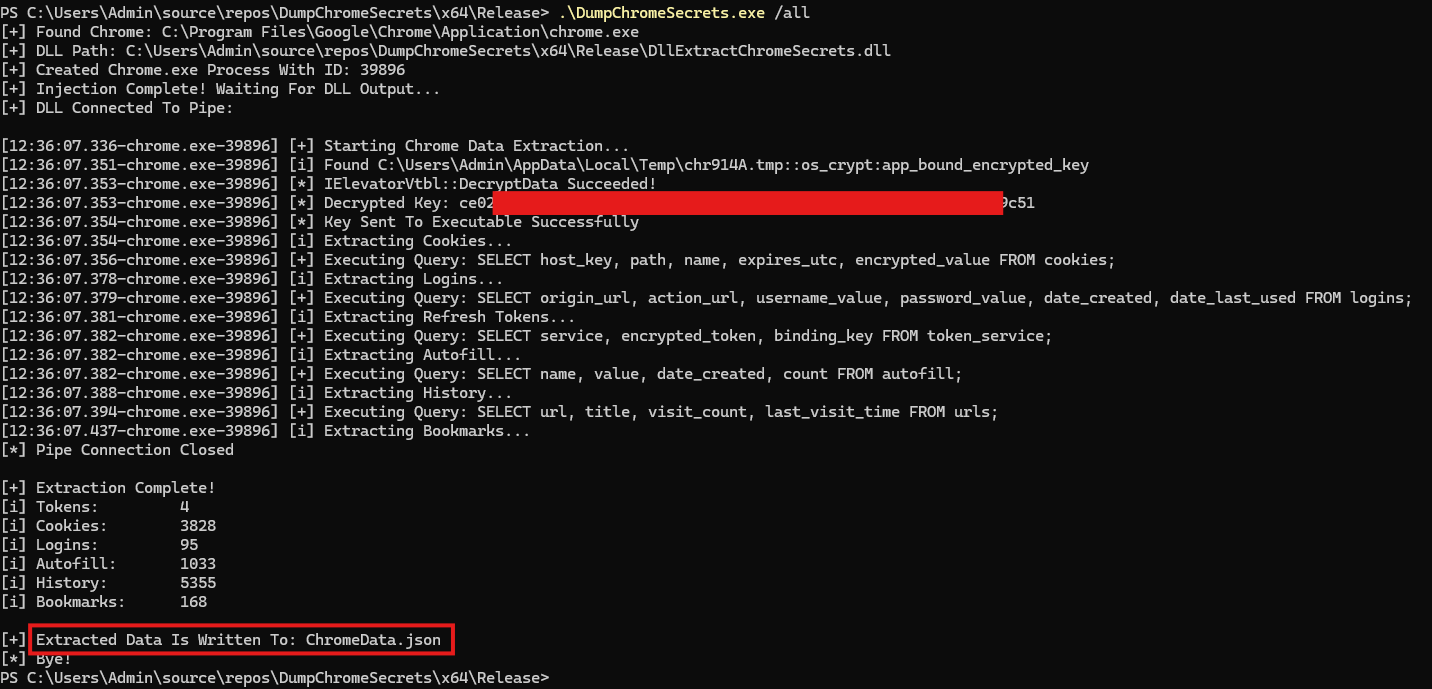 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
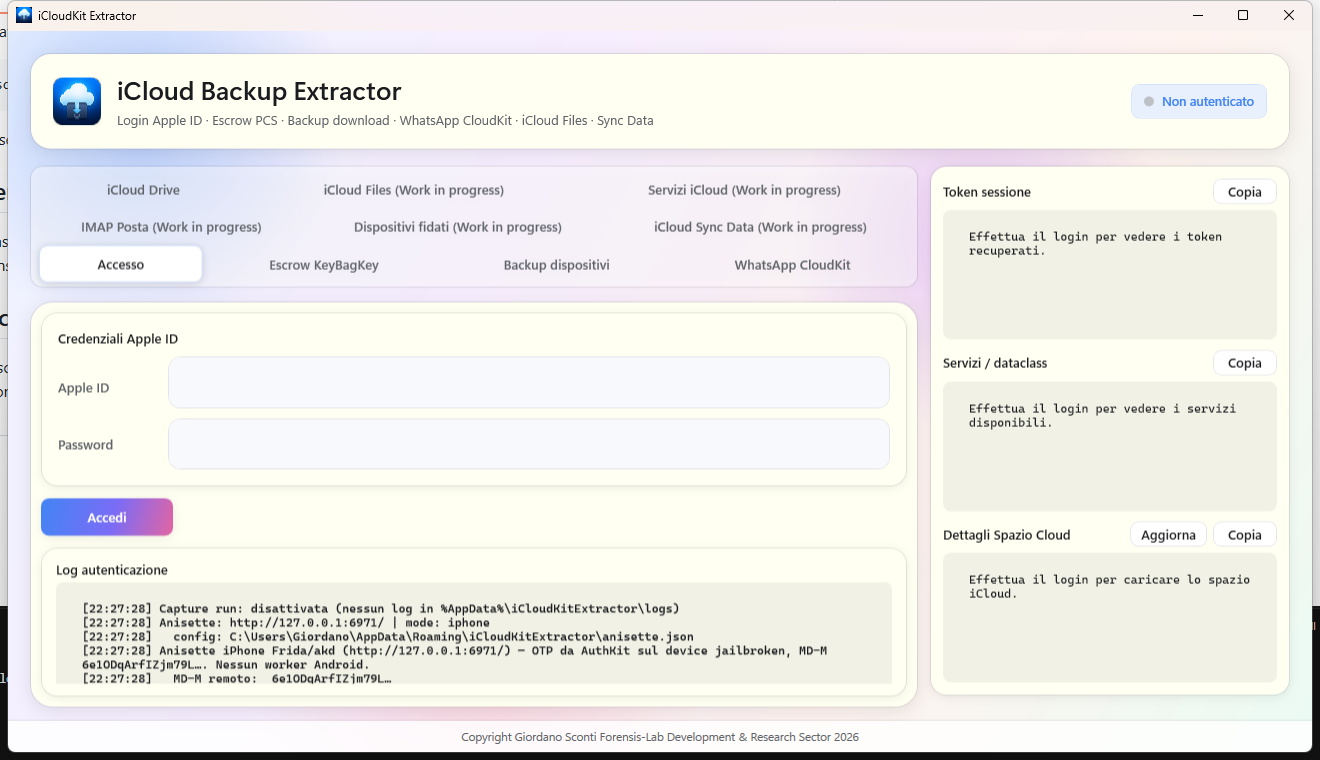 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
 cristianzsh/forensictools
Collection of forensic tools
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
 cyberhatcoil/acf
Android Connections Forensics
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
 frida/frida
Main repo for hosting release binaries

 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…