
bulk_extractor
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
data-recoverydigital-forensicsdisk-forensics+9
simsong/bulk_extractorThis is the development tree. Production downloads are at:
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS

 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
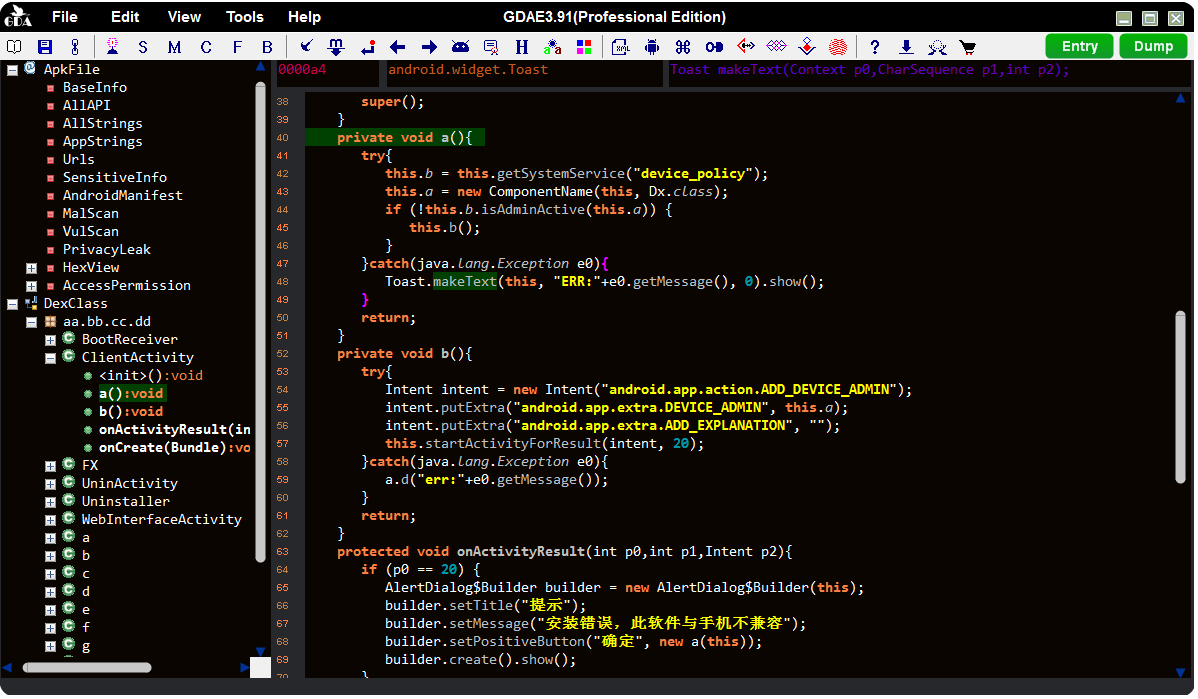 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
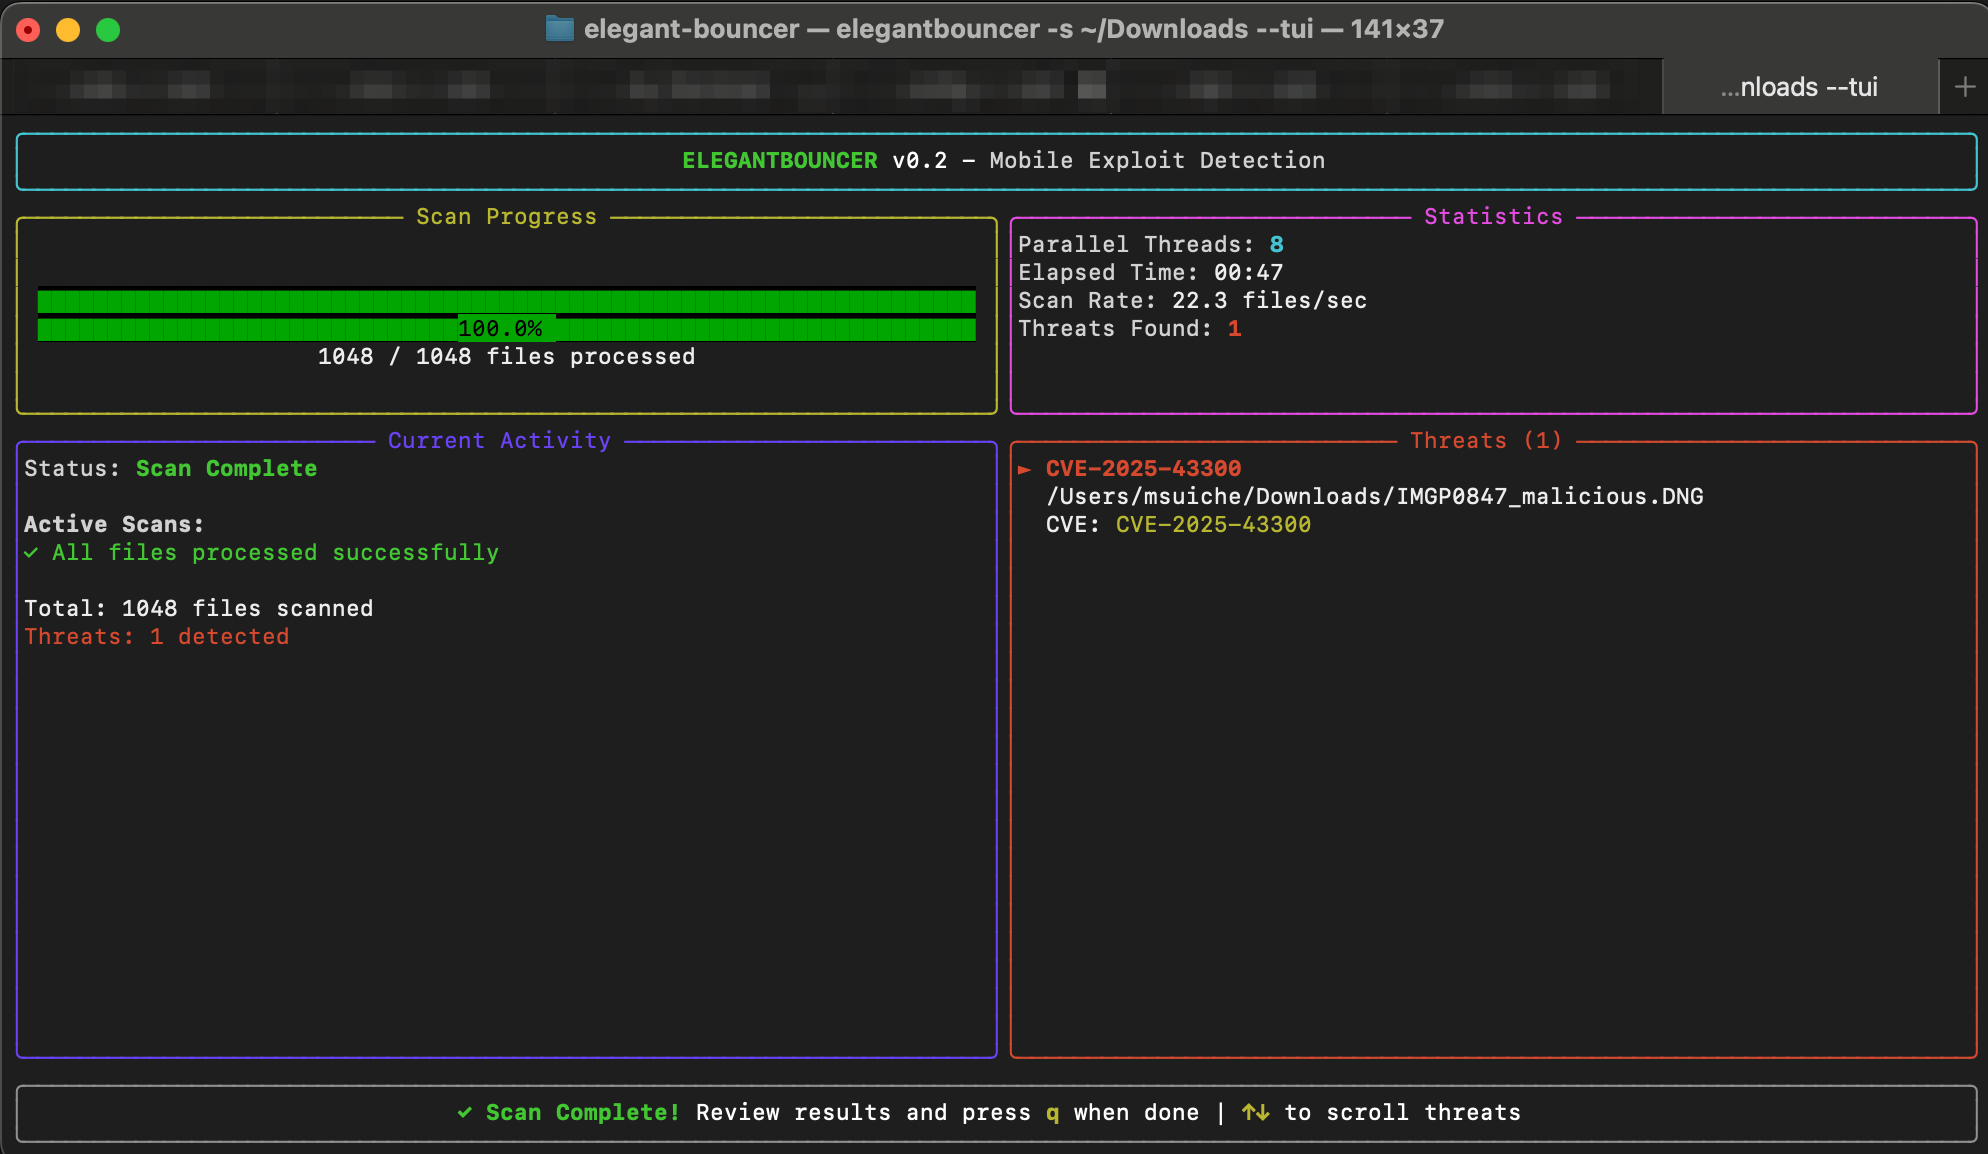 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 nowsecure/r2frida
Radare2 and Frida better together.
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…