GDA-android-reversing-Tool

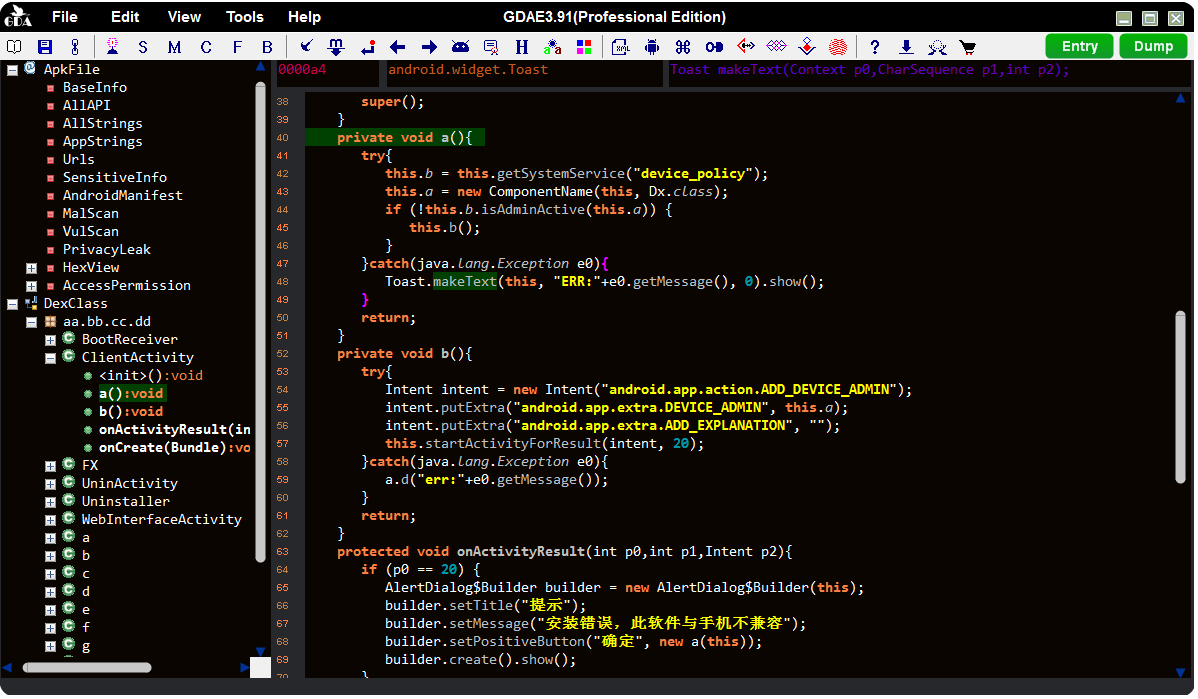
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Radare2 and Frida better together.

Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices

Open source Android Forensics app and framework

Main repo for hosting release binaries

Filesystem monitor tool for Linux/Android iOS/macOS


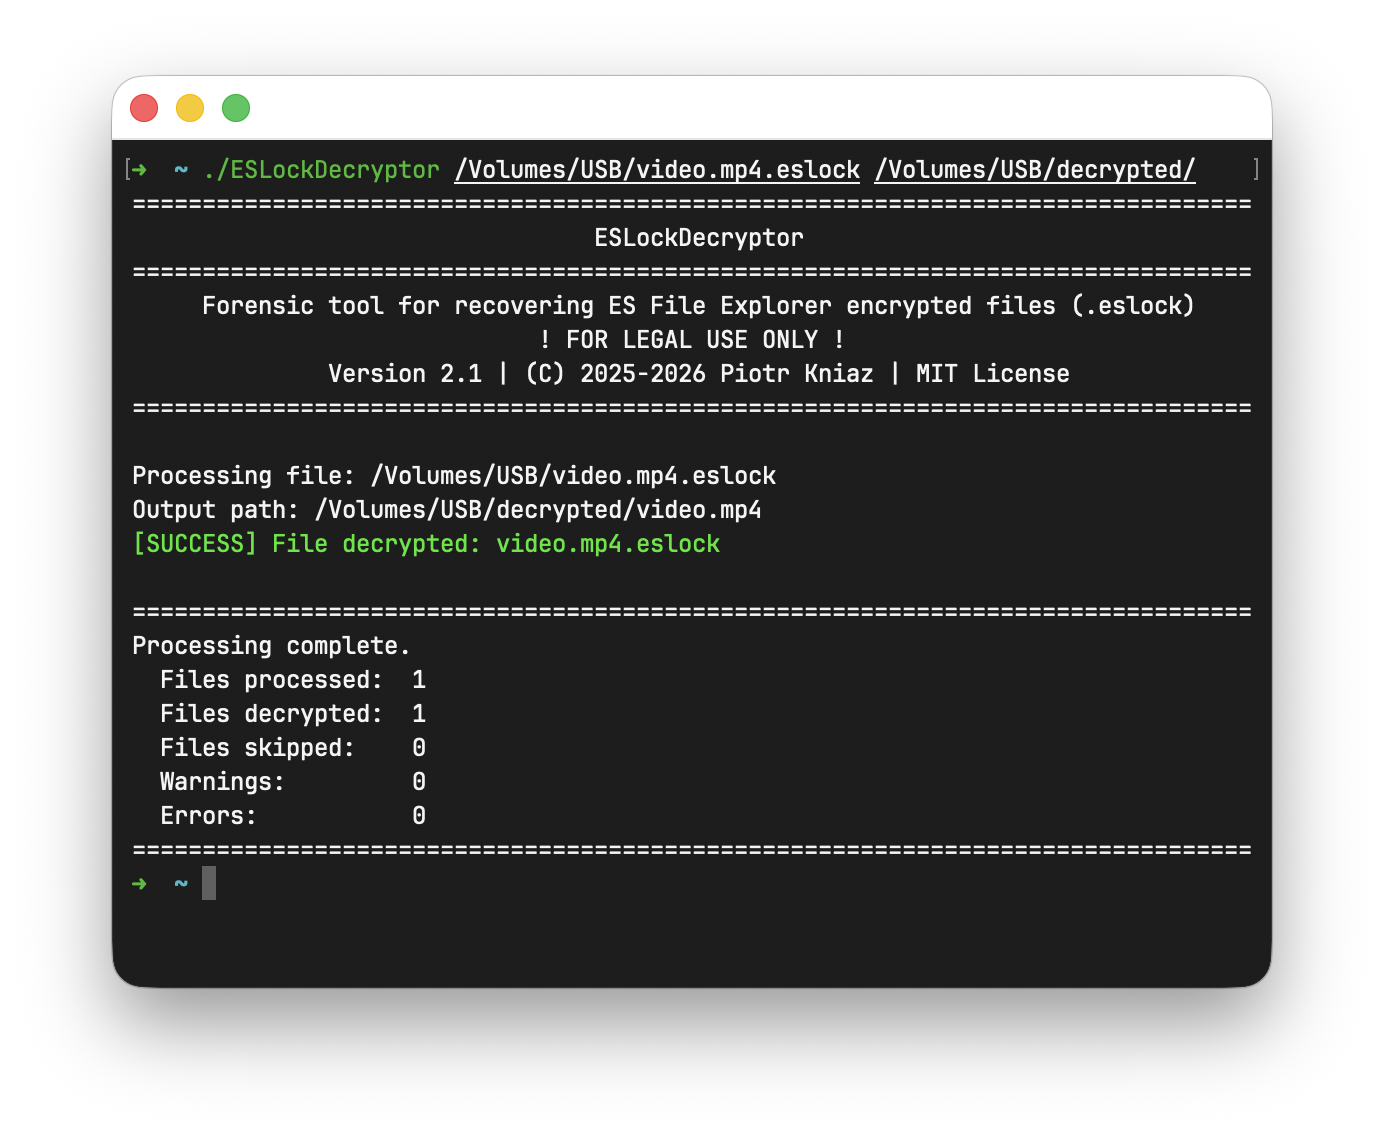
Utility for recovering ES File Explorer encrypted files (.eslock)

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser

A tool for reverse engineering Android apk files

Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

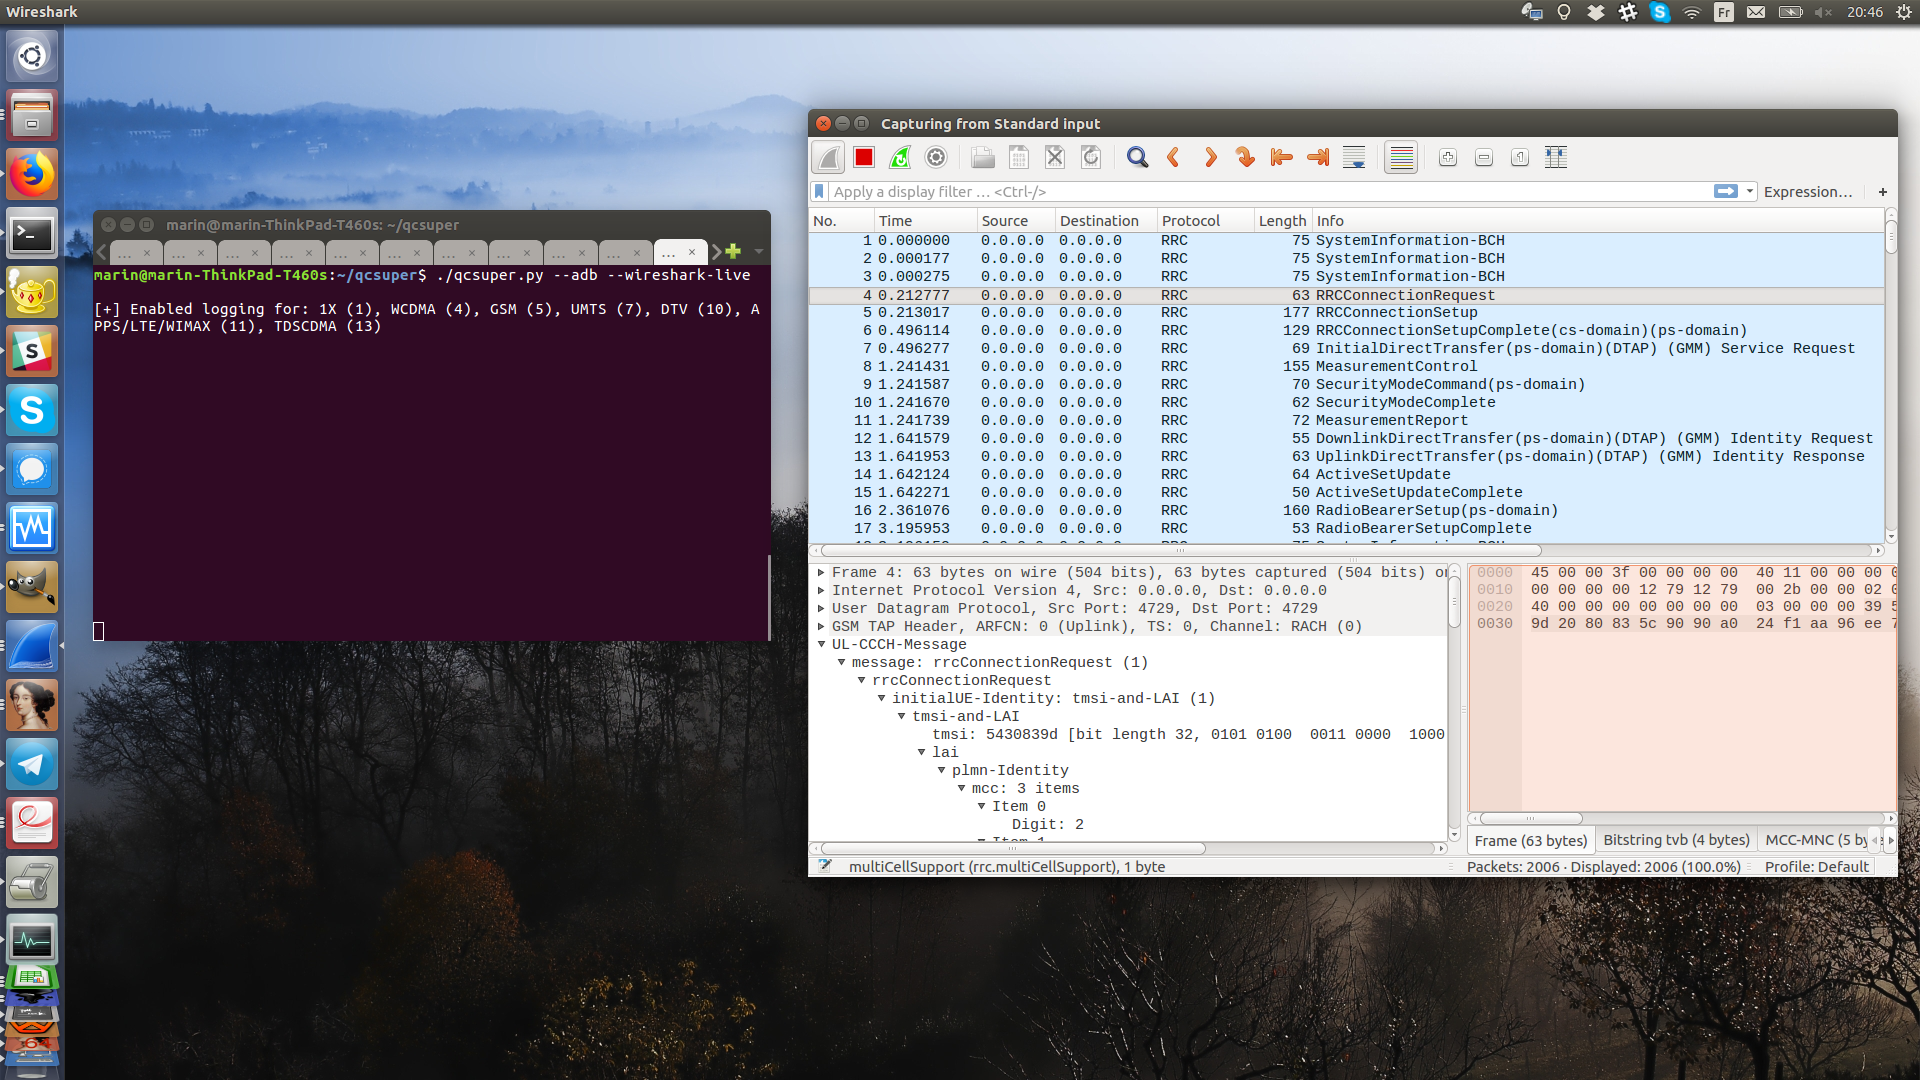
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.