

androidqf
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
326
mvt-project/androidqfandroidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
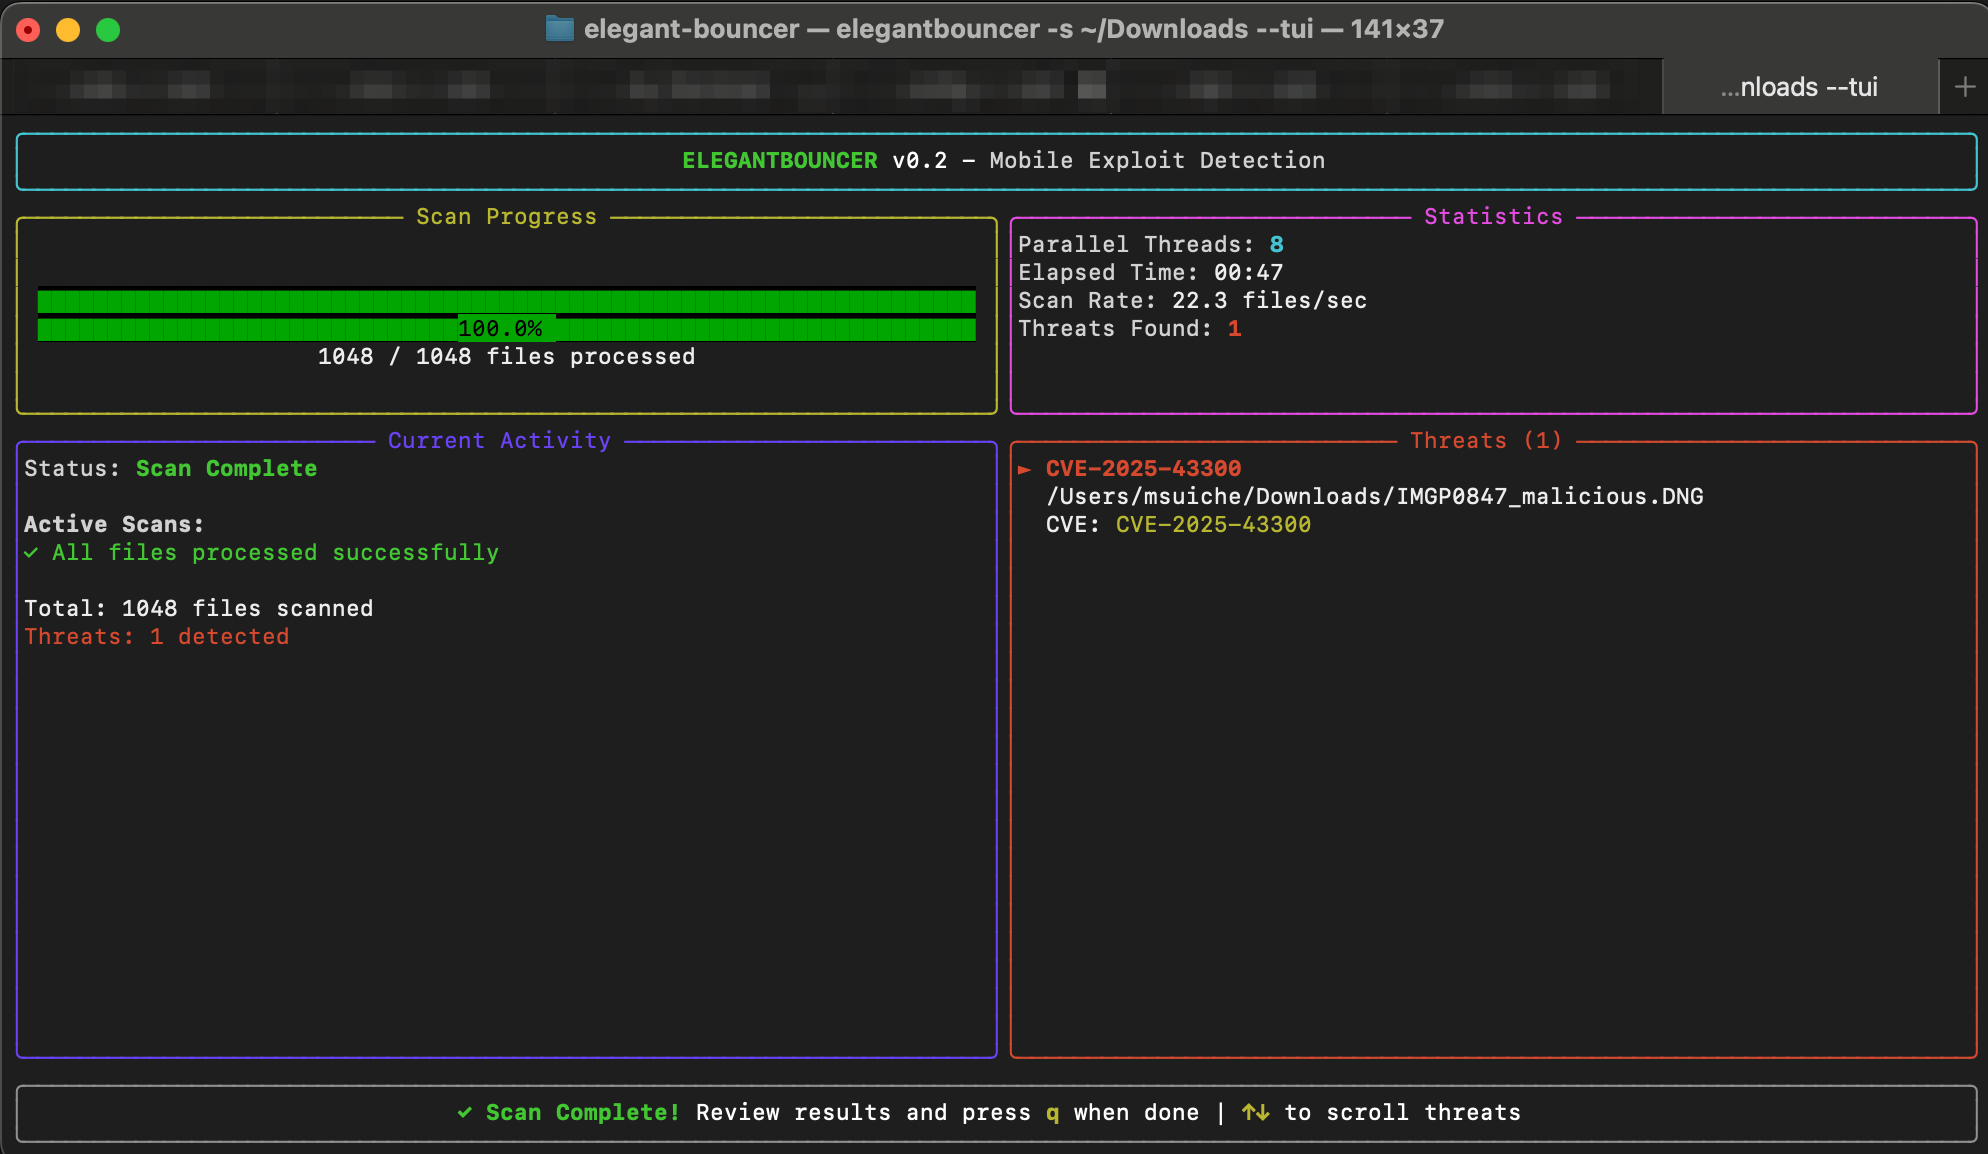 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 nowsecure/android-forensics
Open source Android Forensics app and framework