
ALEAPP
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
digital-forensicsincident-responselog-analysis+1
abrignoni/aleappAndroid Logs Events And Protobuf Parser
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 nowsecure/r2frida
Radare2 and Frida better together.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 androguard/androguard
Reverse engineering and pentesting for Android applications
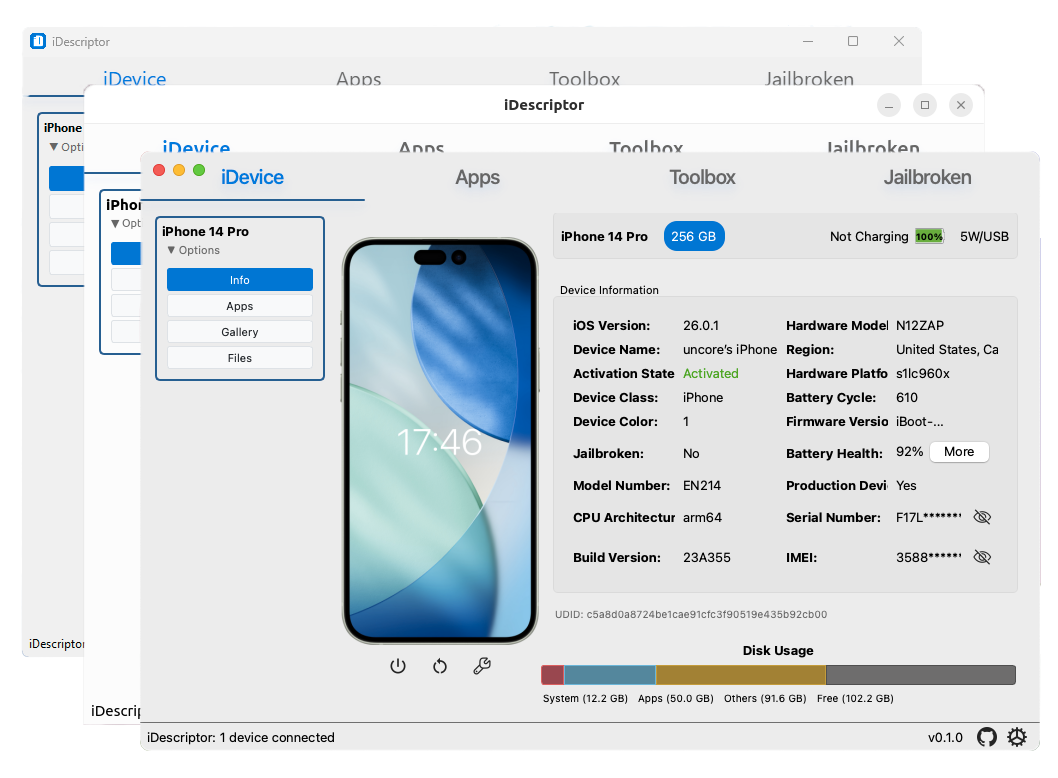 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
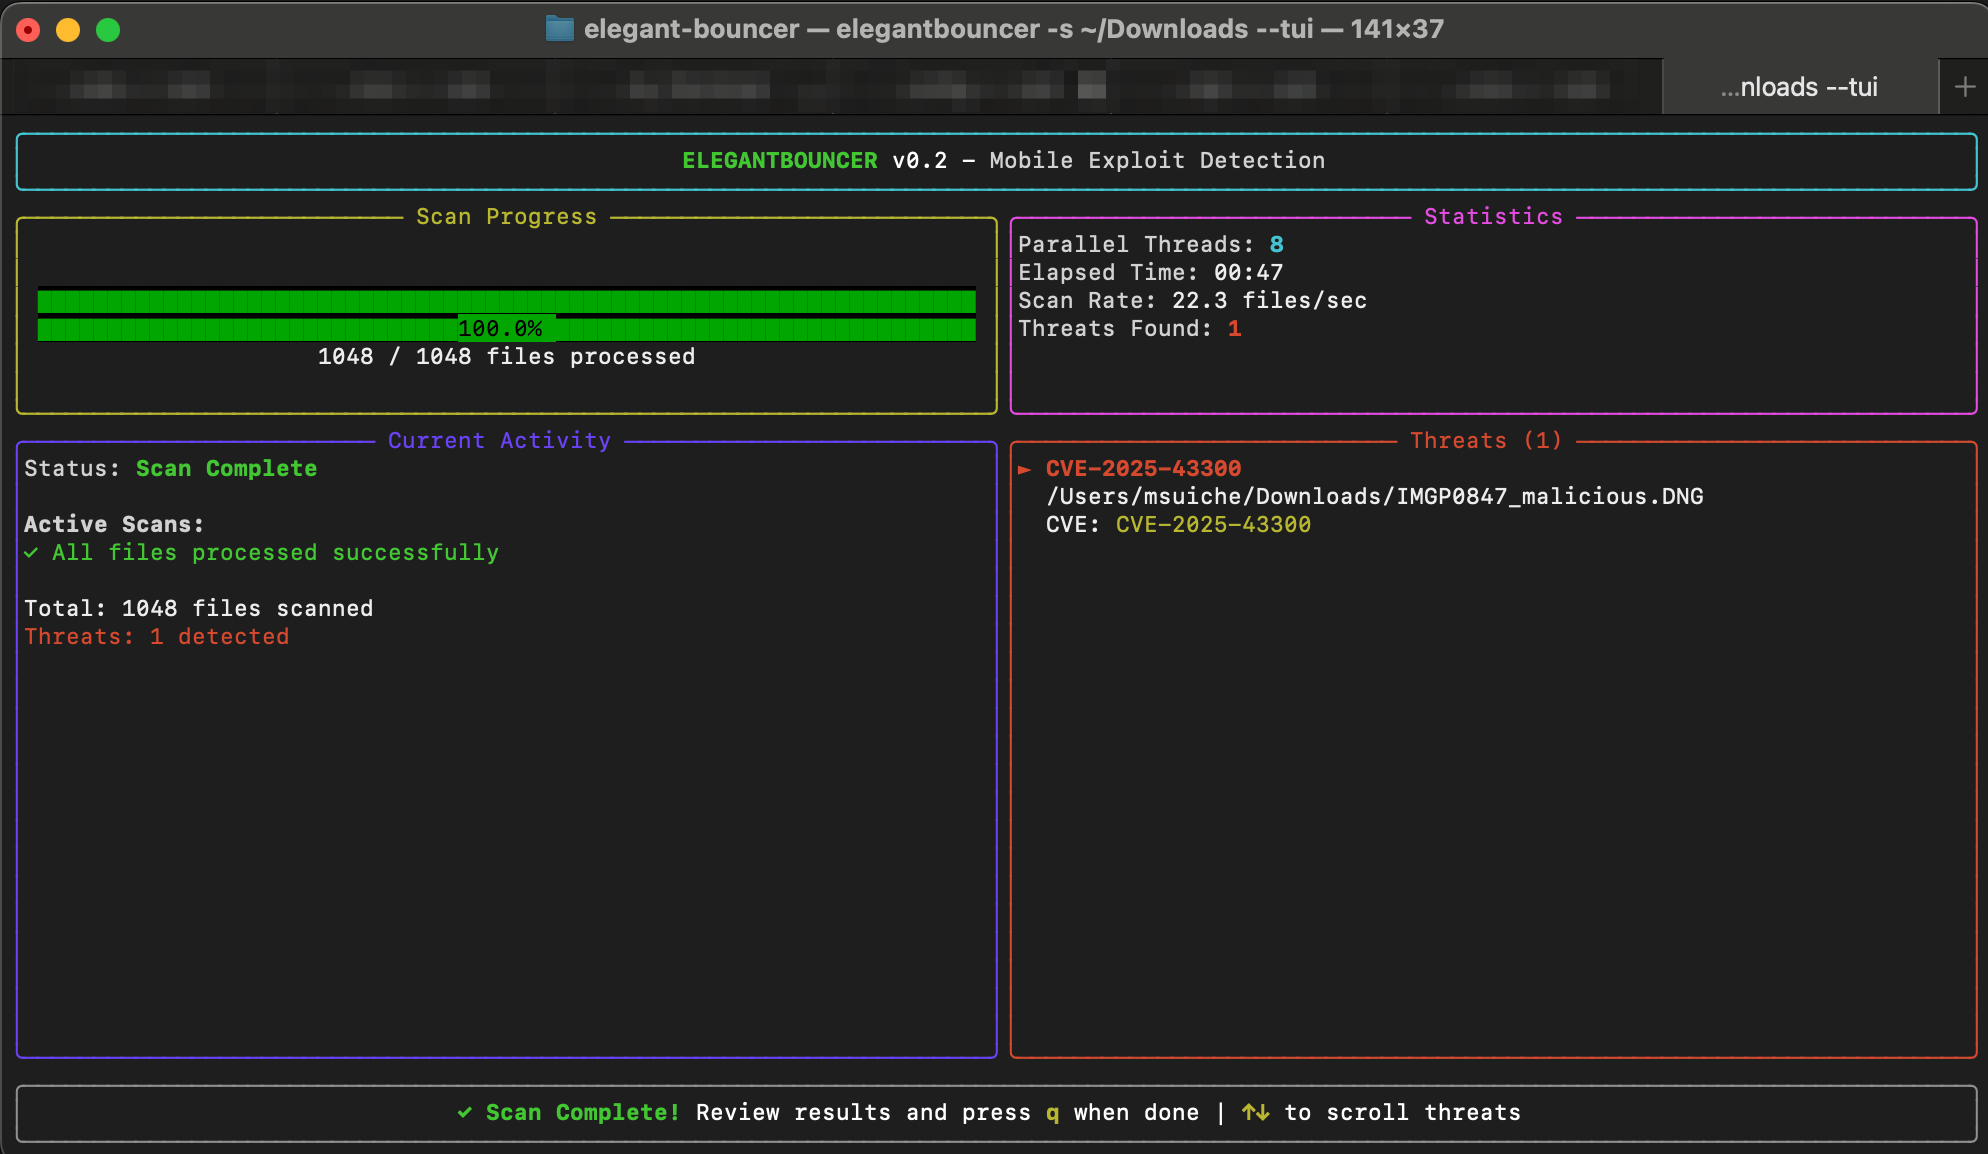 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 cristianzsh/forensictools
Collection of forensic tools
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks