Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

A tool for reverse engineering Android apk files

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Radare2 and Frida better together.

Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)

Reverse engineering and pentesting for Android applications

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Main repo for hosting release binaries

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

Filesystem monitor tool for Linux/Android iOS/macOS

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

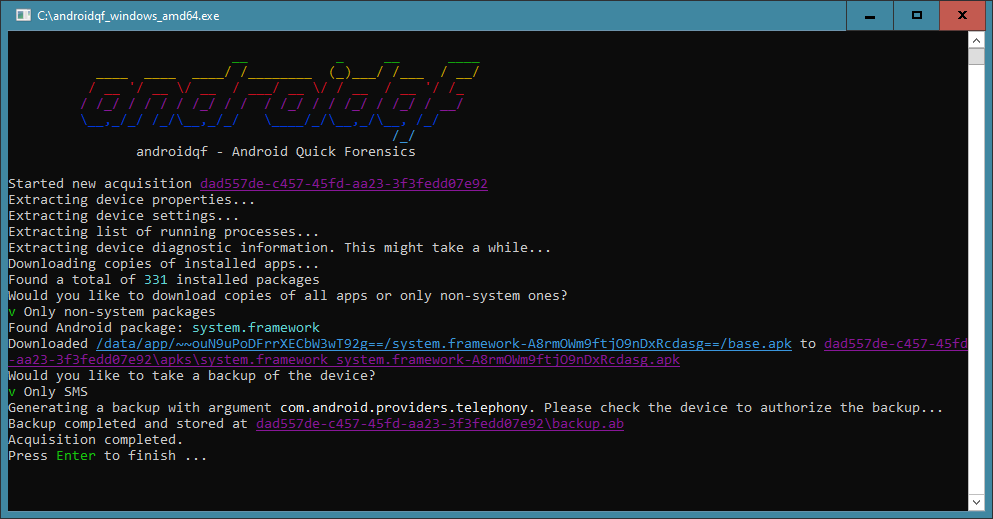
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…