
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.0k
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 levilutz/cve-2021-30860
Scan for evidence of CVE-2021-30860 (FORCEDENTRY) exploit
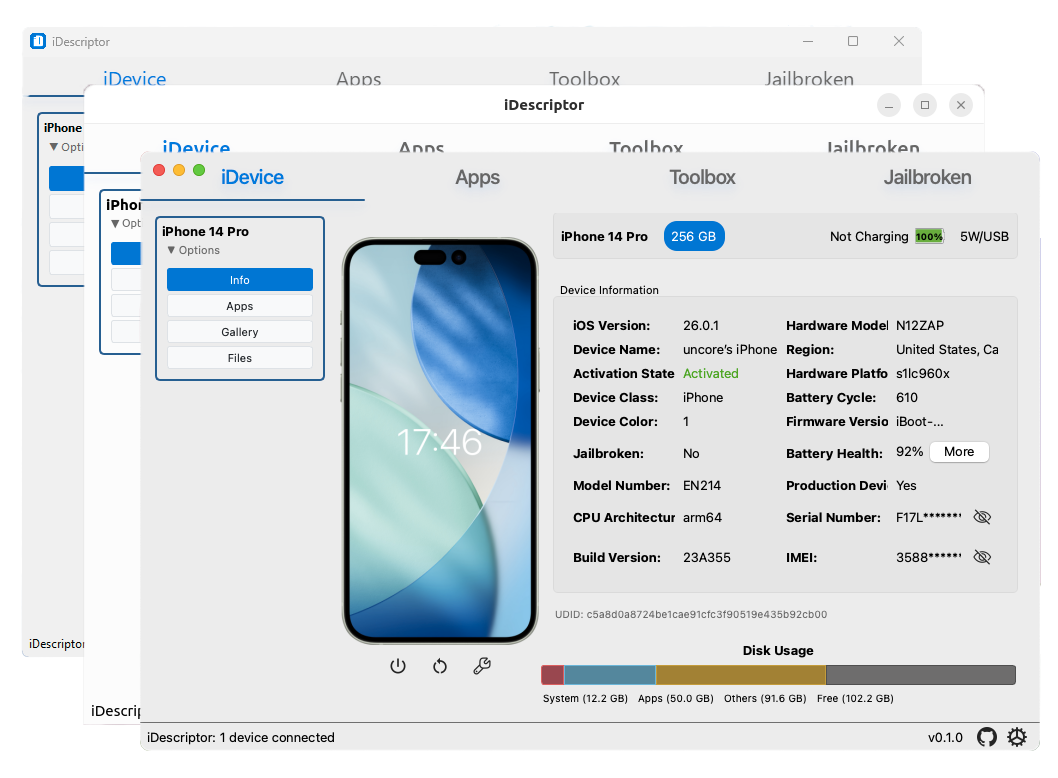 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt