
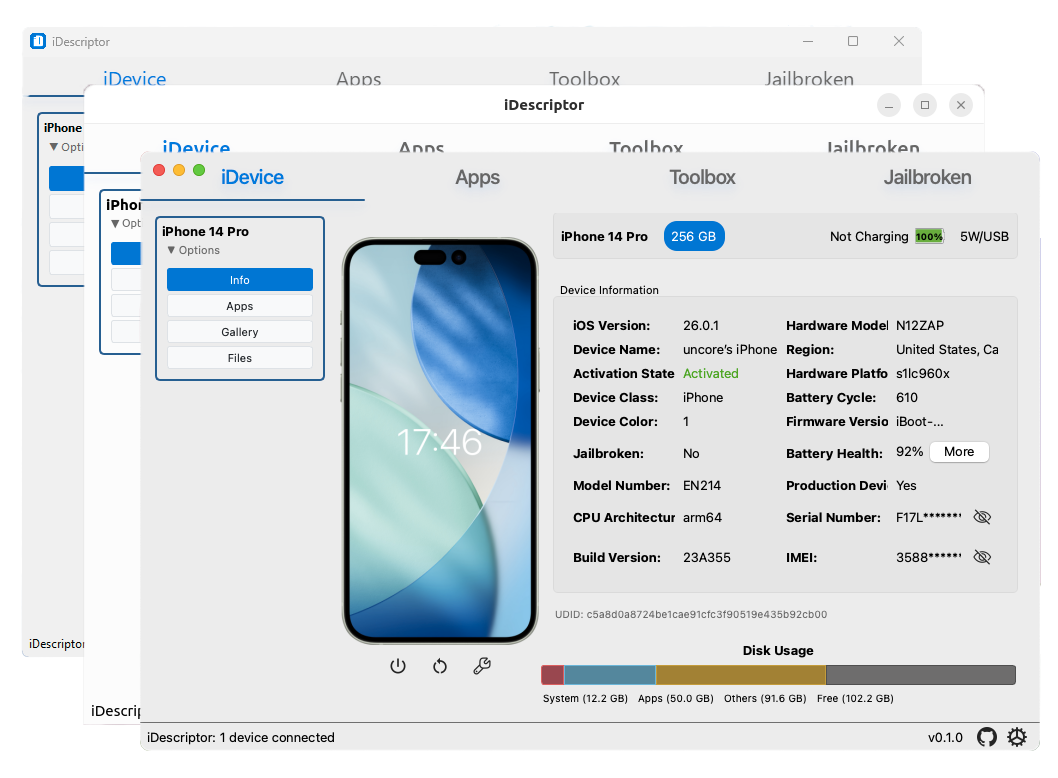
iDescriptor
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.6k
idescriptor/idescriptorprivacy-first, open-source and free idevice management tool written in Rust and Qt
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…