

autopsy
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
data-recoverydigital-forensicsdisk-forensics+3
3.4k
sleuthkit/autopsyAutopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
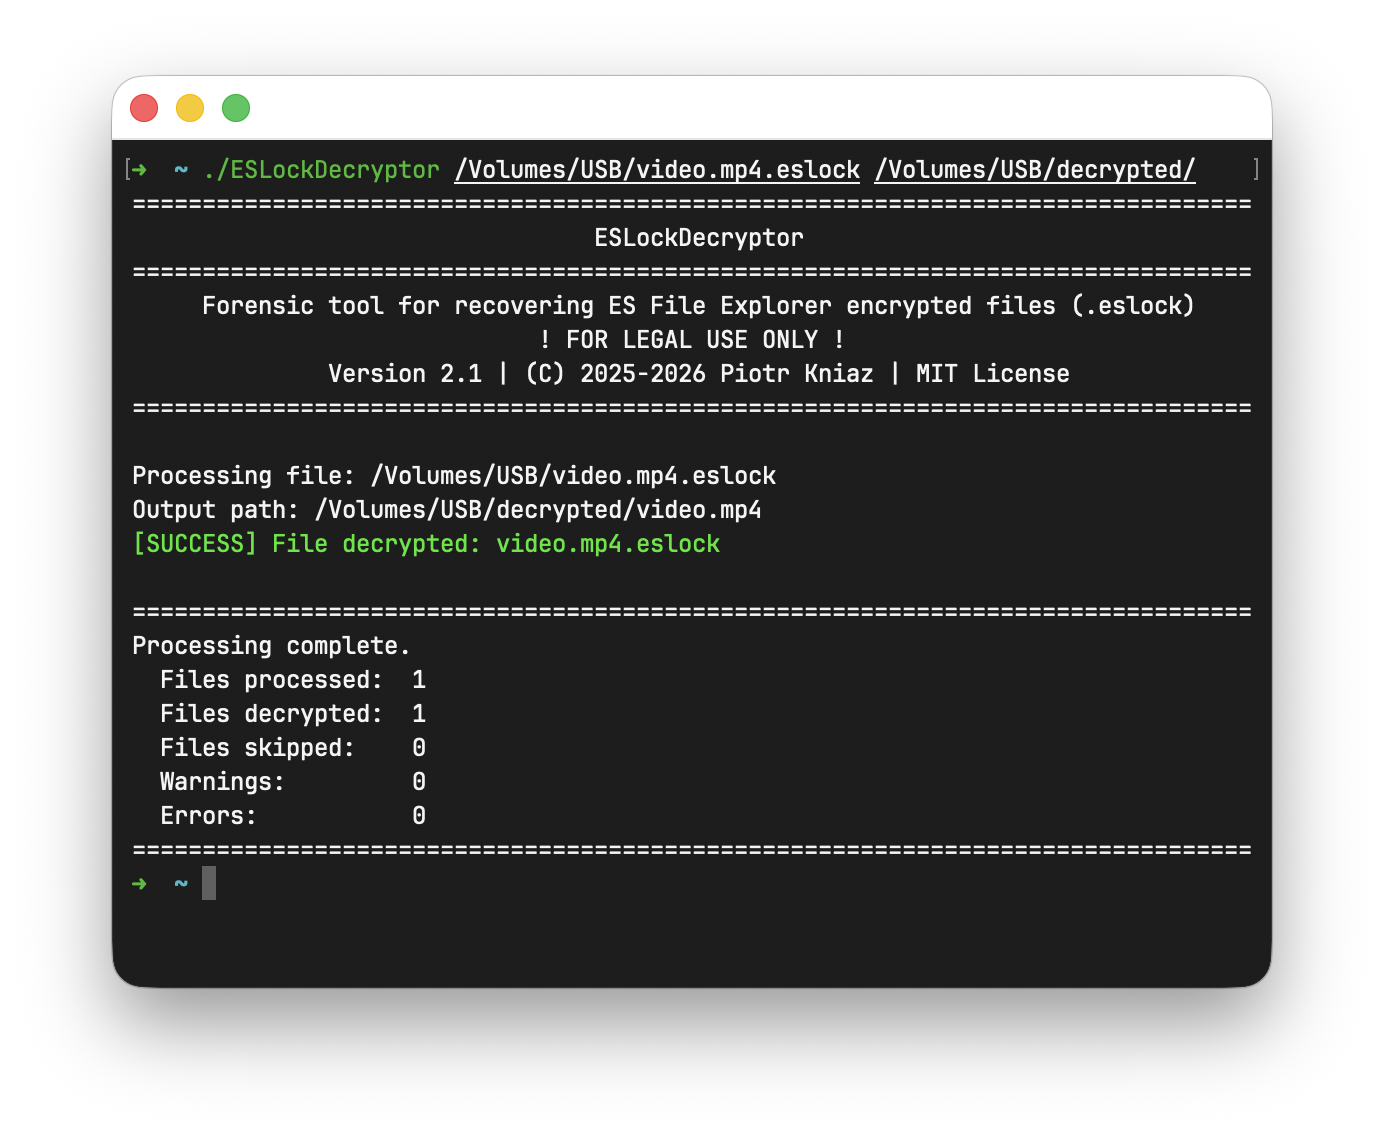 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 cristianzsh/forensictools
Collection of forensic tools
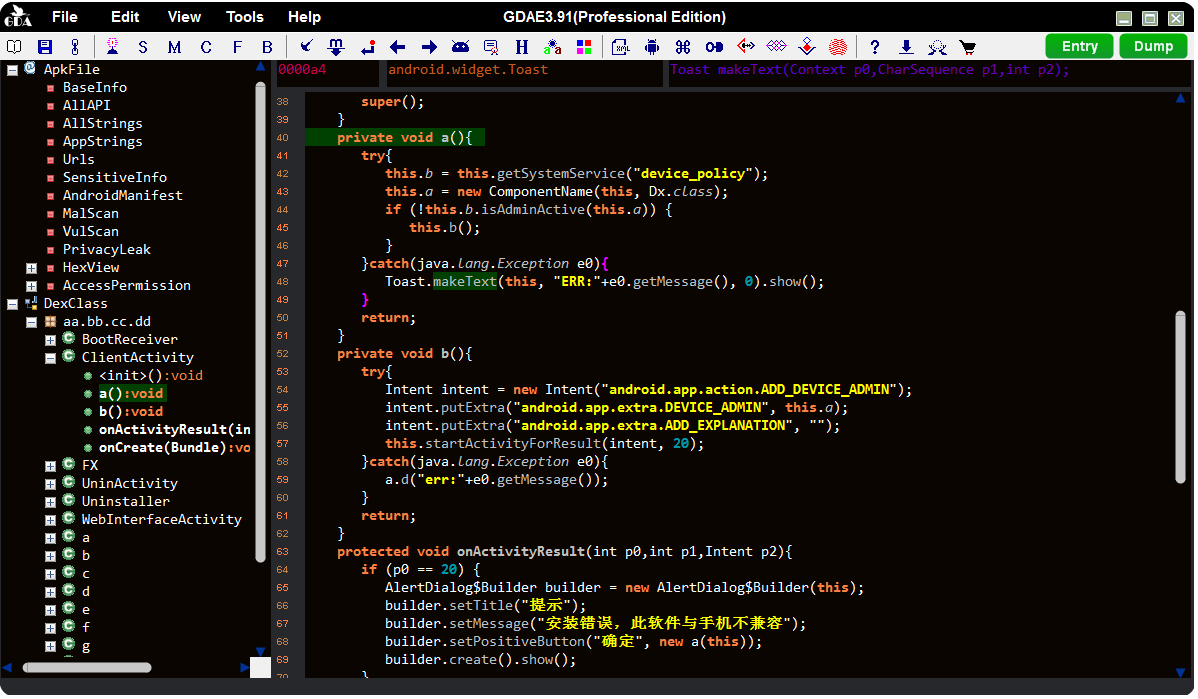 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
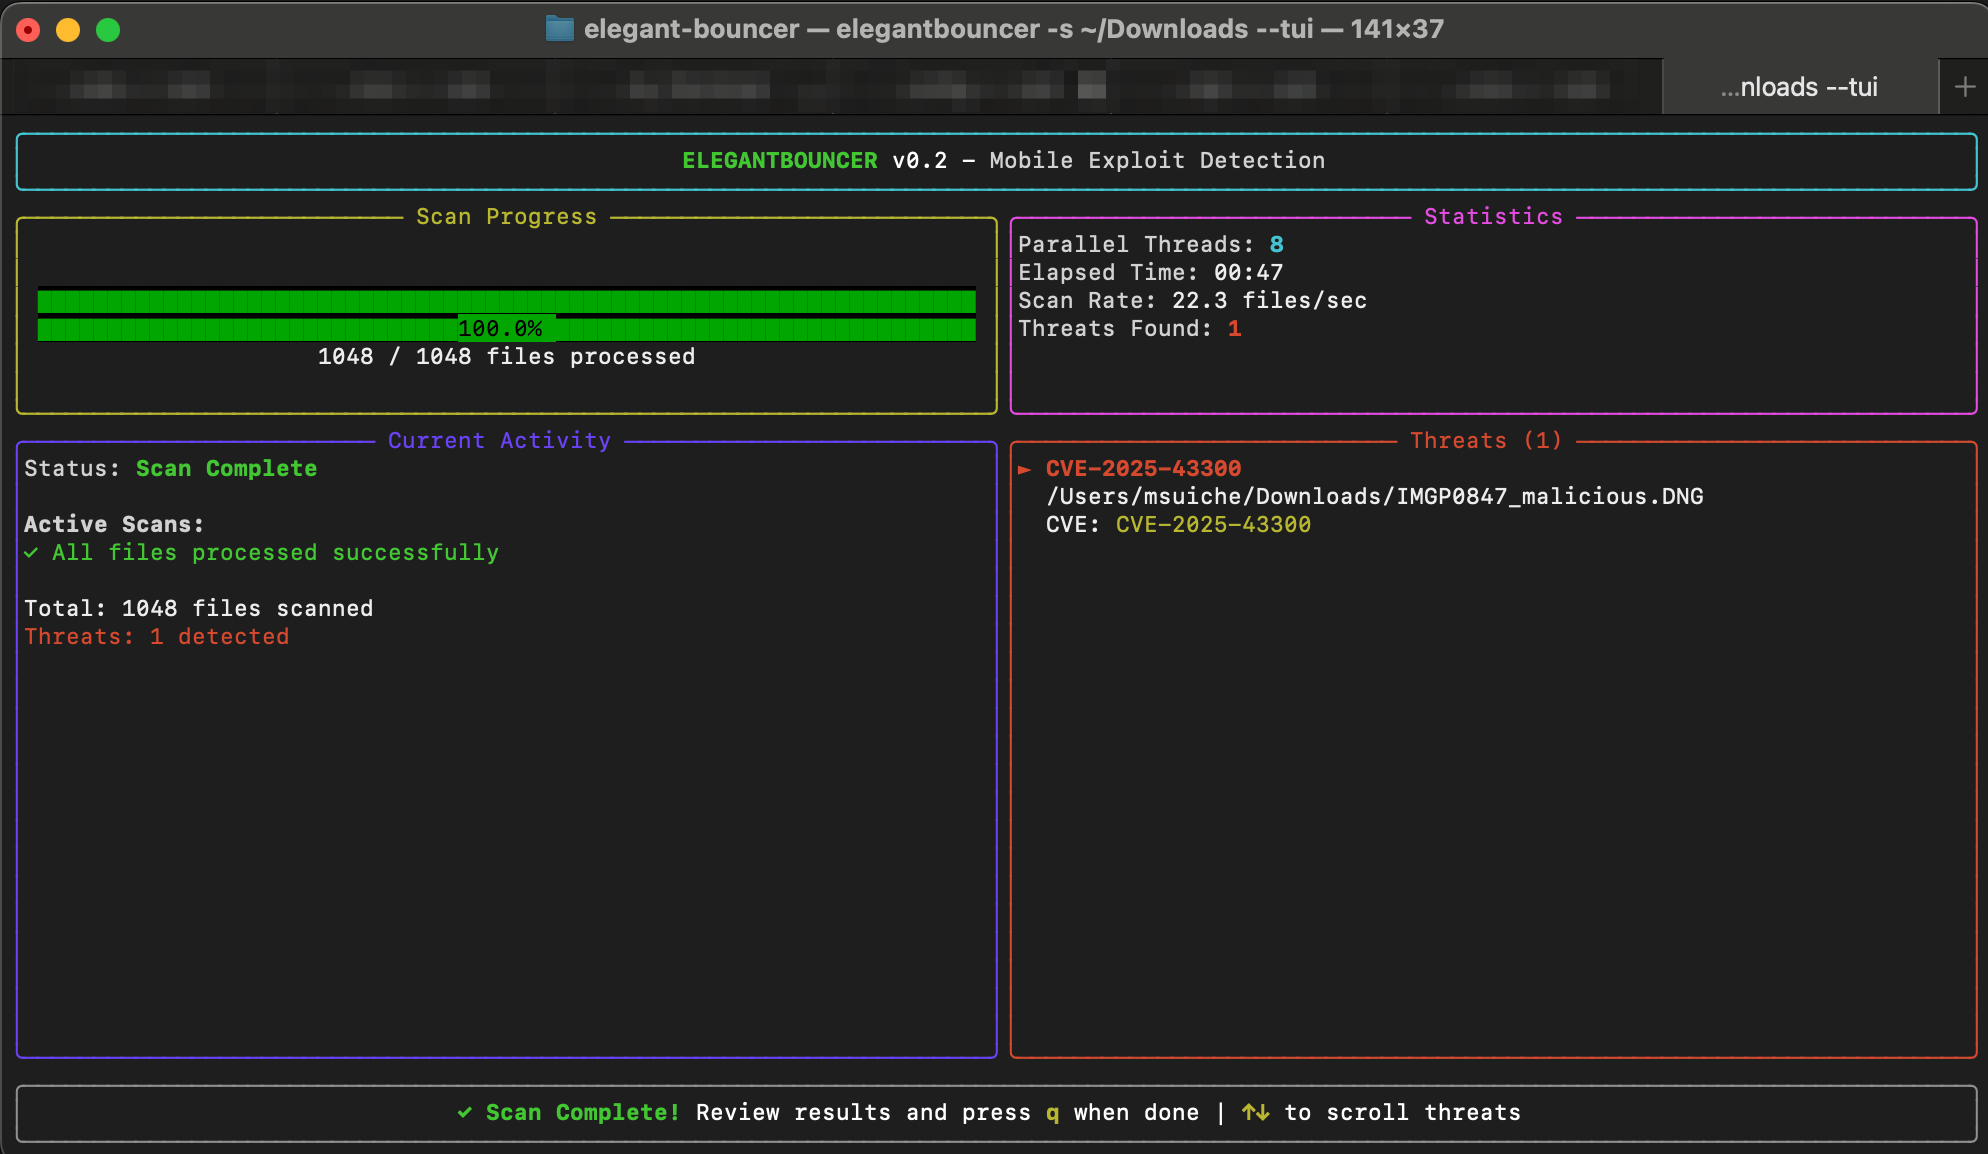 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool

 telegrip/telegrip
GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…