
ipa-medit
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
binary-analysisios-securitymemory-forensics+3
211
sterrasec/ipa-meditMemory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
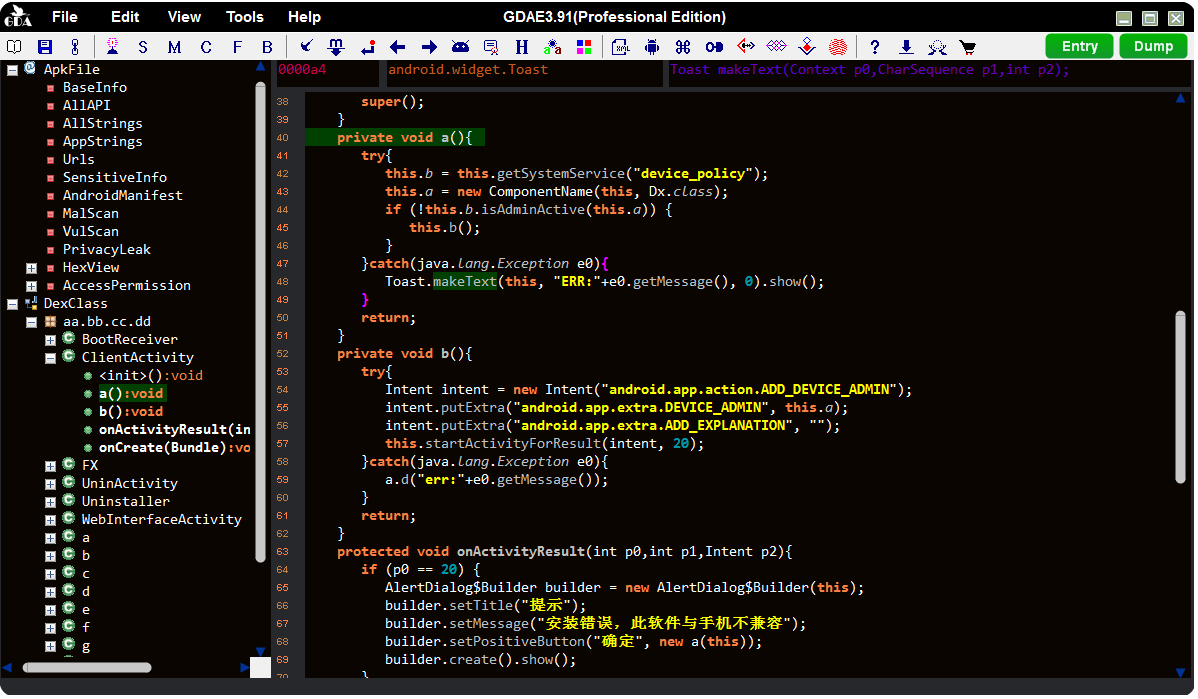 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
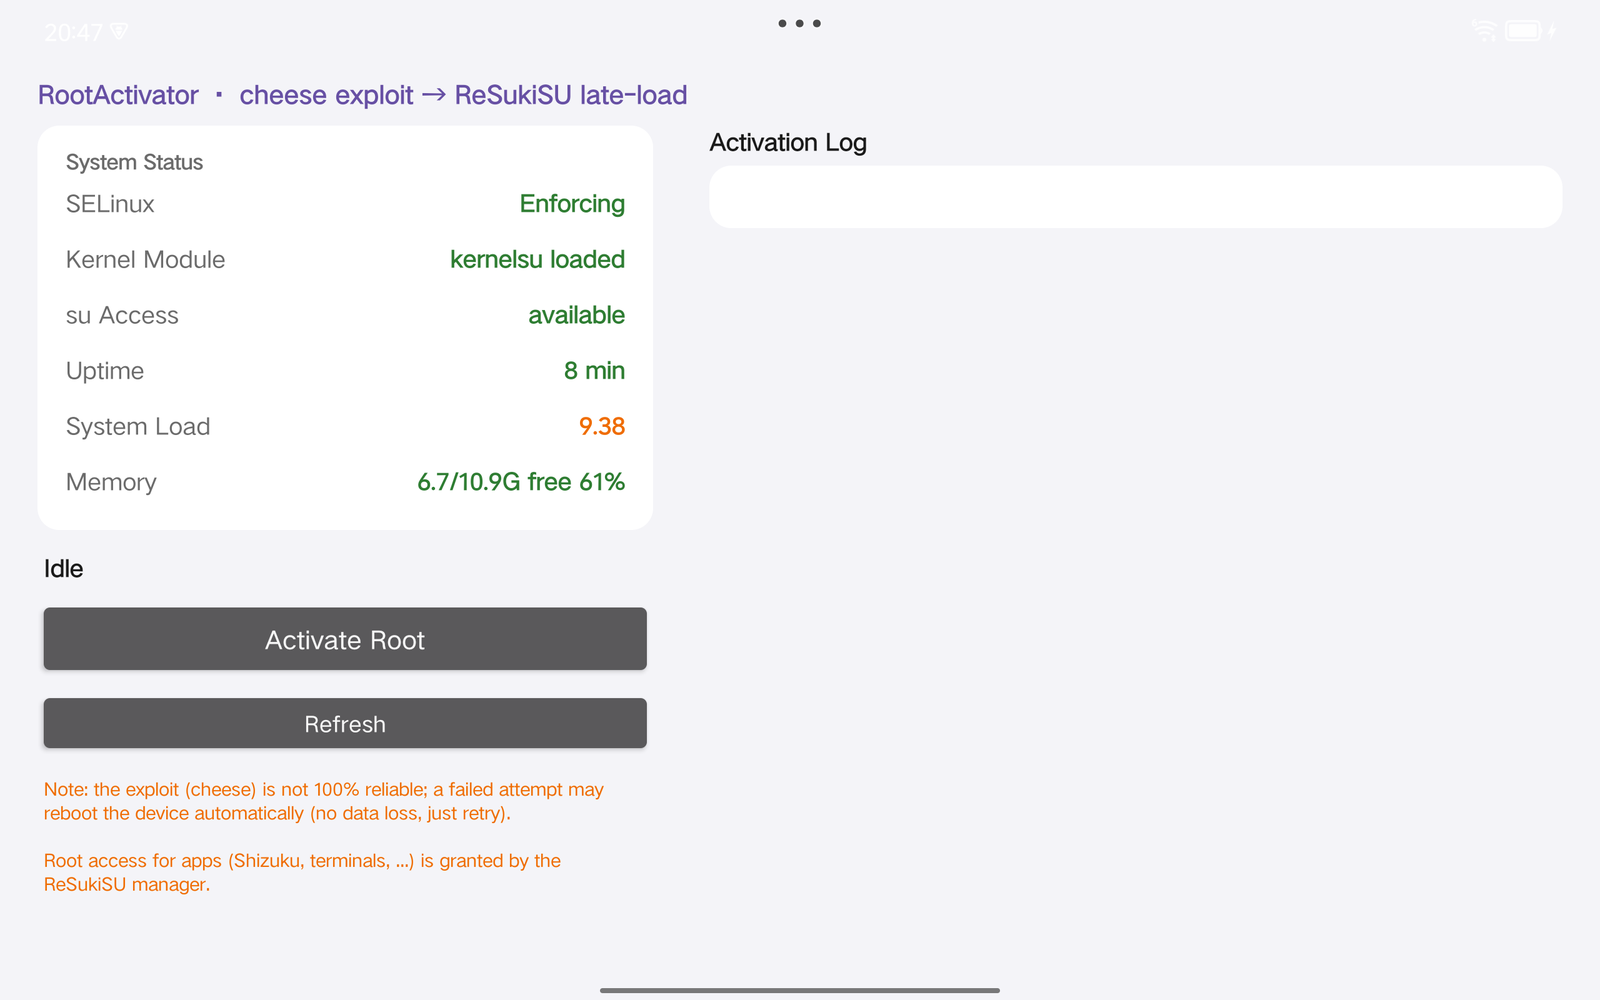 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs