
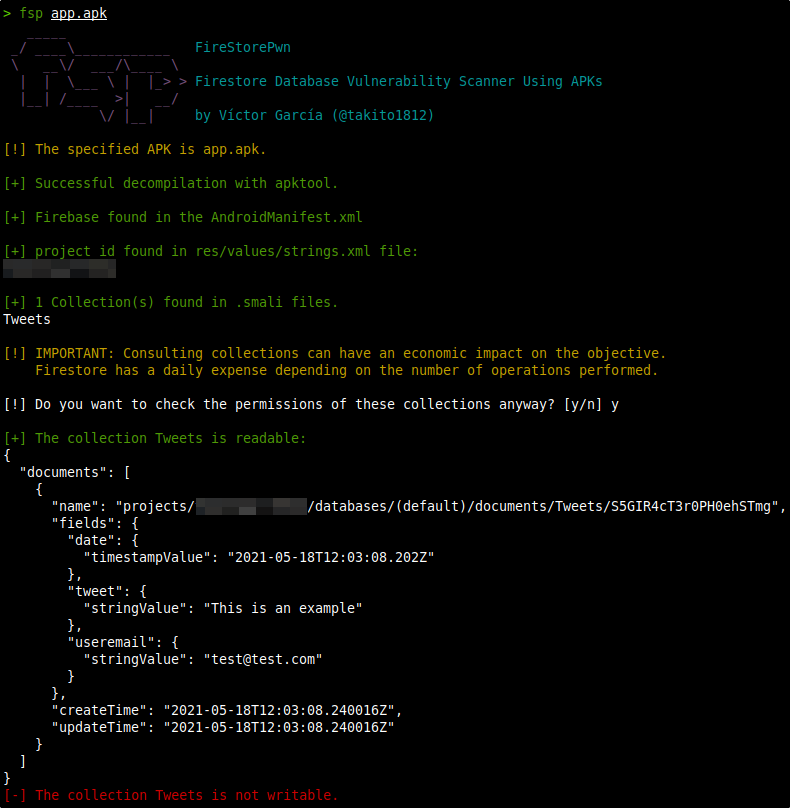
FireStorePwn
 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
android-securitydatabase-securitymobile-app-pentesting+2
655 years ago
takito1812/firestorepwnfsp - Firestore Database Vulnerability Scanner Using APKs
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
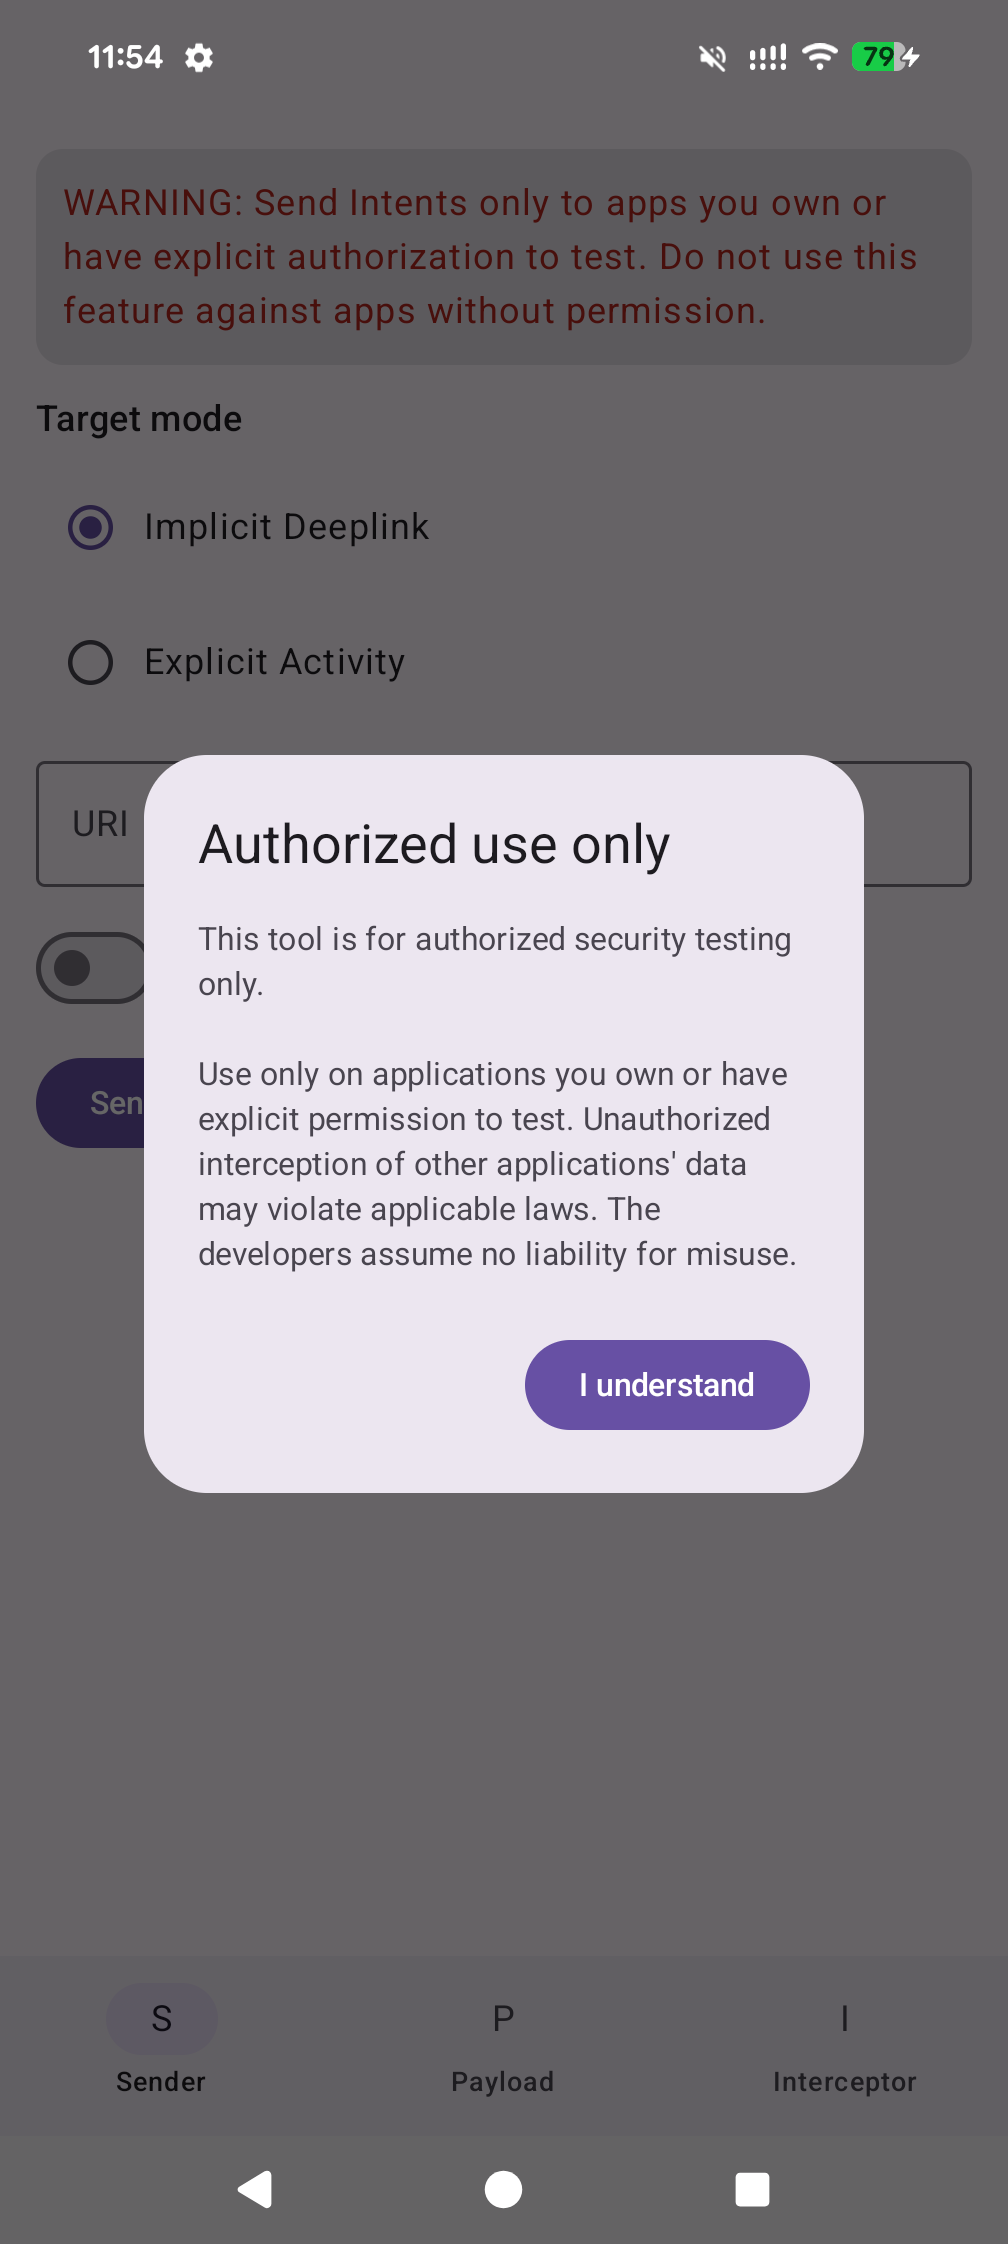 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…