
blackboxprotobuf
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
binary-analysisdigital-forensicsmobile-app-pentesting+3
735
nccgroup/blackboxprotobufBlackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
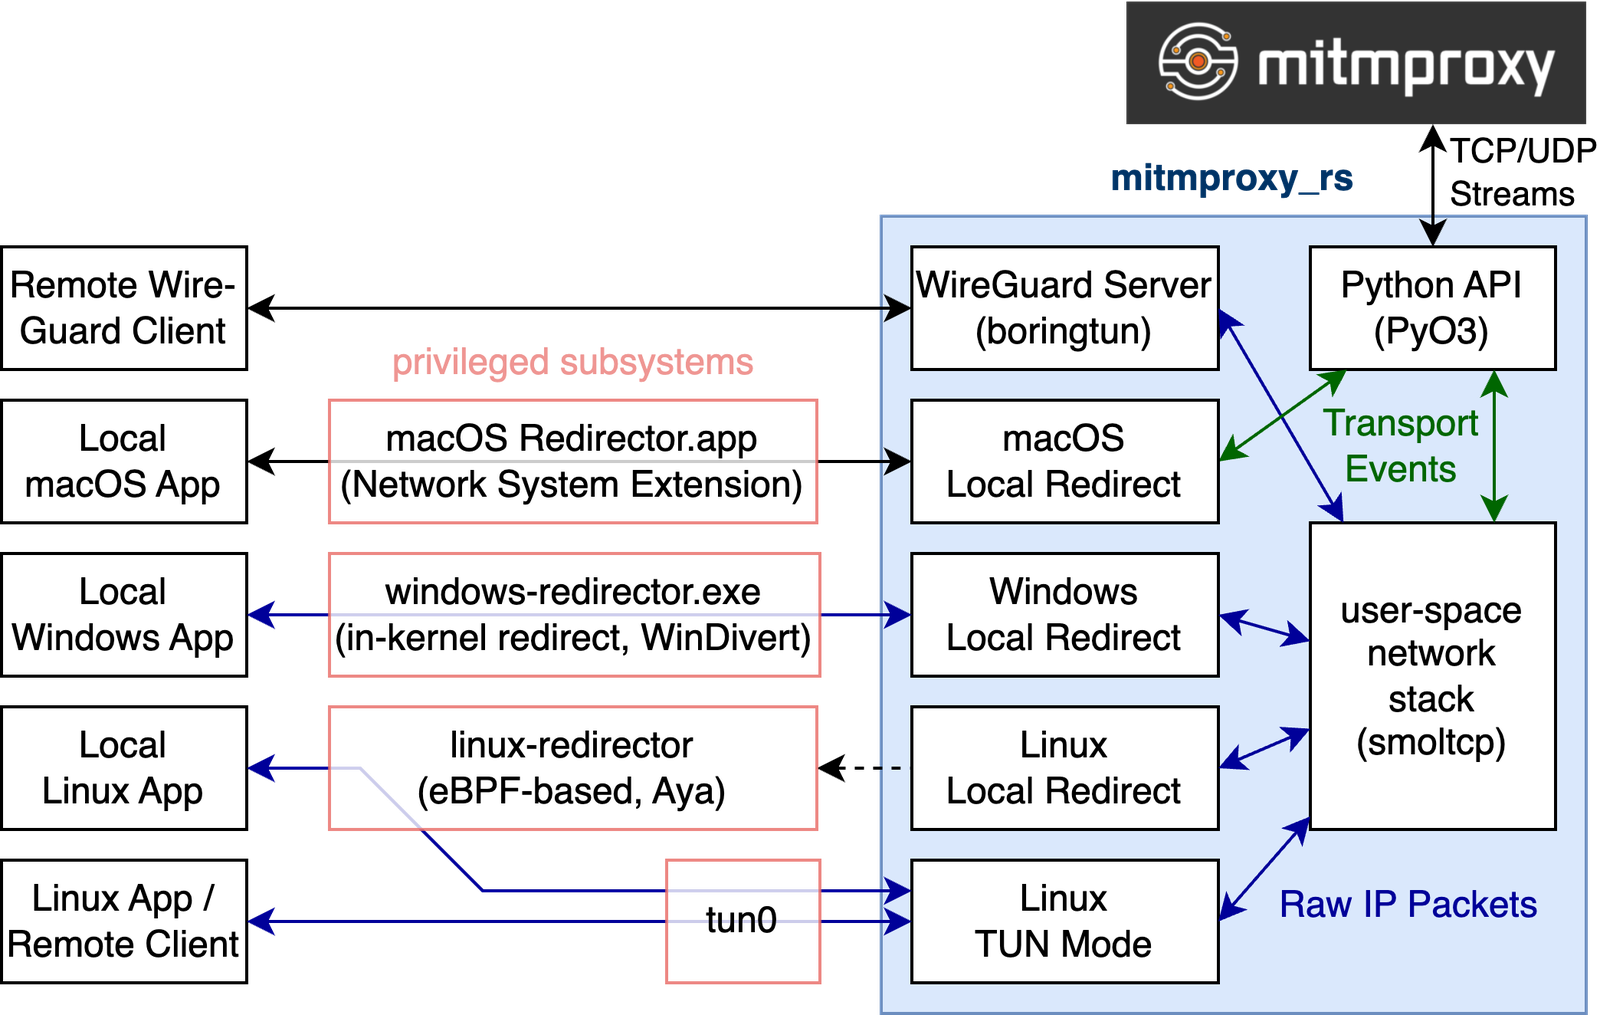 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
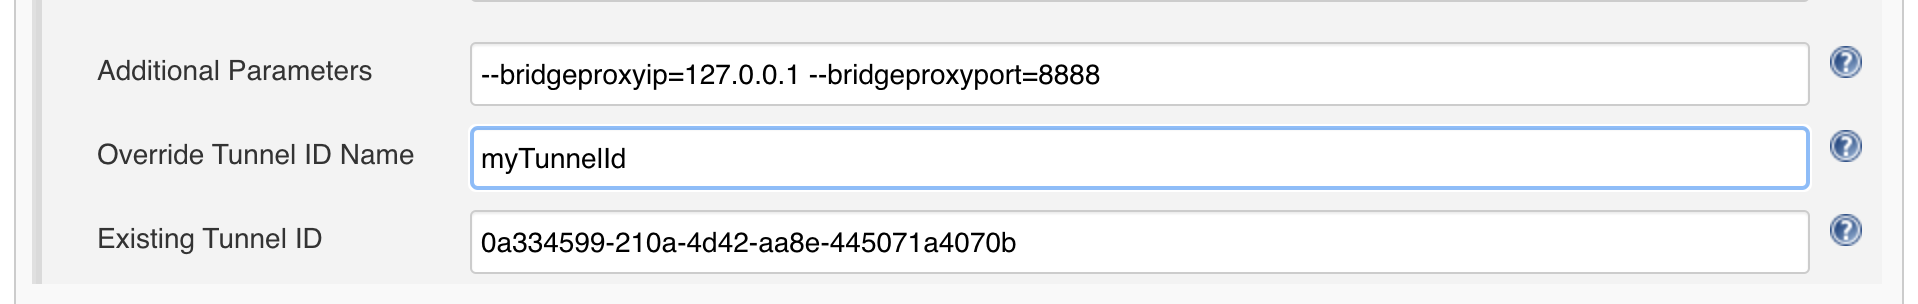 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
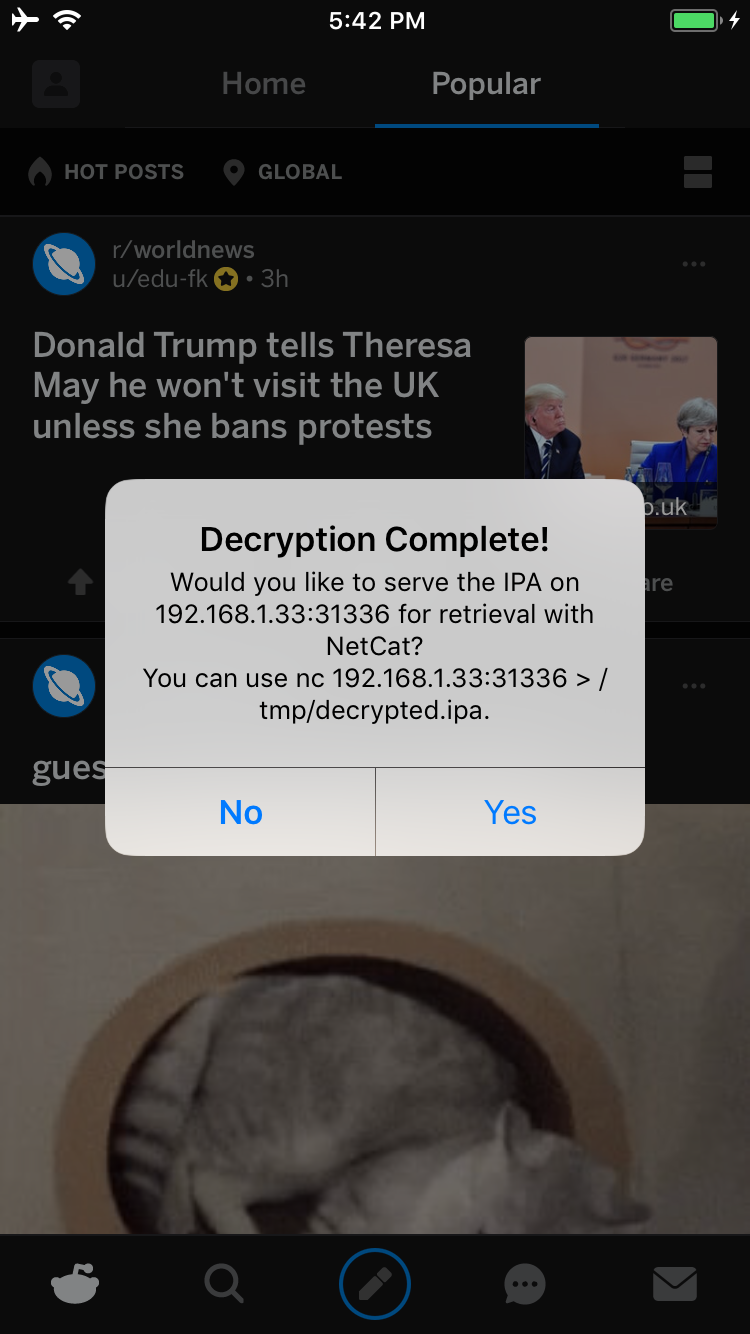 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.