
AuroraStore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.

Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Android security guides, roadmap, docs, courses, write-ups, and teryaagh.

Unofficial frida extension for VSCode

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS

Fermion, an electron wrapper for Frida & Monaco.

Intentionally vulnerable Android application.

MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.

Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.

Static and dynamic Android application security analysis

LD_PRELOAD magic for Android's AssetManager

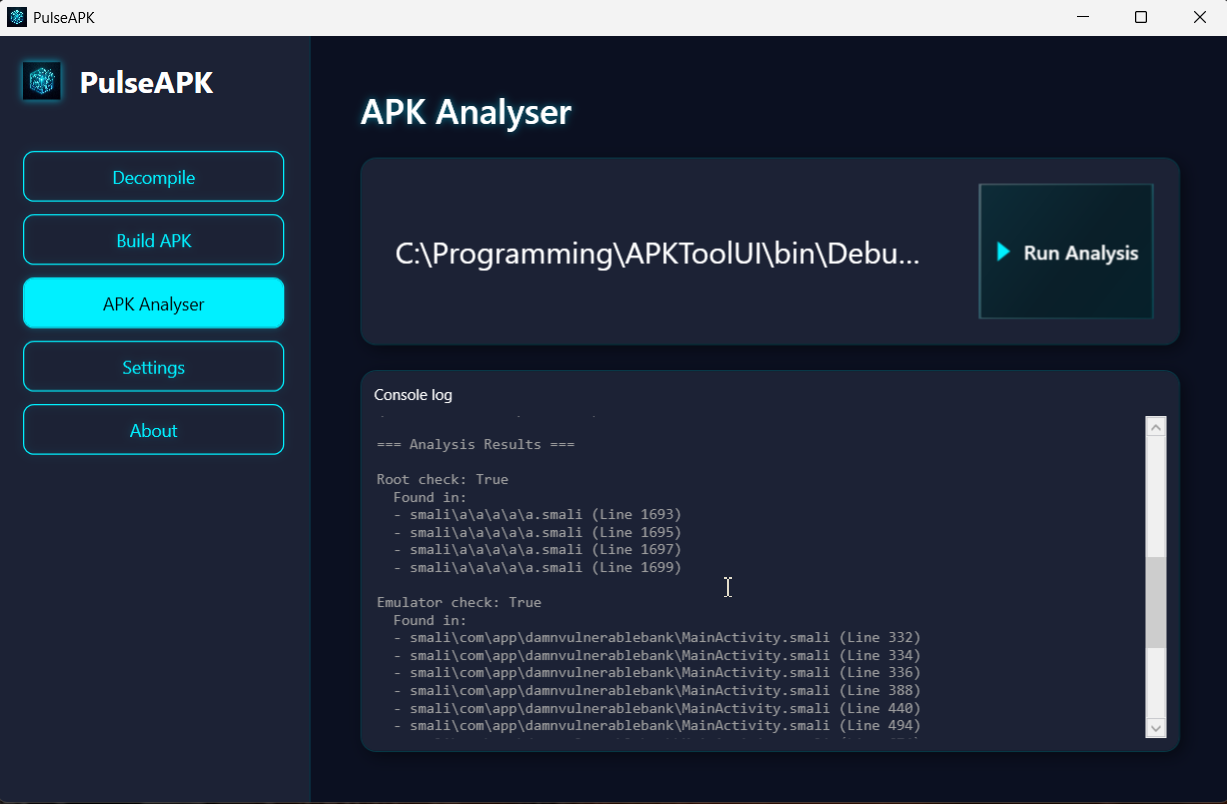
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…

PoC Exploit for AOSP UserDictionary Content Provider (CVE-2018-9375)

CVE-2020-0096-StrandHogg2 复现

Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking

Demo Android application for CVE-2019-9465

Android exploit collection with C-based payloads for mobile device penetration testing and security research.

vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)