
frida-interception-and-unpinning
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
android-securityios-securitymobile-app-pentesting+4
2.3k
httptoolkit/frida-interception-and-unpinningFrida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370
 a0zhar/quarkpoc
iOS Application w/Implementation of CVE-2024-27804
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
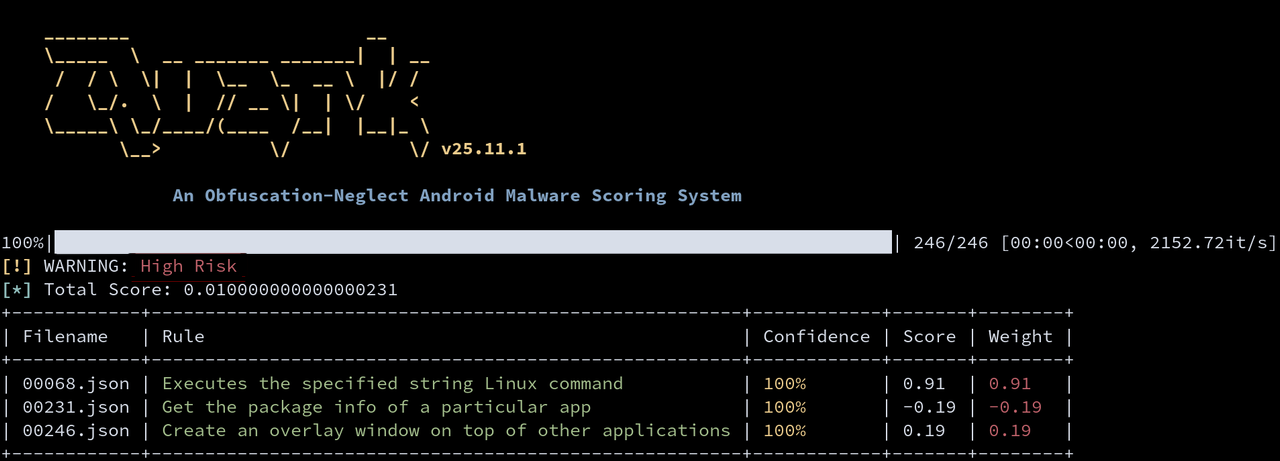 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…