
CVE-2023-41898_Lab
 lazybear8372/cve-2023-41898_lab
Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
android-securityeducationlabs-practice+2
lazybear8372/cve-2023-41898_labWalk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
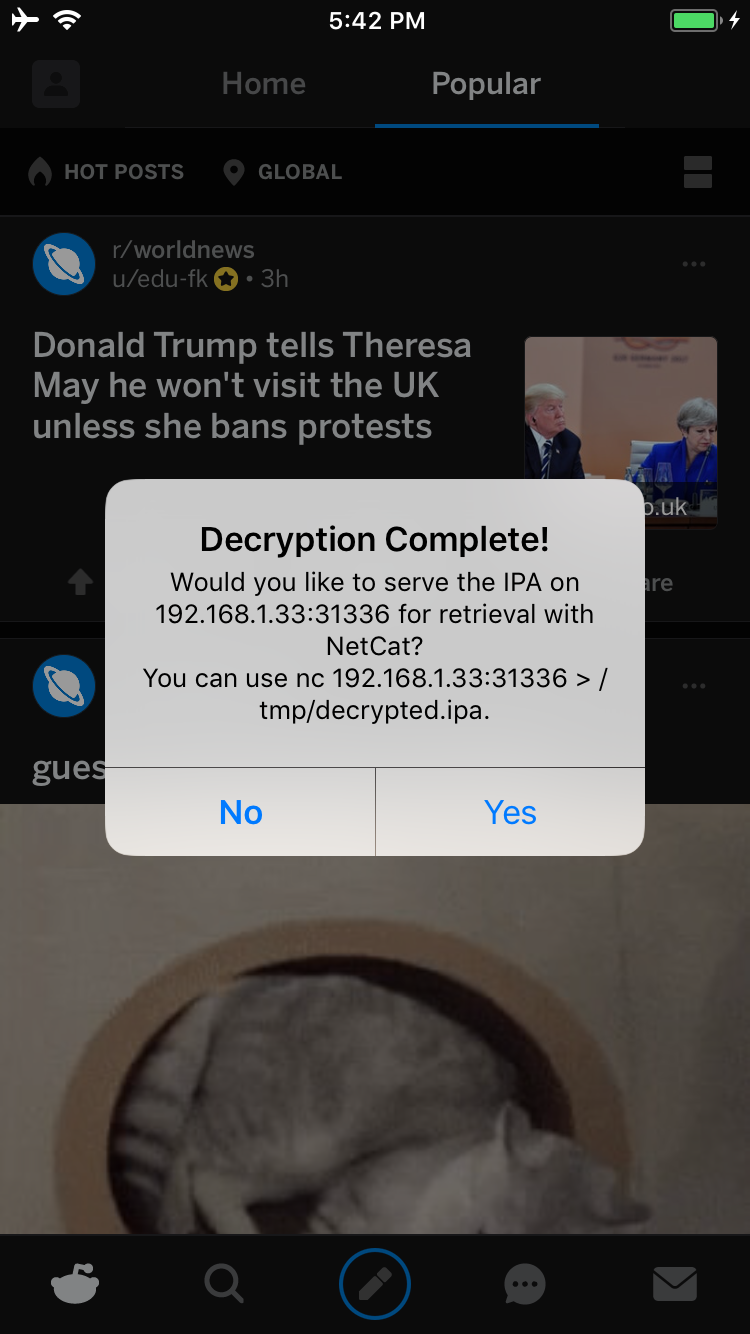 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370
 a0zhar/quarkpoc
iOS Application w/Implementation of CVE-2024-27804