
OrganizerTransaction
 michalbednarski/organizertransaction
PoC for CVE-2021-39749, allowing starting arbitrary Activity on Android 12L Beta
android-securityexploitationmobile-app-pentesting+2
37
michalbednarski/organizertransactionPoC for CVE-2021-39749, allowing starting arbitrary Activity on Android 12L Beta
 naonymous101/cve-2022-46638
Blog Pribadi
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
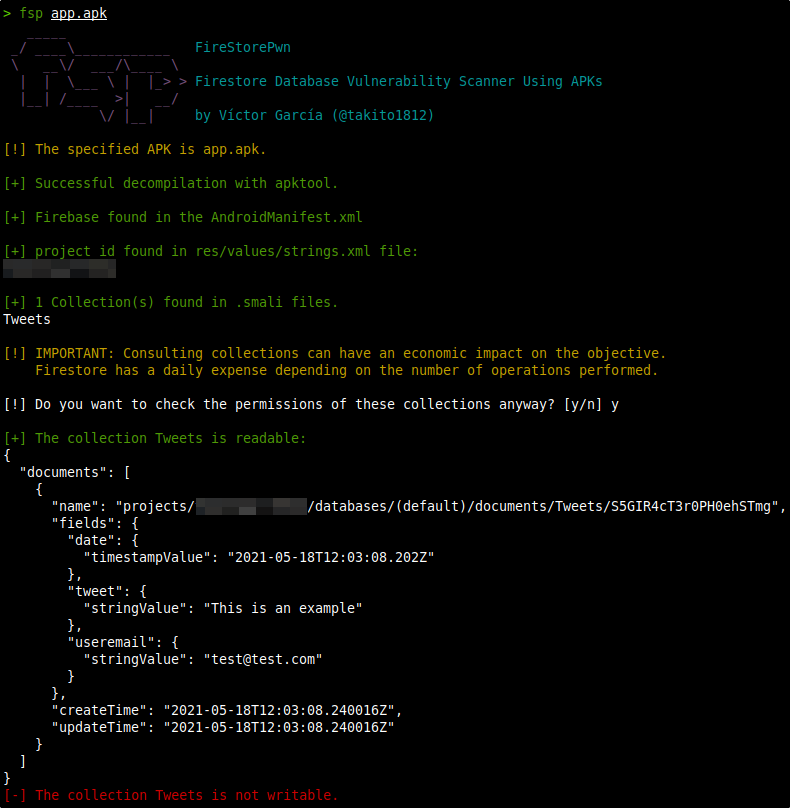 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 frida/frida
Main repo for hosting release binaries
 androguard/androguard
Reverse engineering and pentesting for Android applications
 codinggay/blackdex
Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
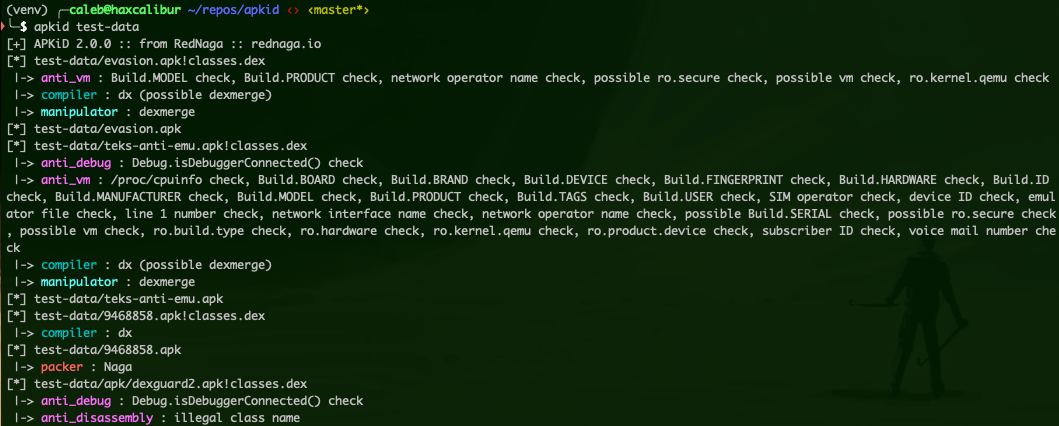 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
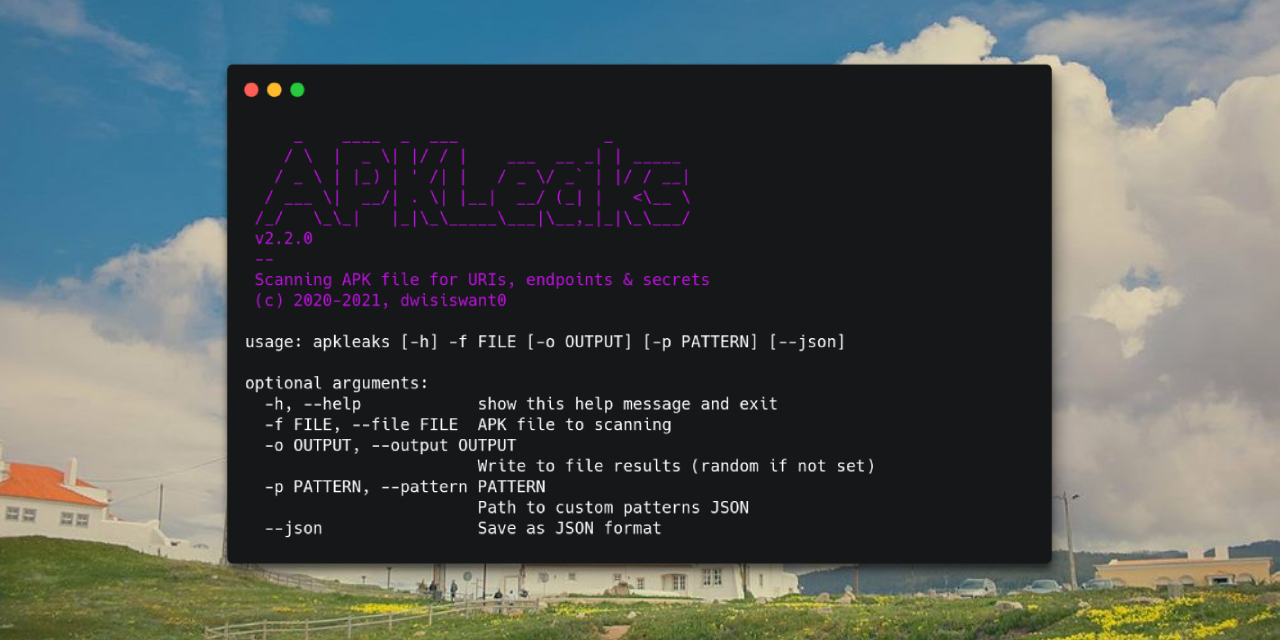 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.