
CVE-2019-9465
 michaelsplayground/cve-2019-9465
Demo Android application demonstrating CVE-2019-9465 for security testing and vulnerability analysis on mobile platforms.
android-securityexploitationmobile-app-pentesting+2
michaelsplayground/cve-2019-9465Demo Android application demonstrating CVE-2019-9465 for security testing and vulnerability analysis on mobile platforms.
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB

 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 nowsecure/r2frida
Radare2 and Frida better together.
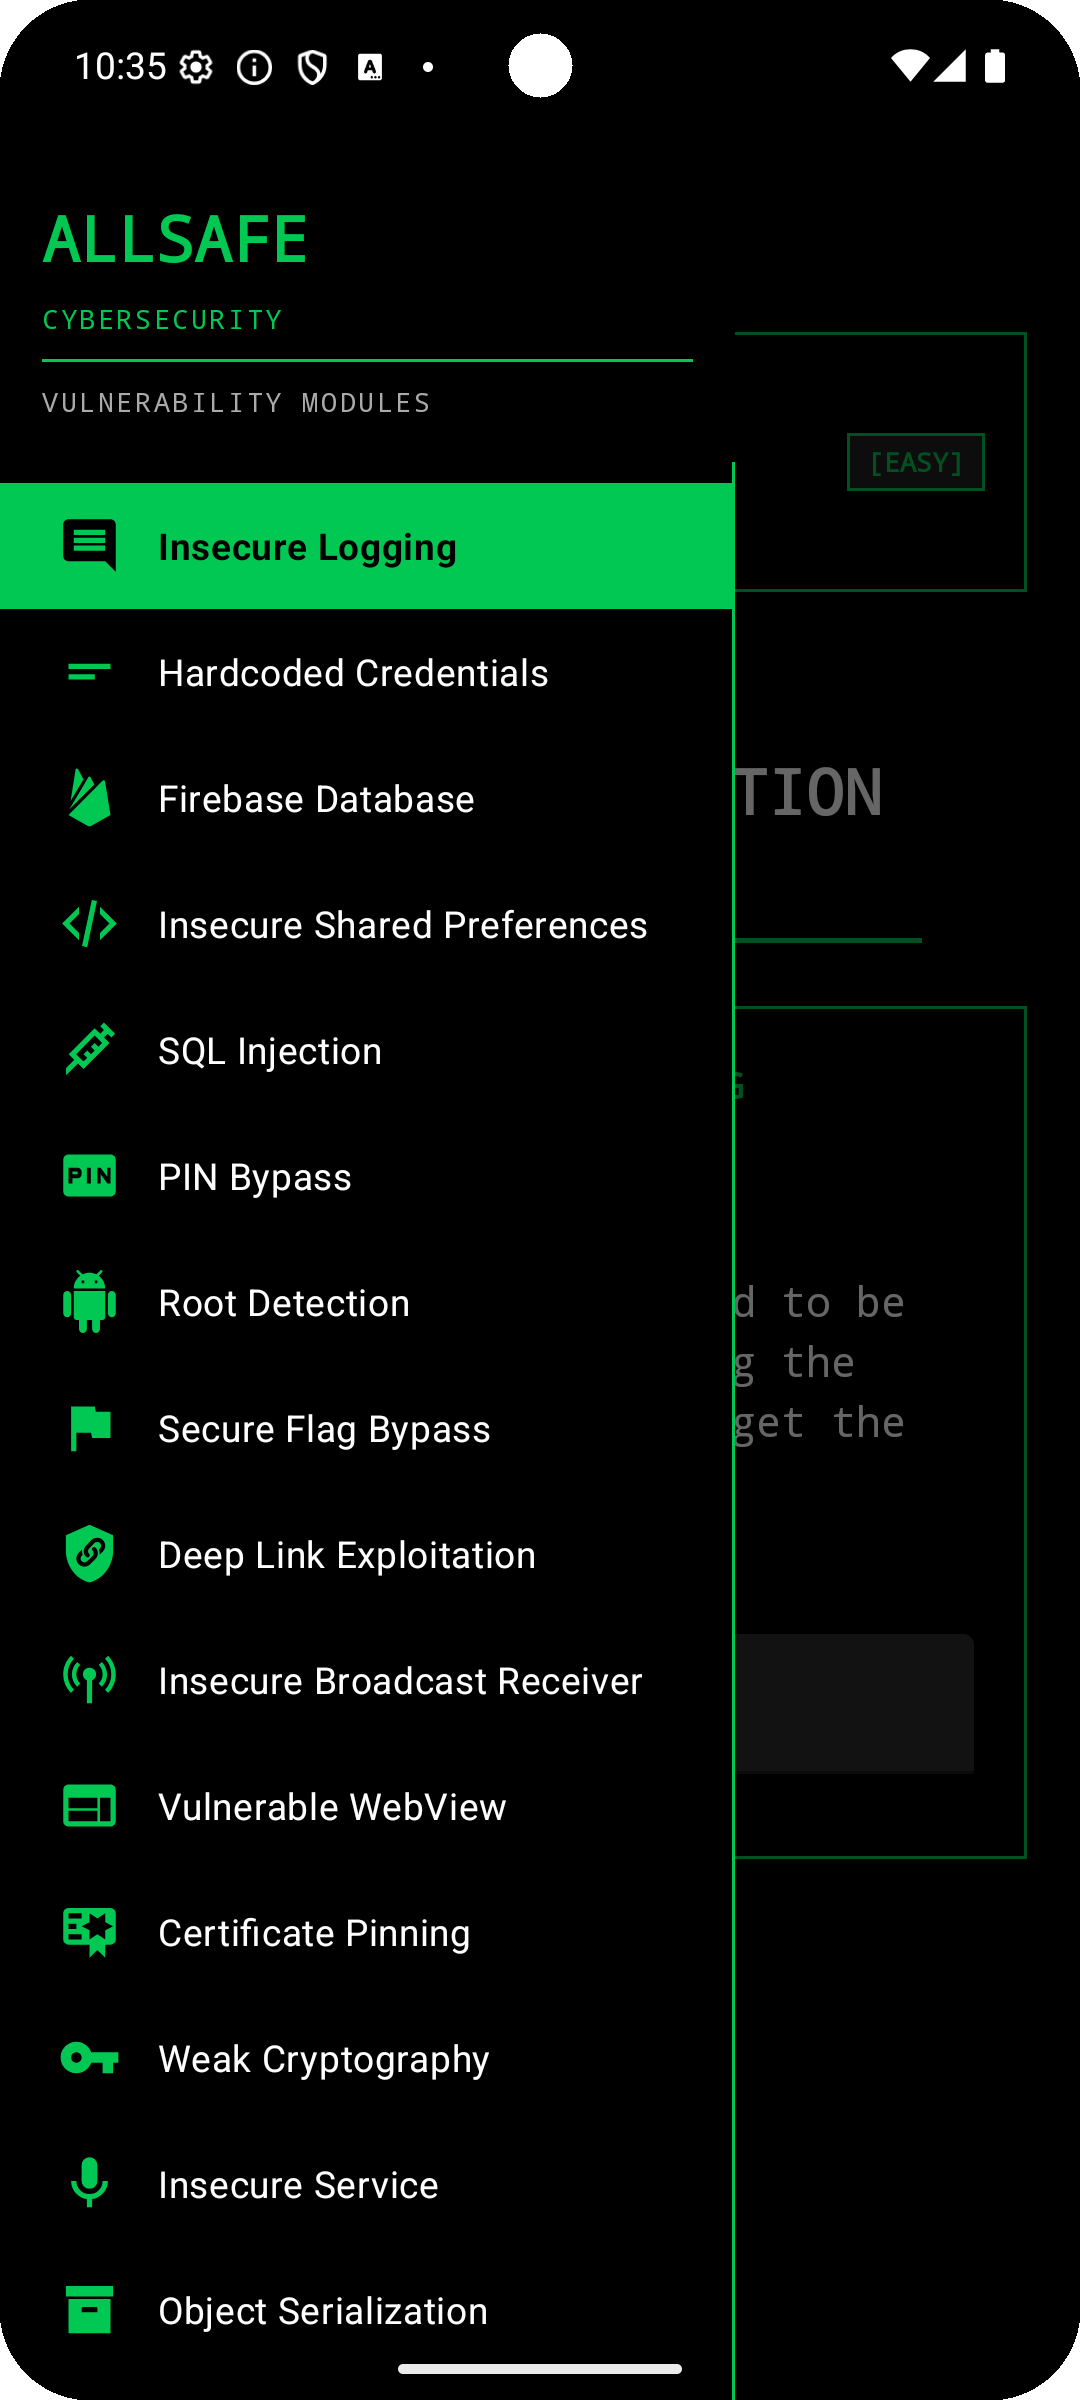 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
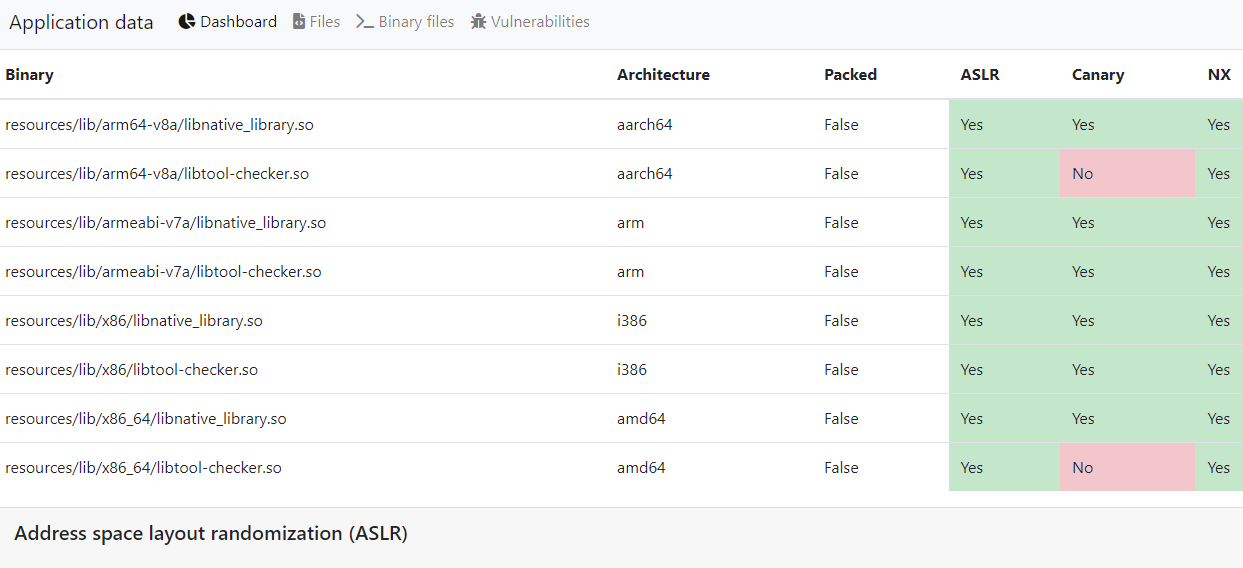 stefan2200/aparoid
Static and dynamic Android application security analysis
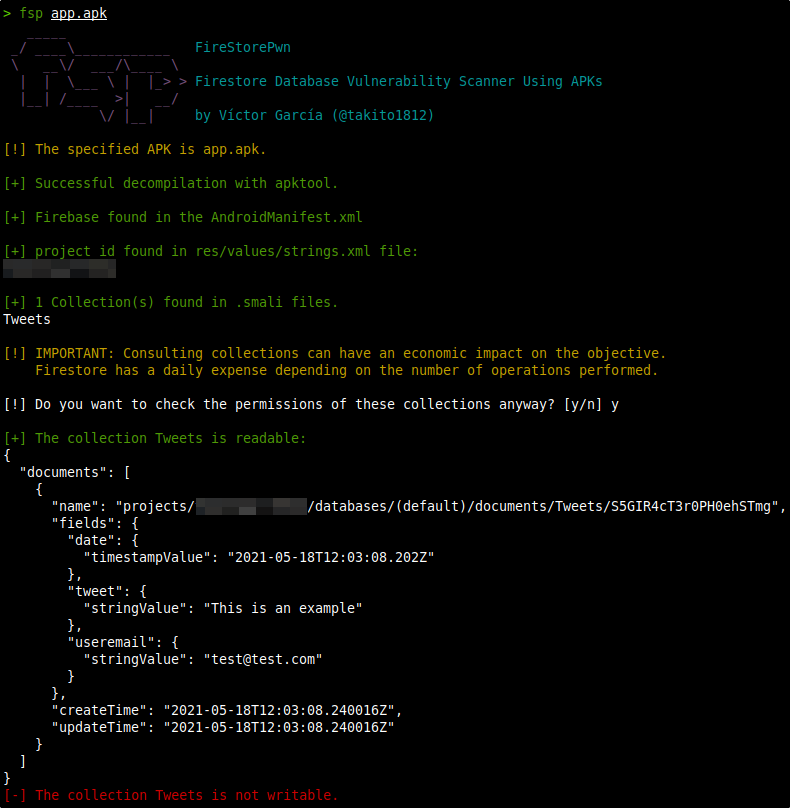 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
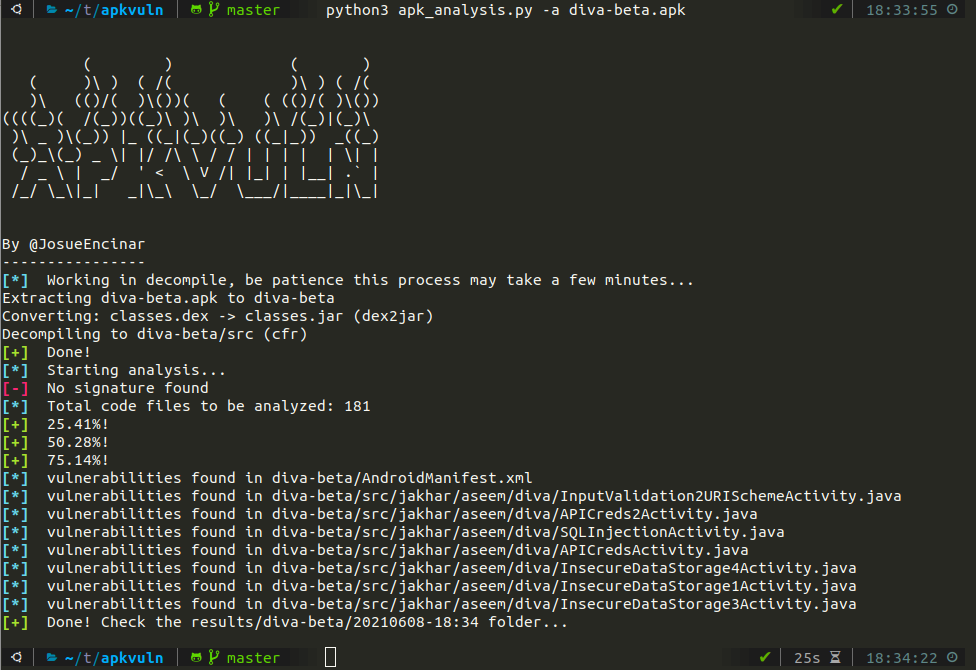 josue87/apkvuln
Static analysis of APKs with regular expressions
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 ymh001/meizu21-ghostlock-root
MEIZU 21 locked-bootloader runtime root via CVE-2026-43499 and KernelSU late-load
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…