
apk-mitm
 niklashigi/apk-mitm
🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
android-securitymobile-app-pentestingmobile-security+3
5.1k2 years ago
niklashigi/apk-mitm🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 stefan2200/aparoid
Static and dynamic Android application security analysis
 michalbednarski/organizertransaction
PoC for CVE-2021-39749, allowing starting arbitrary Activity on Android 12L Beta
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
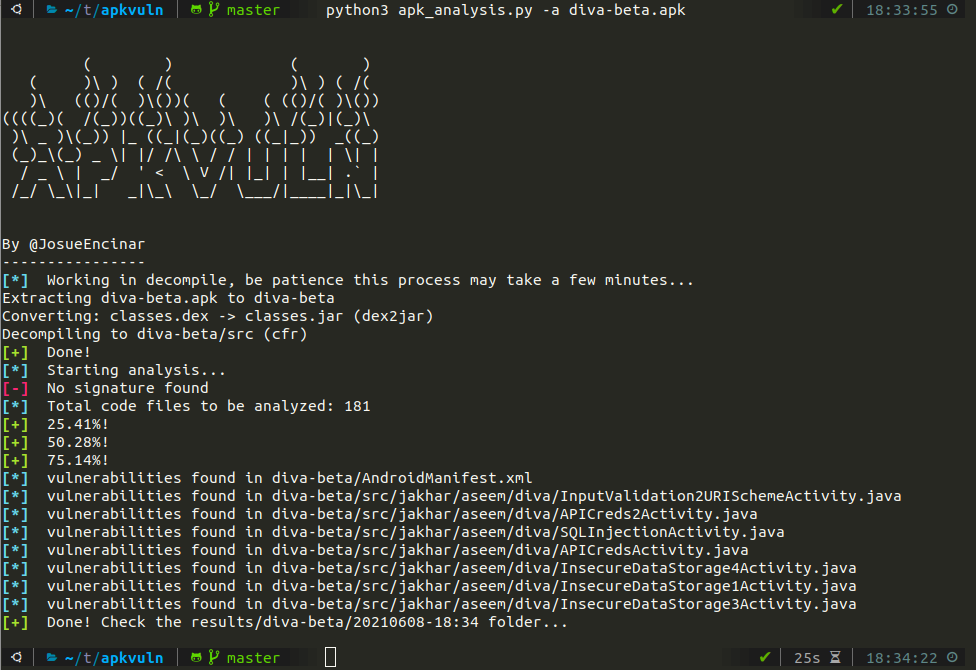 josue87/apkvuln
Static analysis of APKs with regular expressions
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
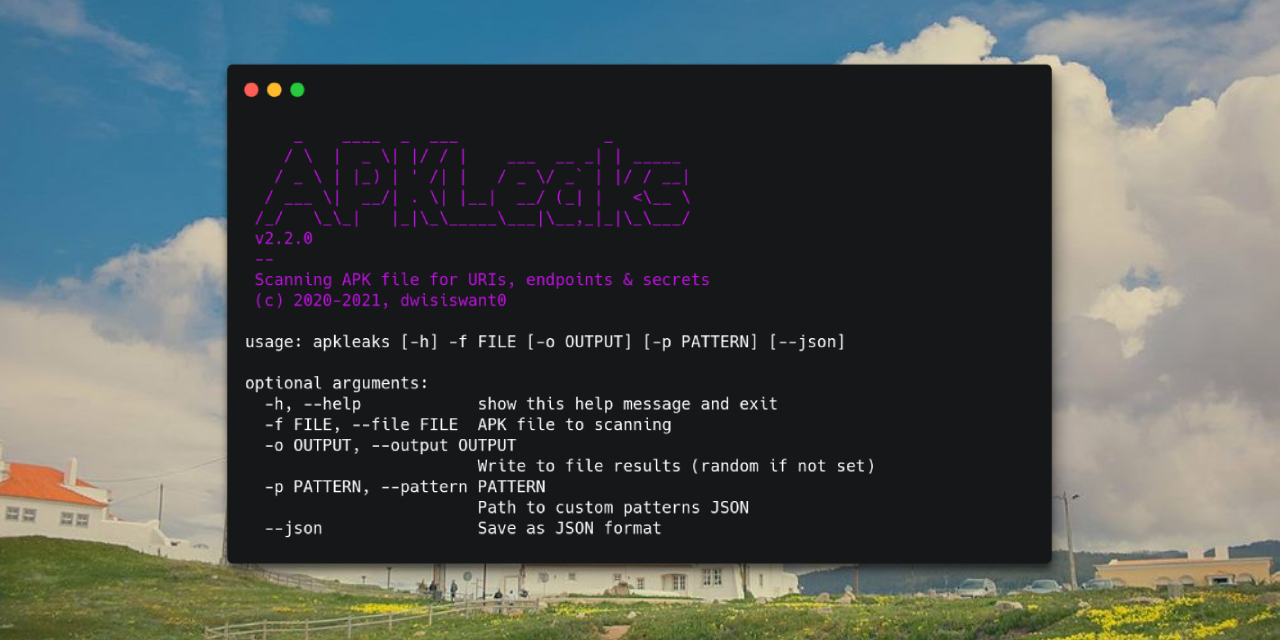 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
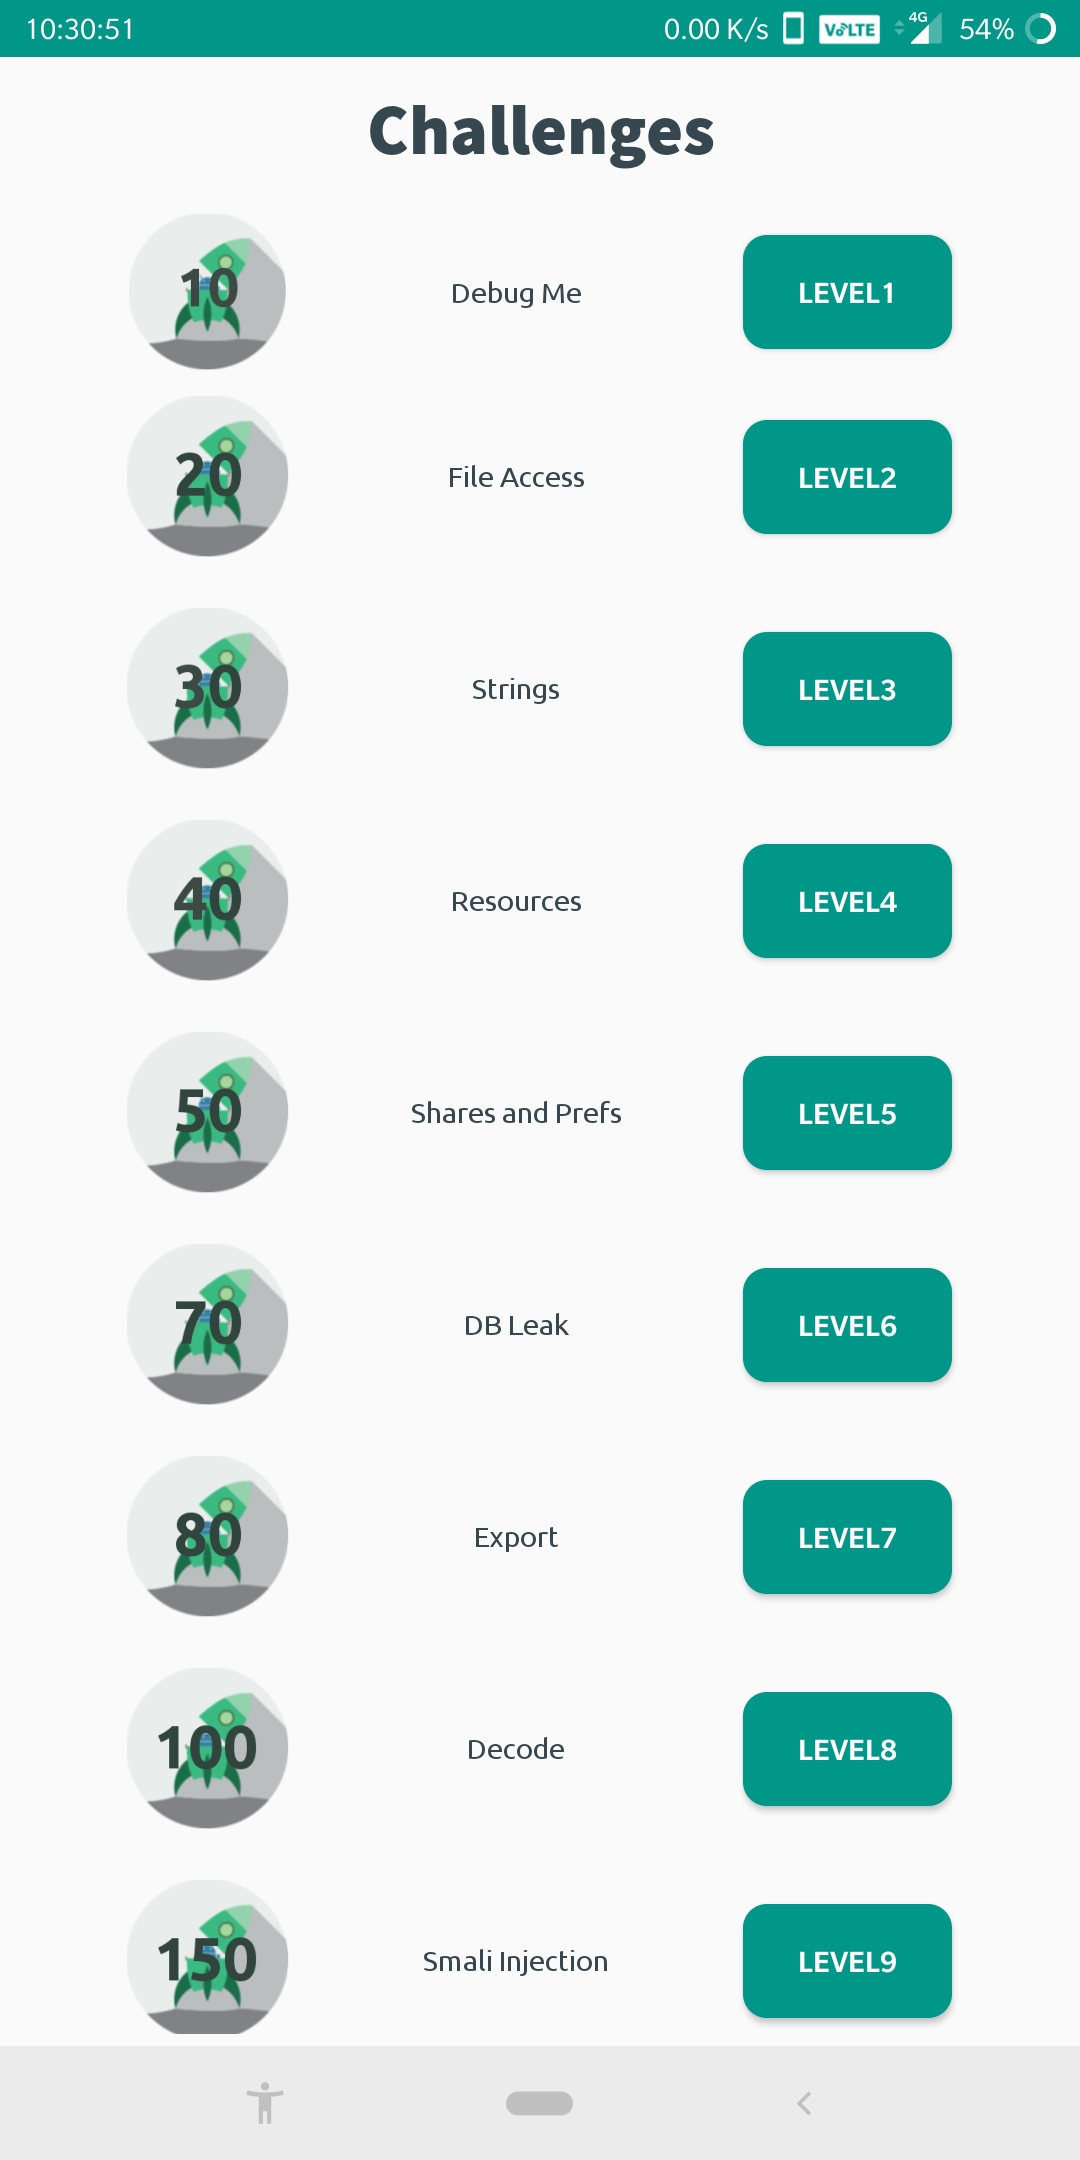 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
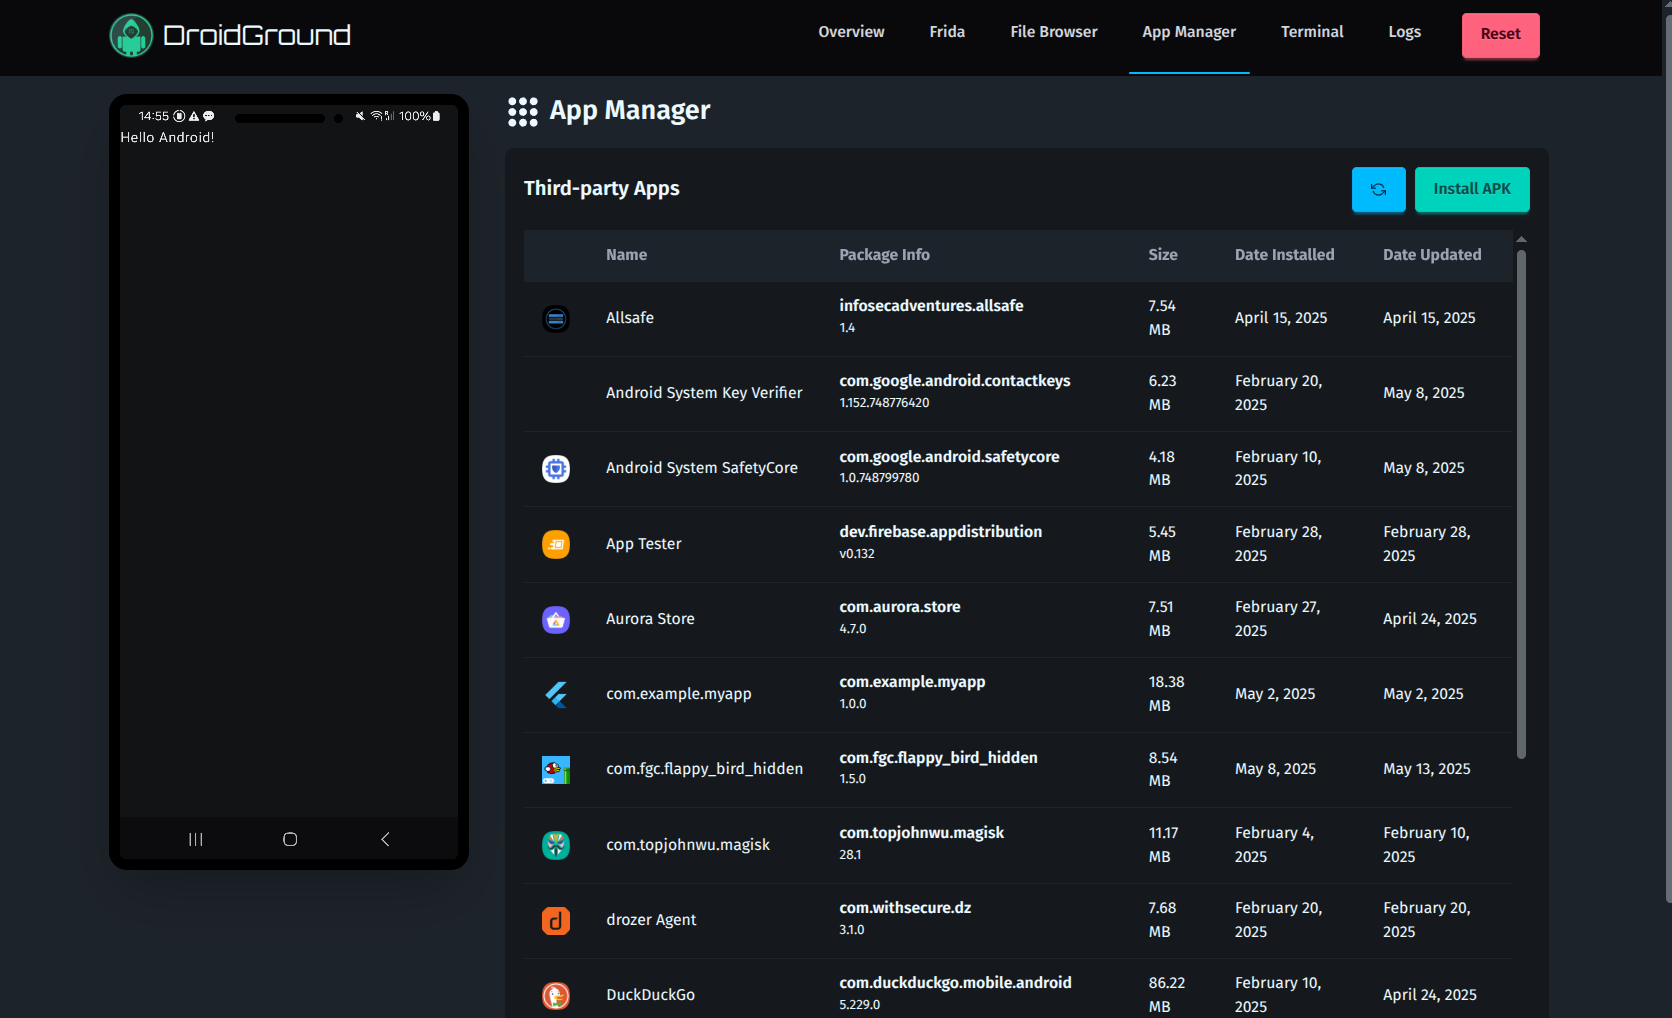 secforce/droidground
A flexible playground for Android CTF challenges.
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…