
kwetza
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
android-securityexploitationmobile-app-pentesting+3
sensepost/kwetzaPython script to inject existing Android applications with a Meterpreter payload.
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 nyamisty/ssl-kill-switch3
Next Generation SSLKillSwitch with much more support!
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
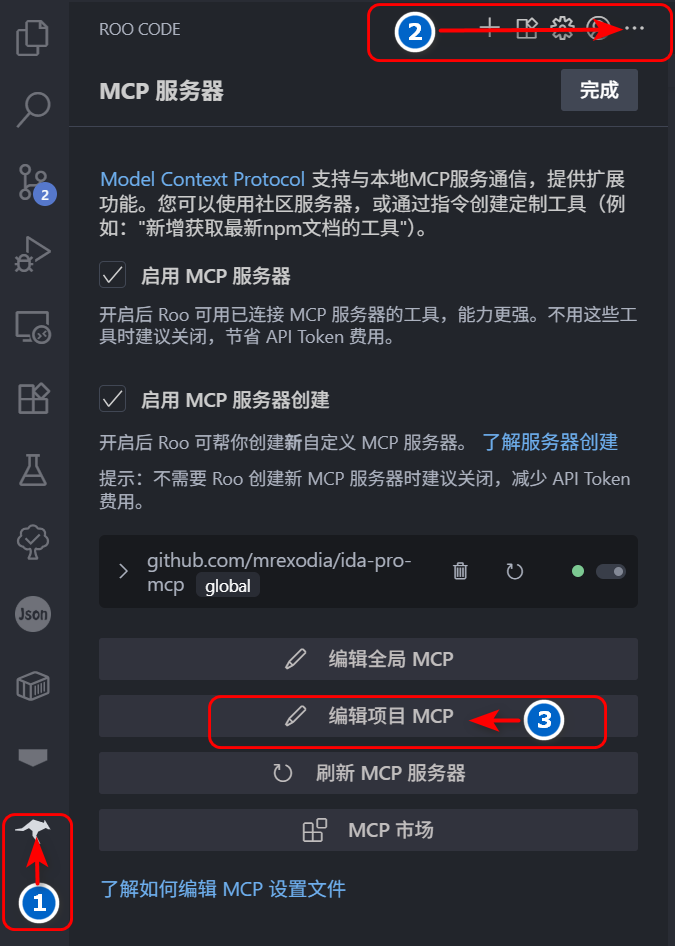 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 mzfr/slicer
A tool to automate the boring process of APK recon
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
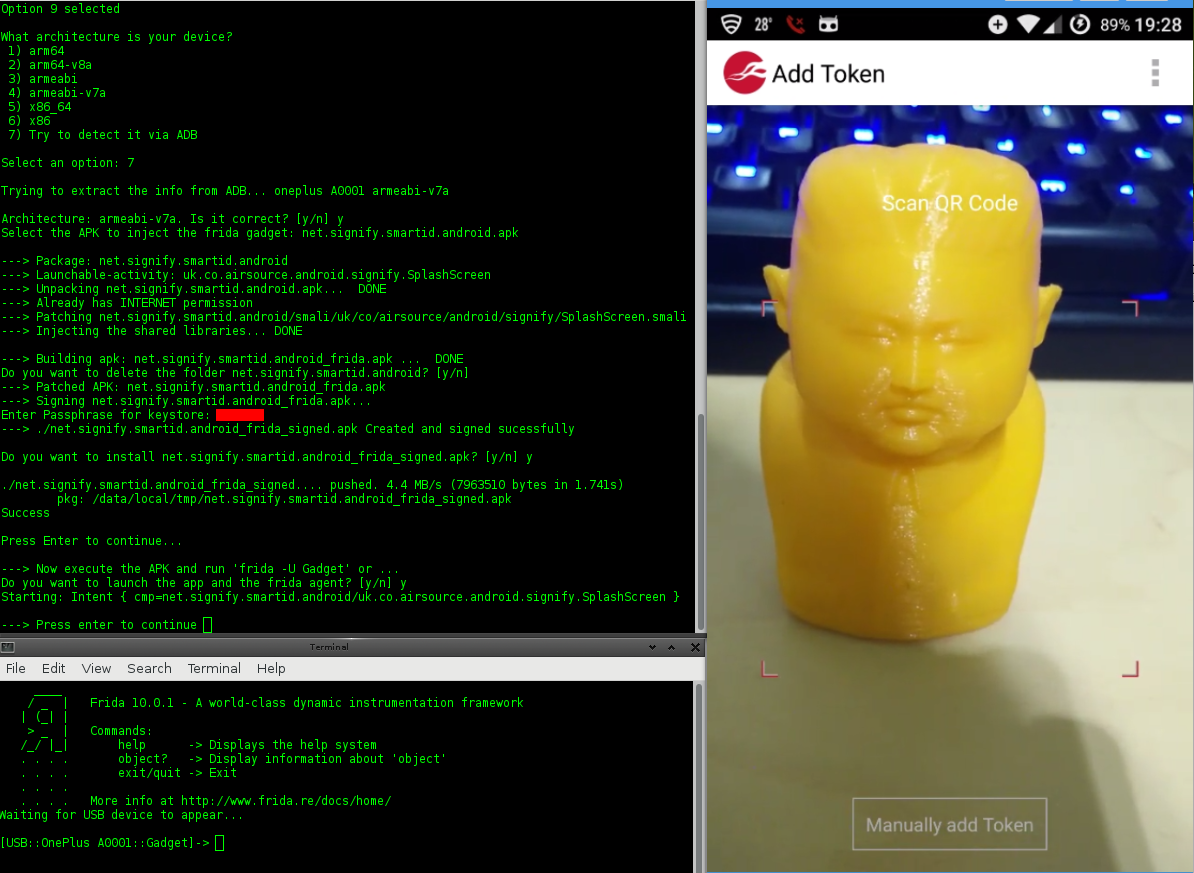 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment