
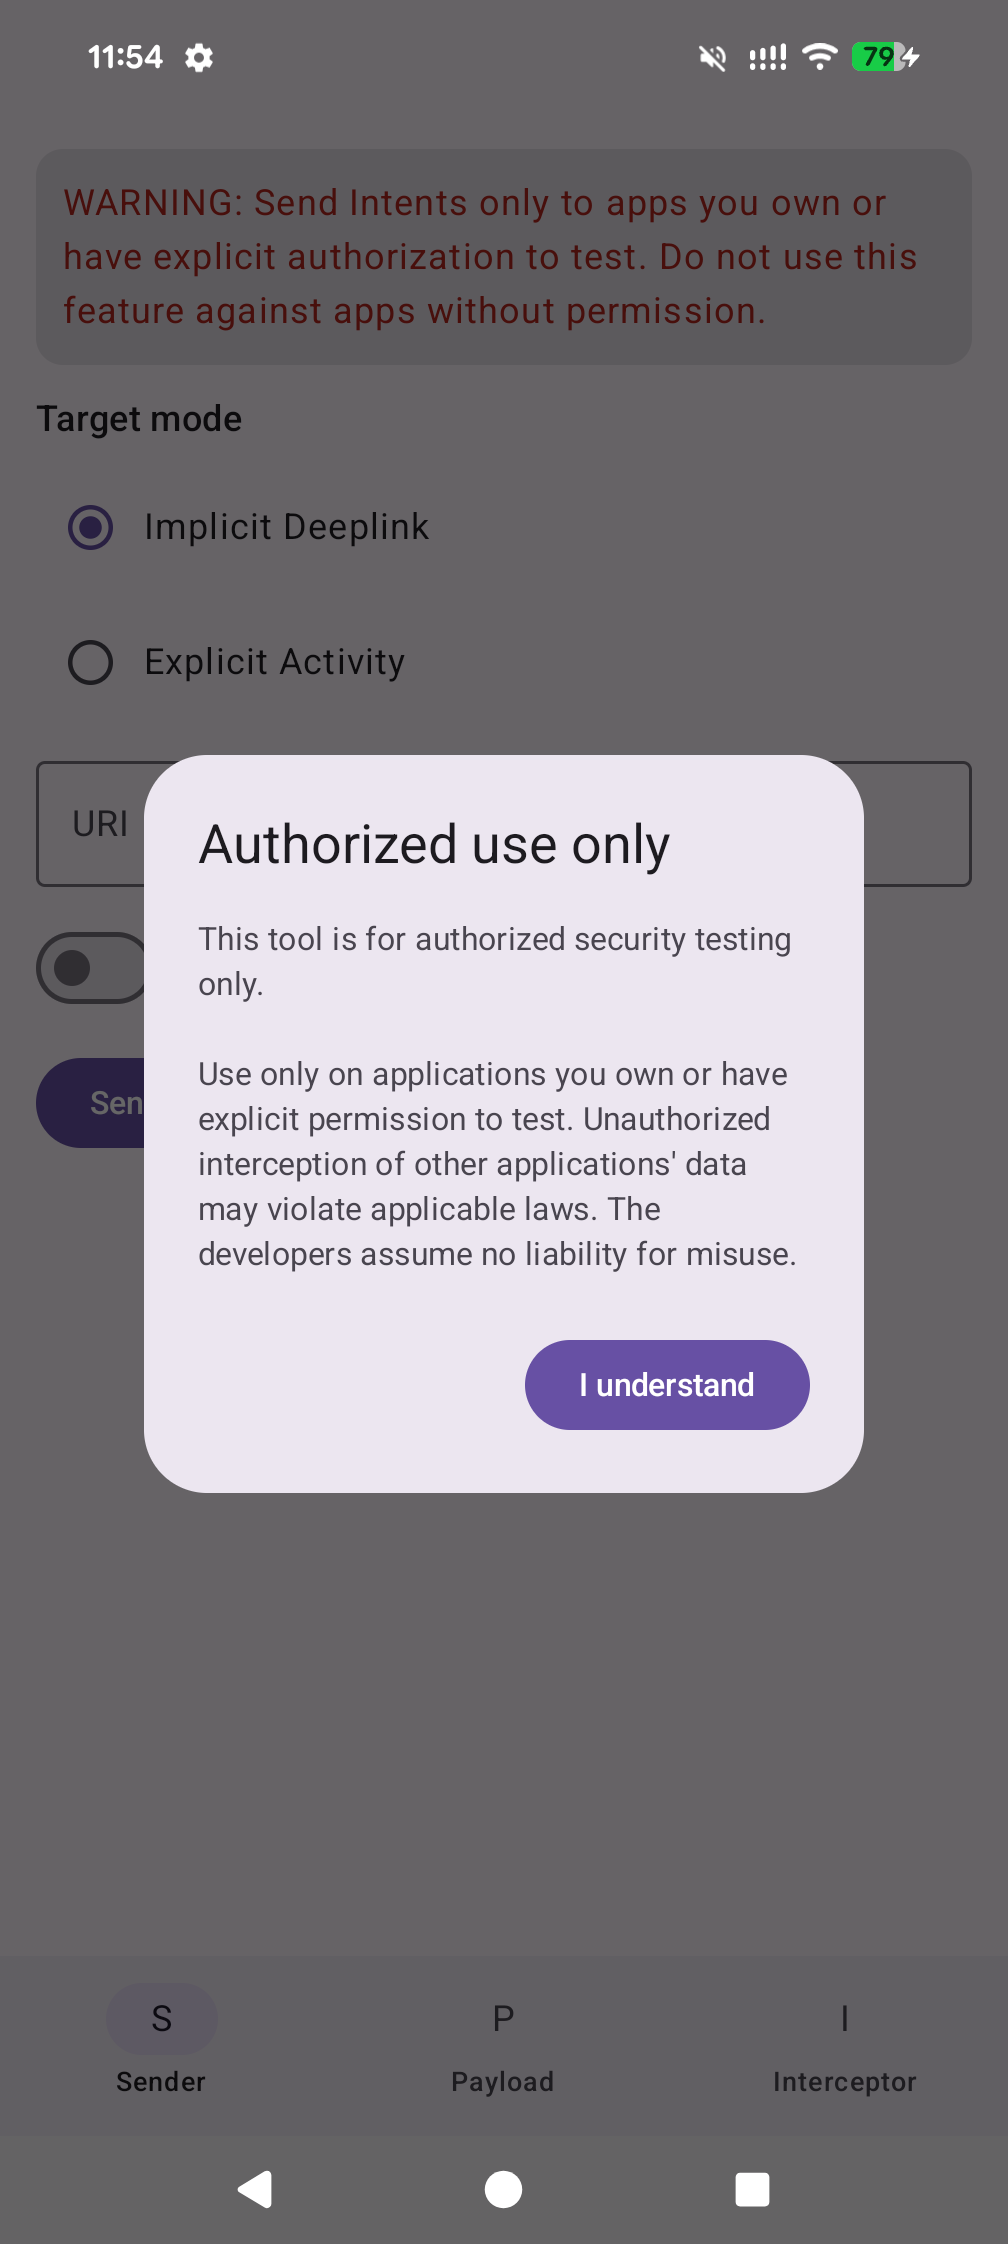
apk-interceptor
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
android-securityinformation-gatheringmobile-app-pentesting+3
8
sterrasec/apk-interceptorAndroid deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 frida/frida
Main repo for hosting release binaries
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
 codinggay/blackdex
Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
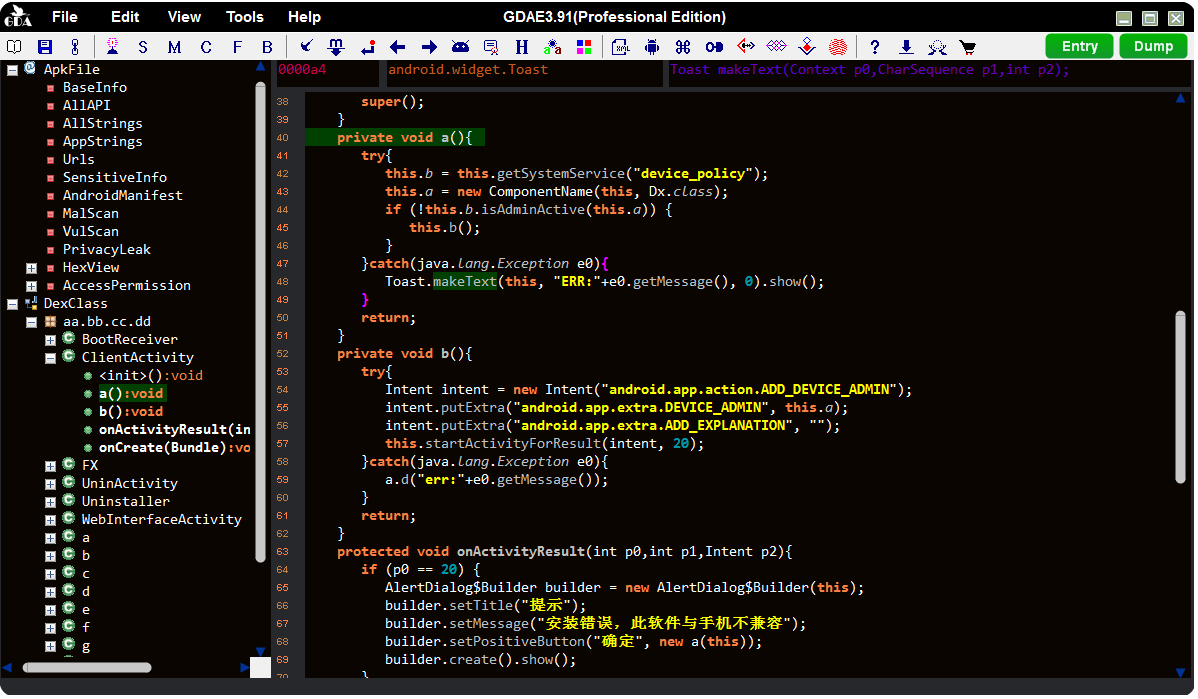 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
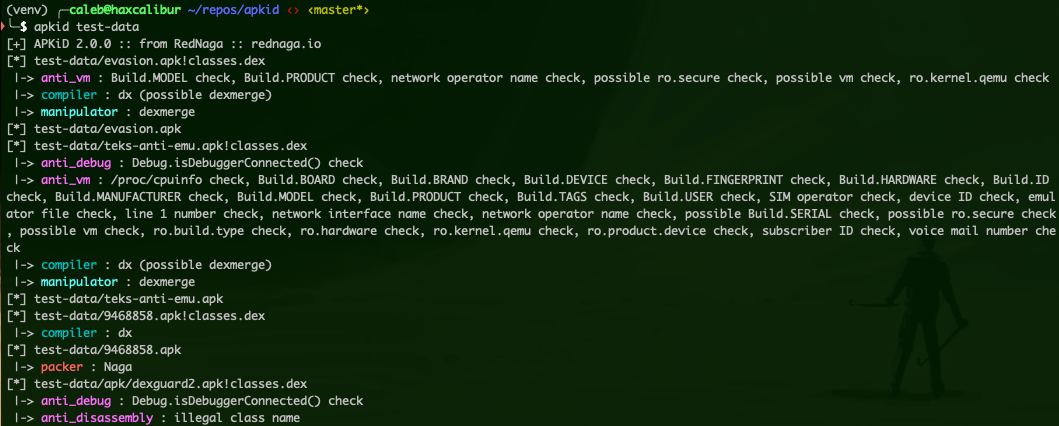 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
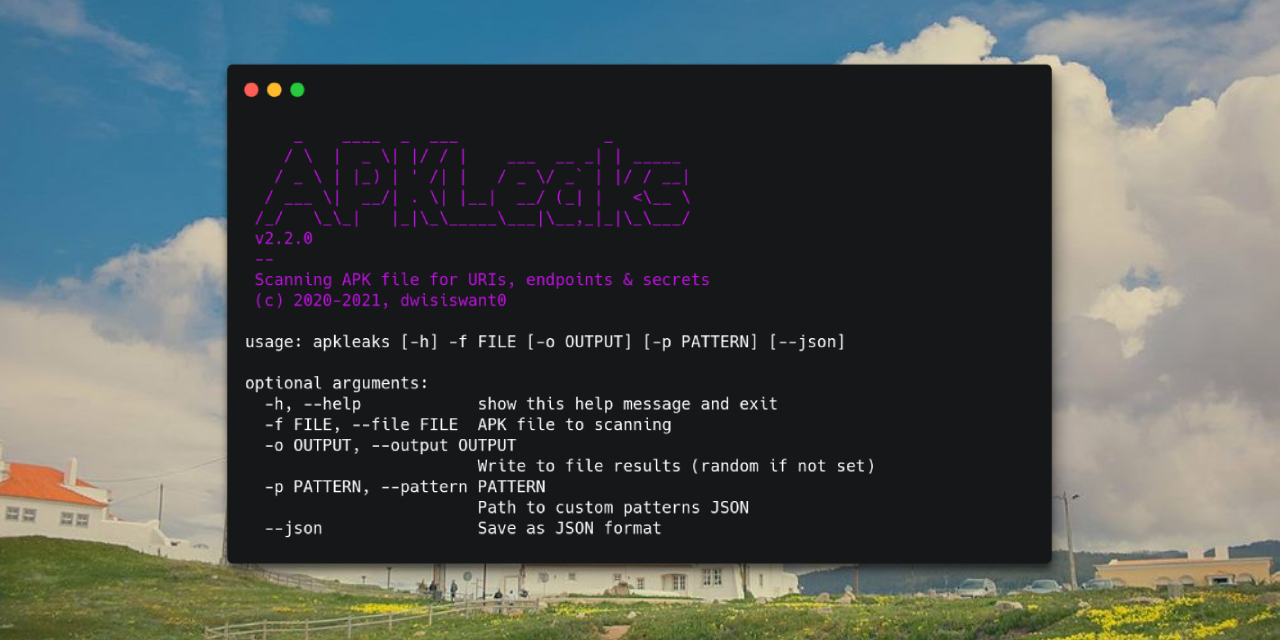 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
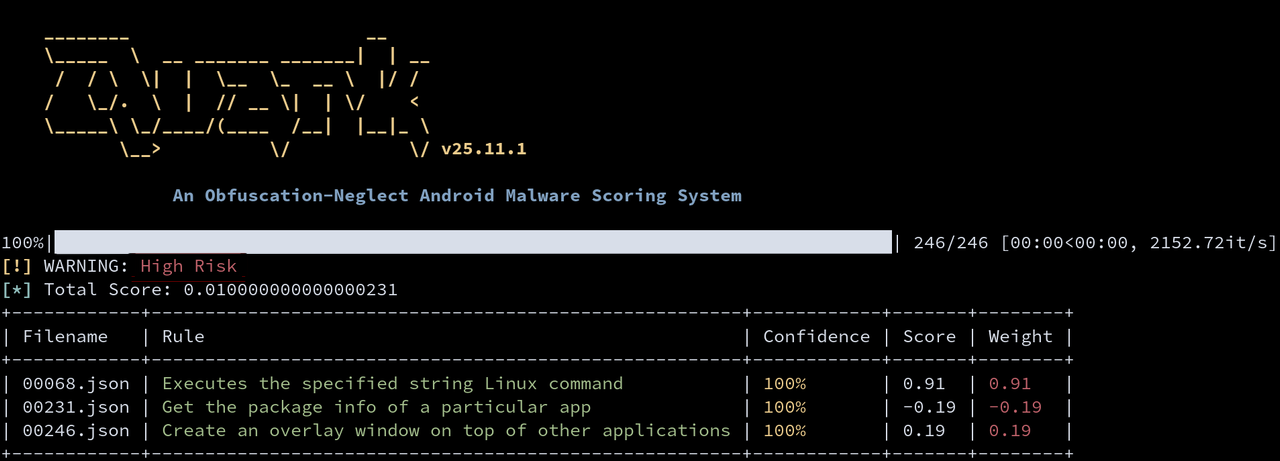 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 nowsecure/r2frida
Radare2 and Frida better together.