
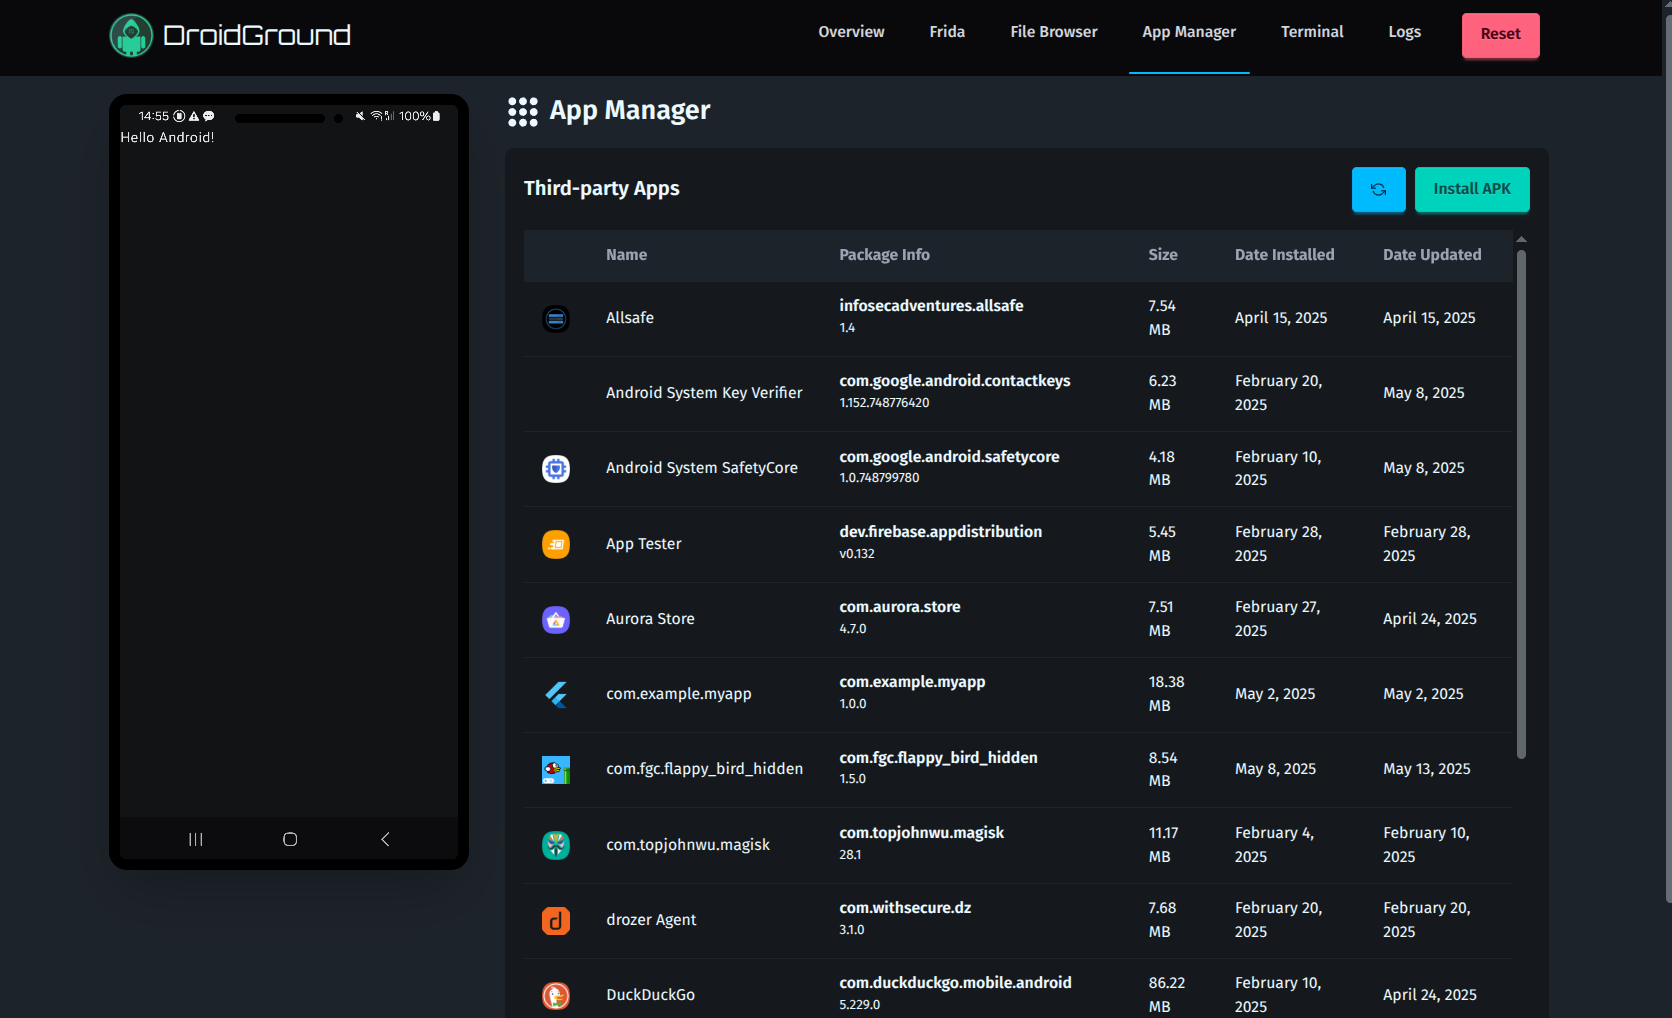
droidground
 secforce/droidground
A flexible playground for Android CTF challenges.
android-securityctfdynamic-analysis-sandboxing+5
secforce/droidgroundA flexible playground for Android CTF challenges.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 a0zhar/quarkpoc
iOS Application w/Implementation of CVE-2024-27804
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…
 nyamisty/ssl-kill-switch3
Next Generation SSLKillSwitch with much more support!
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
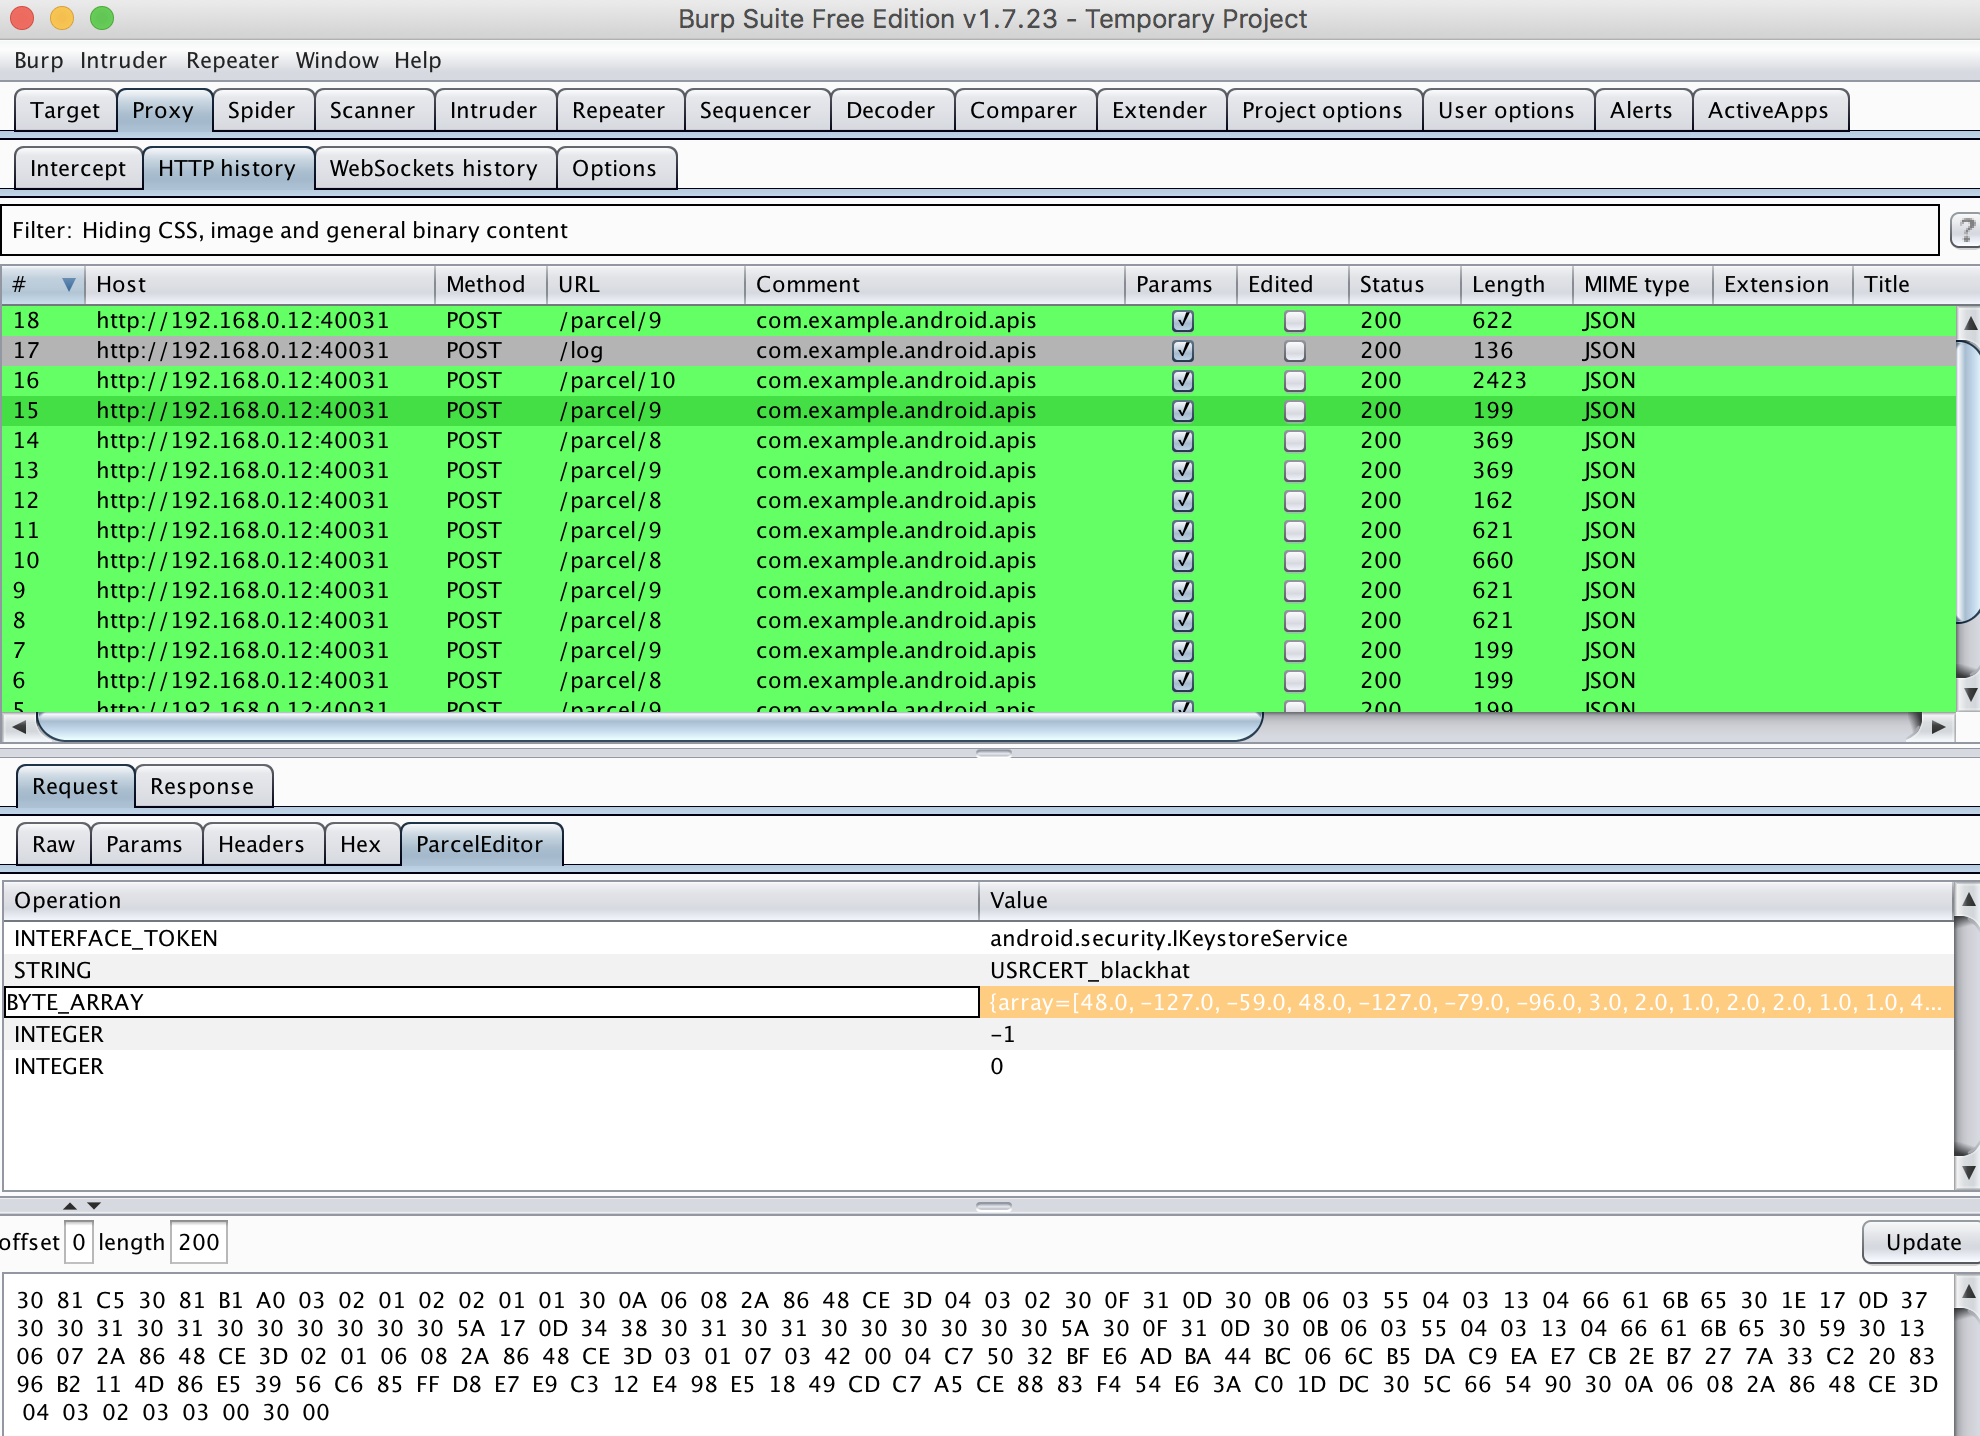 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370