

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
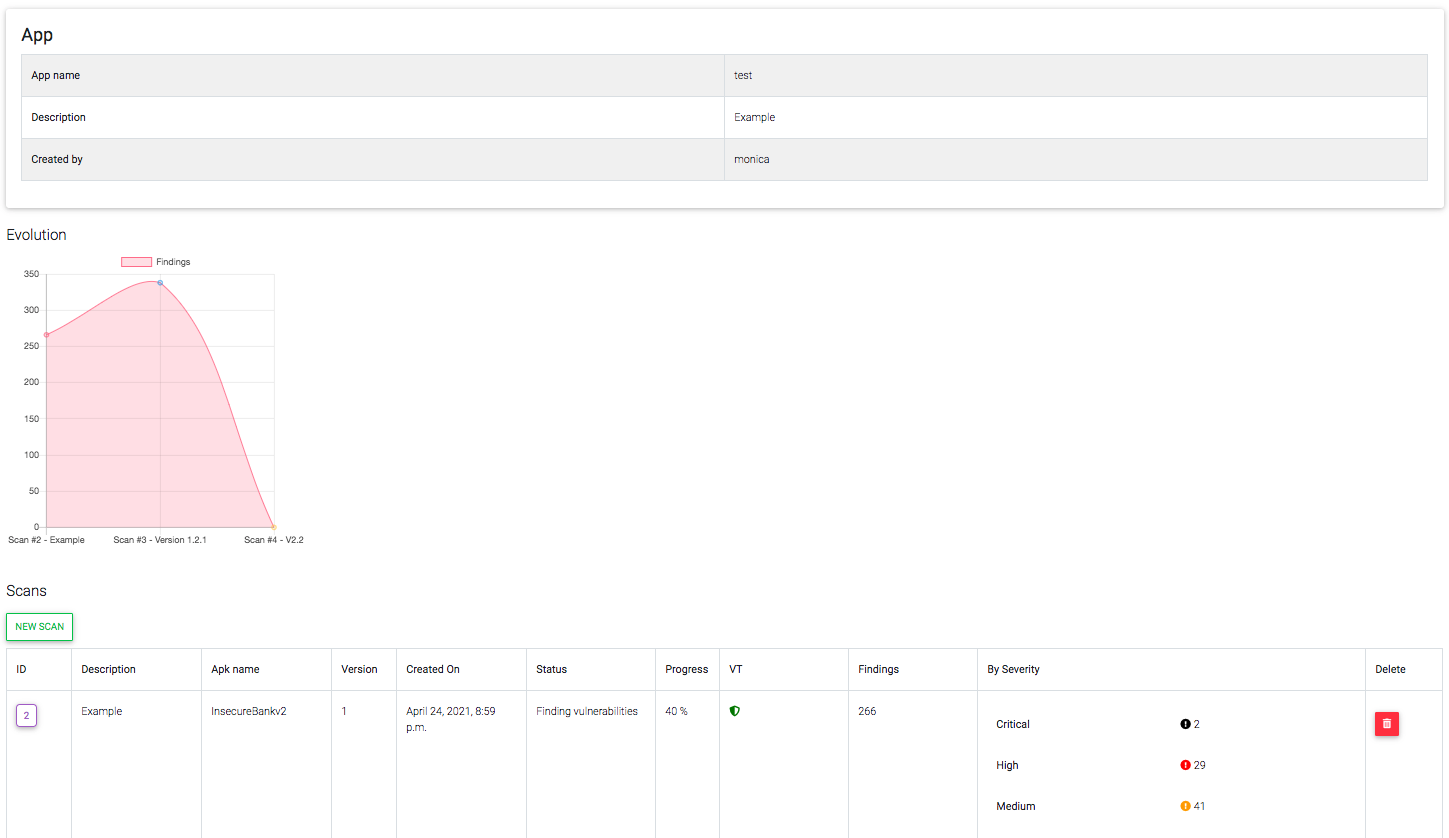 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 frida/frida
Main repo for hosting release binaries
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 nowsecure/r2frida
Radare2 and Frida better together.
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 grapheneos/vanadium
Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…