android-reverse-engineering-skill

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

A tool for reverse engineering Android apk files

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…


Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…

Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…

RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox

Main repo for hosting release binaries

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Radare2 and Frida better together.

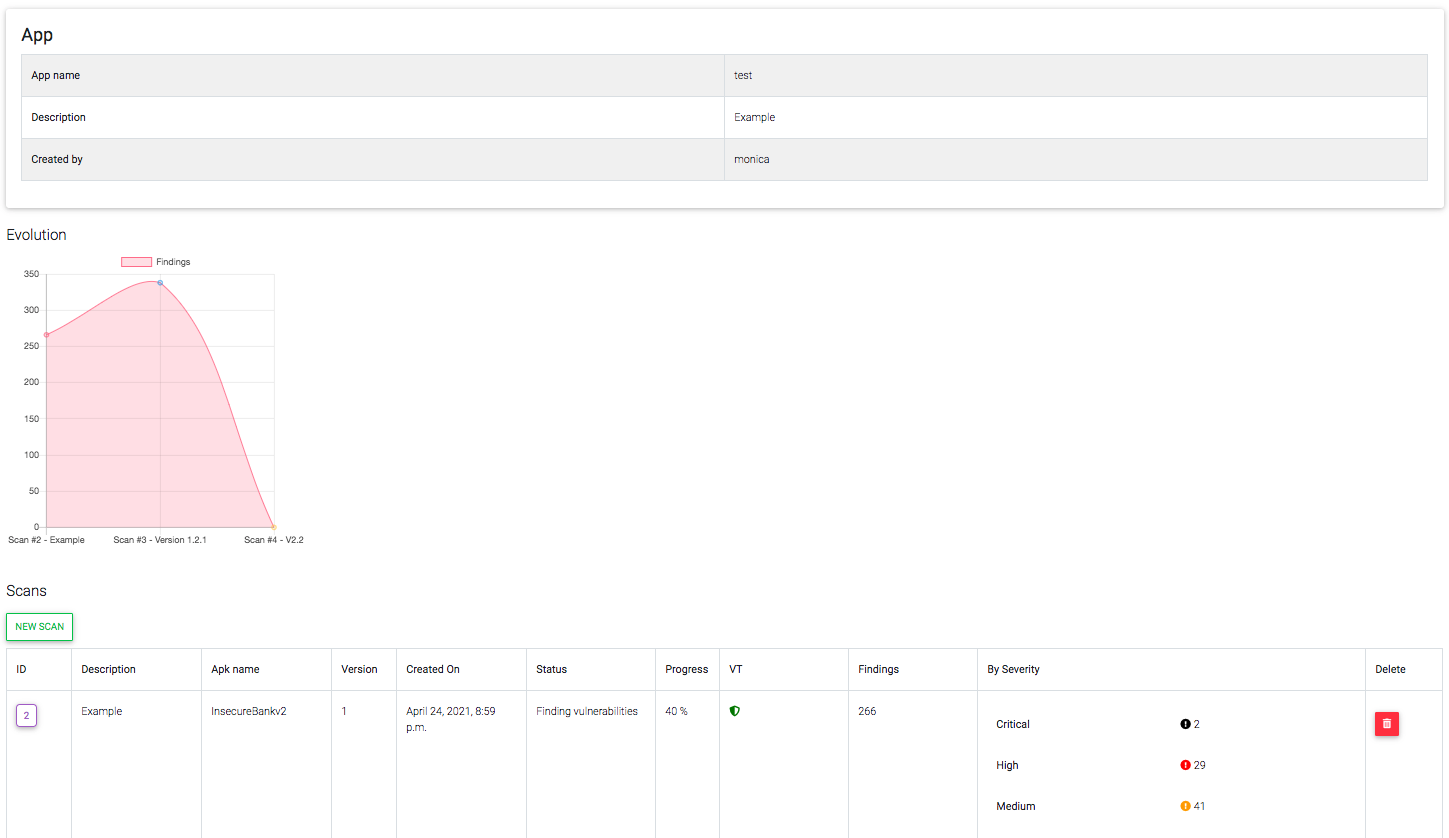
Django application that performs SAST and Malware Analysis for Android APKs

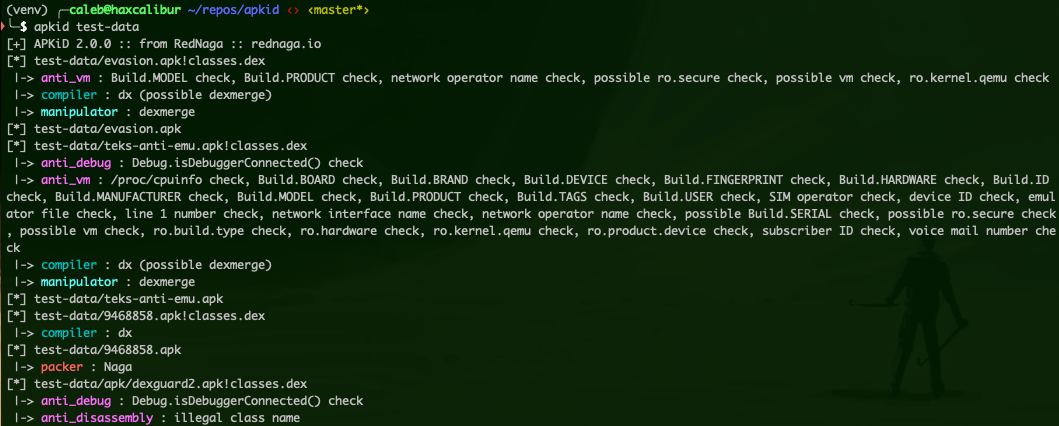
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android

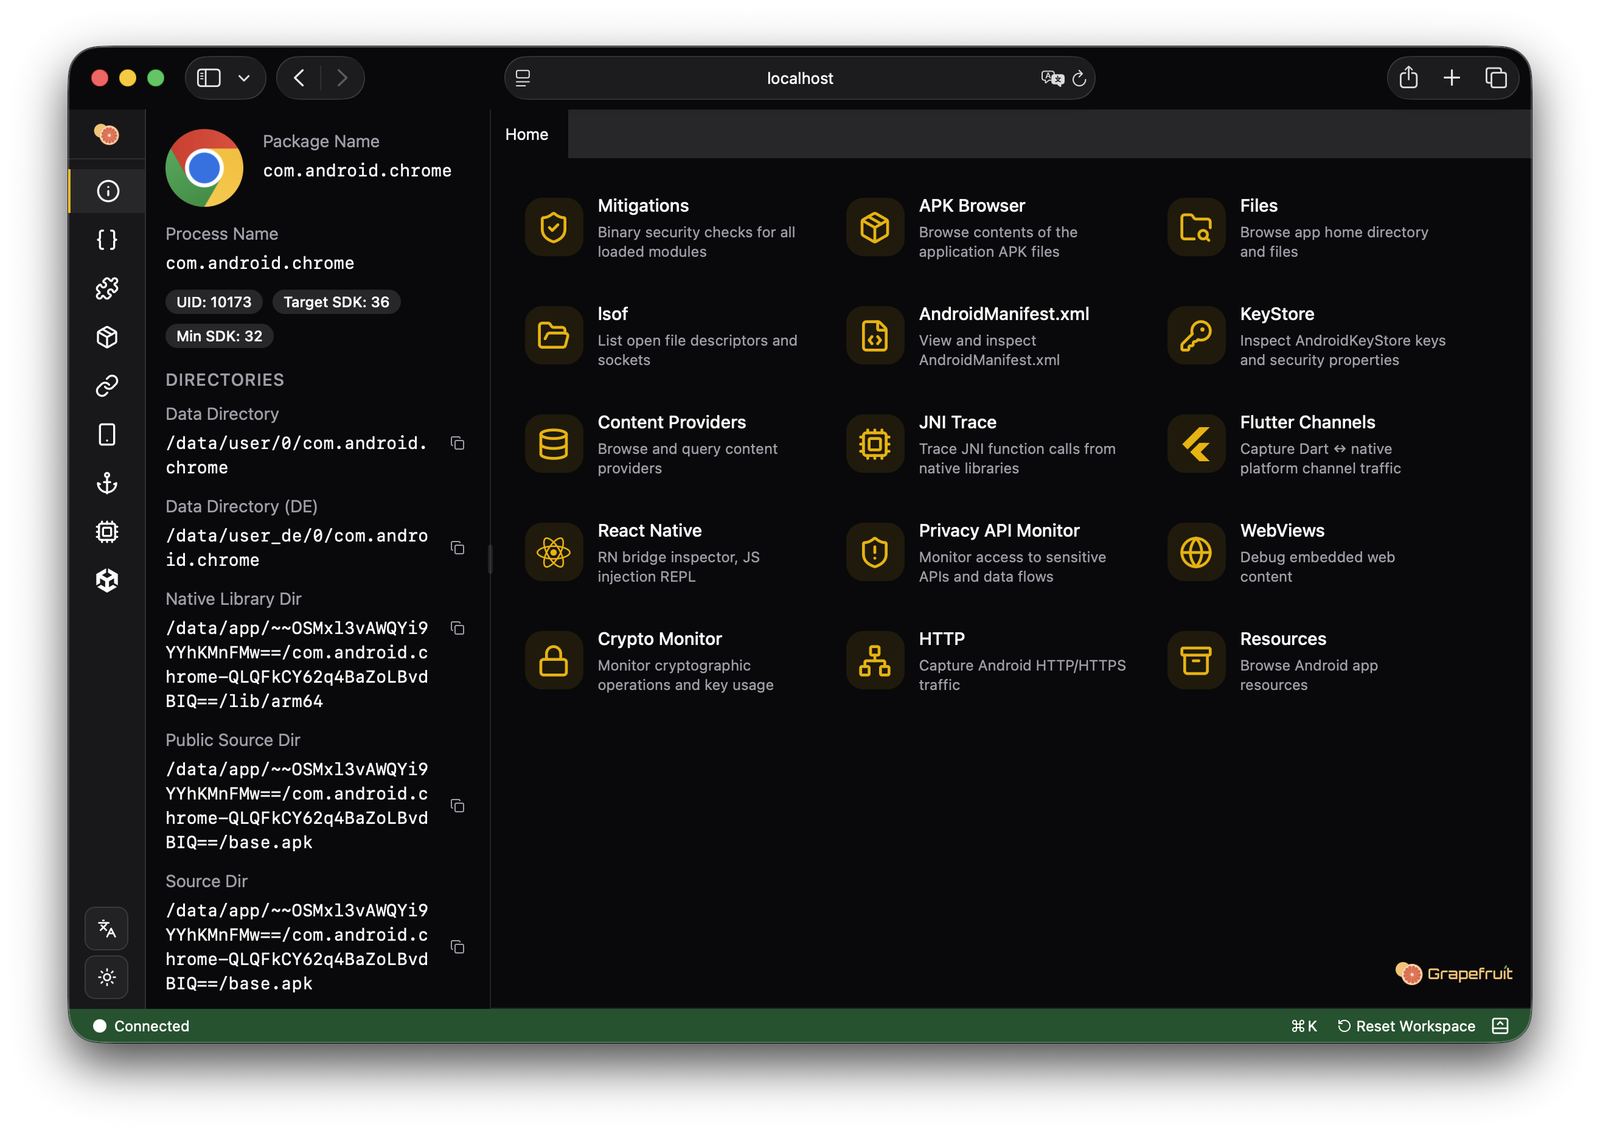
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow

Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…