

 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 nowsecure/r2frida
Radare2 and Frida better together.
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 frida/frida
Main repo for hosting release binaries
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 bronils/aotopsy
Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
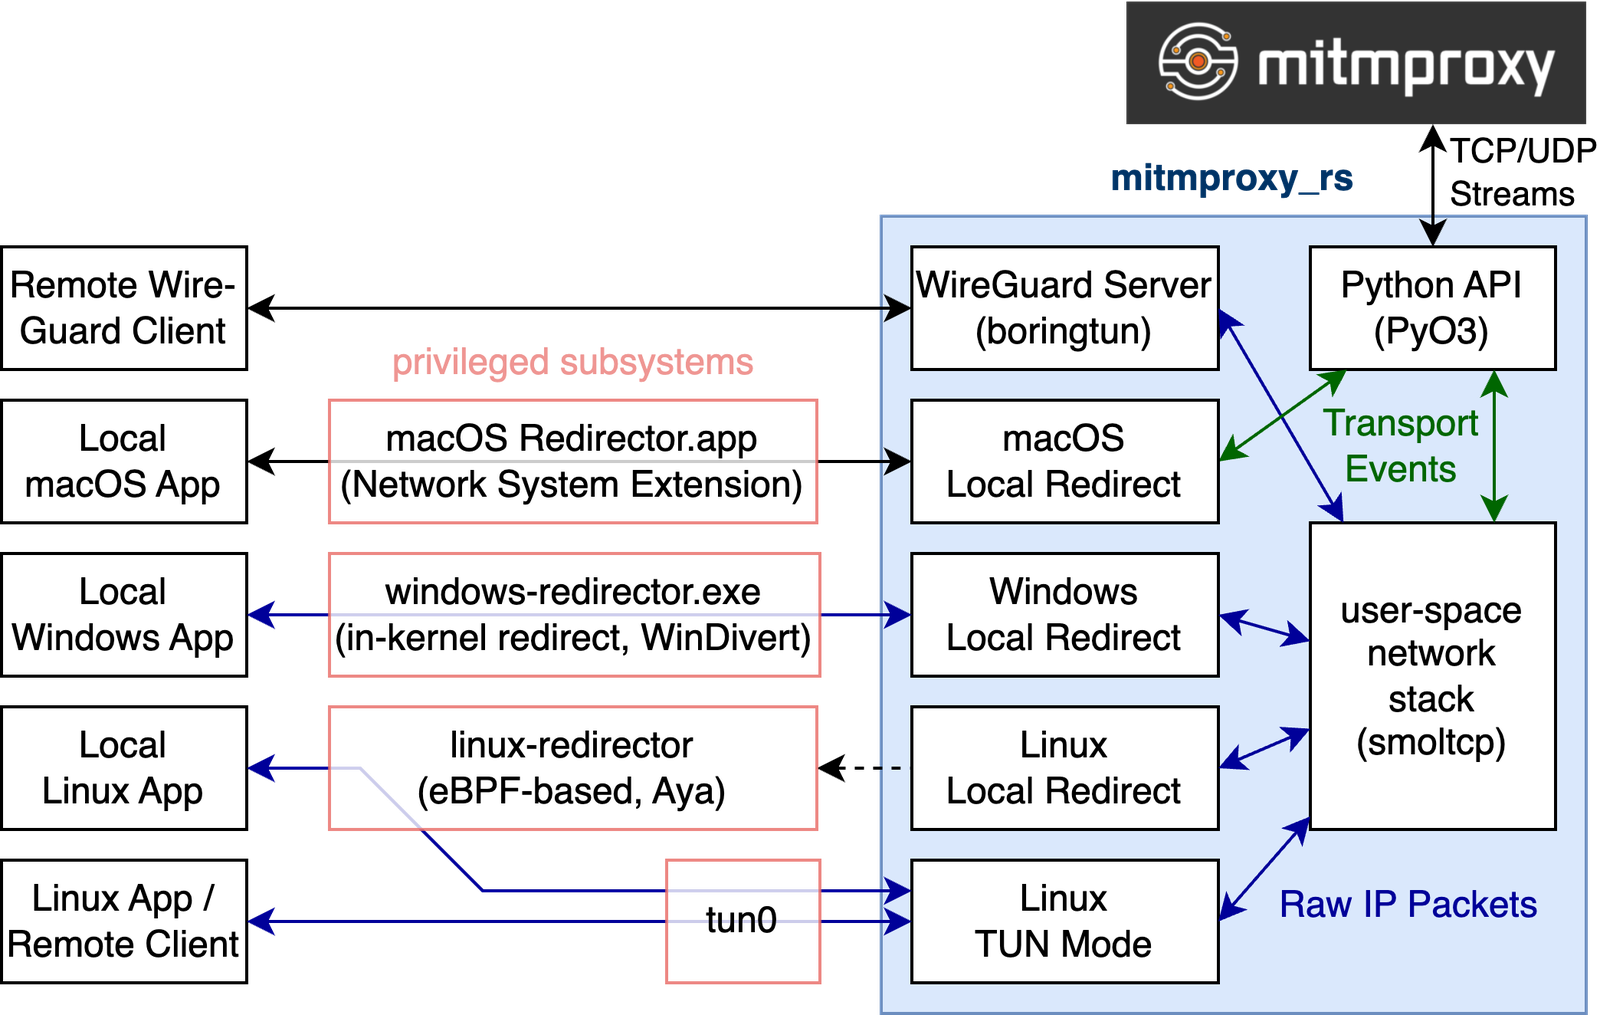 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
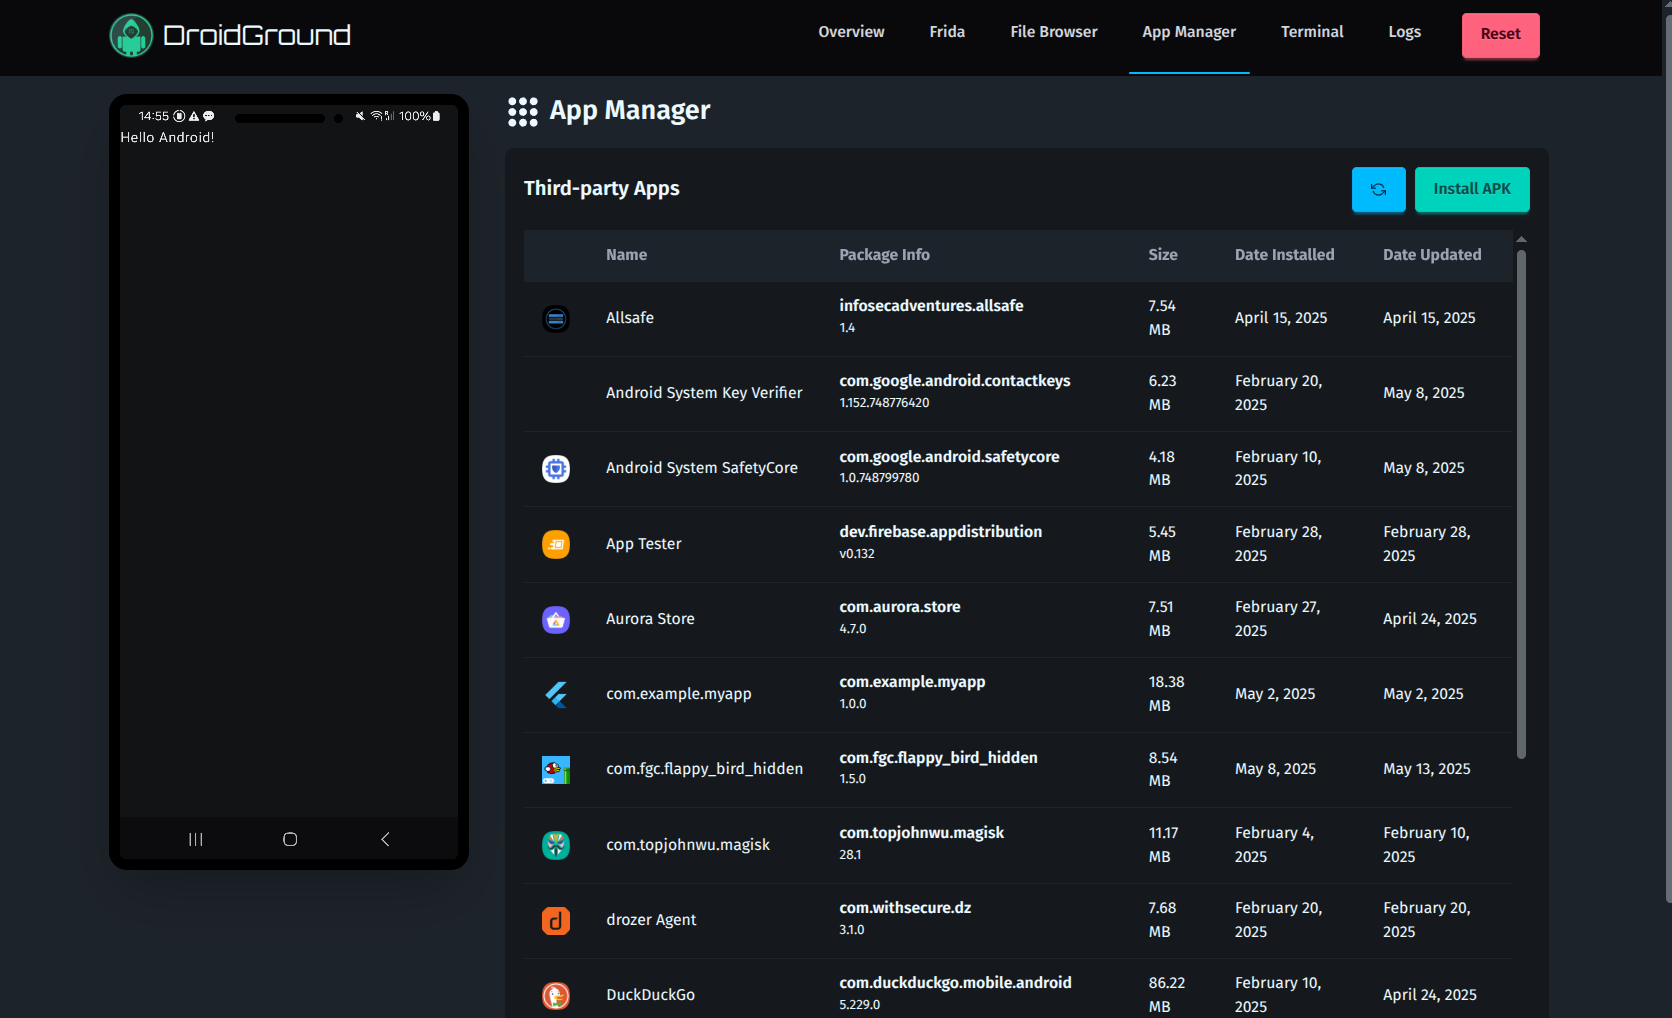 secforce/droidground
A flexible playground for Android CTF challenges.
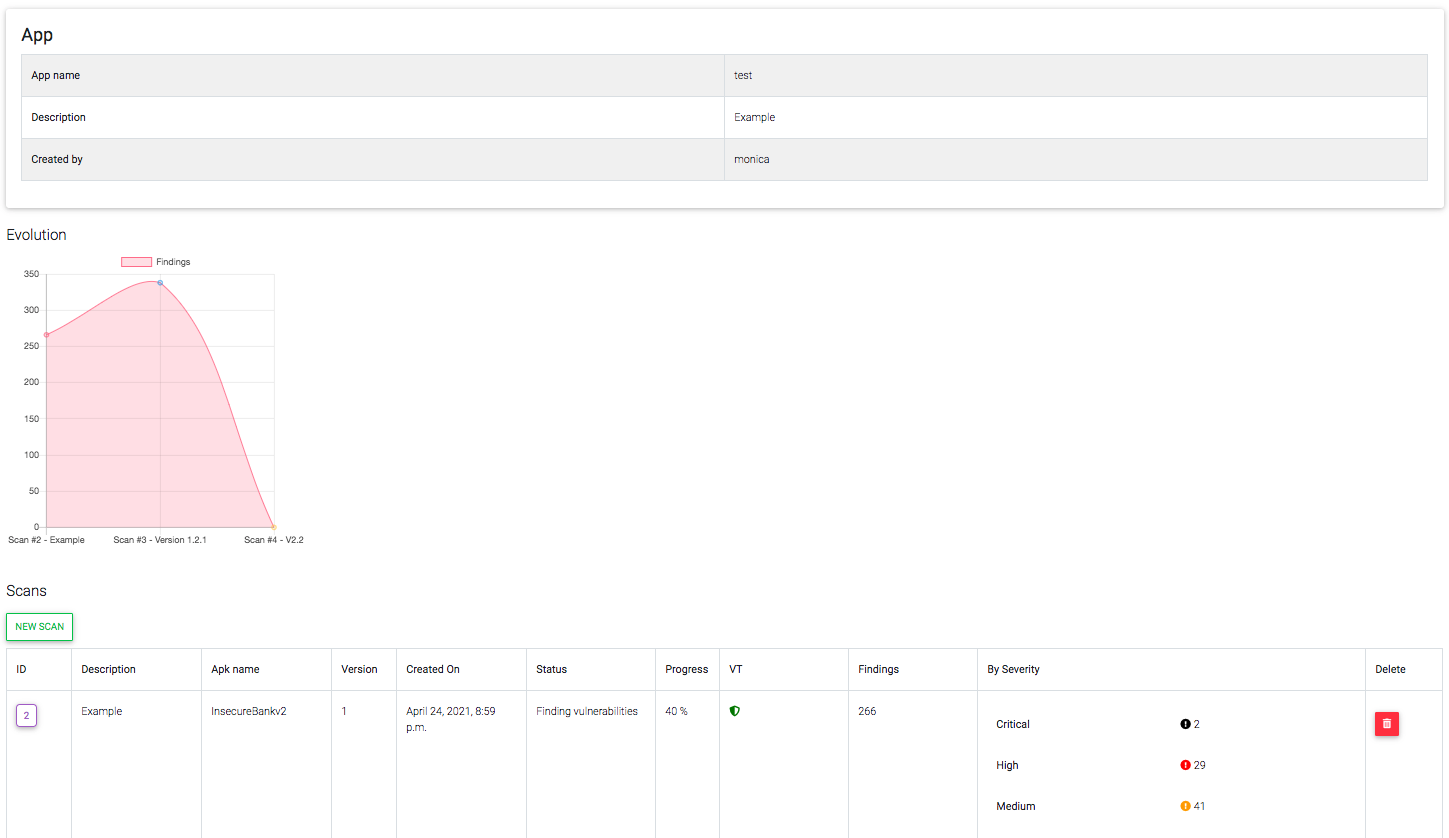 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 chichou/vscode-frida
Unofficial frida extension for VSCode
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…