Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Django application that performs SAST and Malware Analysis for Android APKs

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs

Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…

Demo Android application demonstrating CVE-2019-9465 for security testing and vulnerability analysis on mobile platforms.

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

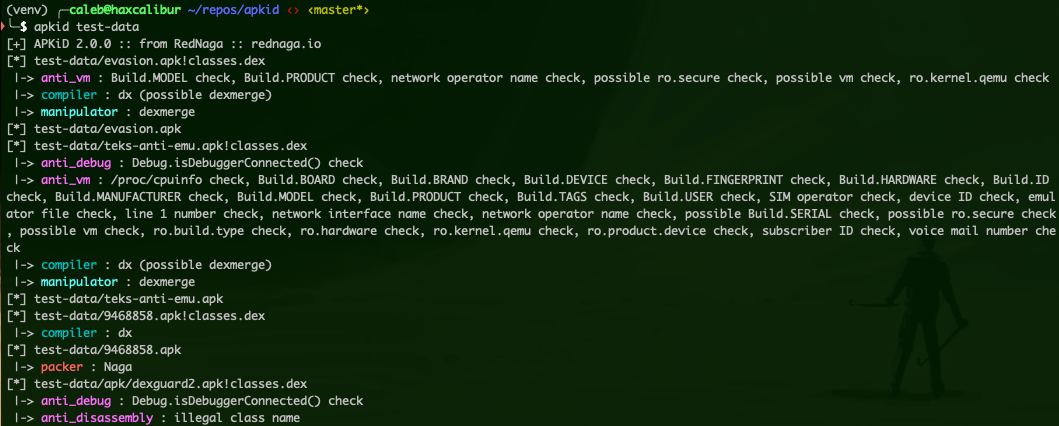
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android

Intentionally vulnerable Android application.

🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection

Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…

An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…

Static and dynamic Android application security analysis

Fermion, an electron wrapper for Frida & Monaco.

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS

Demo Android application for CVE-2019-9465