

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.2k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
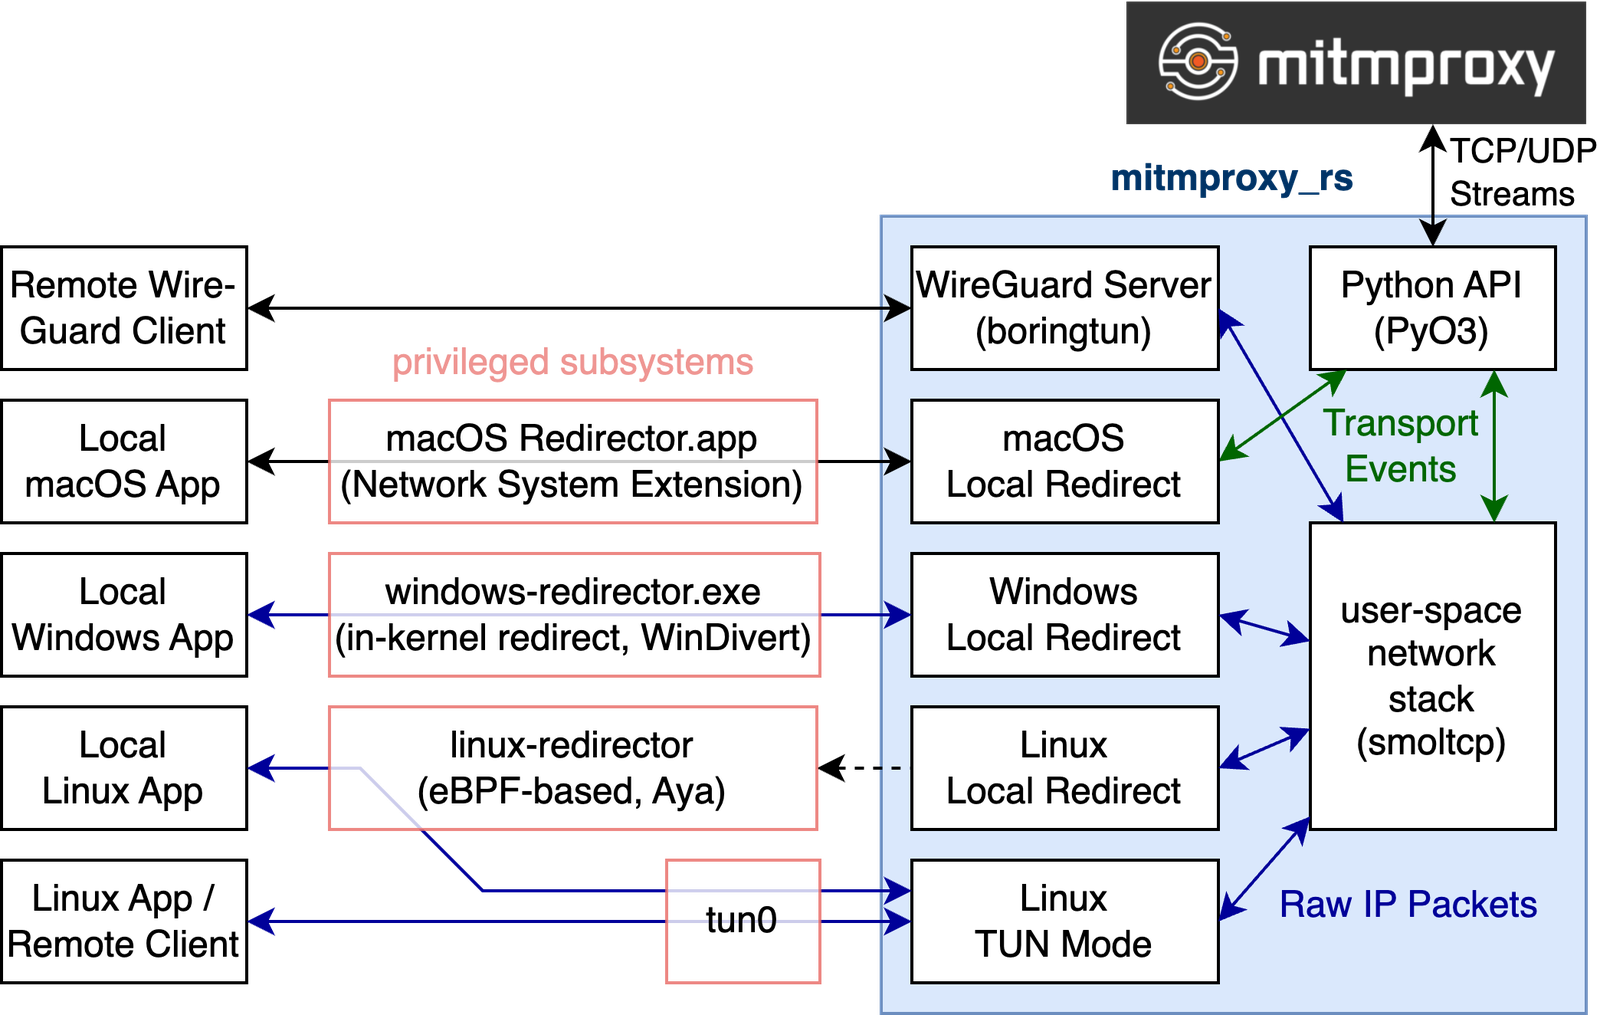 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 frida/frida
Main repo for hosting release binaries
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
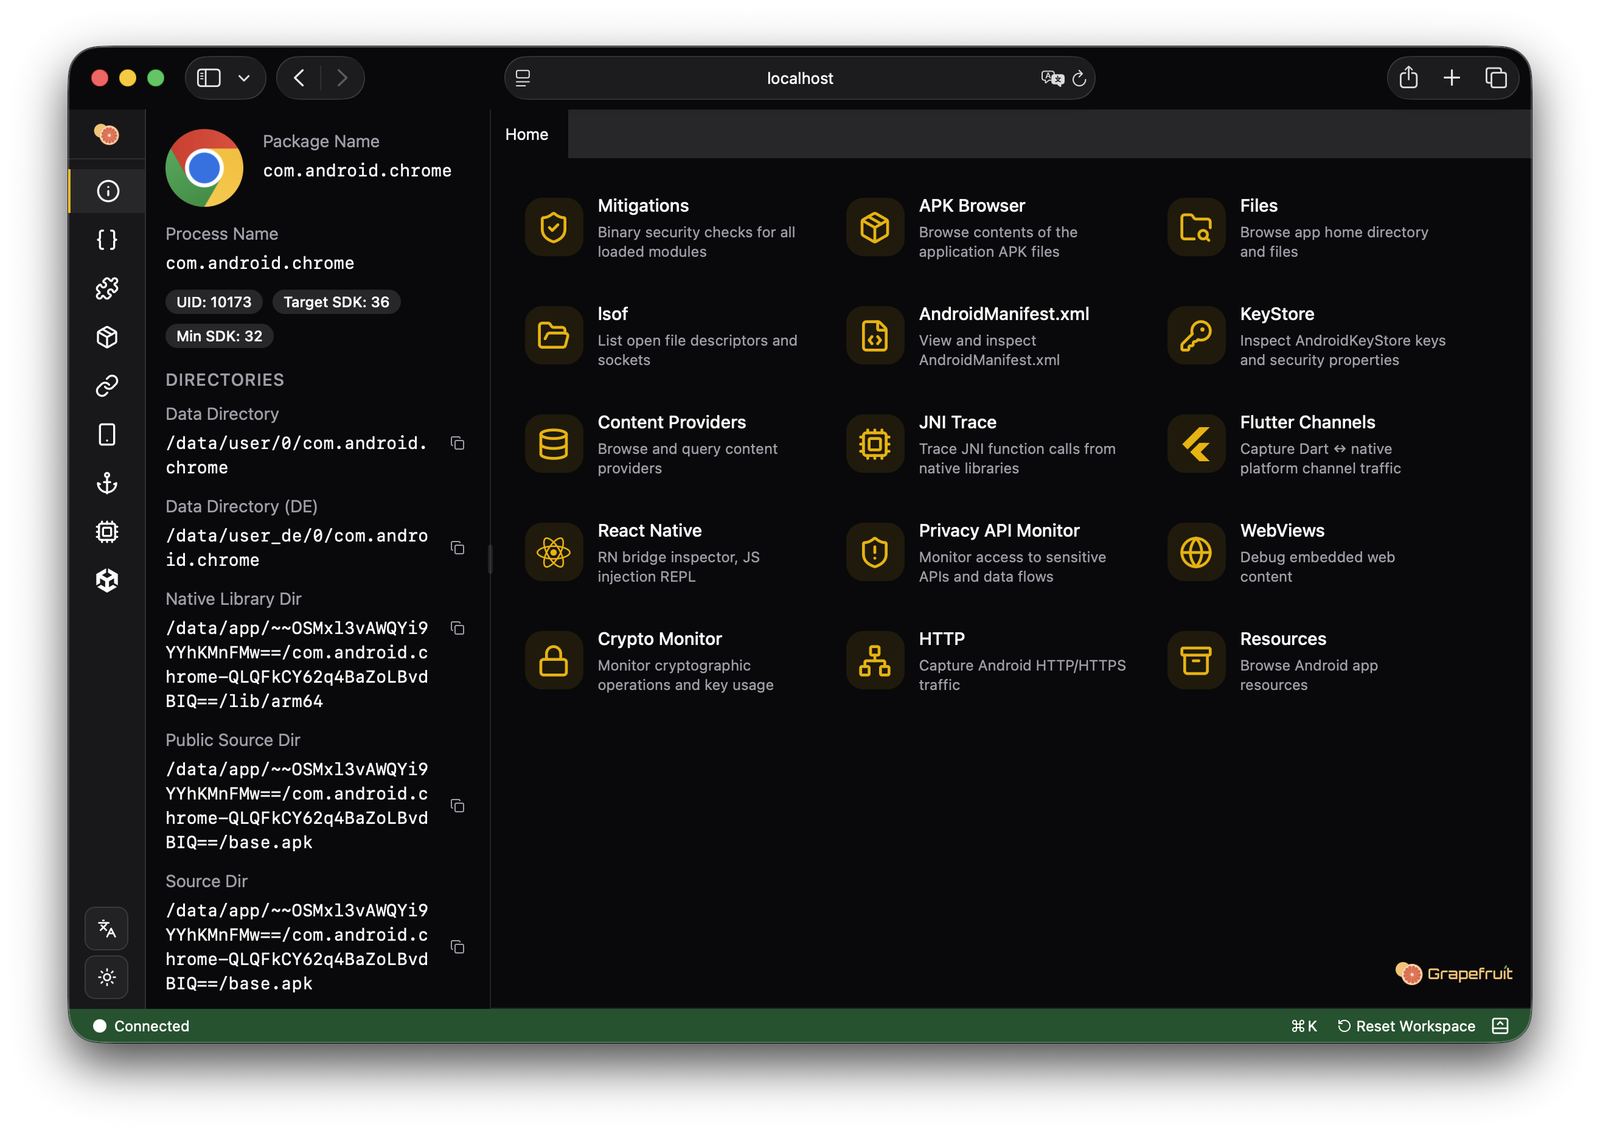 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 michalbednarski/organizertransaction
PoC for CVE-2021-39749, allowing starting arbitrary Activity on Android 12L Beta
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.